
php_reverse_shell
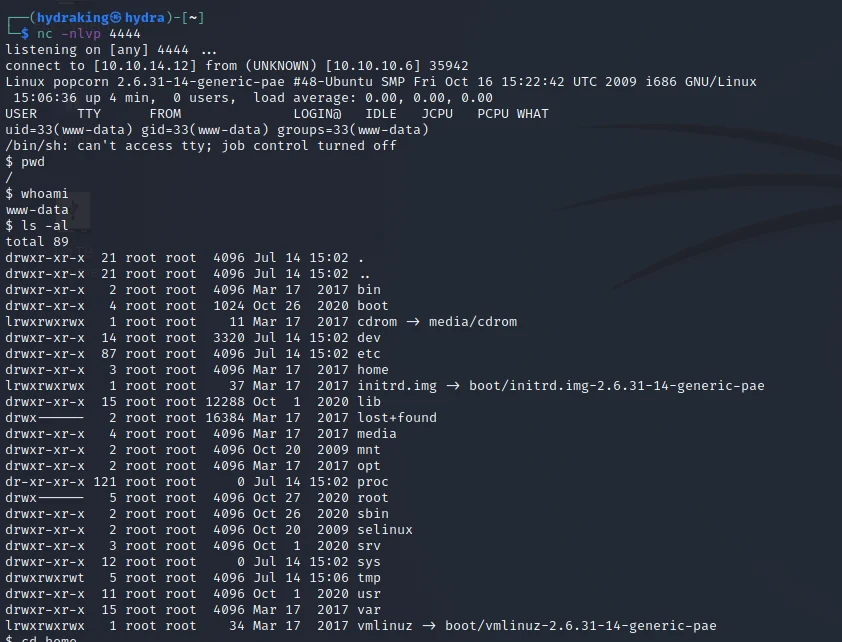
Simple PHP reverse shell script for establishing remote command execution on target systems. Ideal for penetration testing and security assessments.

Simple PHP reverse shell script for establishing remote command execution on target systems. Ideal for penetration testing and security assessments.

Python PoC exploiting CVE-2026-33439, a pre-auth RCE in OpenAM via Java deserialization of the jato.clientSession parameter, with interactive and…

This repository consists of the python exploit for CVE-2022-1388 (F5's BIG-IP Authentication Bypass to RCE)

PHP-based backdoor tool for remote website control via HTTP/HTTPS. Enables file management, command execution, and Tor connectivity with…

Python proof-of-concept exploit for CVE-2026-44011, an authenticated RCE in Craft CMS via Yii behavior injection, with two-stage command output…

All-in-One Hacking Tools For Hackers! And more hacking tools! For termux.

Interactive shell client for React Server Components RCE exploitation via __proto__ pollution (CVE-2025-55182)

Fuel CMS 1.4.1 - Remote Code Execution

Python exploit for CVE-2021-22941 targeting Citrix ShareFile RCE with shell and ping options for remote command execution and network probing.

XWiki 15.10.11, 16.4.1 and 16.5.0RC1 Unauthenticated Remote code execution POC

CraftCMS has an RCE vulnerability via relational conditionals in the control panel

Exploit for CVE-2025-50505 in Clash Verge Rev, demonstrating local privilege escalation and remote code execution via unauthenticated API, including…

Craft CMS RCE via relational conditionals in the control panel

Automated exploit for CVE-2025-59287, an unauthenticated RCE in WSUS, featuring payload generation, reverse shell listener, and AES encryption with…

Weblogic 反序列化漏洞(CVE-2018-2628)

Nmap script to detect VMware vCenter Server CVE-2021-21972 RCE vulnerability by probing the uploadova endpoint and checking for vulnerable response.

CVE-2022-31814 Exploitation Toolkit.

Proof-of-concept exploit for CVE-2025-24813, achieving remote code execution on Apache Tomcat via session deserialization and partial PUT requests.