
shepard
 d3adzo/shepard
In progress persistent download/upload/execution tool using Windows BITS.
command-and-controldata-exfiltrationpersistence-mechanisms+3
415 years ago
d3adzo/shepardIn progress persistent download/upload/execution tool using Windows BITS.
 hev0x/cve-2021-26828_scadabr_rce
Proof-of-concept exploit for CVE-2021-26828 enabling authenticated remote code execution on ScadaBR SCADA systems via JSP file upload. Supports…
 johenlastgen-jlg/cve-2026-18351
Mass exploit tool for CVE-2026-18351, an unauthenticated arbitrary file upload to RCE in Elementor Forms <= 1.6.0, with passive probing, shell…
 iduzzel/cve-2023-24249-exploit
Exploit script for CVE-2023-24249 - a vulnerability allowing remote code execution via file upload and command injection.
 khadafigans/react2shell
React2Shell - CVE-2025-66478 RCE Exploit
 shinthink/cve-2026-57827
CVE-2026-57827 — RSFiles! Joomla Component Unauthenticated File Upload RCE. Split-controller upload bypass. CVSS 9.8 | CWE-434 | com_rsfiles < 1.17.12
 g0d150ne/xss2shell
Exploits WordPress pre-auth XSS (CVE-2026-64638) to achieve remote code execution, installing an AES-encrypted backdoor webshell with persistence,…
 0-d3y/langflow-rce-exploit
Remote Code Execution Exploit for Langflow (CVE-2025-3248) - [ By S4Tech ]
 userb1ank/cve-2021-31630
Exploit for CVE-2021-31630 in OpenPLC, providing a Python script and manual steps to achieve remote code execution via malicious ST file upload and…
 hd-exe/cve-2009-2265-fix
fix for not working exploit script on exploitdb (50057.py)
 d0n601/cve-2025-12399
Alex Reservations: Smart Restaurant Booking <= 2.2.3 - Authenticated (Admin+) Arbitrary File Upload
 dexit/cve-2022-1329
CVE-2022-1329 exploit for WordPress Elementor plugin (3.6.0-3.6.2) enabling authenticated remote code execution via missing capability check and…
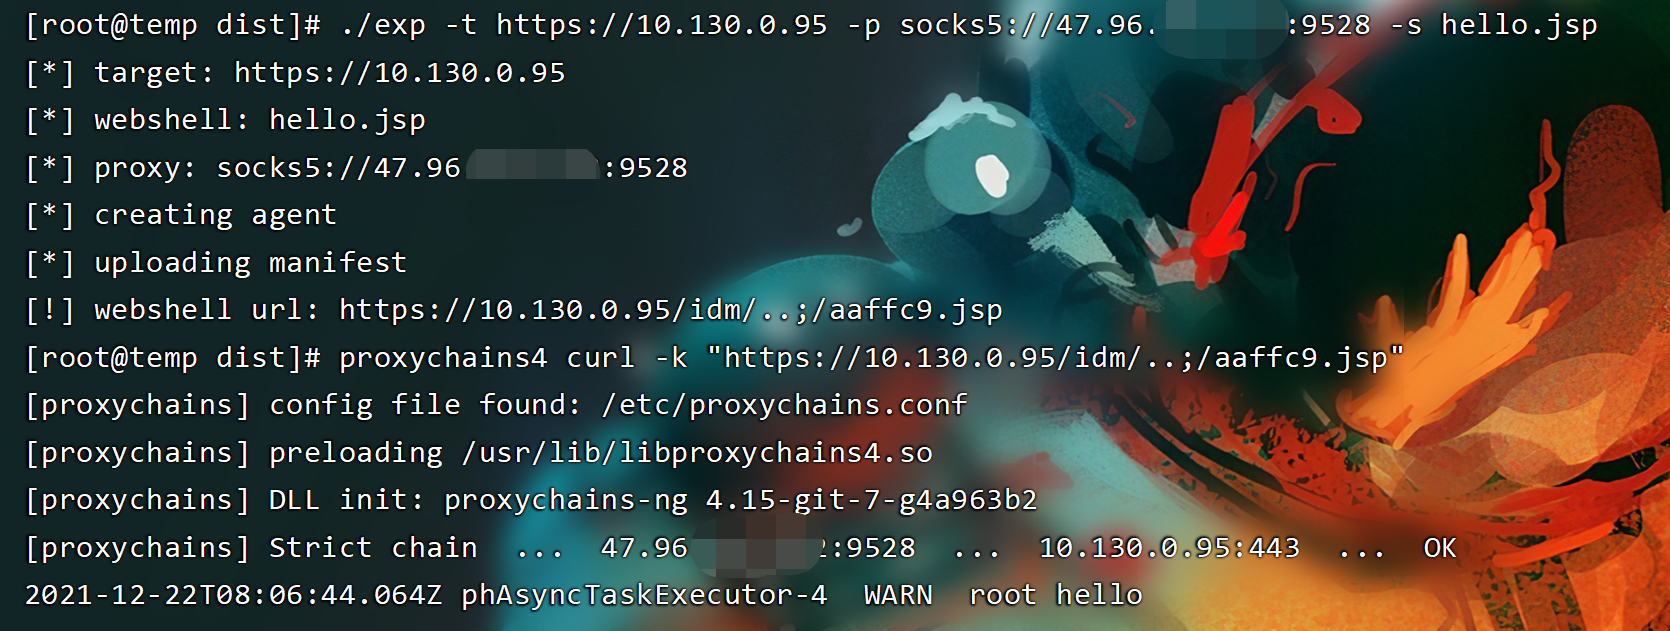 shmilylty/cve-2021-22005-exp
Exploit for CVE-2021-22005, a pre-auth arbitrary file upload vulnerability in VMware vCenter Server, enabling remote code execution via webshell…
 vidura2/cve-2024-46986
Automated Python exploit for Camaleon CMS arbitrary file upload vulnerability (CVE-2024-46986). Supports reverse shell and command execution payloads…
 shinthink/cve-2026-61424
DJ-Classifieds Joomla Component Unauthenticated File Upload RCE. 3-string filter bypass via PHP short tags. CVSS 10.0 | CWE-434 | com_djclassifieds <…
 bly-coder/python-exploit-cve-2020-25213
Python exploit for RCE in Wordpress
 tibbersv6/cve-2026-21440-poc-exp
Proof-of-concept exploit for CVE-2026-21440, enabling file upload and remote command execution on Windows web servers with built-in sensitive path…
 diegogarciayala/cve-2024-24590-clearml-rce-cmd-poc
CVE-2024-24590 ClearML RCE&CMD POC