metasploit-framework

Open-source exploitation framework with modular payload, encoder, and auxiliary system for penetration testing, vulnerability validation, and…

Open-source exploitation framework with modular payload, encoder, and auxiliary system for penetration testing, vulnerability validation, and…

Exploit for CVE-2025-50505 in Clash Verge Rev, demonstrating local privilege escalation and remote code execution via unauthenticated API, including…

This script is a custom security tool designed to test for a critical pre-authentication vulnerability in systems running Erlang-based SSH servers

Nmap script to detect VMware vCenter Server CVE-2021-21972 RCE vulnerability by probing the uploadova endpoint and checking for vulnerable response.

Proof-of-concept exploit for CVE-2023-36845 enabling unauthenticated remote code execution on Juniper SRX firewalls and EX switches via PHP…

A PoC tool for the CVE-2026-0073 on android 11+ devices which allows instant zero click RCE on any unpatched device with adb over tcp enabled

Modular WordPress pre-auth exploit framework chaining SQL injection and authentication bypass to deliver remote code execution, interactive shells,…

marimo is a reactive Python notebook. Prior to 0.23.0, Marimo has a Pre-Auth RCE vulnerability

* React2Shell-CVE-2025-55182

Advanced React Server Components RCE scanner for CVE-2025-55182. Features: multi-stage fingerprinting, vulnerability verification, DNS exfiltration,…

This vulnerability is of the "double-free" type, which occurs during the processing of key exchange (KEX) algorithms in OpenSSH. A "double-free"…

CVE-2026-57827 — RSFiles! Joomla Component Unauthenticated File Upload RCE. Split-controller upload bypass. CVSS 9.8 | CWE-434 | com_rsfiles < 1.17.12

Python exploit tool for OpenCode RCE (CVE-2026-22812) providing command execution, file read/write/upload/download, and interactive shell for…

PoC - Remote Unauthenticated Code Execution Vulnerability in OpenSSH server (Scanner and Exploit)

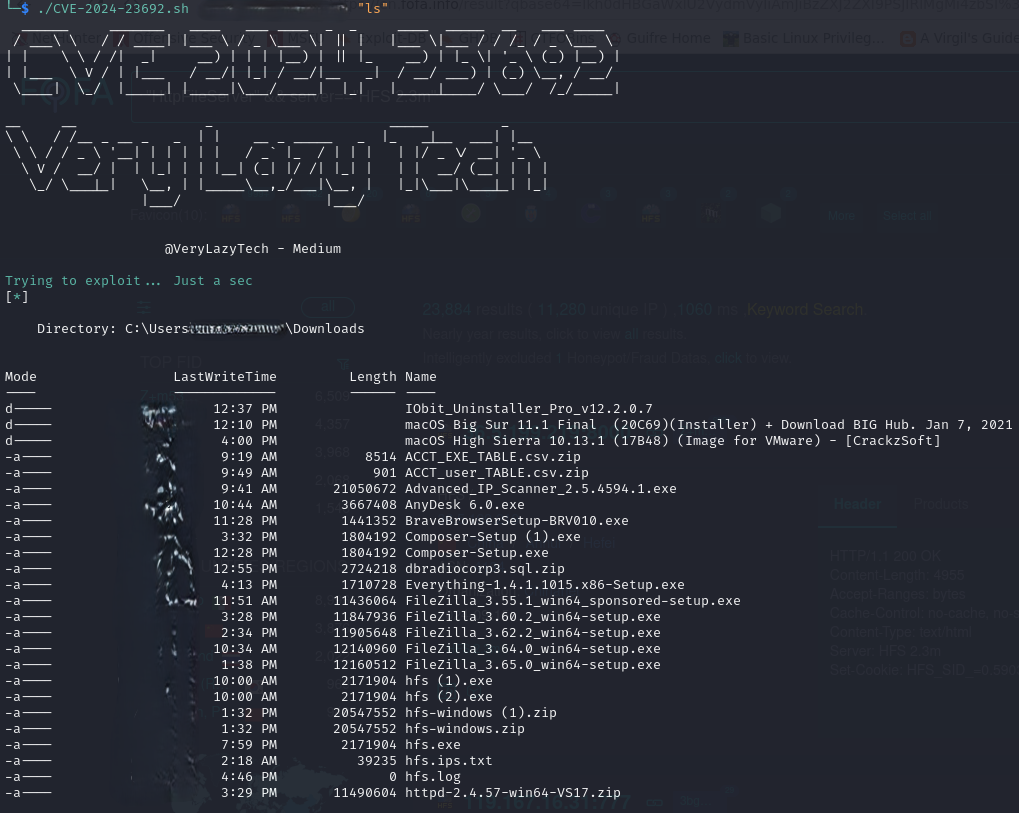
POC - Unauthenticated RCE Flaw in Rejetto HTTP File Server - CVE-2024-23692

Automated exploitation framework for CVE-2025-55182 (Next.js RCE) with subdomain enumeration, vulnerability scanning, payload generation, and…

CVE-2024-6387, also known as RegreSSHion, is a high-severity vulnerability found in OpenSSH servers (sshd) running on glibc-based Linux systems. It…

Remote Unauthenticated Code Execution Vulnerability in OpenSSH server (CVE-2024-6387)