

Koi
 b3rt1ng/koi
Multi-session reverse shell handler with PTY upgrade, post-exploitation modules, Layer 3 tunneling, payload obfuscation for EDR evasion, session…
command-and-controlids-ips-evasionlateral-movement+9
37
b3rt1ng/koiMulti-session reverse shell handler with PTY upgrade, post-exploitation modules, Layer 3 tunneling, payload obfuscation for EDR evasion, session…
 jm33-m0/emp3r0r
Linux post-exploitation C2 framework with gossip mesh networking, memory-only operations, modular payloads, and OPSEC-focused transport for red team…
 boydhacks/dameflare
Python 3 exploit for CVE-2019-3980. Unauthenticated RCE as SYSTEM via SolarWinds Dameware MRC smart card authentication bypass.
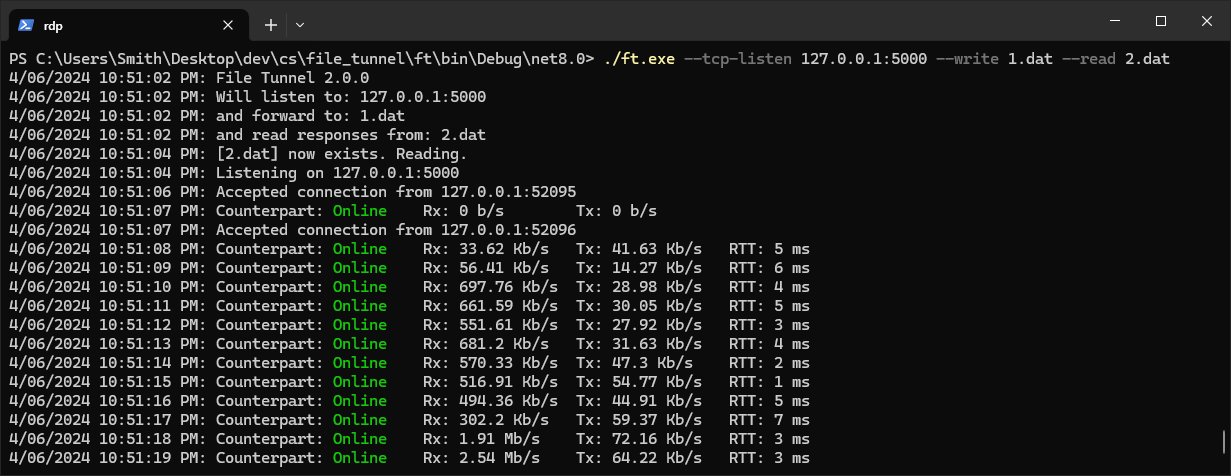 fiddyschmitt/file-tunnel
Tunnel TCP connections through a file
 ldpreload/blacklotus
BlackLotus UEFI Windows Bootkit
 0xtriboulet/revenant
Revenant - A 3rd party agent for Havoc that demonstrates evasion techniques in the context of a C2 framework
 nccgroup/phantap
Phantom Tap (PhanTap) - an ‘invisible’ network tap aimed at red teams
 hackerhouse-opensource/offensivelua
Offensive Lua.
 nccgroup/metasploitavevasion
Metasploit AV Evasion Tool
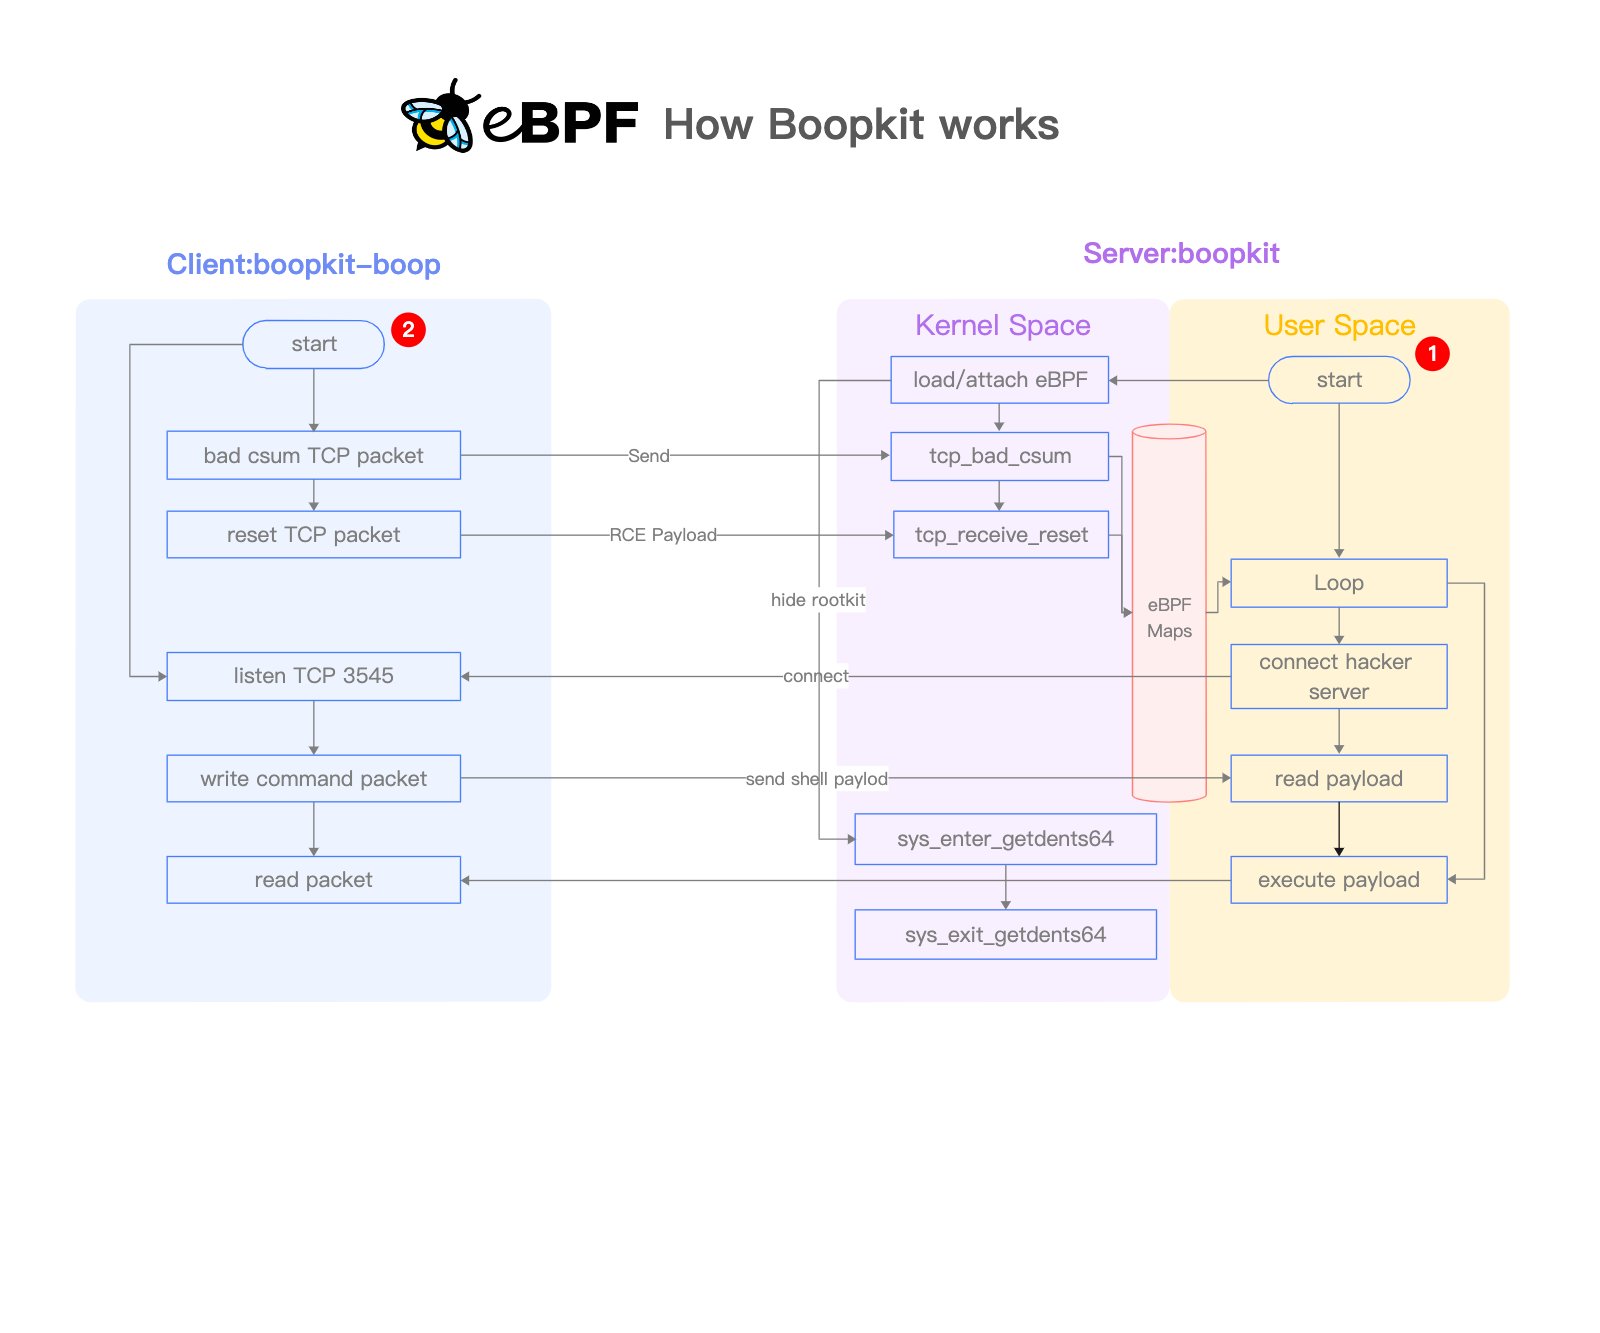 krisnova/boopkit
Linux eBPF backdoor over TCP. Spawn reverse shells, RCE, on prior privileged access. Less Honkin, More Tonkin.
 3v4si0n/http-revshell
Powershell reverse shell using HTTP/S protocol with AMSI bypass and Proxy Aware
 telefonica/ibombshell
Tool to deploy a post-exploitation prompt at any time
 ariary/fileless-xec
Stealth dropper executing remote binaries without dropping them on disk .(HTTP3 support, ICMP support, invisible tracks, cross-platform,...)
 nullsection/chisel-ng
Chisel new generation, written in rust. SSH under WSS with some customization.
 4w4k3/insanity-framework
Generate Payloads and Control Remote Machines. [Discontinued]
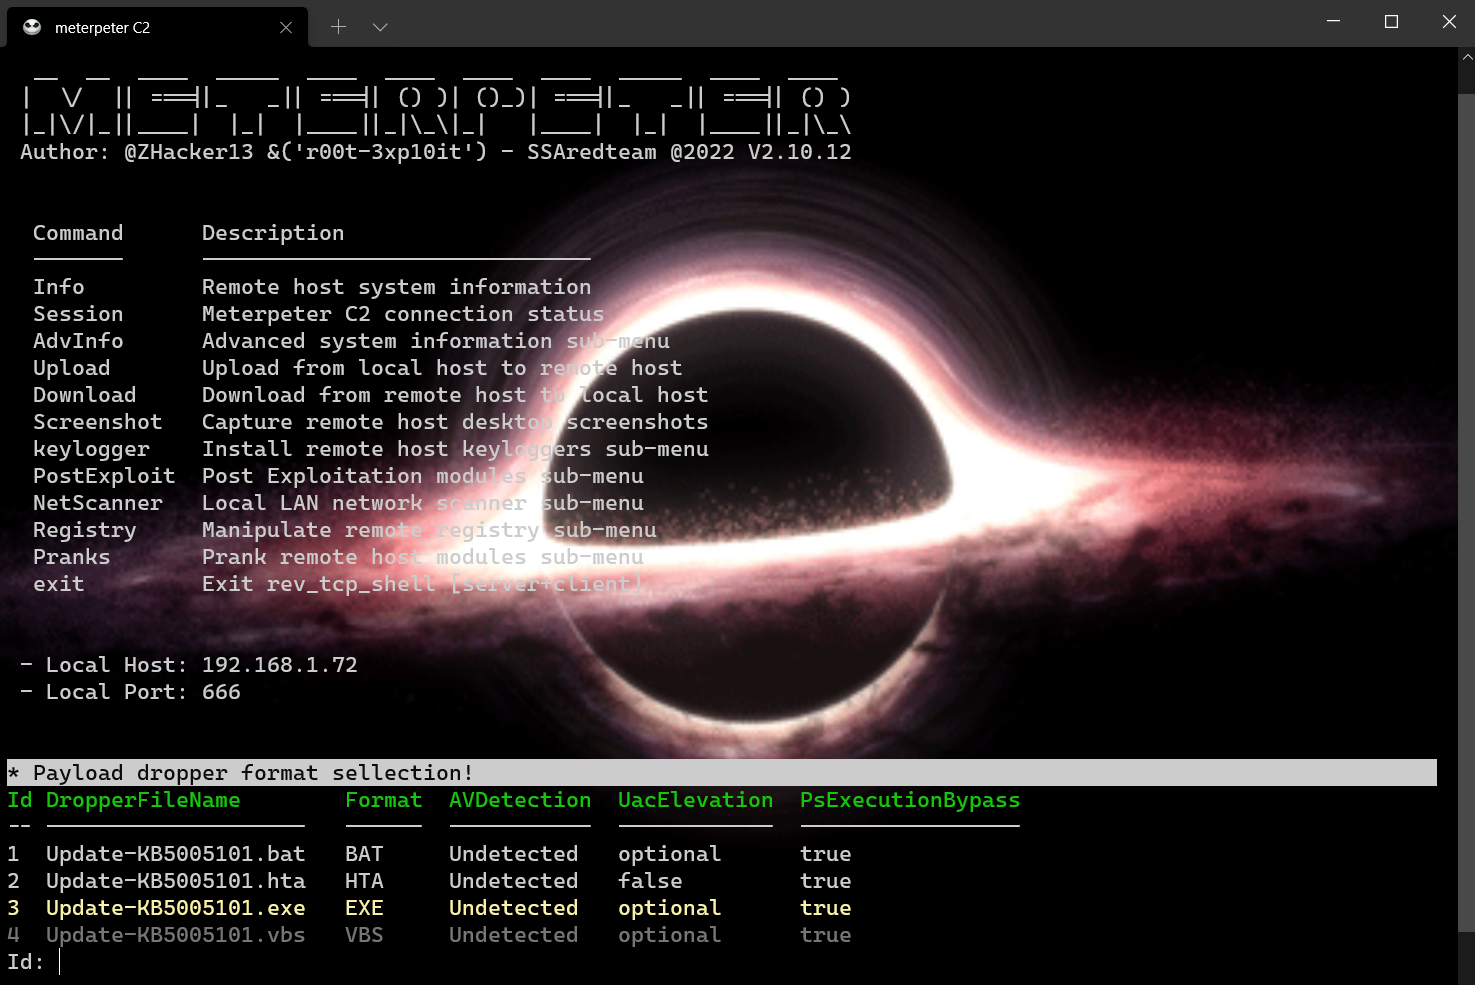 r00t-3xp10it/meterpeter
C2 Powershell Command & Control Framework with BuiltIn Commands
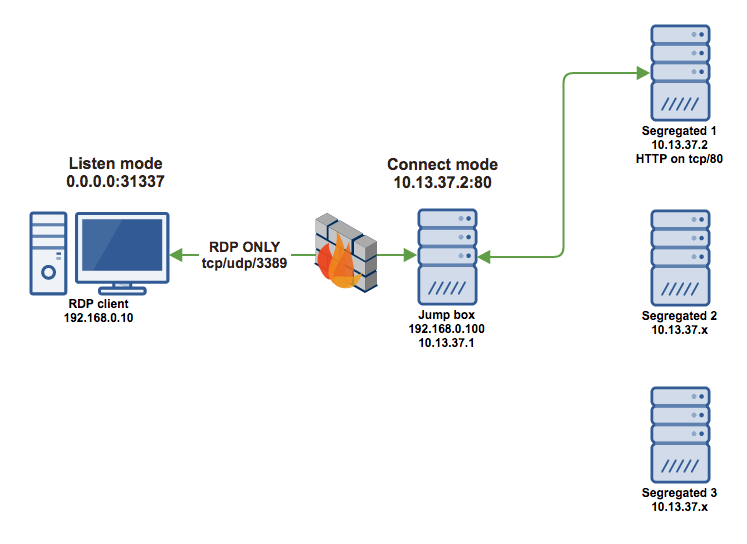 earthquake/universaldvc
Universal Dynamic Virtual Channel connector for Remote Desktop Services