
CVE-2022-1388
 omnigodz/cve-2022-1388
This repository consists of the python exploit for CVE-2022-1388 (F5's BIG-IP Authentication Bypass to RCE)
authentication-authorizationexploitationpenetration-testing+2
omnigodz/cve-2022-1388This repository consists of the python exploit for CVE-2022-1388 (F5's BIG-IP Authentication Bypass to RCE)
 sp00kyskelet0n/py-rdp-patcher
Python script that patches the termsrv.dll file on Windows to enable multiple concurrent RDP sessions, supporting Windows 10 versions 1703 through…
 jas502n/cve-2018-2628
Weblogic 反序列化漏洞(CVE-2018-2628)
 polo35/cve-2020-0022
CVE-2020-0022 vulnerability exploitation on Bouygues BBox Miami (Android TV 8.0 - ARM32 Cortex A9)
 jacobmisirian/dbltekgoippwn
Tool to check if an IP of a DblTek GoIP is vulnerable to a challenge-response login system, send SMS messages from the system, execute remote…
 pritunl/pritunl
Provides distributed enterprise VPN connectivity using OpenVPN, with centralized management, authentication, and encrypted tunnels for cloud and…
 joelgmsec/autordpwn
The Shadow Attack Framework
 superzero/cve-2023-33246
Apache RocketMQ 远程代码执行漏洞(CVE-2023-33246) Exploit
 cyb0r9/androspy
Automated Android backdoor generator with crypter, IP poisoning, and Metasploit payload integration for penetration testing and red team operations.
 nicocha30/ligolo-iwa
A Ligolo-ng JavaScript agent working inside Chrome & Chromium-based browsers by leveraging Isolated Web Applications.
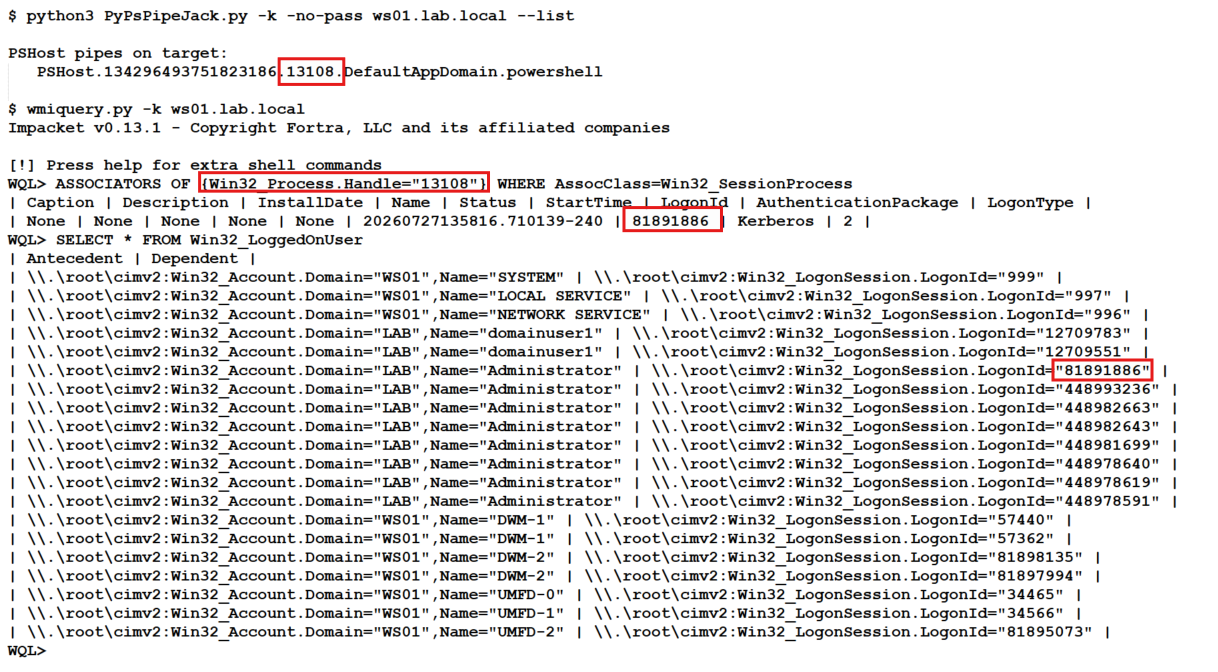 e-fin/pypspipejack
Python implementation of OpenPsPipeJack
 l-urk/cve-2024-6387
Proof of concept python script for regreSSHion exploit.
 cyb0r9/winspy
Generates Windows reverse shell backdoors with automatic IP poisoning, leveraging Metasploit for payload creation and Apache for delivery in…
 0xthirteen/sharpmove
.NET Project for performing Authenticated Remote Execution
 zeyad-azima/cve-2022-1388
F5 BIG-IP iControl REST vulnerability RCE exploit with Java including a testing LAB
 an00byss/doublehop
A Tool to use PowerShell Remoting / WinRM to execute PowerShell commands on remote hosts through WinRM double hop technique.
 gmh5225/gatekeeper
Self-hosted SSH access gateway in Go with OIDC/LDAP auth, RBAC, MFA, session recording, audit export, encryption at rest, IP rules, and policy…
 byt3bl33d3r/pth-toolkit
Modified version of the passing-the-hash tool collection made to work straight out of the box