

Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

··Feeds·Contact·Privacy·© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
60 results
sliver preview

sliver

GitHubbishopfox/sliver

Adversary Emulation Framework

adversarial-attackcommand-and-controldata-exfiltration+16
11.9k4 days ago
Empire preview

Empire

GitHubbc-security/empire

Empire is a post-exploitation and adversary emulation framework that is used to aid Red Teams and Penetration Testers.
adversarial-attackcommand-and-controldata-exfiltration+16
5.3k16 days ago
AllHackingTools preview

AllHackingTools

GitHubmishakorzik/allhackingtools

All-in-One Hacking Tools For Hackers! And more hacking tools! For termux.
crawlerexploitationhash-analysis+8
6.2k7 days ago
CVE-2025-59287 preview

CVE-2025-59287

GitHubgarvitv14/cve-2025-59287

Automated exploit for CVE-2025-59287, an unauthenticated RCE in WSUS, featuring payload generation, reverse shell listener, and AES encryption with…

command-and-controlexploitationpayload-generation+4
1611 months ago
CVE-2023-36845 preview

CVE-2023-36845

GitHubkljunowsky/cve-2023-36845

Proof-of-concept exploit for CVE-2023-36845 enabling unauthenticated remote code execution on Juniper SRX firewalls and EX switches via PHP…
exploitationpenetration-testingreconnaissance+3
552 years ago
Vayne-RaT preview

Vayne-RaT

GitHubthem4hd1/vayne-rat

An Advanced C# .NET Rat, It’s Stable and Contains Many Features.
command-and-controlpassword-crackingpayload-generation+4
2718 years ago
pcileech preview

pcileech

GitHubufrisk/pcileech

Direct Memory Access (DMA) Attack Software

digital-forensicsexploitationhardware-security+7
7.9k2 months ago
AutoRDPwn preview

AutoRDPwn

GitHubjoelgmsec/autordpwn

The Shadow Attack Framework
lateral-movementpassword-crackingpayload-generation+5
1.1k4 years ago
redsnarf preview

redsnarf

GitHubnccgroup/redsnarf

RedSnarf is a pen-testing / red-teaming tool for Windows environments
command-and-controlexploitationhash-analysis+9
1.2k9 years ago
paradoxiaRAT preview

paradoxiaRAT

GitHubquantumcore/paradoxiarat

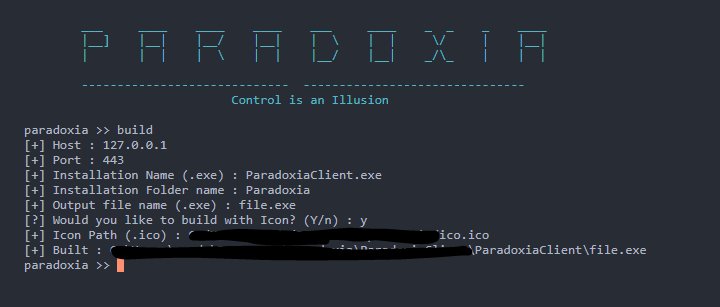
ParadoxiaRat : Native Windows Remote access Tool.
command-and-controlpassword-crackingpenetration-testing+4
8303 years ago
CVE-2024-23692 preview

CVE-2024-23692

GitHubverylazytech/cve-2024-23692

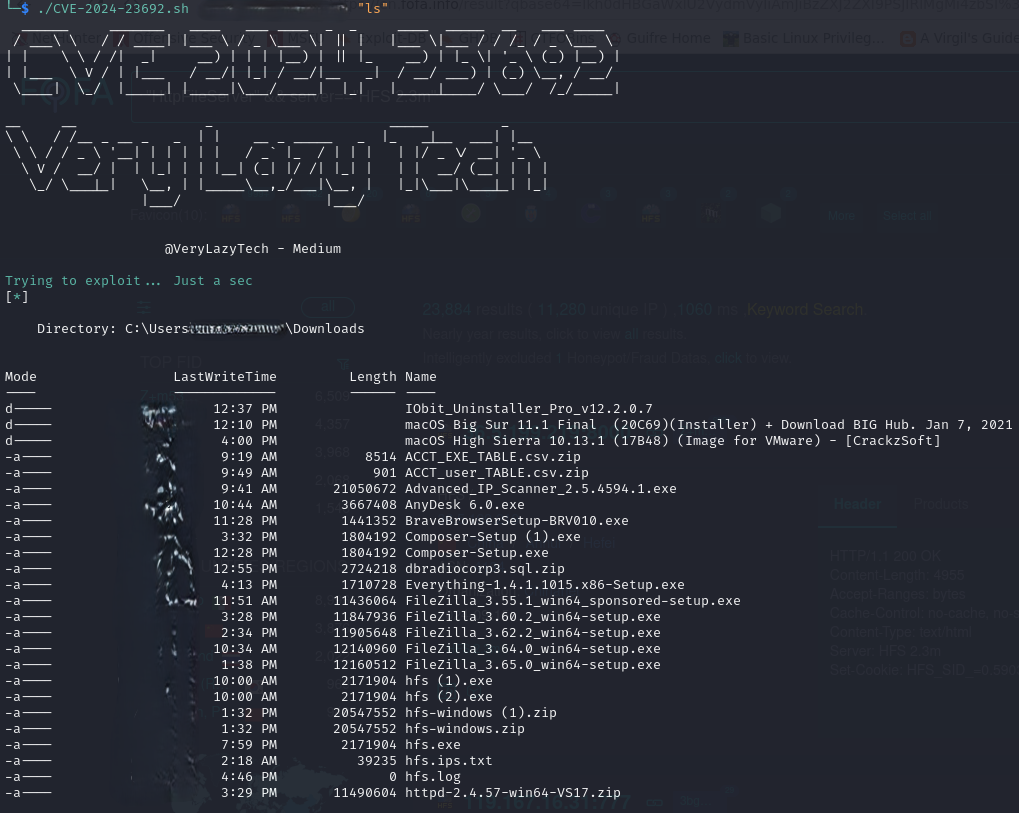
POC - Unauthenticated RCE Flaw in Rejetto HTTP File Server - CVE-2024-23692

exploitationpenetration-testingreconnaissance+3
491 year ago
CVE-2022-26809 preview

CVE-2022-26809

GitHubwebsecnl/cve-2022-26809

Remote Code Execution Exploit in the RPC Library
binary-exploitationexploitationpenetration-testing+2
284 years ago
CVE-2024-6387 preview

CVE-2024-6387

GitHubkarmakstylez/cve-2024-6387

Remote Unauthenticated Code Execution Vulnerability in OpenSSH server (CVE-2024-6387)
exploitationnetwork-securitypenetration-testing+3
1952 years ago
RCE-CVE-2026-10520-CVE-2026-10523 preview

RCE-CVE-2026-10520-CVE-2026-10523

GitHubimbas007/rce-cve-2026-10520-cve-2026-10523

Detection artifact generator for Ivanti Sentry authentication bypass and RCE vulnerabilities (CVE-2026-10520, CVE-2026-10523). Scans single or…
exploitationpenetration-testingreconnaissance+3
1 month ago
ls-poc preview

ls-poc

GitHubtruekas/ls-poc

Proof-of-concept exploit for CVE-2026-30368, demonstrating authentication bypass in Lightspeed Classroom to control student devices via Ably channel.
command-and-controlexploitationpayload-development+3
135 months ago
CVE-2024-6387-poc-1 preview

CVE-2024-6387-poc-1

GitHubanhvutuan/cve-2024-6387-poc-1

CVE-2024-6387, also known as RegreSSHion, is a high-severity vulnerability found in OpenSSH servers (sshd) running on glibc-based Linux systems. It…

exploitationnetwork-securitypenetration-testing+3
22 years ago
CVE-2025-32432-PoC preview

CVE-2025-32432-PoC

GitHubezramansor/cve-2025-32432-poc

A simple PoC on the Remote Code Execution (RCE) Vulnerability of CraftCMS designated as CVE-2025-32432 written in Go
adversarial-attackexploitationpayload-generation+3
1 month ago
tap preview

tap

GitHubtrustedsec/tap

The TrustedSec Attack Platform is a reliable method for droppers on an infrastructure in order to ensure established connections to an organization.

command-and-controlpenetration-testing-frameworkspersistence-mechanisms+3
5053 years ago
Previous1234Next
