awesome-game-security

Curated index of game security research: anti-cheat internals, DMA attacks, reverse engineering, kernel/mobile protections, and graphics API hooking…

Curated index of game security research: anti-cheat internals, DMA attacks, reverse engineering, kernel/mobile protections, and graphics API hooking…

Load your driver like win32k.sys

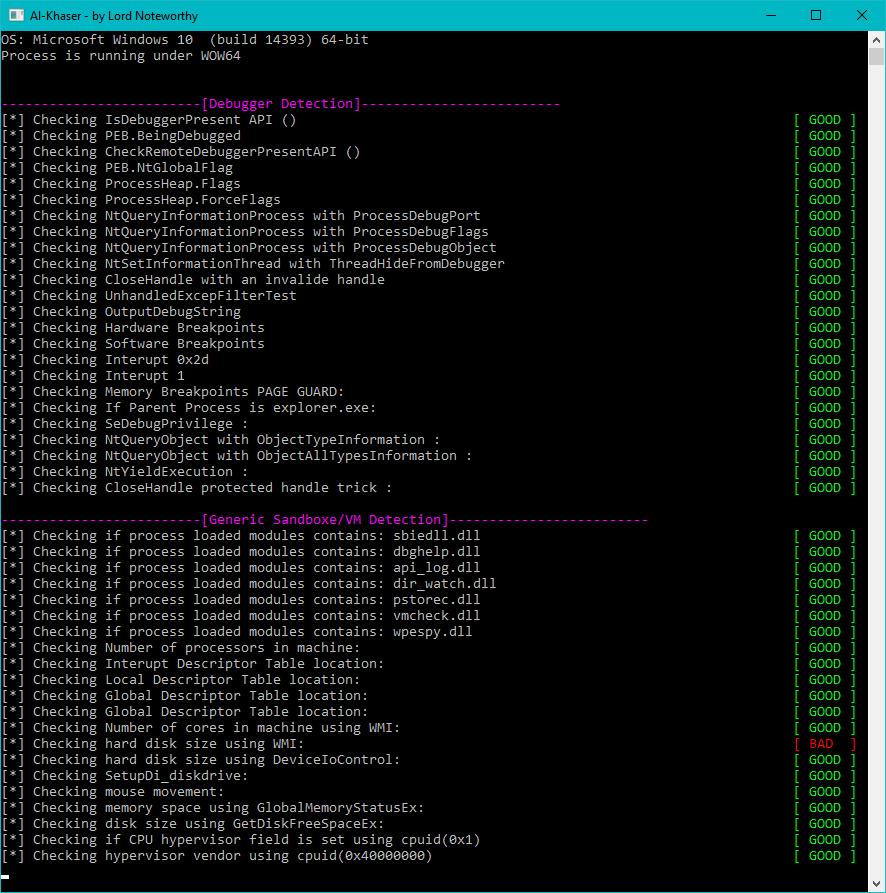
Public malware techniques used in the wild: Virtual Machine, Emulation, Debuggers, Sandbox detection.

This map lists the essential techniques to bypass anti-virus and EDR

Exploitation of echo_driver.sys


E2E encryption for multi-hop tty sessions or portshells + TCP/UDP port forward

The world's fastest agentic crawler. Reclaimed. Reinvented. Ready for war.

LSTAR - CobaltStrike Translated to EN

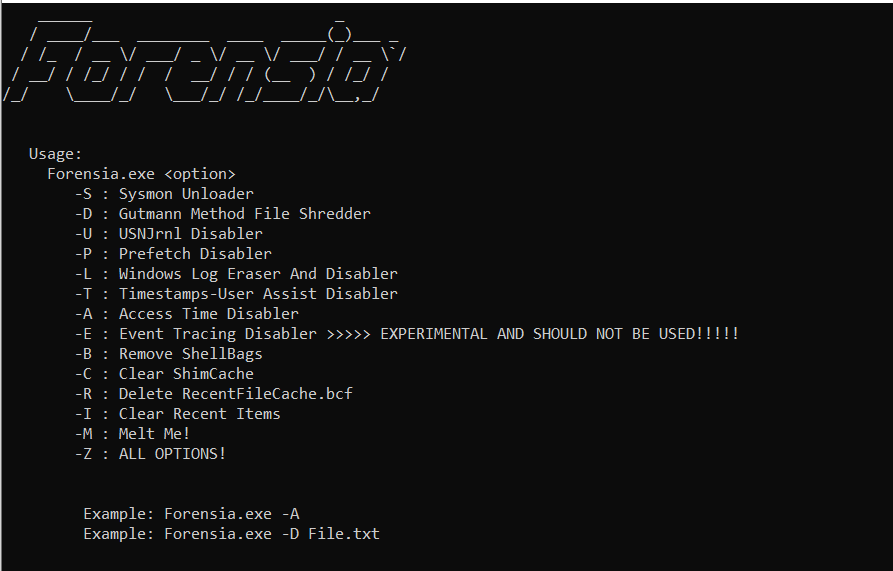
Anti Forensics Tool For Red Teamers, Used For Erasing Footprints In The Post Exploitation Phase.

Exploits a KSLD anti-rootkit driver vulnerability (IOCTL 0x222044) to bypass PPL protection and access sensitive process memory, enabling local…

Academic Research Edition - T1: User-mode evasion (obfuscation + syscall gateway), T2: BYOVD kernel bridge, T3: DMA hardware (future work).

A simple Python CLI to spoof emails.