
wifipumpkin3
 p0cl4bs/wifipumpkin3
Powerful framework for rogue access point attack.
captcha-bypassdns-analysisphishing+5
p0cl4bs/wifipumpkin3Powerful framework for rogue access point attack.
 qyvora/qyvora-toha3ee
Go-based network exploitation and MITM framework for authorized penetration testing, network reconnaissance, traffic interception, wireless security…
 barghest-ngo/mesh
Encrypted peer-to-peer mesh VPN for remote mobile forensics, enabling wireless ADB and libimobiledevice acquisition, network monitoring, and…
 tc4dy/cve-2026-0073-poc-exploit
Zero-click authentication bypass exploit for Android ADB Wireless Debugging (CVE-2026-0073). Provides interactive shell, command execution, and…
 jean-nestor/evil-twin-ap
Automated evil twin access point toolkit with traffic capture and real-time monitoring for wireless penetration testing and security research.

 phantom-brigade1/wifisting
GTK4 and CLI wireless security toolkit with 57 standalone modules for Wi-Fi, Bluetooth, 802.15.4, SDR/RF, NFC and router-side or network MITM testing…
 k4m4/kickthemout
💤 Kick devices off your network by performing an ARP Spoof attack.
 aress31/wirespy
Framework designed to automate various wireless networks attacks (the project was presented on Pentester Academy TV's toolbox in 2017).
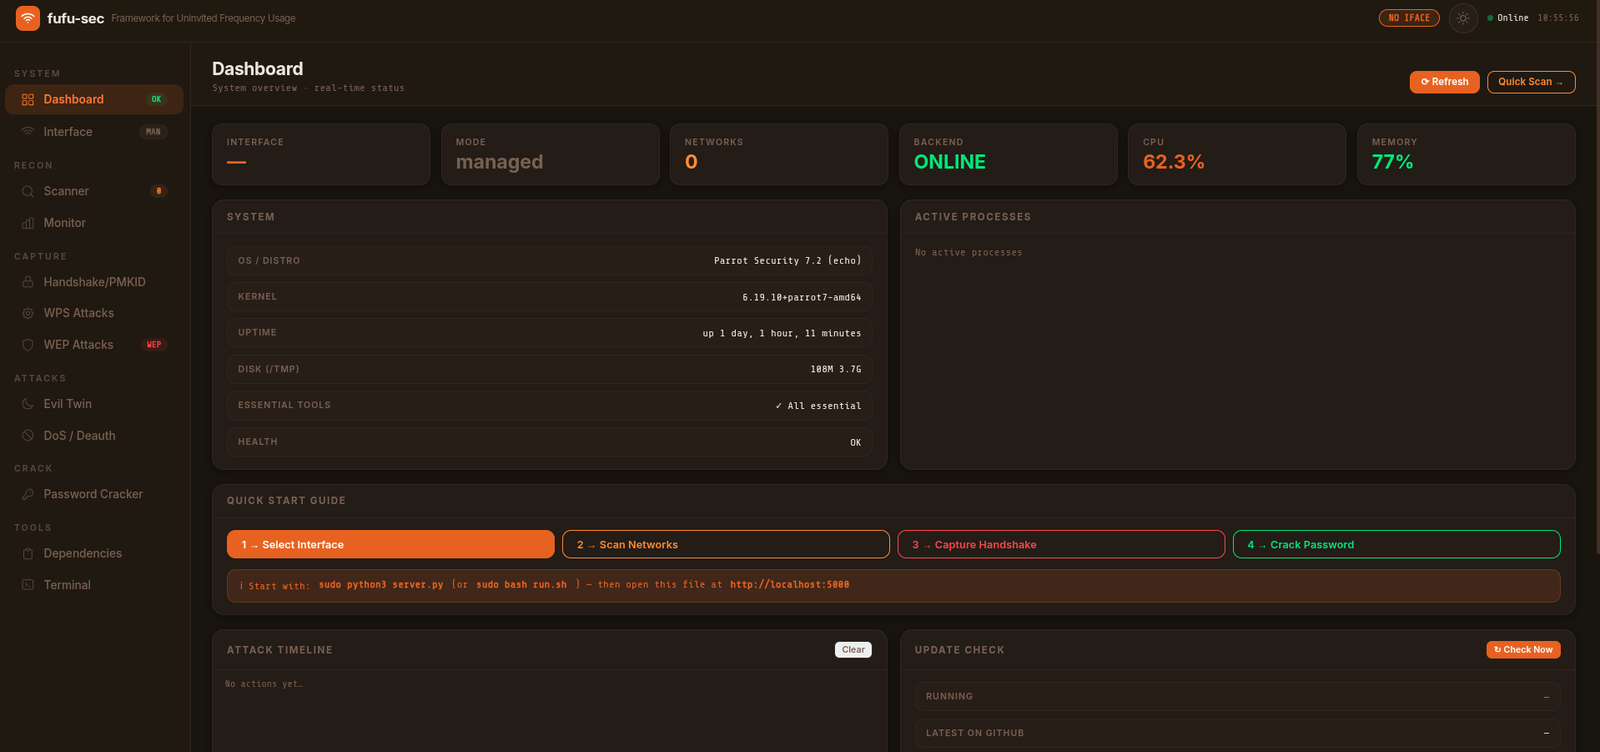 kyllr-qwen/fufu-sec
Framework for Uninvited Frequency Usage
 calebmadrigal/trackerjacker
Like nmap for mapping wifi networks you're not connected to, plus device tracking
 infamoussyn/rogue
An extensible toolkit providing penetration testers an easy-to-use platform to deploy Access Points during penetration testing and red team…
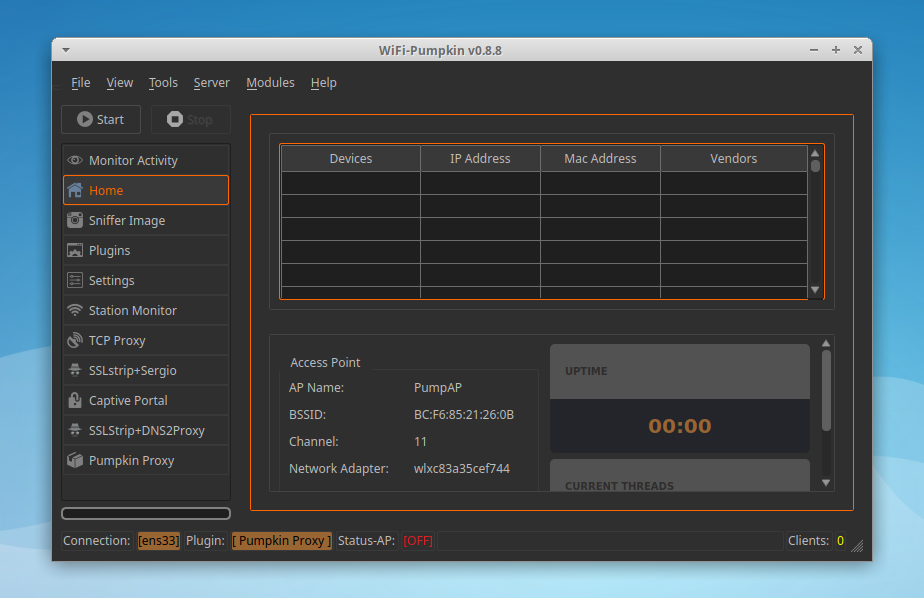 p0cl4bs/wifi-pumpkin-deprecated
DEPRECATED, wifipumpkin3 -> https://github.com/P0cL4bs/wifipumpkin3
 xdavidhu/mitmap
📡 A python program to create a fake AP and sniff data.
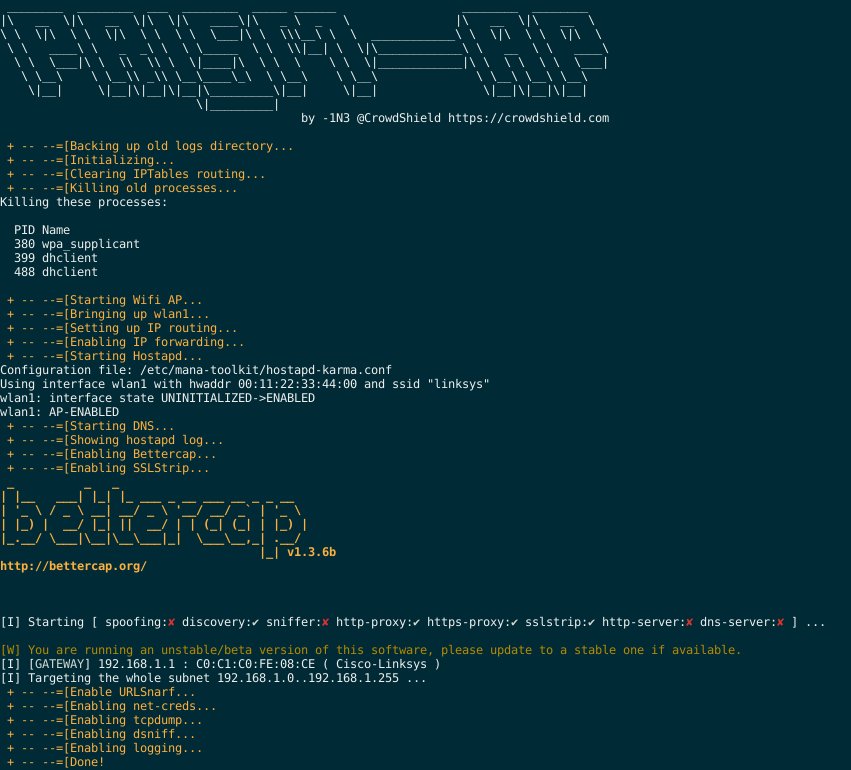 1n3/prism-ap
An automated Wireless RogueAP MITM attack framework.
 momenbasel/autowifi
Wireless penetration testing framework. Automates WPA/WPA2/WEP/WPS attacks - recon to exploitation in one command. aircrack-ng + hashcat + PMKID.
 yslxotwod/wifisting
GTK4 wireless security toolkit with 57 standalone shell modules for Wi-Fi, Bluetooth, RF, Zigbee, NFC and router-side attacks, plus MITM, recon,…
 cifertech/esp32-div
ESP32DIV is a multi-purpose wireless offensive and defensive toolkit powered by an ESP32
 aircrack-ng/rtl8812au
Linux/Android kernel driver for RTL8812AU/21AU and RTL8814AU chipsets with monitor mode and frame injection support for wireless security testing.