
ESP-RFID-Tool
 rfidtool/esp-rfid-tool
A tool for logging data/testing devices with a Wiegand Interface. Can be used to create a portable RFID reader or installed directly into an existing…
embedded-systems-securityfuzzinghardware-hacking+5
588
rfidtool/esp-rfid-toolA tool for logging data/testing devices with a Wiegand Interface. Can be used to create a portable RFID reader or installed directly into an existing…
 aryanrtm/kawaiideauther
Jam all wifi clients/routers.
 p0cl4bs/wifi-pumpkin-deprecated
DEPRECATED, wifipumpkin3 -> https://github.com/P0cL4bs/wifipumpkin3
 geniuszly/genwififaker
is a tool for creating fake WiFi access points
 danmcinerney/wifijammer
Continuously jam all wifi clients/routers
 martinpsdev/cve-2026-0073-android-adbd-bypass-poc
CVE-2026-0073 — Android ADB daemon (adbd) TLS authentication bypass via EVP_PKEY_cmp type confusion. Gain unauthorized shell access over WiFi using…
 roostercoopllc/flipper-mcp
AI-powered MCP server for Flipper Zero. Control SubGHz, NFC, RFID, IR, BLE, GPIO, and more over WiFi using Claude or any MCP client.
 d4rkcat/killosx
use the Apple CoreText exploit (CVE-2012-3716) and launch an AP to affect all devices within wifi range
 blackhillsinfosec/wififorge
Automated WiFi hacking lab environment using mininet-wifi to simulate wireless attack vectors for pentester training, eliminating hardware overhead.
 oblique/create_ap
[NOT MAINTAINED] This script creates a NATed or Bridged WiFi Access Point.
 riccardocataldi/access-point
Rogue open Wi-Fi AP for controlled traffic capture using hostapd, dnsmasq, and iptables NAT. Enables real-time client monitoring, DNS/DHCP logging,…
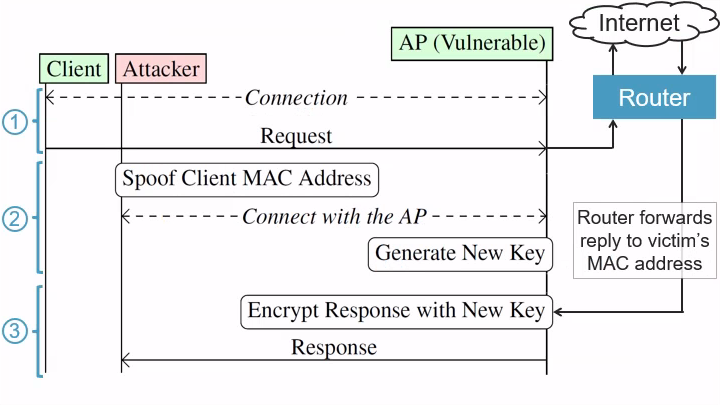 vanhoefm/macstealer
MacStealer: Wi-Fi Client Isolation Bypass
 xdavidhu/mitmap
📡 A python program to create a fake AP and sniff data.
 k4m4/kickthemout
💤 Kick devices off your network by performing an ARP Spoof attack.
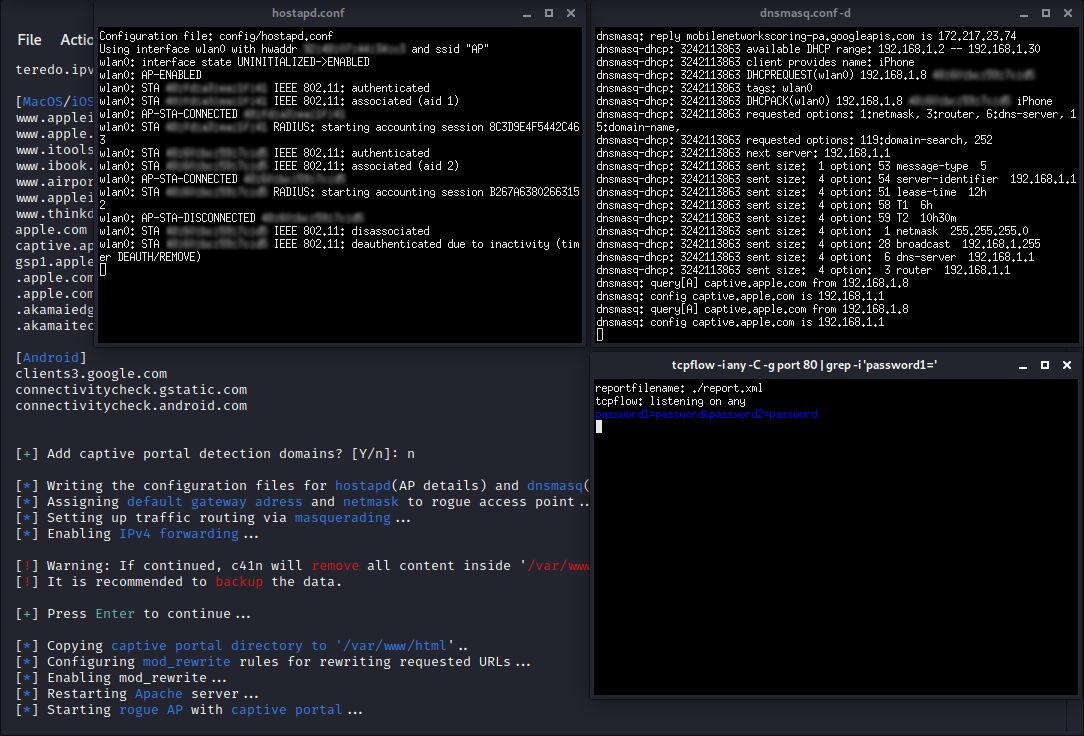 ms-web-bn/c41n
Automated rogue access point setup tool.
 wifiphisher/wifiphisher
Rogue Access Point framework for red team engagements and Wi-Fi security testing. Performs Evil Twin, KARMA, and Known Beacons attacks to achieve…
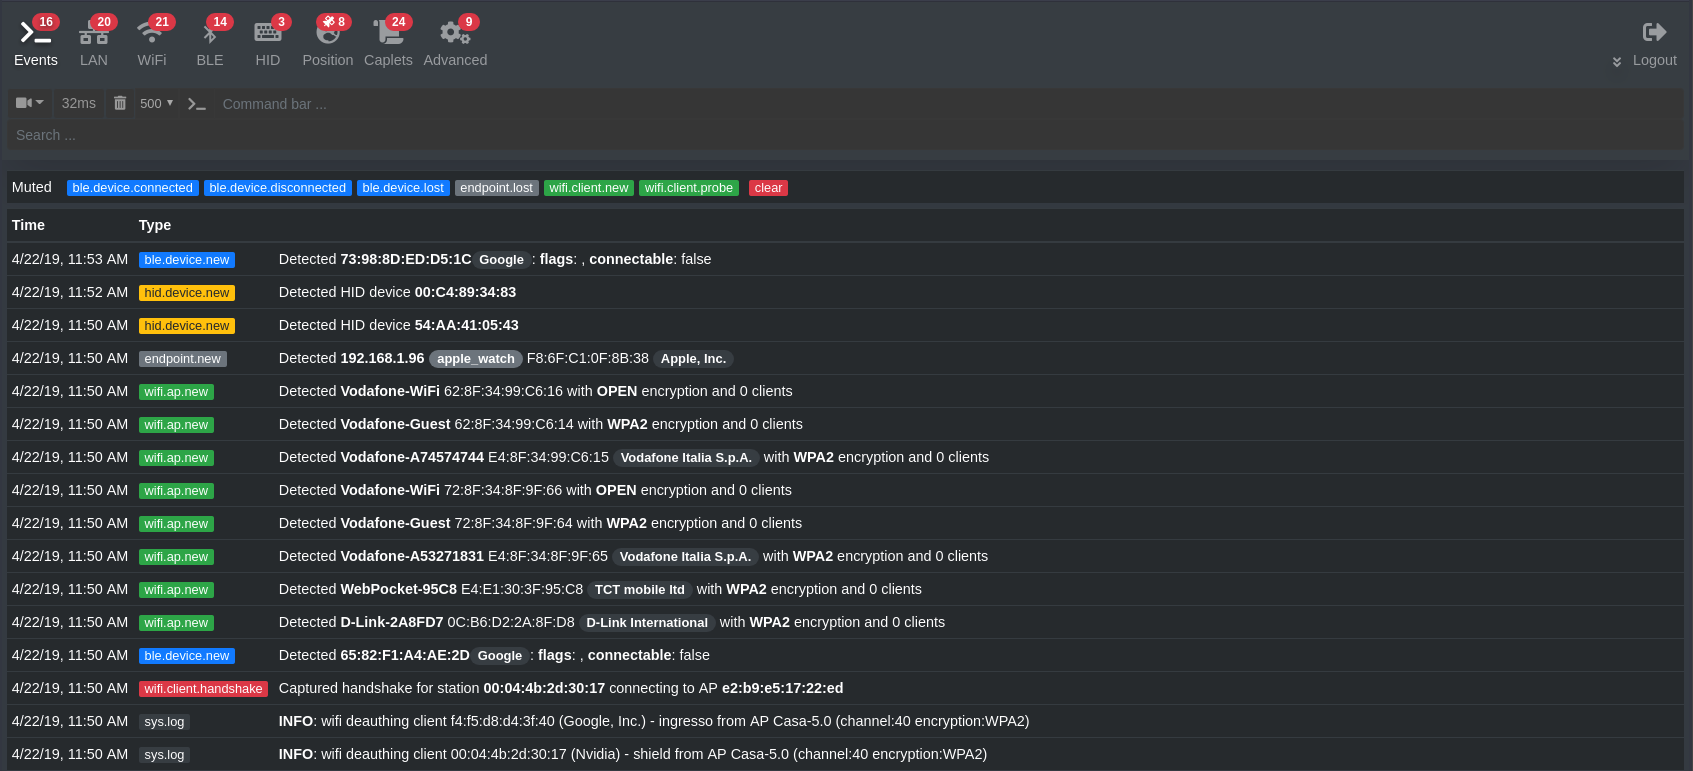 bettercap/bettercap
The Swiss Army knife for 802.11, BLE, HID, CAN-bus, IPv4 and IPv6 networks reconnaissance and MITM attacks.
 cifertech/esp32-div
ESP32DIV is a multi-purpose wireless offensive and defensive toolkit powered by an ESP32