

Facad1ng
 spyboy-productions/facad1ng
Open-source URL masking & analysis tool for security research, phishing awareness, and defensive testing. Demonstrates adversary techniques used to…
defensive-toolseducationphishing+3
529
spyboy-productions/facad1ngOpen-source URL masking & analysis tool for security research, phishing awareness, and defensive testing. Demonstrates adversary techniques used to…
 iamblacksolo2-bugbounty/poc-cve-2025-55182
Bash-based scanner for detecting and exploiting CVE-2025-55182 (React Server Components RCE) in Next.js applications. Supports custom command…
 layer-6/cve-2026-5027-langflow
Multi-CVE exploit tool for pre-auth remote code execution on Ivanti Sentry and FortiSandbox. Features interactive shell, webshell deployment,…
 kimtangker/cve-2024-46256
CVE-2024-46256 tool
 hoav18/cve-2021-22941
Python exploit for CVE-2021-22941 targeting Citrix ShareFile RCE with shell and ping options for remote command execution and network probing.
 vanboomqi/cve-2024-23692
Python exploit script for CVE-2024-23692, a template injection RCE in Rejetto HFS 2.3m. Supports single and batch URL exploitation with custom…
 nccgroup/clickjacking-poc
Clickjacking PoC Generator
 securitycipher/cve-2023-24488
POC for CVE-2023-24488
 lemonteatw1/cve-2025-55182-exploit
Python-based proof-of-concept exploit for CVE-2025-55182, targeting web applications via URL parameter injection for authorized penetration testing.
 devbuihieu/cve-2025-33053-proof-of-concept
CVE-2025-33053 Proof Of Concept (PoC)
 pumpkinpiteam/cve-2022-24716
Python exploit for CVE-2022-24716: arbitrary file disclosure in Icinga Web 2 versions <2.8.6, <2.9.6, <2.10. Usage: python3 exploit.py -u <url> -f…
 10cks/cve-2014-6287
Rejetto http File Server 2.3.x (Reverse shell)
 kra1t0/cve-2025-33053-webdav-rce-poc-and-c2-concept
Proof-of-Concept for CVE-2025-33053 Exploiting WebDAV with .url file delivery to demonstrate realistic remote code execution. Includes a decoy PDF…
 hackinglz/ip-obfuscation
Generates obfuscated IP addresses and URLs using DWORD, octal, hex, IPv6-mapped, and fake-domain @ tricks for penetration testing, phishing…
 hev0x/cve-2022-29464
Python-based exploit for WSO2 RCE (CVE-2022-29464) supporting multi-target scanning via URL list input.
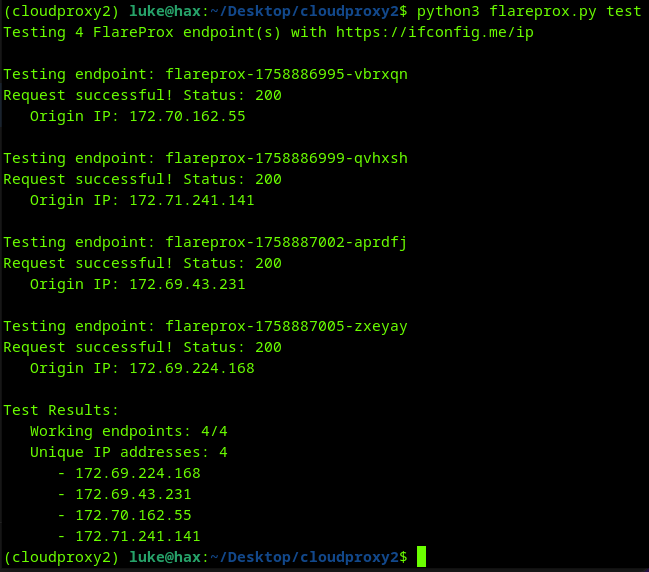 mrturvey/flareprox
Use Cloudflare to create HTTP pass-through proxies for unique IP rotation, similar to fireprox
 holygu/cve-2023-42442
Go-based exploit for JumpServer unauthorized access vulnerability (CVE-2023-42442) with a single-command execution interface for penetration testing.
 mbanyamer/cve-2026-27180-majordomo-unauthenticated-rce
Proof-of-concept exploit for CVE-2026-27180, an unauthenticated RCE in MajorDoMo via update URL poisoning, delivering a webshell to the web root.