
Antecursor
 antecursor/antecursor
Autonomous and modular system for network based information gathering and exploitation. WEB interface here: https://antecursor.fr/ More info…
command-and-controlexploitationhardware-iot-security+5
5
antecursor/antecursorAutonomous and modular system for network based information gathering and exploitation. WEB interface here: https://antecursor.fr/ More info…

 mandatoryprogrammer/sonar.js
A framework for identifying and launching exploits against internal network hosts. Works via WebRTC IP enumeration combined with WebSockets and…
 machine1337/telegramrat
Cross Platform Telegram based RAT that communicates via telegram to evade network restrictions
 chrizator/netattack2
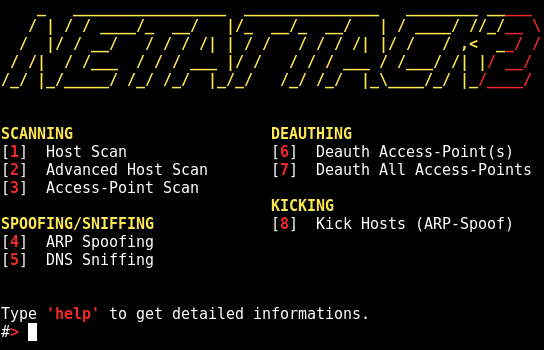
An advanced network scan and attack script based on GUI. 2nd version of no-GUI netattack.
 y0oshi/project-deep-focus
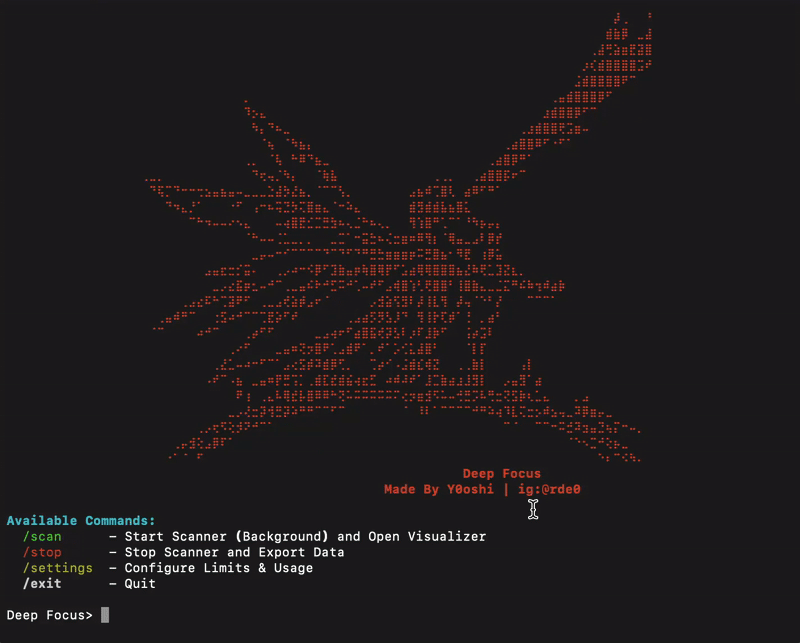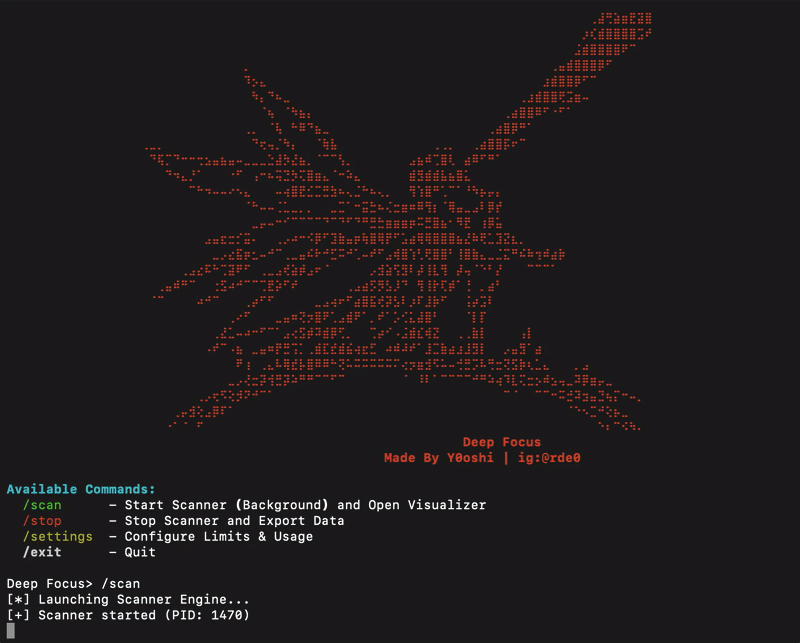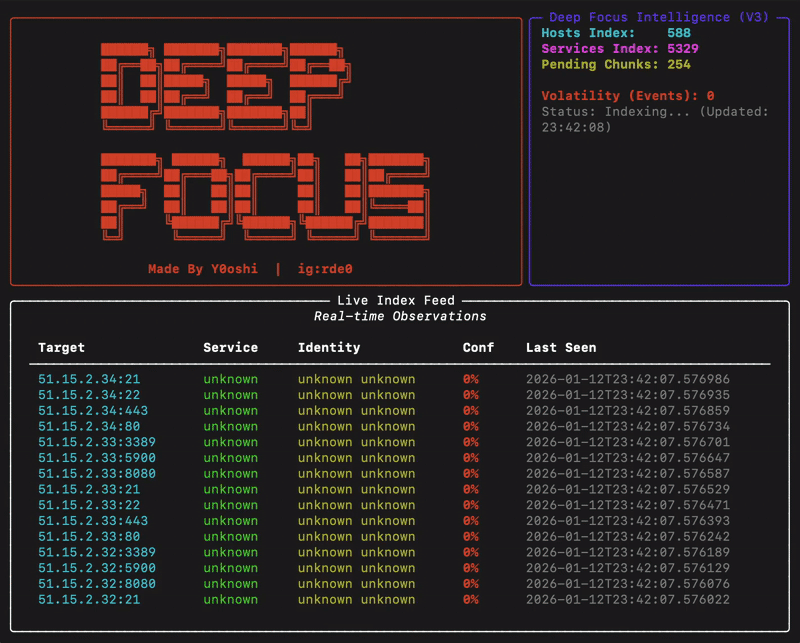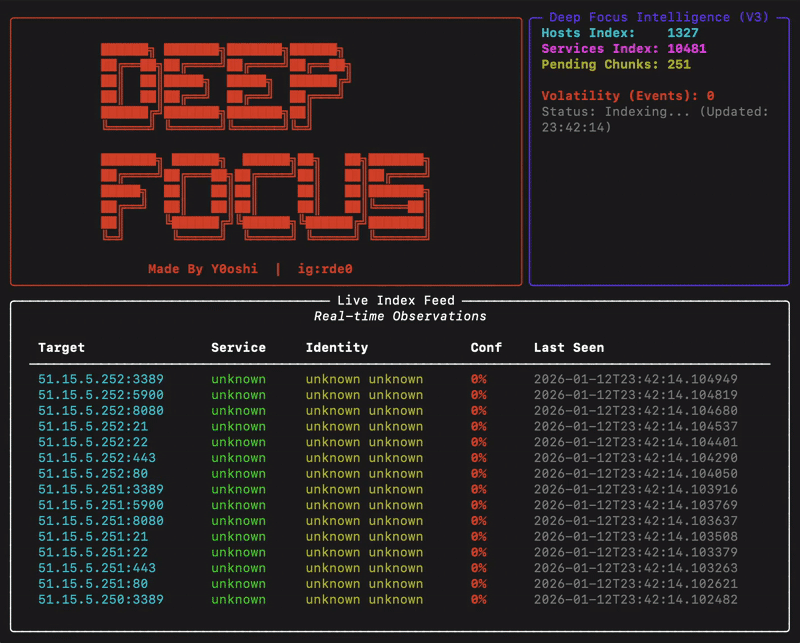
Asynchronous network reconnaissance engine for large-scale service discovery and fingerprinting. Identifies unsecured services (RTSP cameras, VNC,…
 aleksamcode/preferred-network-list-sniffer
A reconnaissance tool for capturing and displaying SSIDs from device's Preferred Network List.
 darkoperator/veil-powerview
PowerShell toolkit for Active Directory reconnaissance and network situational awareness, enabling domain enumeration, privilege escalation path…
 blue0x1/nimux
Pure-Nim network enumeration and remote execution toolkit for authorized security assessments. Supports SMB, LDAP, Kerberos, WinRM, database clients,…
 cappricio-securities/ipchanger
IPChanger is a lightweight command-line tool designed for ethical hackers, security researchers, and privacy enthusiasts. It allows users to…
 stiffies/airscout
A nice tool that automates network hash capturing and has a nice GUI. Read README.md for more information and NEVER use this without explicit…
 netomize/http-basma
In the realm of cybersecurity, accurately identifying and characterizing web servers is crucial for threat detection, vulnerability assessment, and…
 astaruf/cve-2026-42281
Proof-of-concept exploit for CVE-2026-42281, an unauthenticated SSRF in MagicMirror² ≤ 2.35.0, enabling config exfiltration, cloud metadata probing,…
 niker-lixy/postex
Windows post-exploitation reconnaissance agent that collects system info, privileges, patches, defenses, network config, credentials, and persistence…
 spiderlabs/portia
Portia aims to automate a number of techniques commonly performed on internal network penetration tests after a low privileged account has been…
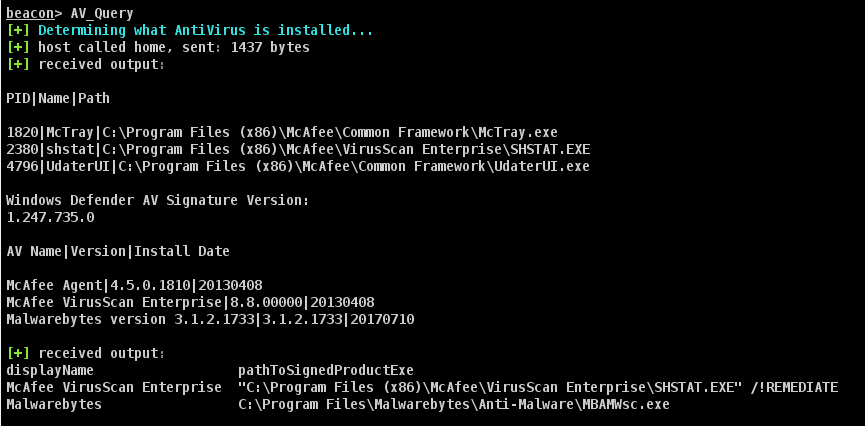 harleyqu1nn/aggressorscripts
Collection of Aggressor scripts for Cobalt Strike 3.0+ pulled from multiple sources
 nh-red-team/rusthound
Active Directory data ingestor for BloodHound Legacy written in Rust. 🦀
 punk-security/smbeagle
SMBeagle - Fileshare auditing tool.
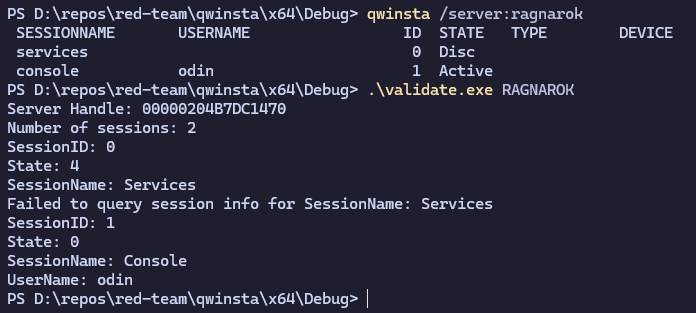 0xv1n/remotesessionenum
Remotely Enumerate sessions using undocumented Windows Station APIs