
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
39 results
iodine preview

iodine

GitHubyarrick/iodine

Tunnel IPv4 data through DNS servers to bypass firewall restrictions and provide covert network access for penetration testing.

command-and-controldata-exfiltrationids-ips-evasion+4
8.0k
4 days ago
CVE-2022-36446-Webmin-Software-Package-Updates-RCE preview

CVE-2022-36446-Webmin-Software-Package-Updates-RCE

GitHubp0dalirius/cve-2022-36446-webmin-software-package-updates-rce

A Python script to exploit CVE-2022-36446 Software Package Updates RCE (Authenticated) on Webmin < 1.997.

command-and-controlexploitationpenetration-testing+3
1151 year ago
ship-safe preview

ship-safe

GitHubasamassekou10/ship-safe

The independent security agent for AI-written software. Finds issues, investigates whether they are real, and shows you the evidence. Deterministic…
ai-securityapi-security-testingcloud-infrastructure-security+8
84913 days ago
wePWNise preview

wePWNise

GitHubreverseclabs/wepwnise

WePWNise generates architecture independent VBA code to be used in Office documents or templates and automates bypassing application control and…
exploit-frameworksids-ips-evasionpayload-development+5
3498 years ago
doublepulsar-usermode-injector preview

doublepulsar-usermode-injector

GitHubwithsecurelabs/doublepulsar-usermode-injector

A utility to use the usermode shellcode from the DOUBLEPULSAR payload to reflectively load an arbitrary DLL into another process, for use in testing…

exploitationmalware-analysispayload-development+2
1229 years ago
deepin-linux_reader_RCE-exploit preview

deepin-linux_reader_RCE-exploit

GitHubfebinrev/deepin-linux_reader_rce-exploit

CVE-2023-50254: PoC Exploit for Deepin-reader RCE that affects unpatched Deepin Linux Desktops. Deepin Linux's default document reader…
exploitationpayload-developmentpenetration-testing+3
162 years ago
metabase-pre-auth-rce-poc preview

metabase-pre-auth-rce-poc

GitHubm3m0o/metabase-pre-auth-rce-poc

This is a script written in Python that allows the exploitation of the Metabase's software security flaw described in CVE-2023-38646.
exploitationpenetration-testingred-teaming+3
22 years ago
EpSiLoNPoInTlnk preview

EpSiLoNPoInTlnk

GitHubepsilonpointori/epsilonpointlnk

Generates obfuscated .lnk files exploiting CVE-2026-21510 with LNK stomping, encrypted payloads, and anti-forensics for authorized penetration…
anti-botexploitationmalware-analysis+4
24 months ago
cve-2024-6387-nuclei-template preview

cve-2024-6387-nuclei-template

GitHubbrandonlynch2402/cve-2024-6387-nuclei-template

Nuclei template to detect OpenSSH servers vulnerable to CVE-2024-6387 (regreSSHion) by checking software version.
exploitationpenetration-testingred-teaming+3
32 years ago
CTT-Mailpit-RCE-v1.0---Temporal-Resonance-Mail-Server-Takeover preview

CTT-Mailpit-RCE-v1.0---Temporal-Resonance-Mail-Server-Takeover

GitHubsimoesctt/ctt-mailpit-rce-v1.0---temporal-resonance-mail-server-takeover

Exploit tool that transforms SMTP header injection into remote code execution with self-propagating worm capabilities, featuring persistence…
command-and-controlexploitationmalware-analysis+5
8 months ago
PoC-Exploit-CVE-2024-20467 preview

PoC-Exploit-CVE-2024-20467

GitHubsaler-cve/poc-exploit-cve-2024-20467

Proof-of-concept exploit for CVE-2024-20467, a remote denial-of-service vulnerability in Cisco IOS XE Software. Sends crafted fragmented IPv4 packets…
exploitationnetwork-securitypenetration-testing+2
2 years ago
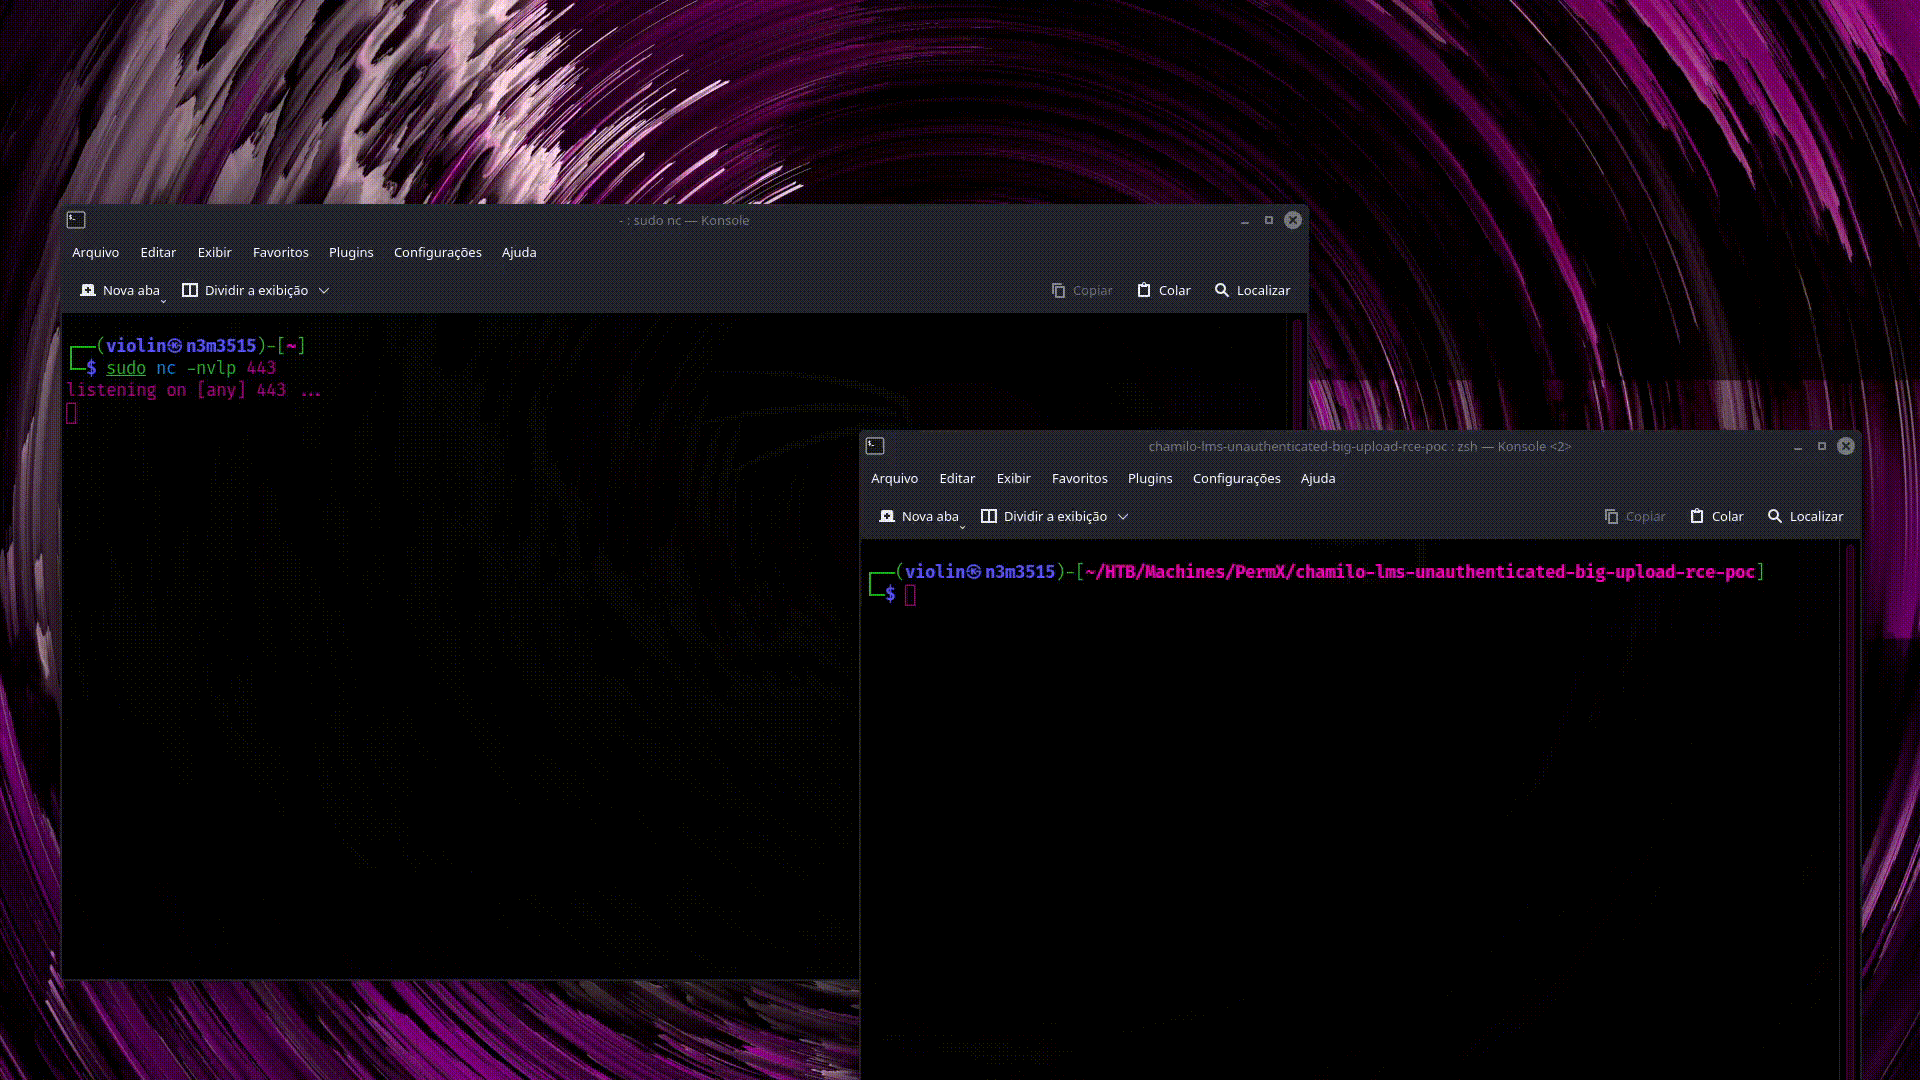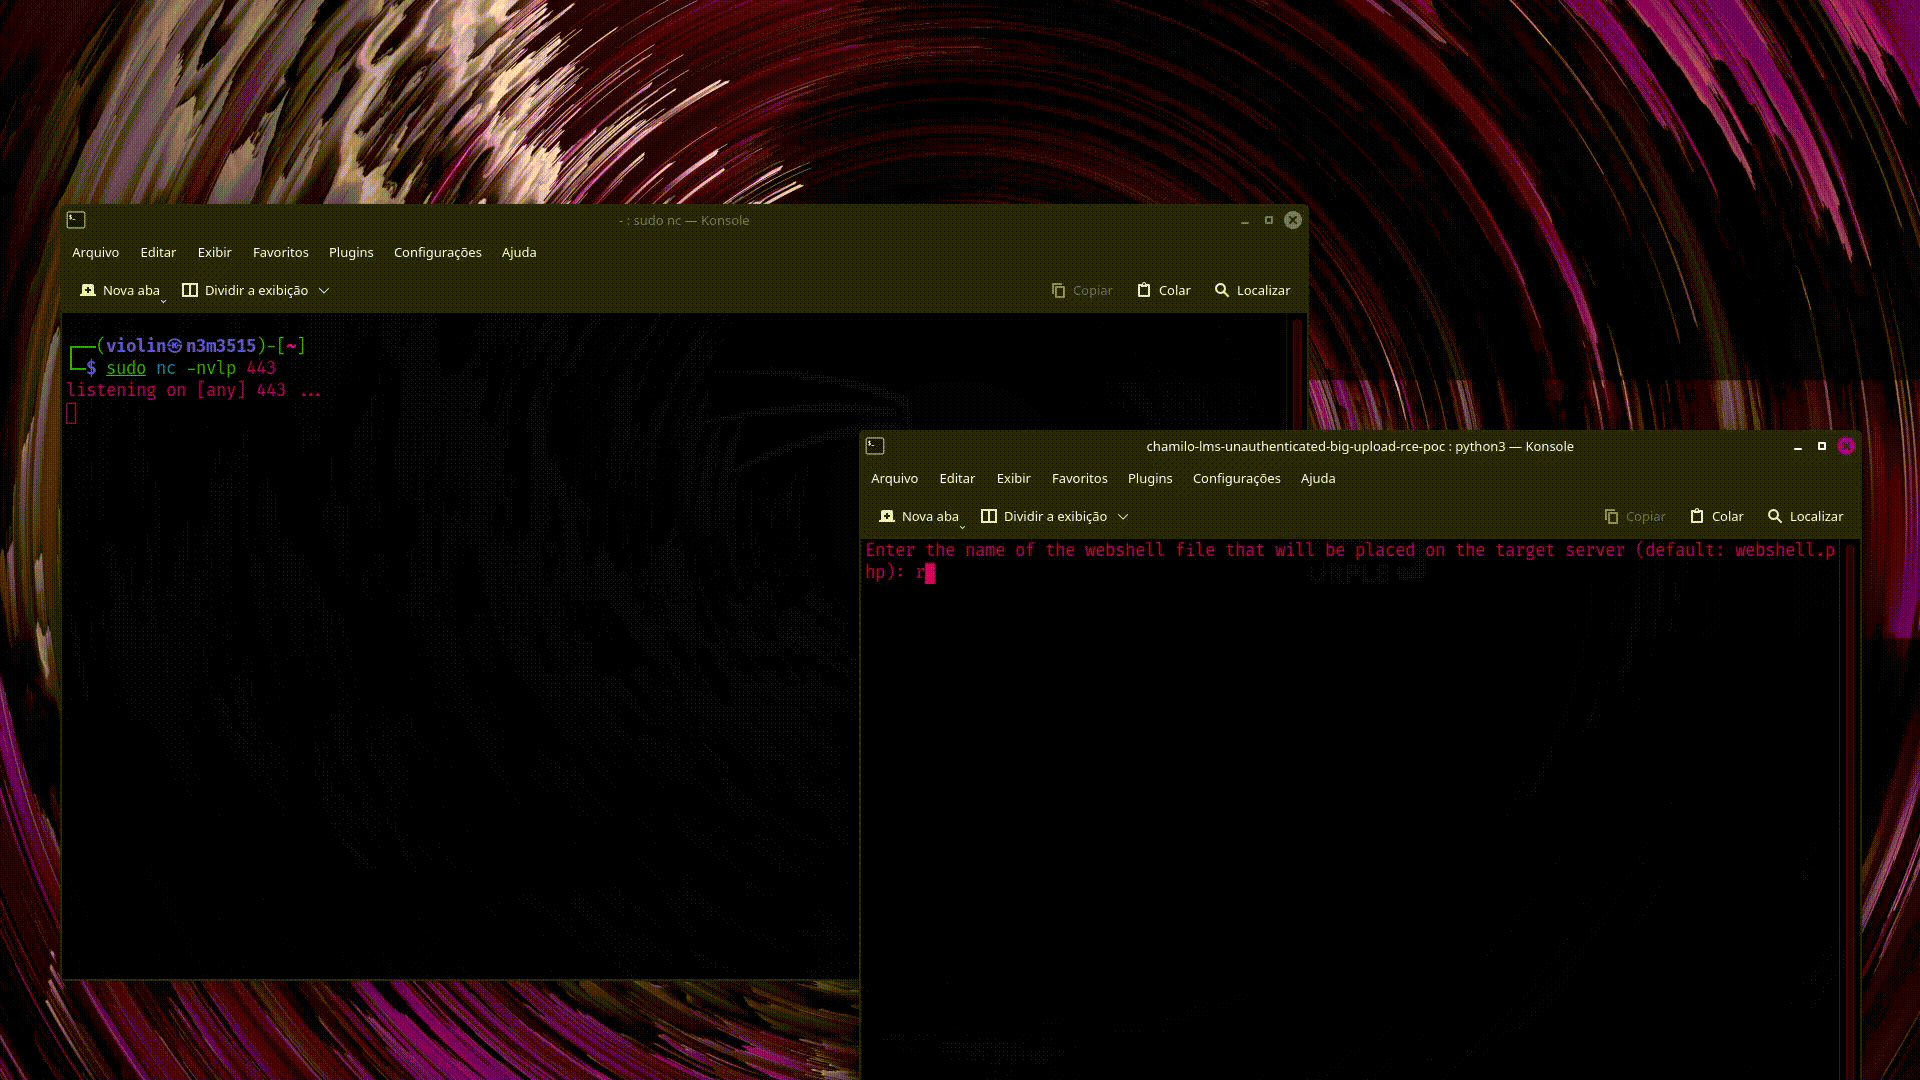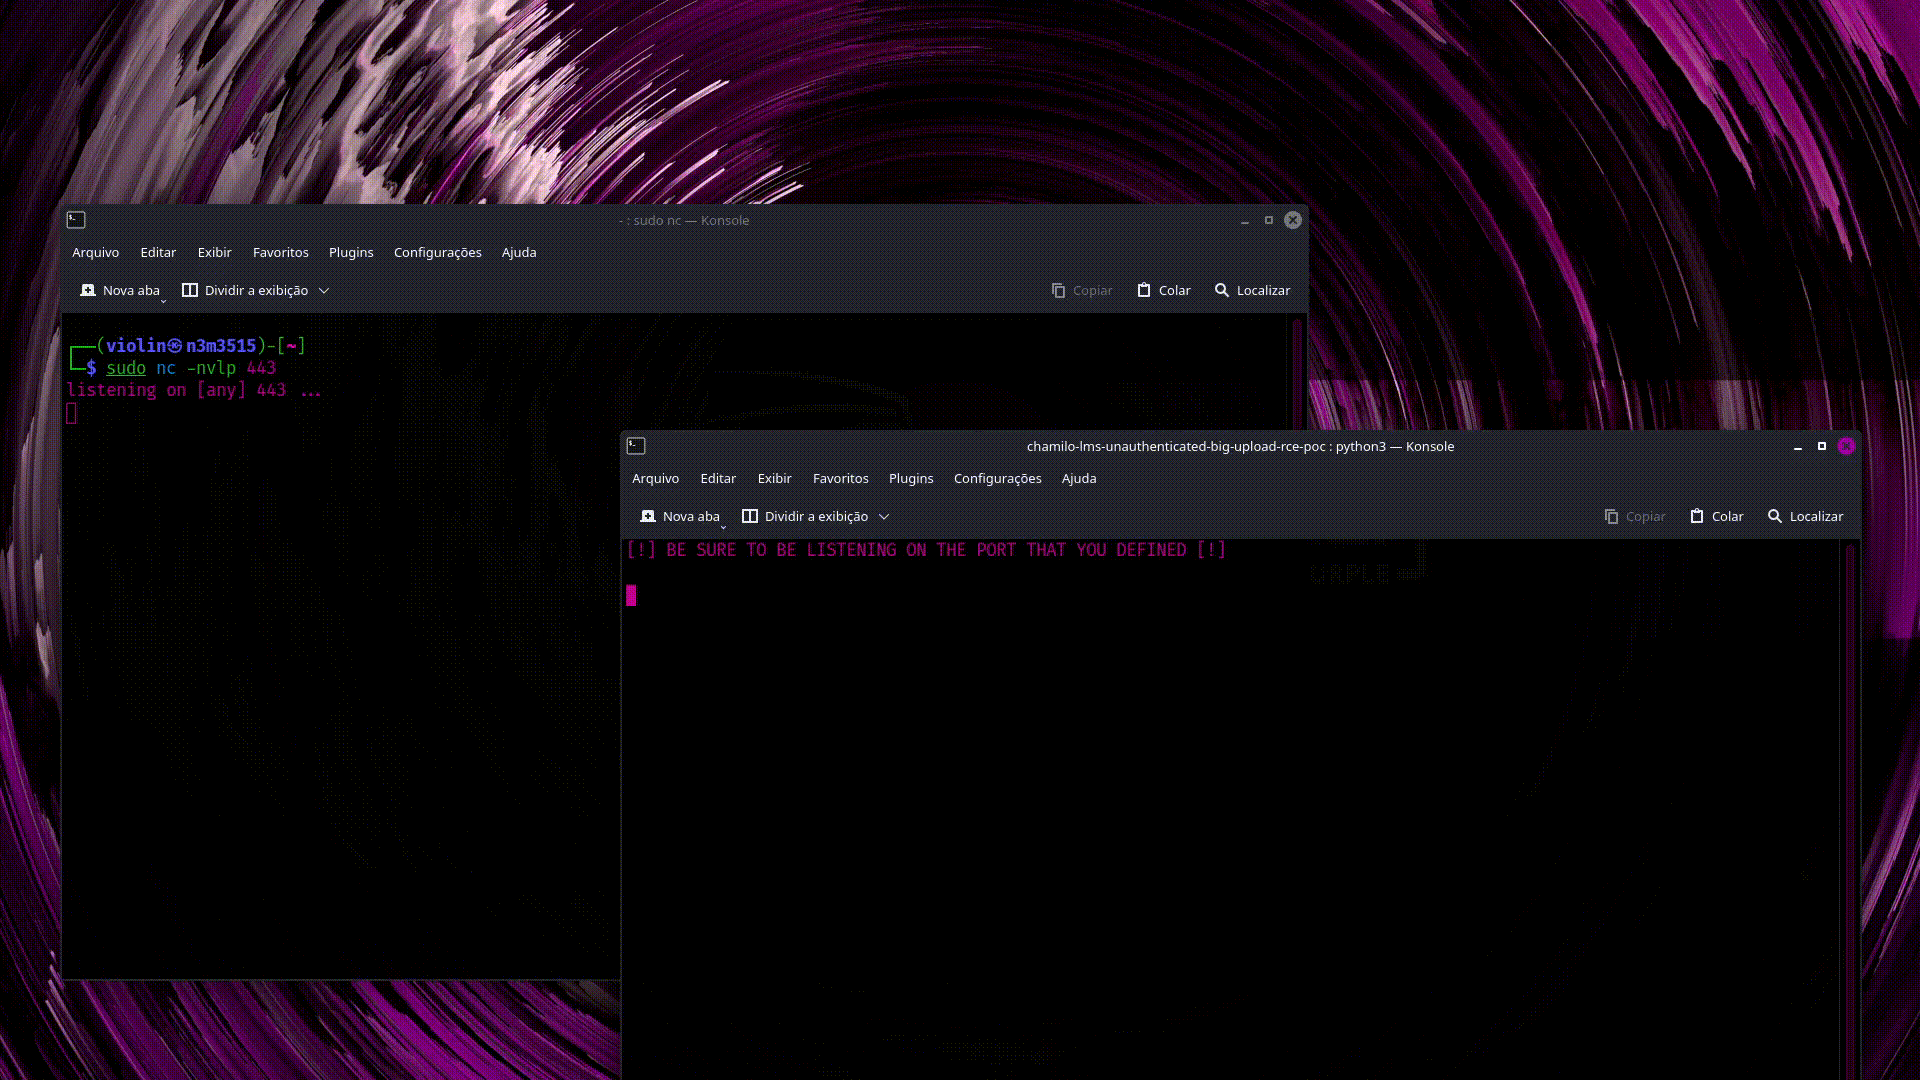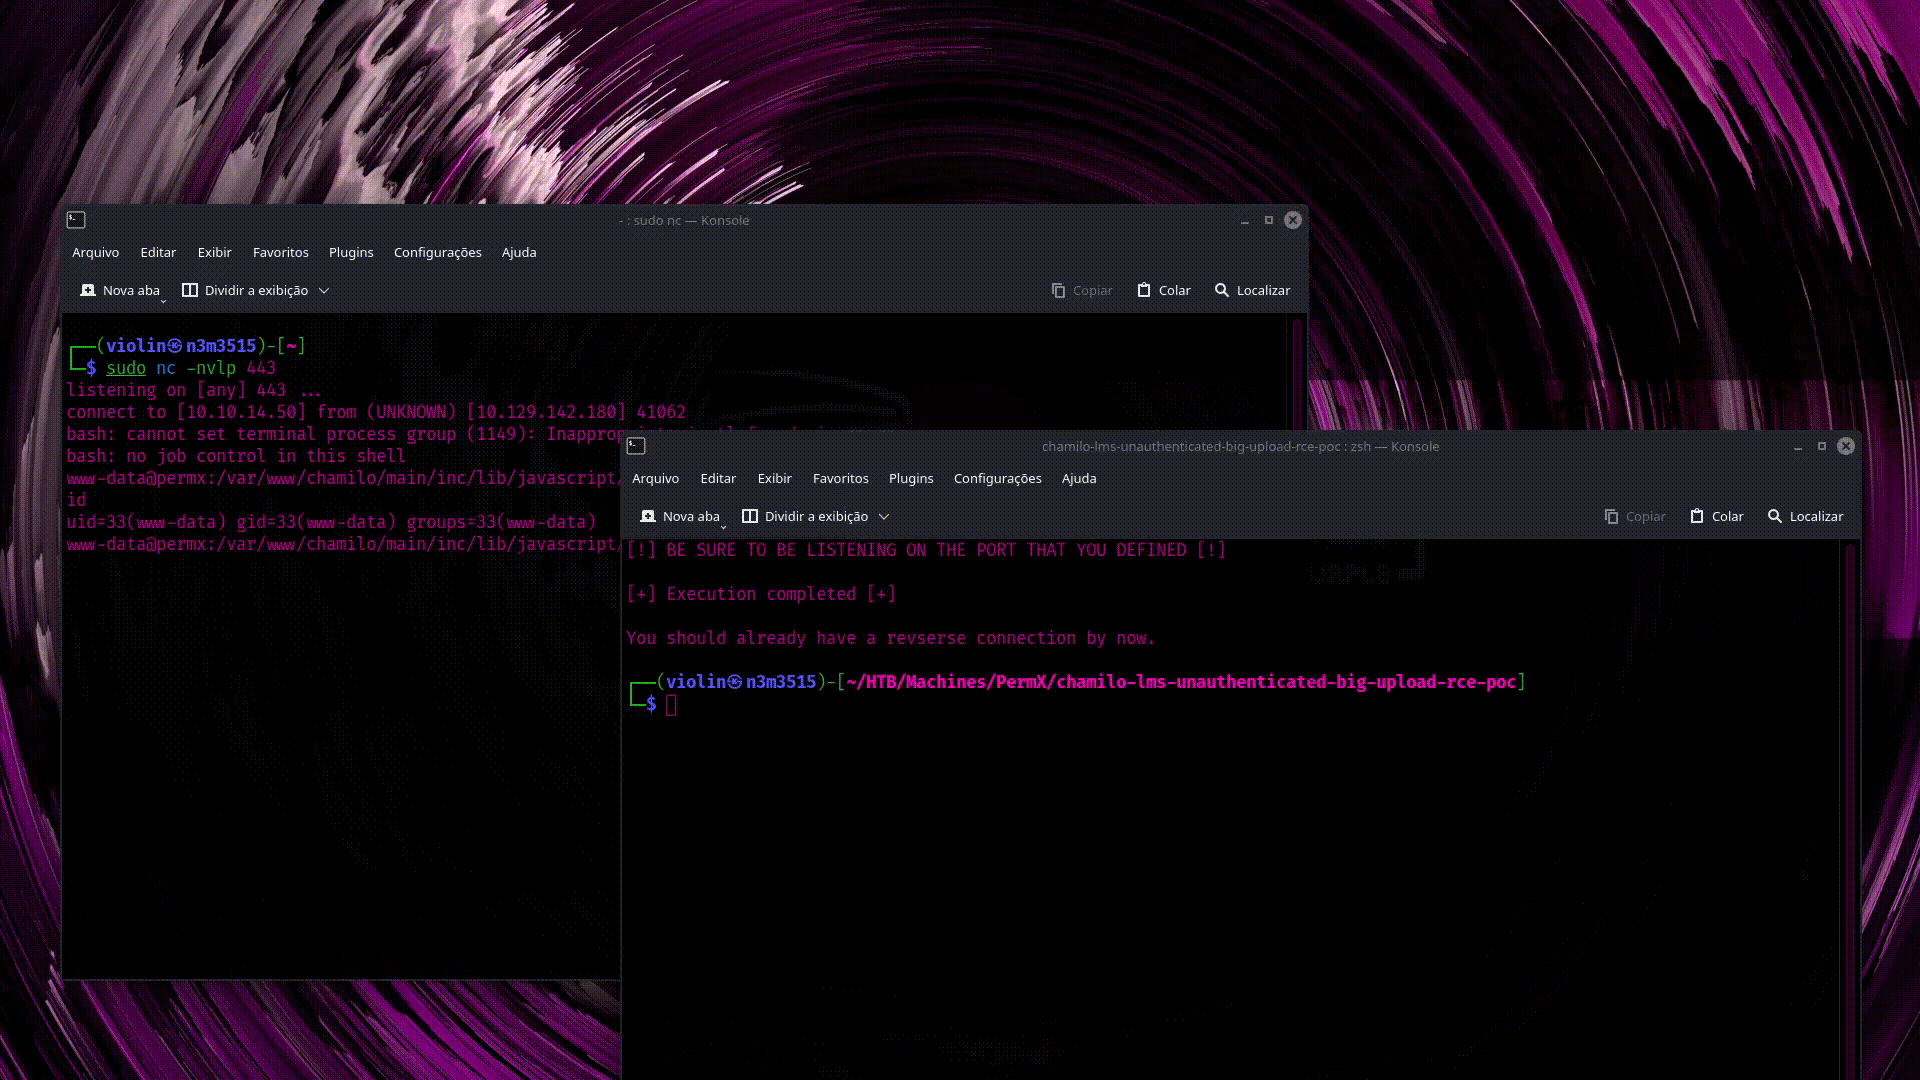
chamilo-lms-unauthenticated-big-upload-rce-poc preview

chamilo-lms-unauthenticated-big-upload-rce-poc

GitHubm3m0o/chamilo-lms-unauthenticated-big-upload-rce-poc

This is a script written in Python that allows the exploitation of the Chamilo's LMS software security flaw described in CVE-2023-4220
exploitationpayload-developmentpenetration-testing+3
2 years ago
CVE-2025-22604-Cacti-RCE preview

CVE-2025-22604-Cacti-RCE

GitHubishwardeepp/cve-2025-22604-cacti-rce

Proof-of-concept exploit for CVE-2025-22604, a remote code execution vulnerability in Cacti network monitoring software. Enables authenticated RCE…
exploitationpenetration-testingred-teaming+2
1 year ago
CVE-2023-27350-Ongoing-Exploitation-of-PaperCut-Remote-Code-Execution-Vulnerability preview

CVE-2023-27350-Ongoing-Exploitation-of-PaperCut-Remote-Code-Execution-Vulnerability

GitHubrasan2001/cve-2023-27350-ongoing-exploitation-of-papercut-remote-code-execution-vulnerability

Proof-of-concept exploit for CVE-2023-27350, a remote code execution vulnerability in PaperCut print management software, enabling unauthenticated…
exploitationpenetration-testingred-teaming+2
2 years ago
-CVE-2017-7494-Samba-Exploit-POC preview

-CVE-2017-7494-Samba-Exploit-POC

GitHubadjaliya/-cve-2017-7494-samba-exploit-poc

According to researchers with Rapid7, over 110,000 devices appear on internet, which run stable Samba versions, while 92,500 seem to run unstable…

exploitationpenetration-testingred-teaming+3
5 years ago
foolav preview

foolav

GitHubhvqzao/foolav

Pentest tool for antivirus evasion and running arbitrary payload on target Wintel host
penetration-testingred-teaming
17310 years ago
CVE-2022-3368 preview

CVE-2022-3368

GitHubwh04m1001/cve-2022-3368

Proof-of-concept for local privilege escalation in Avira Security via arbitrary file move, exploiting junction points to load a malicious DLL into a…
binary-exploitationexploitationpenetration-testing+3
293 years ago
CVE-2022-24706-CouchDB-Exploit preview

CVE-2022-24706-CouchDB-Exploit

GitHubsadshade/cve-2022-24706-couchdb-exploit

Apache CouchDB 3.2.1 - Remote Code Execution (RCE)

database-securityexploitationpenetration-testing+2
294 years ago
Previous123Next