

Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
31 results
Burp2Malleable preview

Burp2Malleable

GitHubcodextf2/burp2malleable

Quick python utility I wrote to turn HTTP requests from burp suite into Cobalt Strike Malleable C2 profiles
command-and-controlids-ips-evasionpayload-development+2
418
3 years ago
Burp-Encode-IP preview

Burp-Encode-IP

GitHube1abrador/burp-encode-ip

Burp Suite extension to encode an IP address focused to bypass application IP / domain blacklist.
dns-fuzzingpenetration-testingred-teaming+2
482 years ago
ChromeAlone preview

ChromeAlone

GitHubpraetorian-inc/chromealone

A tool to transform Chromium browsers into a C2 Implant

command-and-controlpayload-developmentpersistence-mechanisms+6
60811 months ago
DLLHijackHunter preview

DLLHijackHunter

GitHubghostvectoracademy/dllhijackhunter

Automated DLL Hijacking Discovery, Validation, and Confirmation. Turning local misconfigurations into weaponized, confirmed attack paths.
binary-analysisdynamic-code-analysiseducation+8
4081 month ago
frieren preview

frieren

GitHubxchwarze/frieren

Frieren is a micro-framework designed for use in routers and Single Board Computers (SBCs). This framework is built to be lightweight, efficient, and…
embedded-systems-securityhardware-iot-securityiot-security+8
22715 days ago
go-http-proxy-to-socks preview

go-http-proxy-to-socks

GitHubshadowy-pycoder/go-http-proxy-to-socks

CLI MITM proxy that converts SOCKS4/SOCKS5 into HTTP/HTTPS/HTTP2/HTTP3 proxy with transparent TCP/UDP redirection, ARP/NDP/DNS spoofing, traffic…
dns-analysisdns-fuzzingids-ips-evasion+6
711 month ago
wp2shell preview

wp2shell

GitHubmcipekci/wp2shell

Pre-auth RCE PoC for WordPress core — chains CVE-2026-63030 (REST /batch/v1 route-confusion desync) with CVE-2026-60137 (author__not_in SQLi) into an…
command-and-controlexploitationpayload-development+7
163 months ago
RedRoot preview

RedRoot

GitHubagampreet-singh/redroot

RedRoot is a Python-based, CLI-driven offensive security framework that brings essential red teaming tools into one unified terminal environment.…
ctfexploit-frameworksfuzzing+9
1817 days ago
CVE-2025-49706-SharePoint-Spoofing-Vulnerability-Under-Active-Exploitation preview

CVE-2025-49706-SharePoint-Spoofing-Vulnerability-Under-Active-Exploitation

GitHubadityabhatt3010/cve-2025-49706-sharepoint-spoofing-vulnerability-under-active-exploitation

A deep dive into CVE-2025-49706 — the SharePoint spoofing flaw now exploited in the wild for stealthy web shell deployment and privilege escalation.
educationexploitationincident-response+6
181 year ago
CVE-2025-59287 preview

CVE-2025-59287

GitHub0x7556/cve-2025-59287

Exploit for CVE-2025-59287, injecting WolfShell memory webshell into WSUS servers to achieve remote code execution when the admin console is opened.


exploitationpayload-developmentpenetration-testing+3
711 months ago
ultrasploiter preview

ultrasploiter

GitLabvqkro/ultrasploiter

A single binary that folds a port scanner, the full Exploit-DB index (47k entries) and runnable exploit modules into one tool. Written in Rust, runs…

command-and-controlexploitationexploit-frameworks+9
11 days ago
CVE-2026-63030 preview

CVE-2026-63030

GitHubfl0ydsec/cve-2026-63030

Python mass exploit and detector for the WordPress Core pre-auth RCE chain CVE-2026-63030 and CVE-2026-60137, chaining SQL injection into remote code…

exploitationpassword-attackspayload-development+7
10 days ago
-CVE-2024-21683-RCE-in-Confluence-Data-Center-and-Server preview

-CVE-2024-21683-RCE-in-Confluence-Data-Center-and-Server

GitHubr00t7oo2jm/-cve-2024-21683-rce-in-confluence-data-center-and-server

This vulnerability allows an unauthenticated attacker to remotely execute arbitrary code on a vulnerable Confluence server. The vulnerability exists…
exploitationpayload-developmentpenetration-testing+3
22 years ago
CVE-2026-17544 preview

CVE-2026-17544

GitHubr2qa/cve-2026-17544

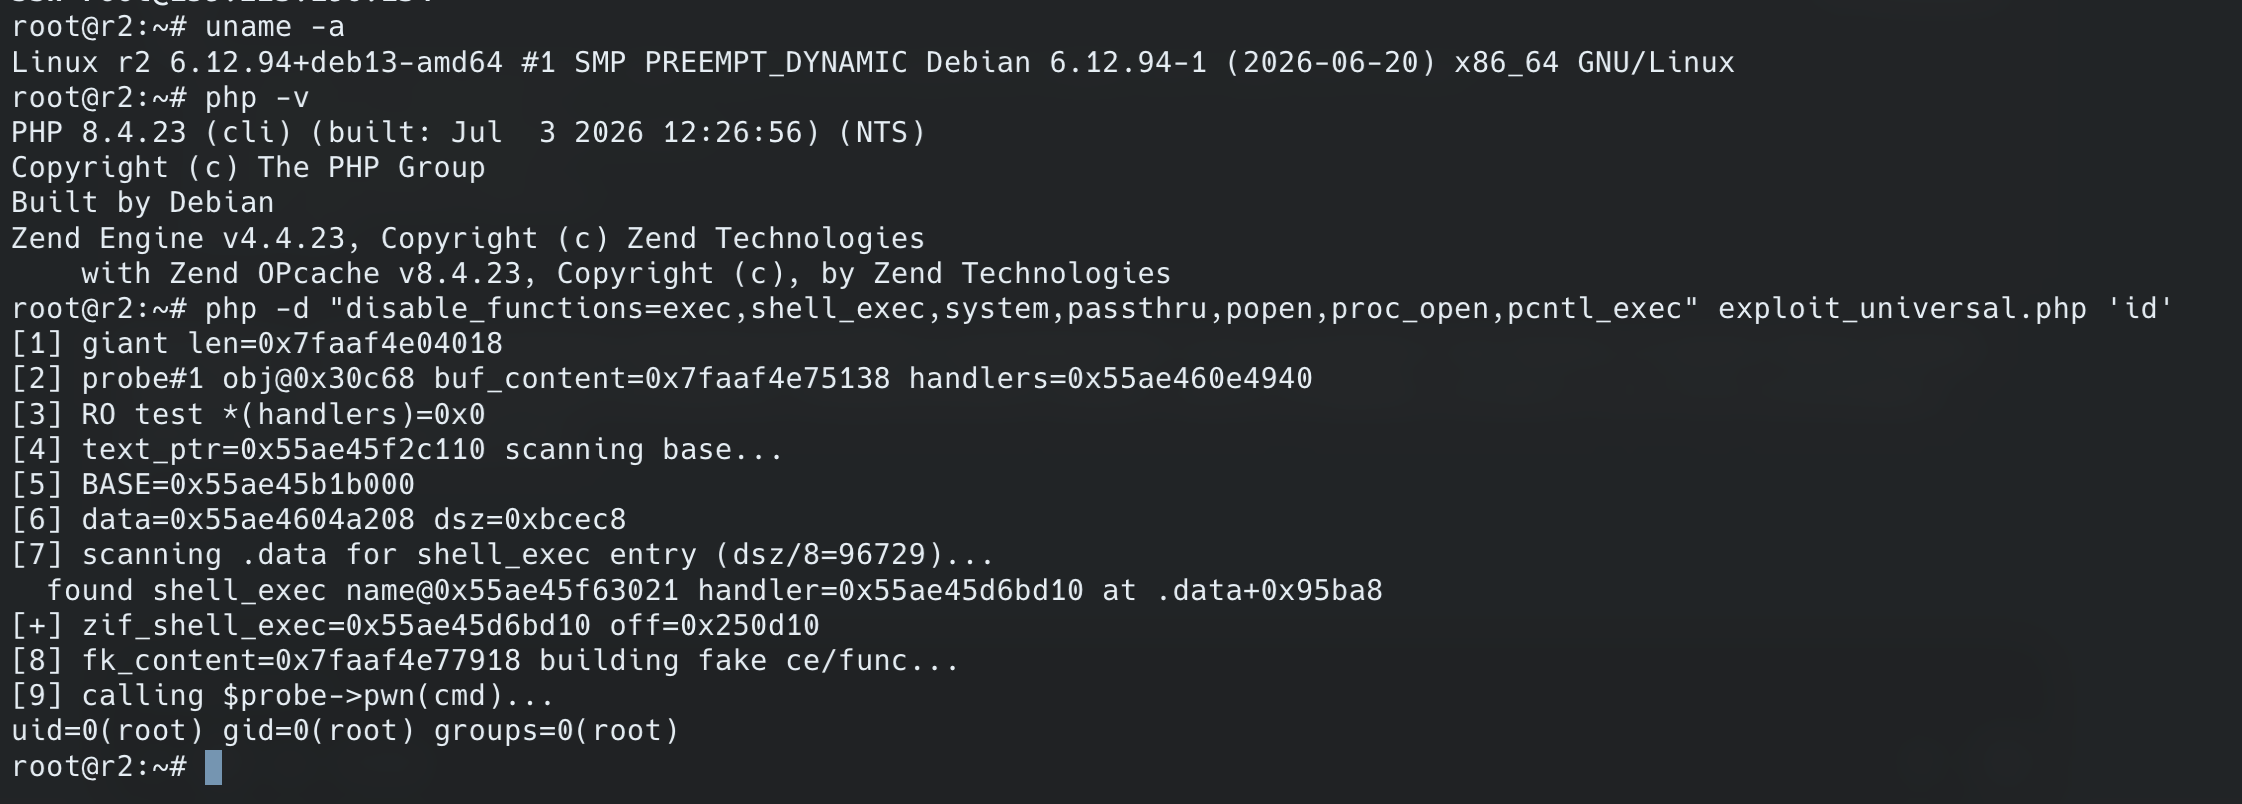
Exploit for CVE-2026-17544: PHP bcmath OOB write converted into memory-only RCE, bypassing disable_functions and open_basedir with a runtime…
binary-exploitationexploitationpayload-development+4
2 months ago
CVE-2026-57517 preview

CVE-2026-57517

GitHubshinthink/cve-2026-57517

💉 Blind SQL Injection → RCE exploit for Control Web Panel (CWP) ≤ 0.9.8.1224 — userRes POST → INTO DUMPFILE → cwpsvc shell
exploitationpayload-developmentpenetration-testing+4
13 months ago
CTT-Mailpit-RCE-v1.0---Temporal-Resonance-Mail-Server-Takeover preview

CTT-Mailpit-RCE-v1.0---Temporal-Resonance-Mail-Server-Takeover

GitHubsimoesctt/ctt-mailpit-rce-v1.0---temporal-resonance-mail-server-takeover

Exploit tool that transforms SMTP header injection into remote code execution with self-propagating worm capabilities, featuring persistence…
command-and-controlexploitationmalware-analysis+5
8 months ago
CVE-2025-471812-POC preview

CVE-2025-471812-POC

GitHubd3vn0mi/cve-2025-471812-poc

Python PoC for CVE-2025-47812, unauthenticated RCE in Wing FTP Server <= 7.4.3 via NULL-byte Lua injection into session files
exploitationpayload-generationpenetration-testing+3
8 months ago
winrar-exploit preview

winrar-exploit

GitHubskander1337/winrar-exploit

C++ implementation of CVE-2025-8088 WinRAR exploit using Alternate Data Streams to drop payloads into Windows Startup folder for persistence.

educationexploitationmalware-analysis+3
1 year ago
Previous12Next