Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
30 results
Joomla-webshell-plugin preview

Joomla-webshell-plugin

GitHubp0dalirius/joomla-webshell-plugin

A webshell plugin and interactive shell for pentesting a Joomla website.
command-and-controlexploitationpayload-development+6
62
4 years ago
StayKit preview

StayKit

GitHub0xthirteen/staykit

Cobalt Strike extension for post-exploitation persistence using SharpStay .NET assembly. Provides GUI-driven persistence via Registry keys, Scheduled…

exploit-frameworkspayload-generationpersistence-mechanisms+2
4936 years ago
JS-Tap preview

JS-Tap

GitHubhoodoer/js-tap

JavaScript beacons and C2 to be used for XSS payload or post exploitation implants on webapp servers or desktop software to monitor users and…
command-and-controldata-exfiltrationinformation-gathering+8
4743 months ago
pyCobaltHound preview

pyCobaltHound

GitHubnvisosecurity/pycobalthound

pyCobaltHound is an Aggressor script extension for Cobalt Strike which aims to provide a deep integration between Cobalt Strike and Bloodhound.
exploit-frameworksinformation-gatheringlateral-movement+5
1354 years ago
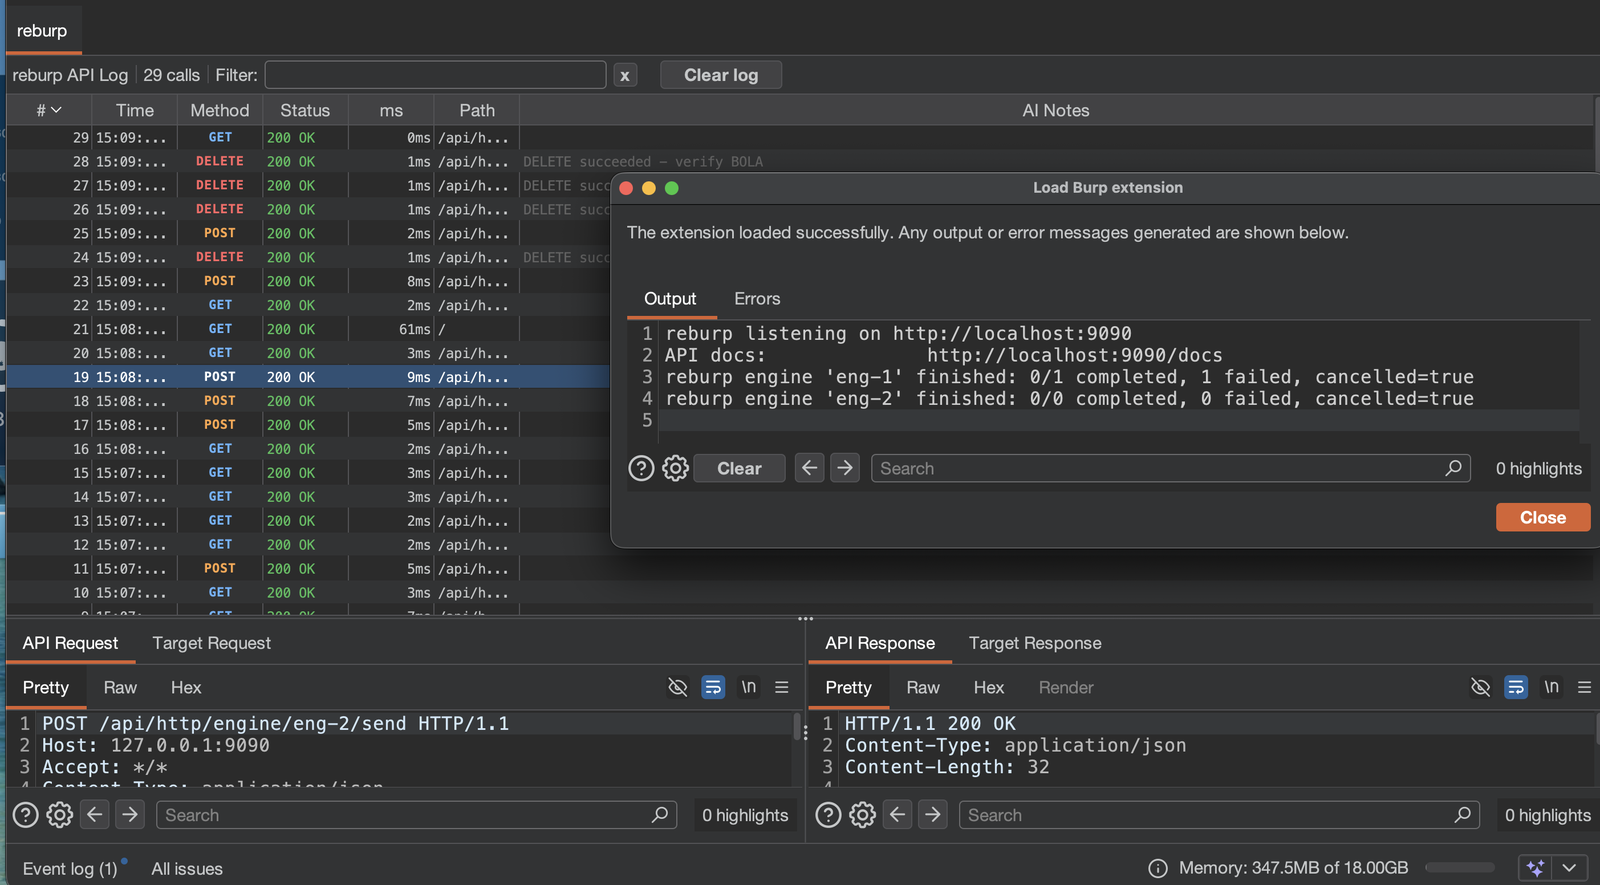
reburp preview

reburp

GitHubforefy/reburp

A Burp Suite extension that exposes the full Montoya API as a local REST API, with Swagger UI
ai-securityapi-security-testingfuzzing+7
1317 days ago
aggrokatz preview

aggrokatz

GitHubsec-consult/aggrokatz

Aggrokatz is an aggressor plugin extension for Cobalt Strike which enables pypykatz to interface with the beacons remotely and allows it to parse…
exploit-frameworkspayload-developmentpenetration-testing+2
1555 years ago
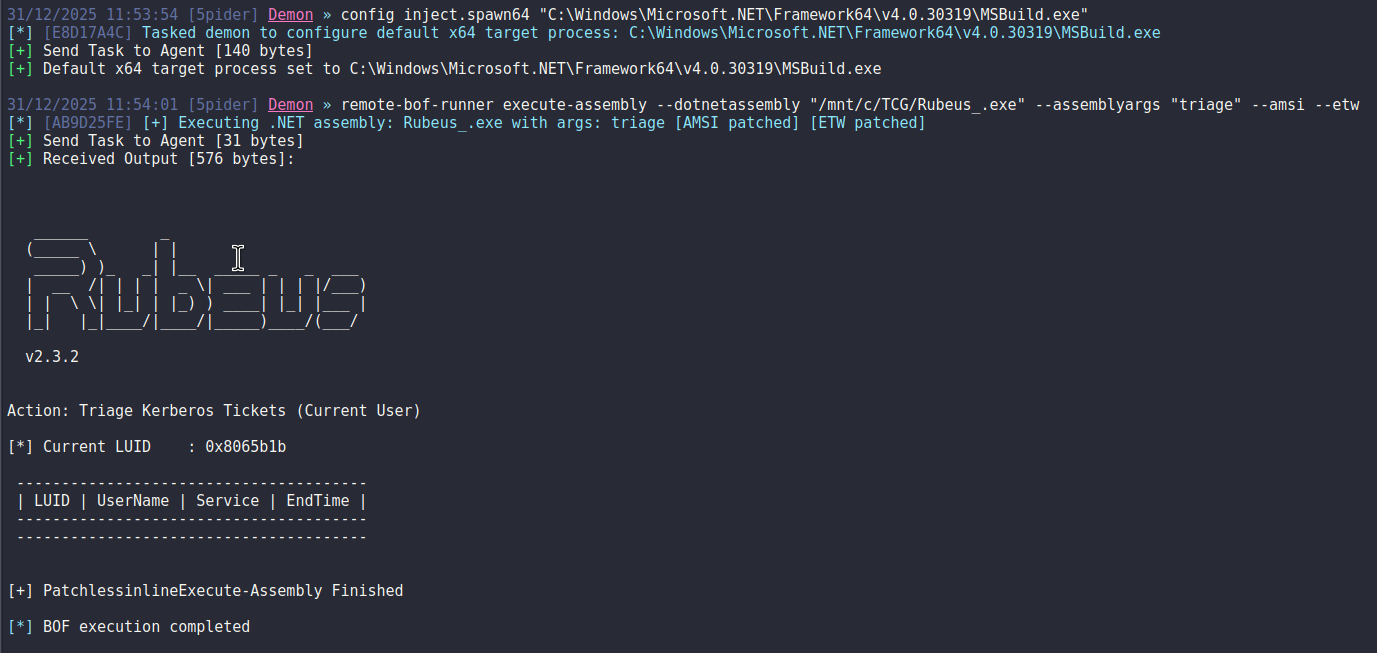
Remote-BOF-Runner preview

Remote-BOF-Runner

GitHubpard0p/remote-bof-runner

Remote BOF Runner is a Havoc extension framework for remote execution of Beacon Object Files (BOFs) using a PIC loader made with Crystal Palace.
binary-exploitationcommand-and-controleducation+8
10210 months ago
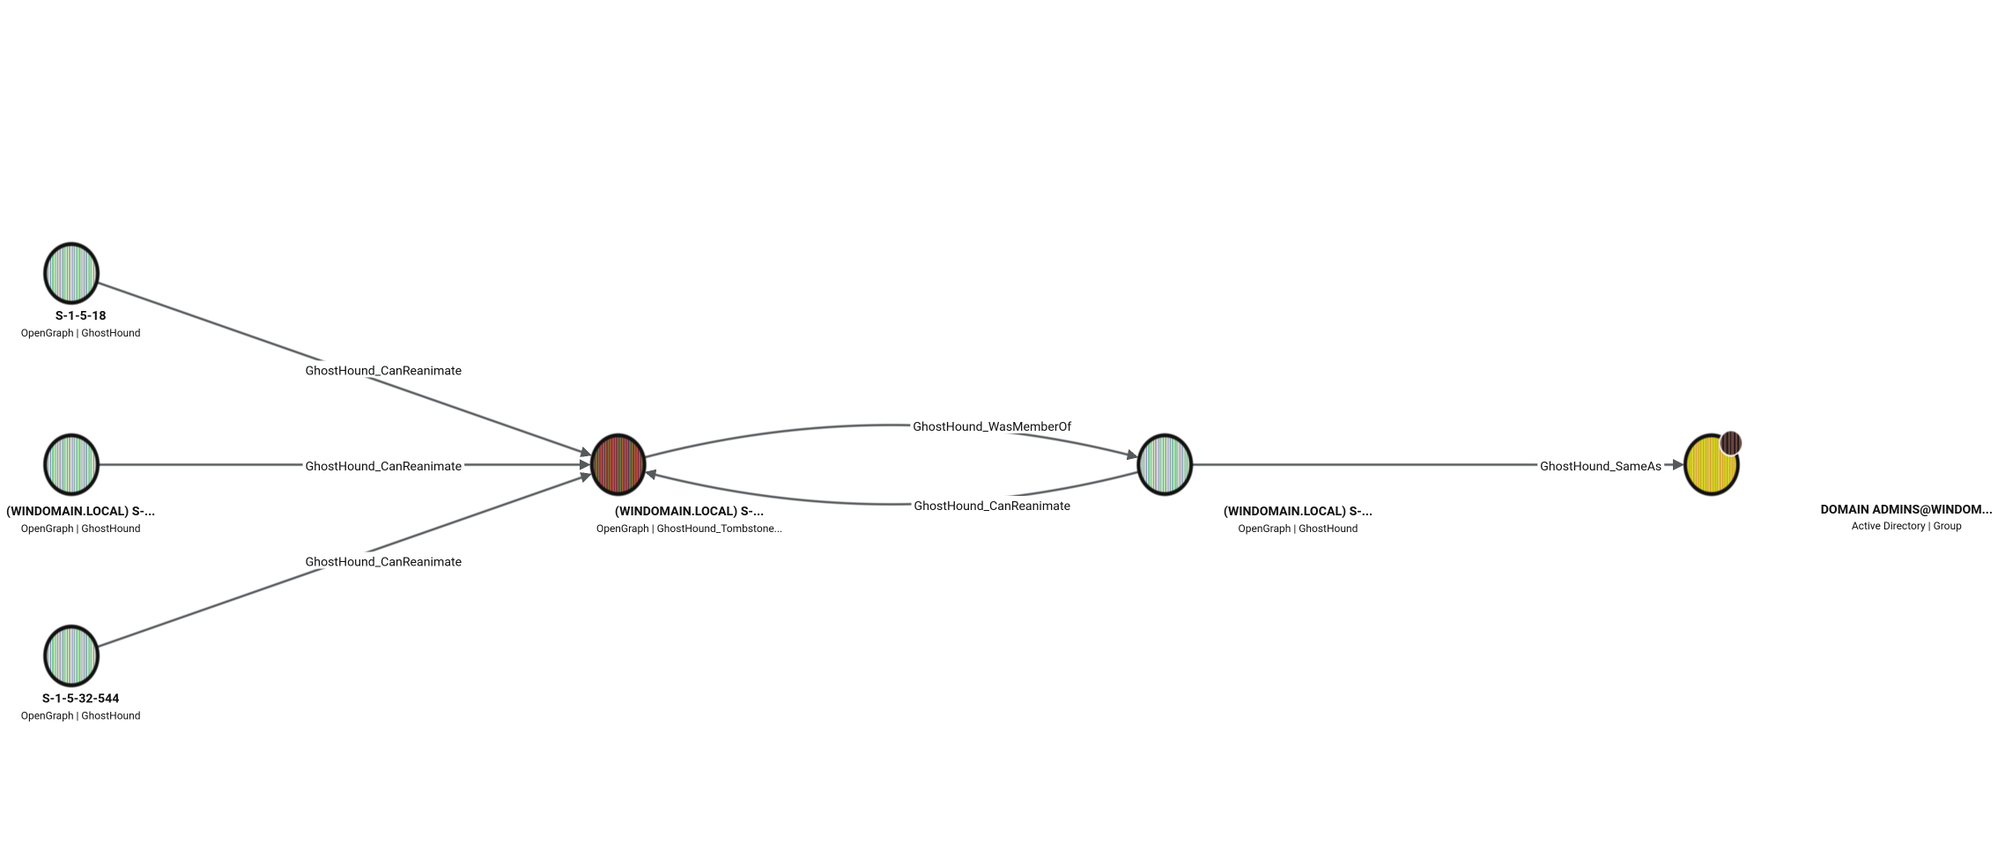
ghosthound preview

ghosthound

GitHubjvbotelho/ghosthound

GhostHound is a BloodHound OpenGraph extension that surfaces Active Directory tombstone reanimation as a first-class attack path, enumerating deleted…
exploitationinformation-gatheringlateral-movement+5
422 months ago
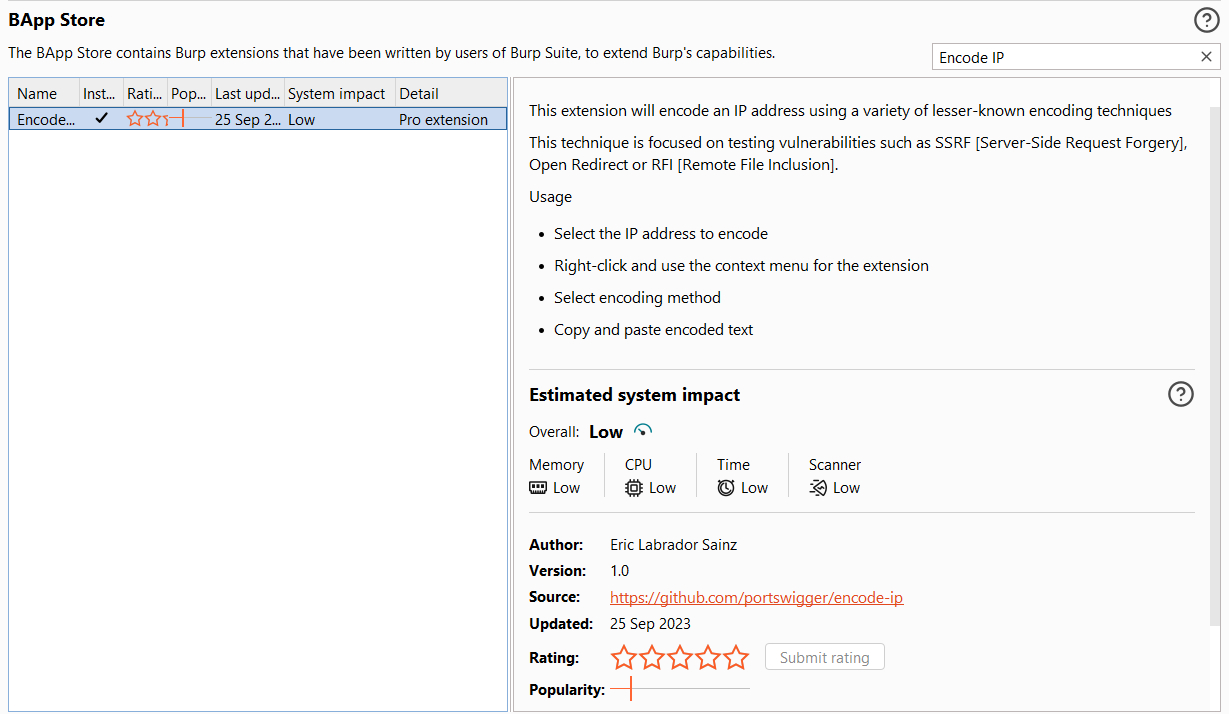
Burp-Encode-IP preview

Burp-Encode-IP

GitHube1abrador/burp-encode-ip

Burp Suite extension to encode an IP address focused to bypass application IP / domain blacklist.
dns-fuzzingpenetration-testingred-teaming+2
482 years ago
processhacker-mcp preview

processhacker-mcp

GitHubillegal-instruction-co/processhacker-mcp

Runtime process analysis and memory hacking MCP server for AI agents. Supports dynamic extension loading, read-only mode, audit logging, and…
debuggersdynamic-analysis-sandboxingexploitation+7
508 months ago
extloader preview

extloader

GitHubsynacktiv/extloader

A chromium extension exploitation toolkit

exploitationinformation-gatheringpenetration-testing+4
261 year ago
apfell-chrome-extension-c2server preview

apfell-chrome-extension-c2server

GitHubxorrior/apfell-chrome-extension-c2server

Apfell C2 Server for the Google Chrome Extension Payload

command-and-controlexploit-frameworkspayload-development+3
126 years ago
CVE-2026-48939 preview

CVE-2026-48939

GitHubshinthink/cve-2026-48939

Pre-auth arbitrary file upload RCE exploit for iCagenda Joomla extension < 4.0.8 (CVSS 10.0)
exploitationpayload-generationpenetration-testing+3
23 months ago
CVE-2026-48909-Joomla-SP-Exploit preview

CVE-2026-48909-Joomla-SP-Exploit

GitHubcerberusmrxi/cve-2026-48909-joomla-sp-exploit

CVE-2026-48909 - Unauthenticated PHP Object Injection to RCE exploit for Joomla SP LMS extension versions <= 4.1.3. Exploits lmsOrders cookie…

code-analysiscommand-and-controleducation+8
23 months ago
CVE-2019-15120 preview

CVE-2019-15120

GitHubh3llraiser/cve-2019-15120

Exploit for XSS via BBCode on Kunena extension before 5.1.14 for Joomla!

educationexploitationpenetration-testing+3
16 years ago
CVE-2026-48907_PoC preview

CVE-2026-48907_PoC

GitHubchiefyoru/cve-2026-48907_poc

Unauthenticated Remote Code Execution (RCE) vulnerability in the JCE (Joomla Content Editor) extension for Joomla

exploitationpenetration-testingred-teaming+2
13 months ago
chromebackdoor preview
Archived

chromebackdoor

GitHubgraniet/chromebackdoor

Chromebackdoor is a PoC of pentest tool, this tool use a MITB technique for generate a windows executable ".exe" after launch run a malicious…

command-and-controlpayload-generationpenetration-testing+2
5139 years ago
external_c2_framework preview

external_c2_framework

GitHubund3rf10w/external_c2_framework

Python api for usage with cobalt strike's External C2 specification

command-and-controlexploit-frameworkspayload-development+3
2394 years ago
Previous12Next