
CVE-2024-30270-PoC
The script exploits Mailcow vulnerabilities via XSS and RCE, emphasizing the need for robust security measures and responsible usage to enhance web…

The script exploits Mailcow vulnerabilities via XSS and RCE, emphasizing the need for robust security measures and responsible usage to enhance web…

Local-first AI red team for web, API, and LLM application security. Attacker-style reasoning, evidence-backed findings, and skills for AI coding…

Engagement Manager is a web application for tracking offensive security engagements. It features a modern UI, built with Next.js, Prisma, and…

Fixed exploit for CVE-2022-46169 targeting a web application vulnerability, enabling authenticated remote code execution for penetration testing and…

evilwaf is a penetration testing tool designed to detect and bypass common Web Application Firewalls (WAFs).

TCP tunneling over HTTP/HTTPS for web application servers

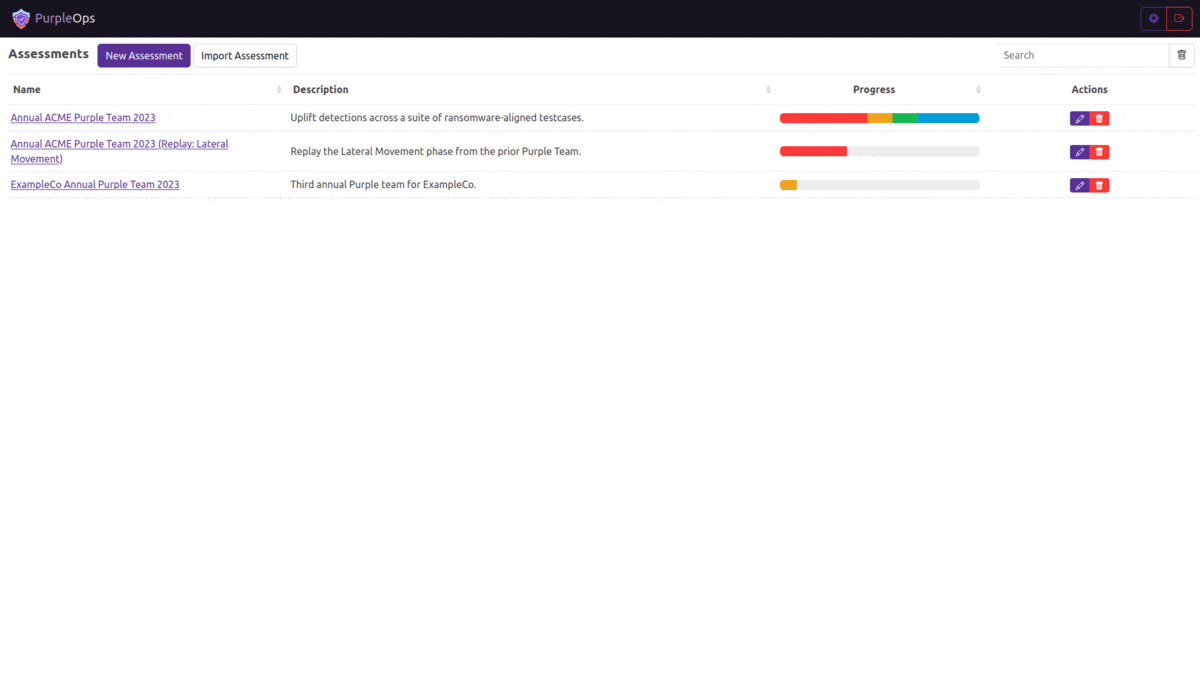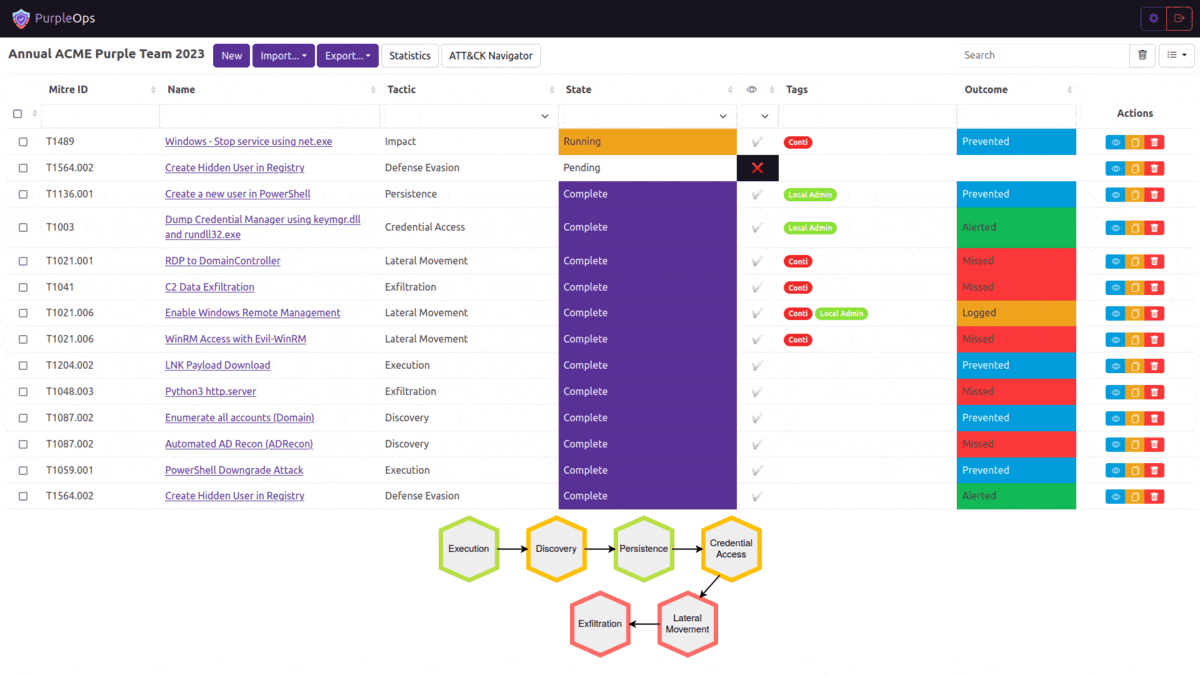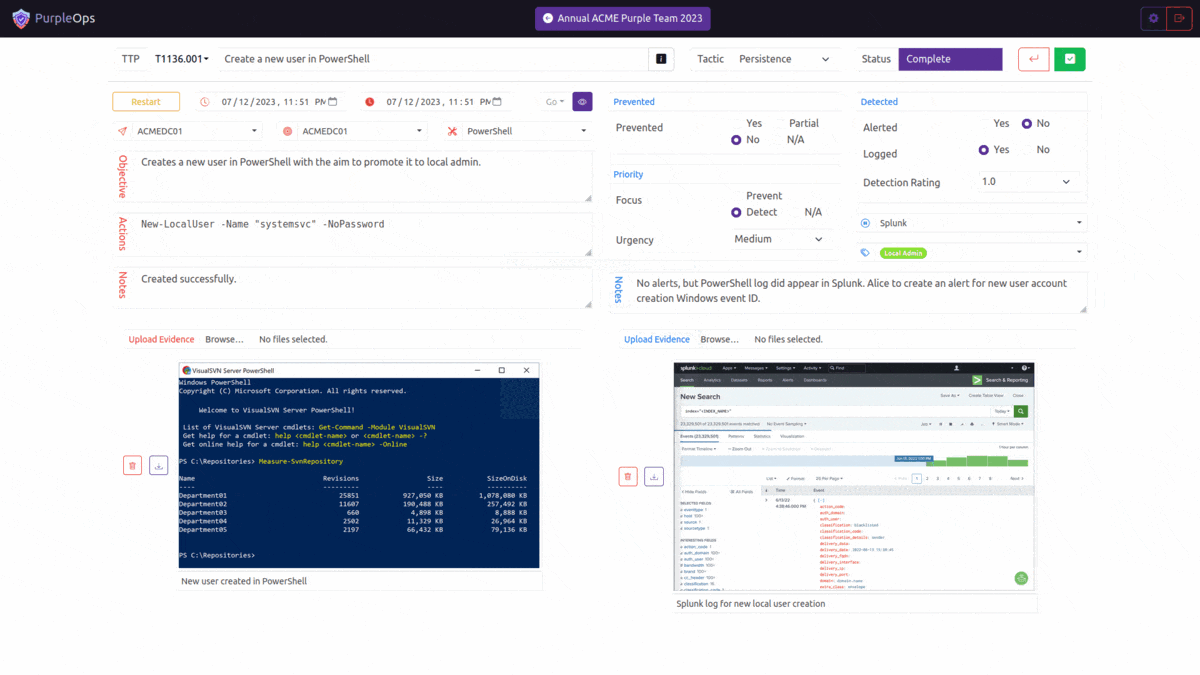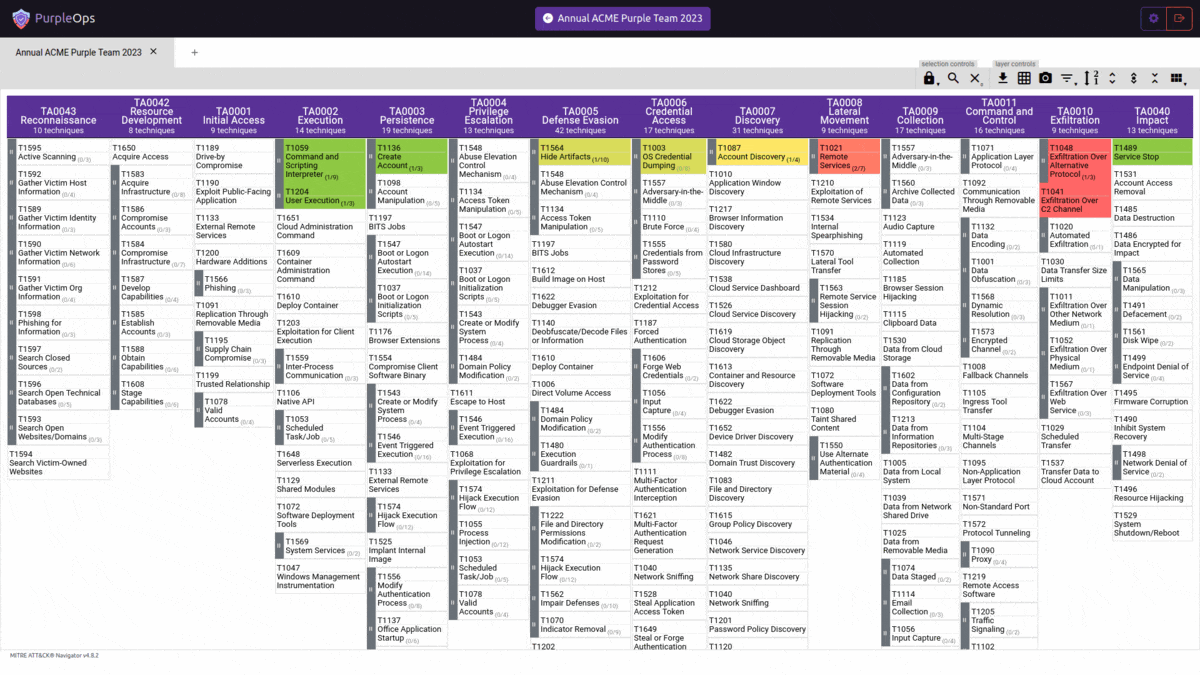
An open-source self-hosted purple team management web application.

Modular WAF bypass fuzzer with multi-threading, request manipulation, and payload encoding for red team web application testing.

CoWitness is a powerful web application testing tool that enhances the accuracy and efficiency of your testing efforts. It allows you to mimic an…

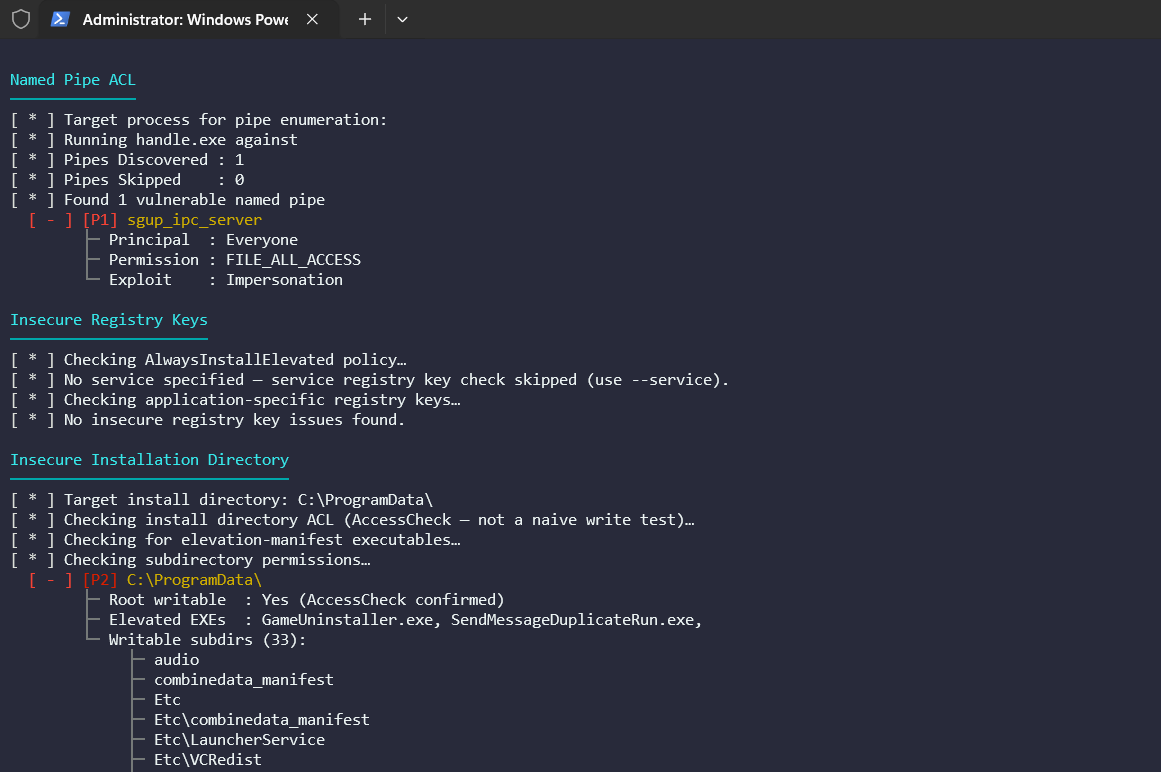
Anvil is a runtime-first attack surface assessment tool for Windows thick client applications, built for penetration testers and security researchers…

Web application penetration testing project targeting a WordPress environment. Includes exploitation of CVE-2019-9978, reverse shell execution,…

Bypass exploit for CVE-2019-16759 targeting a specific web application vulnerability, enabling unauthorized access or privilege escalation during…

PHP-based exploit for CVE-2020-23342, designed to be run in a Docker container for local testing of a specific web application vulnerability.

Python exploit for CVE-2026-3333 demonstrating DNS rebinding to access cloud metadata and steal IAM credentials through an SSRF-vulnerable web app.

Six Degrees of Domain Admin

Burp Plugin to Bypass WAFs through the insertion of Junk Data

Automated WAF assessment tool that detects firewall vendors, tests 19 attack categories with advanced evasion payloads, and provides color-coded…

Webshell, Virtual Private Server (VPS) and cPanel Database