Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

··Feeds·Contact·Privacy·© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
54 results
watchguard-sso-client preview

watchguard-sso-client

GitHubredteampentesting/watchguard-sso-client

Client Implementation for the WatchGuard SSO Agent Protocol used for Security Research (CVE-2024-6592, CVE-2024-6593, CVE-2024-6594)

authenticationexploitationnetwork-security+3
3
2 years ago
Registry-Recon preview

Registry-Recon

GitHuboptiv/registry-recon

Cobalt Strike Aggressor Script that Performs System/AV/EDR Recon

information-gatheringpenetration-testing-frameworksreconnaissance+1
3384 years ago
MouseJack preview

MouseJack

GitHubsecurityward/mousejack

All the details and steps needed to perform tactical mousejacking using Autojack
exploitationpayload-generationred-teaming+2
157 years ago
metabase-cve-2023-38646 preview

metabase-cve-2023-38646

GitHubkushiro45/metabase-cve-2023-38646

Repo contains the PoC and steps to reproduce cve 2023-38646
exploitationpayload-developmentpenetration-testing+3
2 months ago
CVE-2025-49844_POC preview

CVE-2025-49844_POC

GitHubmiclelsoncn/cve-2025-49844_poc

Proof-of-concept exploit for CVE-2025-49844, a Redis Lua script remote code execution vulnerability, demonstrating exploitation and providing…
exploitationpenetration-testingred-teaming+2
211 months ago
Eaton-UPS-Companion-Exploit preview

Eaton-UPS-Companion-Exploit

GitHubravss/eaton-ups-companion-exploit

This repository details CVE-2020-6650, a vulnerability I discovered within Eaton's UPS Companion. All users should upgrade to v1.06 immediately or…
command-and-controlexploitationpayload-development+5
16 years ago
CVE-2025-60787-POC preview

CVE-2025-60787-POC

GitHubd3vn0mi/cve-2025-60787-poc

Python PoC for CVE-2025-60787, authenticated OS command injection RCE in motionEye <= 0.43.1b4 via unsanitized image_file_name config
command-and-controlexploitationpayload-development+4
6 months ago
CVE-2024-24590-ClearML-RCE-Exploit preview

CVE-2024-24590-ClearML-RCE-Exploit

GitHubrippsec/cve-2024-24590-clearml-rce-exploit

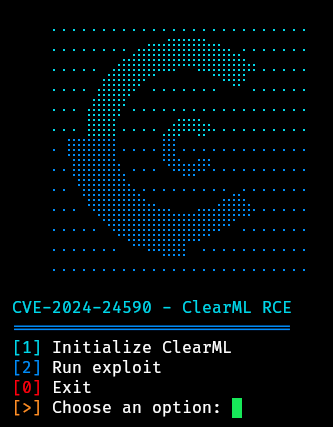
CVE-2024-24590 – ClearML RCE via unsafe pickle artifact deserialization (0.17.0–1.14.2)
command-and-controleducationexploitation+6
65 months ago
CVE-2022-22274_CVE-2023-0656 preview

CVE-2022-22274_CVE-2023-0656

GitHubbishopfox/cve-2022-22274_cve-2023-0656

Proof-of-concept exploit for SonicWall SonicOS stack-based buffer overflows (CVE-2022-22274, CVE-2023-0656) that tests and triggers crashes via…
exploitationfuzzingpenetration-testing+3
192 years ago
CVE-2025-69212-PoC preview

CVE-2025-69212-PoC

GitHubbridgeralderson/cve-2025-69212-poc

OpenSTAManager v2.9.8 and earlier versions contain a critical OS Command Injection vulnerability in the P7M (signed XML) file decoding function.

command-and-controlexploitationpayload-development+5
42 months ago
CVE-2017-16778-Intercom-DTMF-Injection preview

CVE-2017-16778-Intercom-DTMF-Injection

GitHubbreaktoprotect/cve-2017-16778-intercom-dtmf-injection

A coordinated disclosure and security advisory on Fermax Intercom DTML Injection vulneraiblity. Special thanks to Fermax International for prompt…

embedded-systems-securityexploitationhardware-hacking+6
226 years ago
Fortijump-Exploit-CVE-2024-47575 preview

Fortijump-Exploit-CVE-2024-47575

GitHubwatchtowrlabs/fortijump-exploit-cve-2024-47575

Fortinet Fortimanager Unauthenticated Remote Code Execution AKA FortiJump CVE-2024-47575

exploitationpenetration-testingred-teaming+3
971 year ago
Mindmap preview

Mindmap

GitHubignitetechnologies/mindmap

This repository will contain many mindmaps for cyber security technologies, methodologies, courses, and certifications in a tree structure to give…
curated-resourceseducationlearning-paths-courses+2
9.3k2 months ago
ntlmscout preview

ntlmscout

GitHubboydhacks/ntlmscout

Unauthenticated NTLM endpoint reconnaissance tool that decodes Type-2 challenges across HTTP, SMB, MSSQL, SMTP, IMAP, POP3, NNTP, LDAP, and RDP to…
authenticationdns-analysisinformation-gathering+8
183 days ago
nimvoke preview

nimvoke

GitHubnbaertsch/nimvoke

Indirect syscalls + DInvoke made simple.
ids-ips-evasionpayload-developmentpost-exploitation+2
951 year ago
CVE-2023-23397 preview

CVE-2023-23397

GitHubka7ana/cve-2023-23397

PowerShell proof-of-concept for CVE-2023-23397 that exploits Outlook's ReminderSoundFile property to intercept Net-NTLMv2 hashes via SMB or WebDAV…
authenticationexploitationpenetration-testing+3
403 years ago
ModuleStomping preview

ModuleStomping

GitHubwithsecurelabs/modulestomping

Research and proof-of-concept for module stomping, a technique to hide malicious code in legitimate Windows modules, with documentation and…

binary-analysismalware-analysisred-teaming
1237 years ago
watchTowr-vs-FortiWeb-CVE-2025-25257 preview

watchTowr-vs-FortiWeb-CVE-2025-25257

GitHubwatchtowrlabs/watchtowr-vs-fortiweb-cve-2025-25257

Detection artifact generator for FortiWeb CVE-2025-25257, exploiting unauthenticated SQL injection to achieve remote code execution via hex-encoded…

exploitationpayload-generationpenetration-testing+3
1001 year ago
Previous123Next