Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
Registry-Recon — Cobalt Strike Aggressor Script that Performs System/AV/EDR Recon | Kitploit

Tools/GitHubGitHub/optiv/registry-recon
Penetration Testing FrameworksReconnaissanceInformation GatheringRed Teaming
GitHuboptiv/registry-recon

Registry-Recon

Cobalt Strike Aggressor Script that Performs System/AV/EDR Recon

View Repository
33934384 years agoReviewed by Kitploit
Share

Registry-Recon

Cobalt Strike Aggressor Script that Performs System/AV/EDR Recon.

Author: Jess Hires

Description

As a red-team practitioner, we are often using tools that attempt to fingerprint details about a compromised system, preferably in the most stealthy way possible. Some of our usual tooling for this started getting flagged by EDR products, due to the use of Windows CLI commands. This aggressor script aims to solve that problem by only probing the system using native registry queries, no CLI commands.

Setup

Simply load reg.cna into Cobalt Strike using the Script Manager. Then right-click on the beacon you want to run registry recon on, and choose Registry then Recon, or type regenum into the beacon console.

Installation and Usage

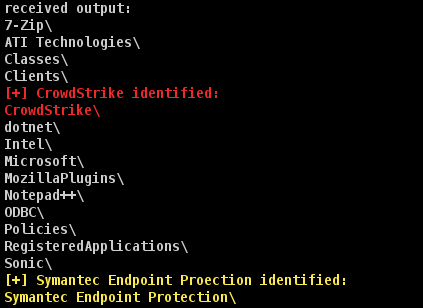
Sample Output 1

Sample Output 2

How does this work?

Primarily, using Cobalt Strike's breg_query and breg_queryv functions. Then, all beacon output is hijacked with beacon_output, looking for specific values. When a positive match is made, the output will be highlighted in the beacon output. Since there is no beacon_output_reg or something similar, like beacon_output_ls and beacon_output_ps, all output must be captured for parsing.

What if my AV/EDR product isn't detected? / How can I help?

This is expected. We couldn't test for every AV/EDR solution, and we knew that many would be missing. You can help us out by submitting a GitHub issue including the following info:


  • If this is a System/AV/EDR entry
  • The name of the product
  • Relevant registry entries that can be used to positively ID the product
Download Tool

Most Popular

View all →

Discover the most used tools by our community.

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 The ultimate OSINT toolkit: investigation graph, confidence scoring, alias families, map, timeline and reports. 49 modules, 400+ sites, no API keys required.

    851
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    GhostLock One-Tap Execution App (CVE-2026-43499)

    538
  • 3

    ARTEX

    baarai/artex

    LLM multi-agent autonomous penetration testing platform with planner/worker agents, asset and exploration graphs, MITM traffic recording, and vulnerability retesting.

    420
  • 4

    redforge

    cybersecurity91/redforge

    Browser-side red team toolkit with 102 offline tools for recon, payload generation, credential attacks, crypto, encoding and engagement reporting.

    357
  • 5

    looking-glass

    anonghosty/looking-glass

    CSIRT platform that ingests Shadowserver reports into MongoDB and replays them as interactive maps, analysis, findings, advisories and executive dashboards.

    297
  • 6

    CyberStrikeAI

    ed1s0nz/cyberstrikeai

    The system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation improves the next.

    280

Explore all tools

Browse our collection of tools

View all tools →