
RSPET
 panagiks/rspet
RSPET (Reverse Shell and Post Exploitation Tool) is a Python based reverse shell equipped with functionalities that assist in a post exploitation…
command-and-controlexploitationpayload-generation+4
263
panagiks/rspetRSPET (Reverse Shell and Post Exploitation Tool) is a Python based reverse shell equipped with functionalities that assist in a post exploitation…
 yardenshafir/ioringreadwriteprimitive
Post exploitation technique to turn arbitrary kernel write / increment into full read/write primitive on Windows 11 22H2
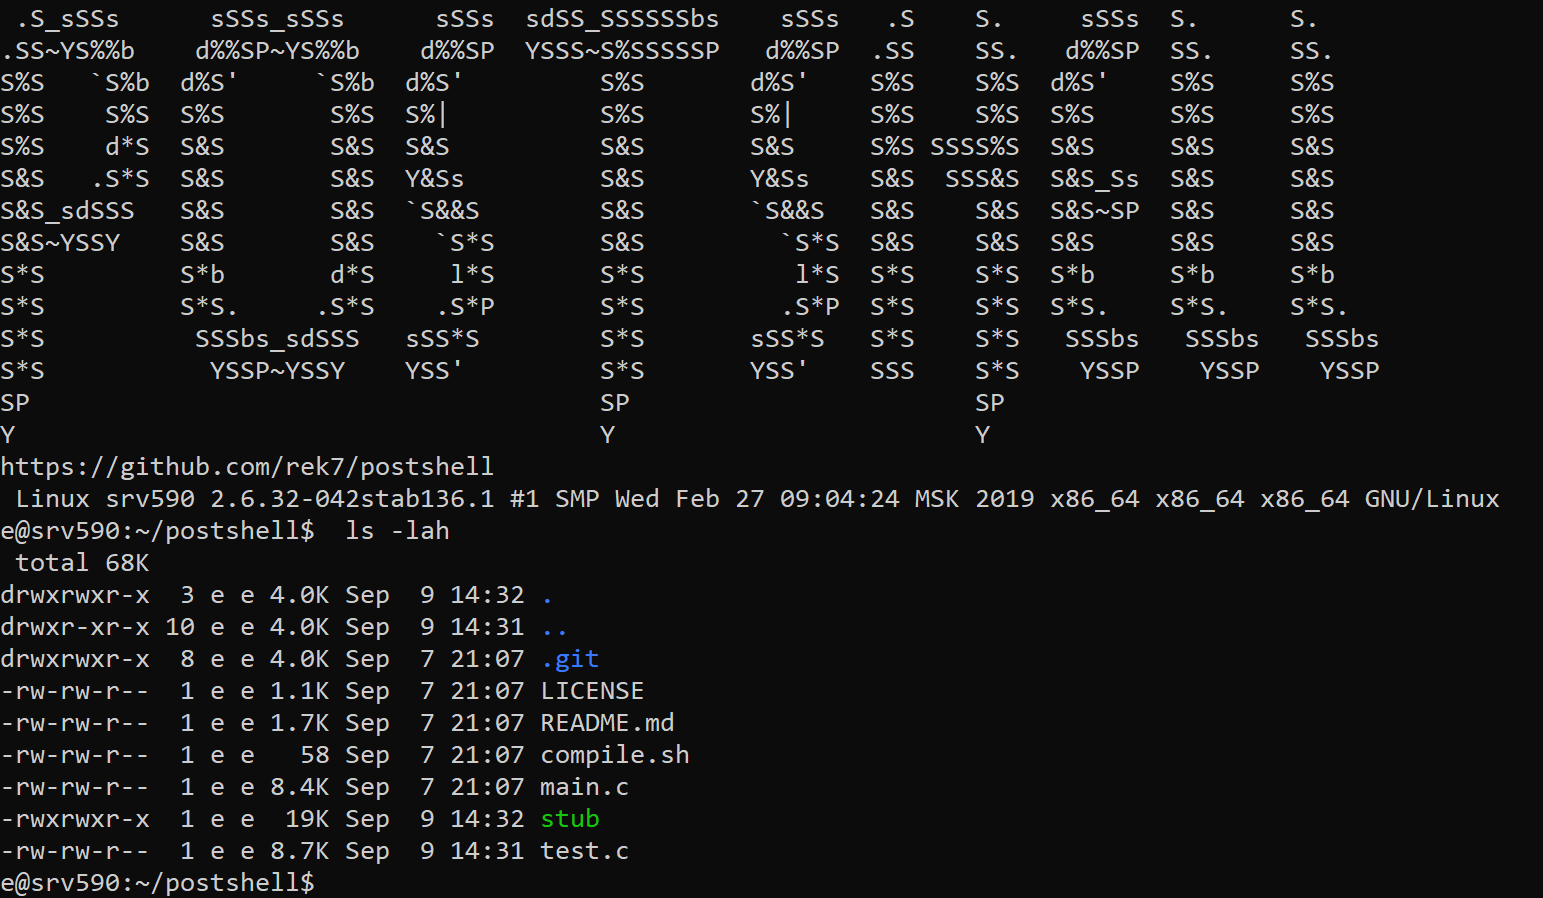 rek7/postshell
PostShell - Post Exploitation Bind/Backconnect Shell
 infosecn1nja/ad-attack-defense
Attack and defend active directory using modern post exploitation adversary tradecraft activity
 cn33liz/p0wnedshell
PowerShell Runspace Post Exploitation Toolkit
 bats3c/shad0w
A post exploitation framework designed to operate covertly on heavily monitored environments
 redcode-labs/bashark
Bash post exploitation toolkit
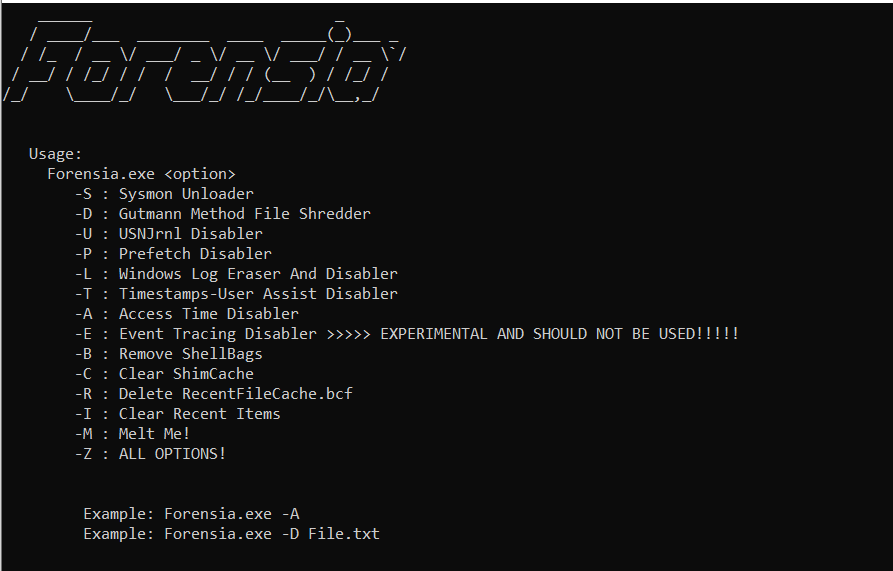 paulnorman01/forensia
Anti Forensics Tool For Red Teamers, Used For Erasing Footprints In The Post Exploitation Phase.
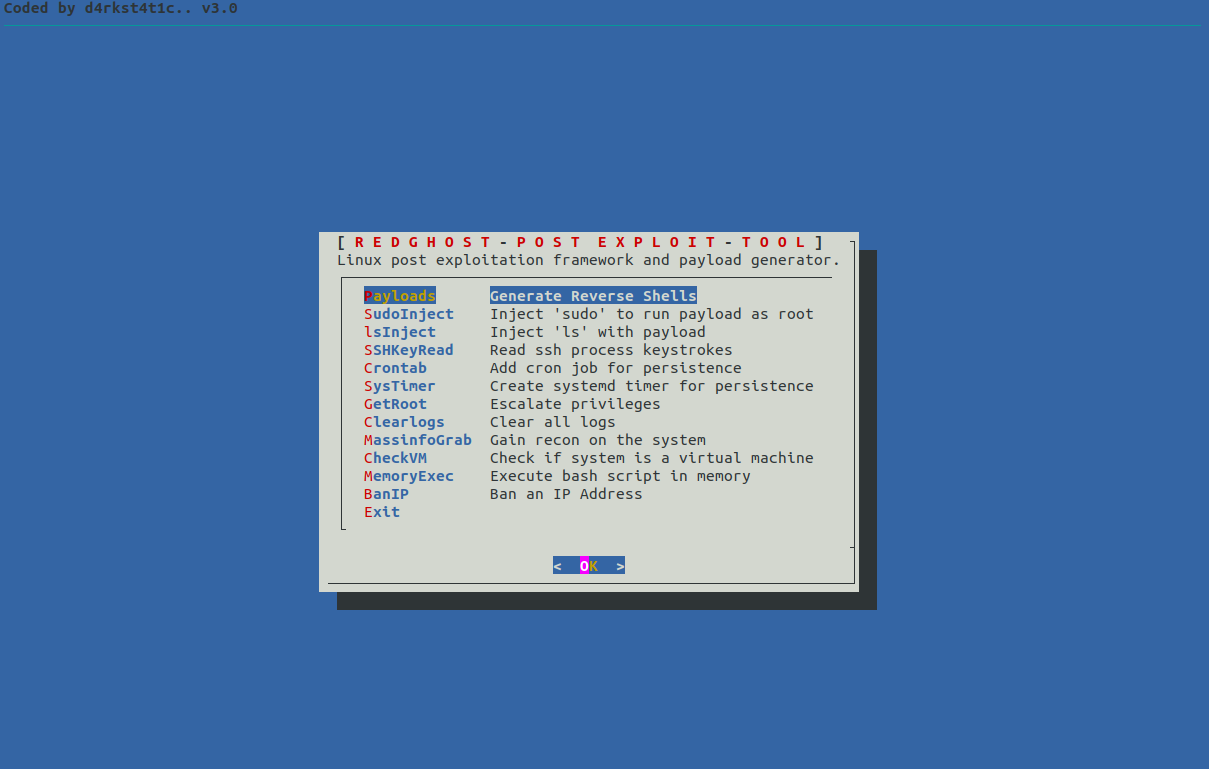 d4rk007/redghost
Linux post exploitation framework written in bash designed to assist red teams in persistence, reconnaissance, privilege escalation and leaving no…
 hoodoer/js-tap
JavaScript beacons and C2 to be used for XSS payload or post exploitation implants on webapp servers or desktop software to monitor users and…
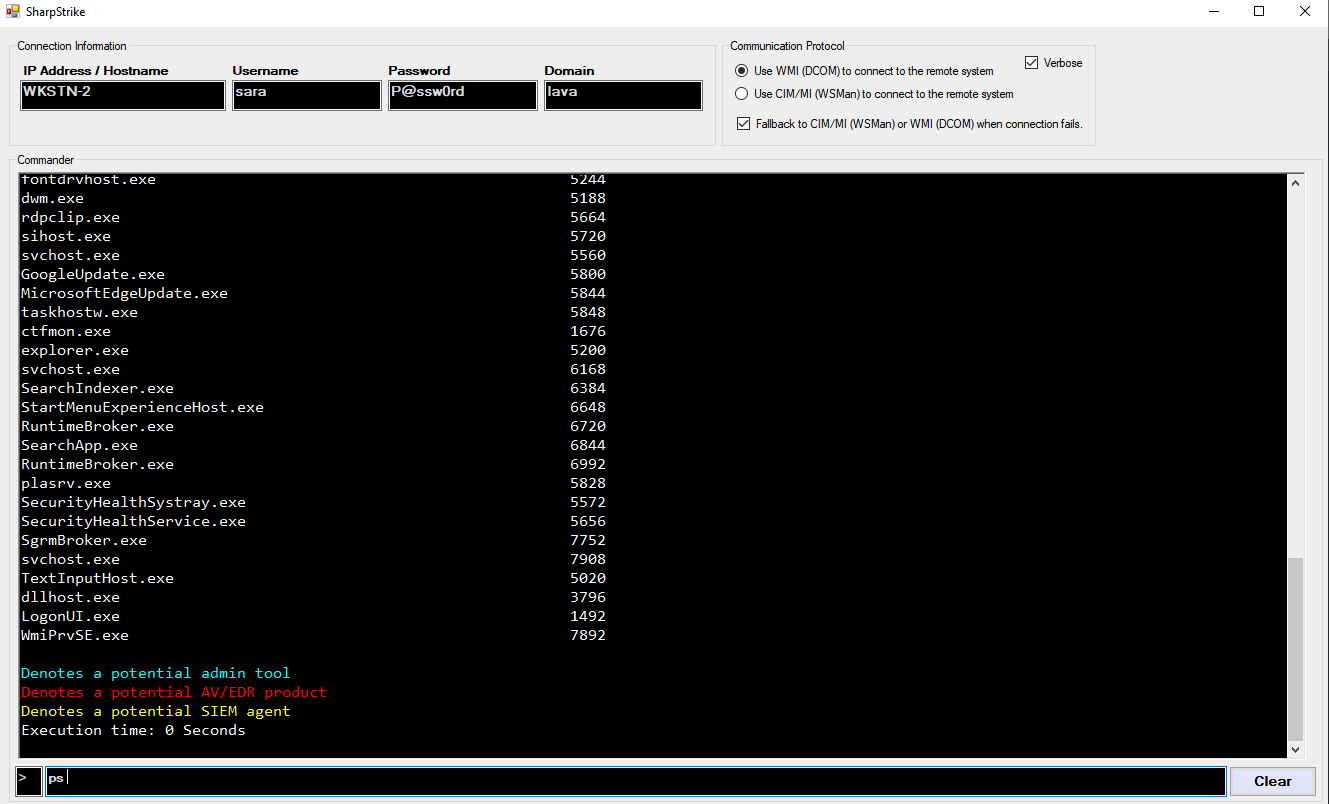 iomoath/sharpstrike
A Post exploitation tool written in C# uses either CIM or WMI to query remote systems.
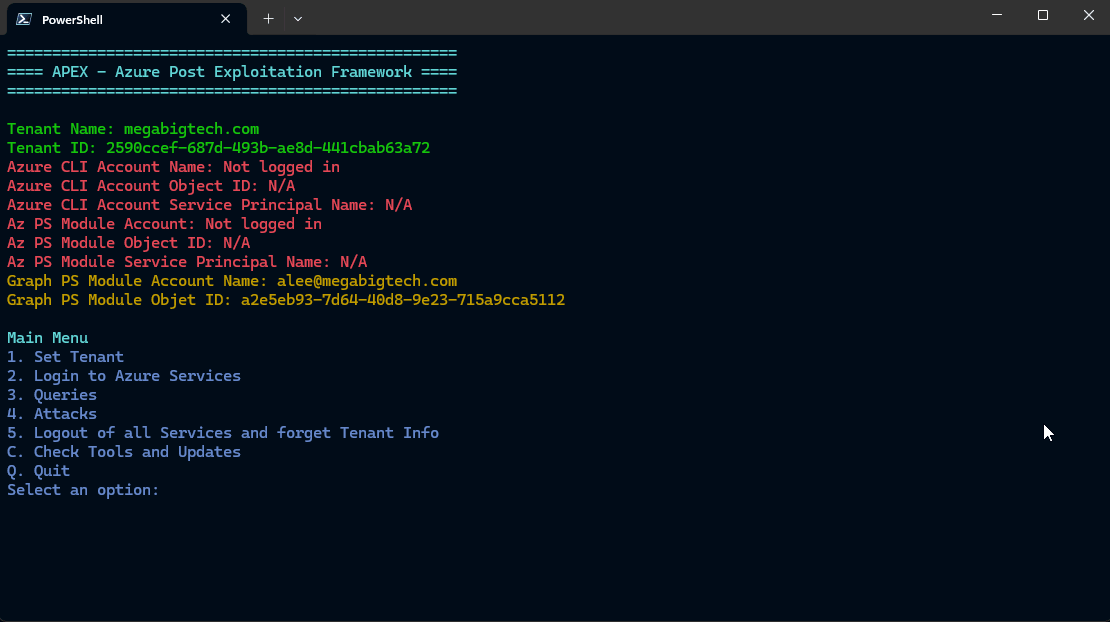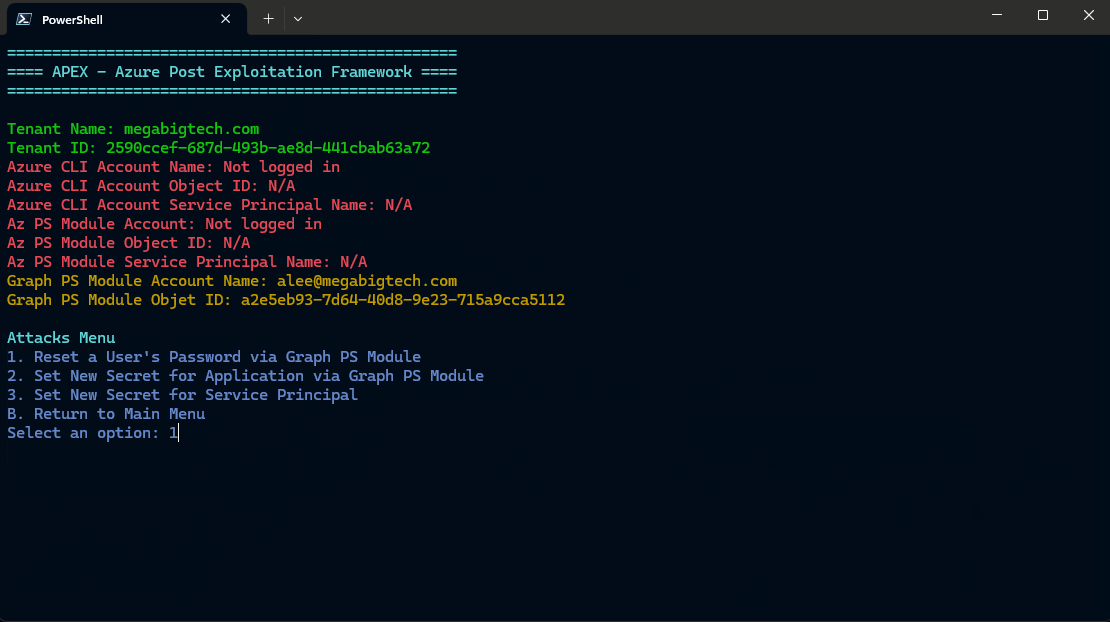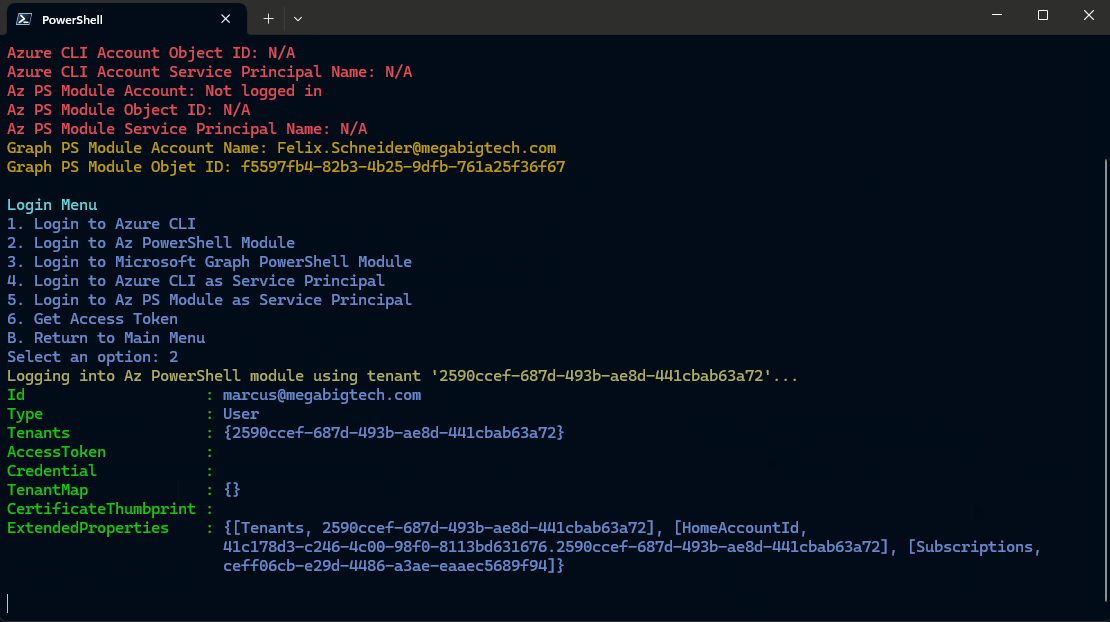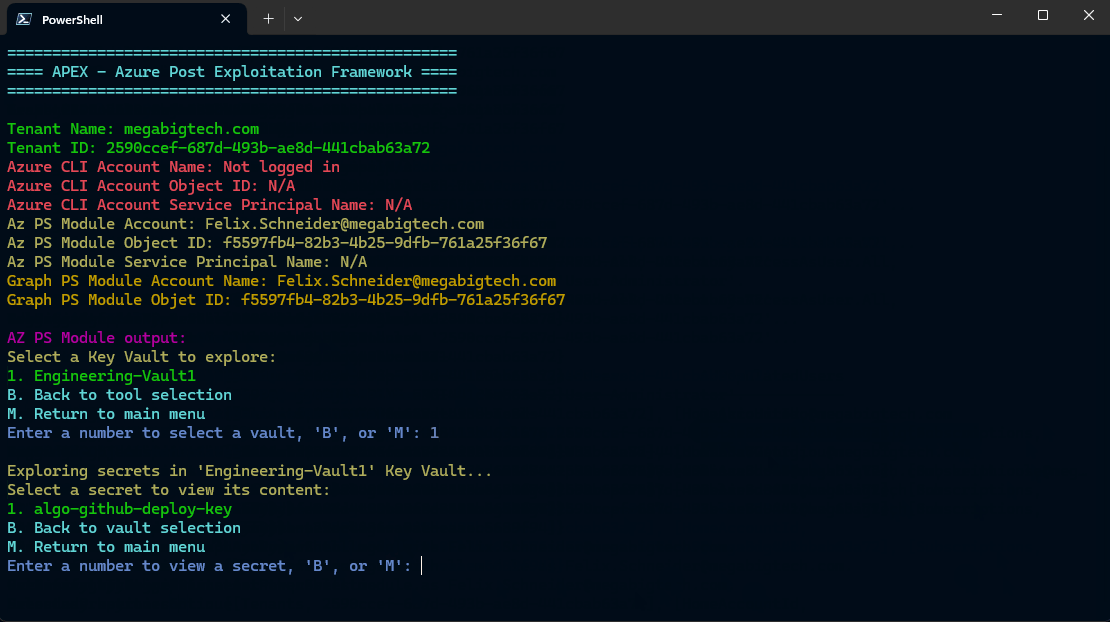 luemmelsec/apex
Azure Post Exploitation Framework
 cedowens/macshellswift
Proof of concept MacOS post exploitation tool written in Swift. Designed as a POC for blue teams to build macOS detections. Author: Cedric Owens
 master-of-servers/mose
Post exploitation tool for configuration management servers.
 0x09al/browser-c2
Post Exploitation agent which uses a browser to do C2 operations.
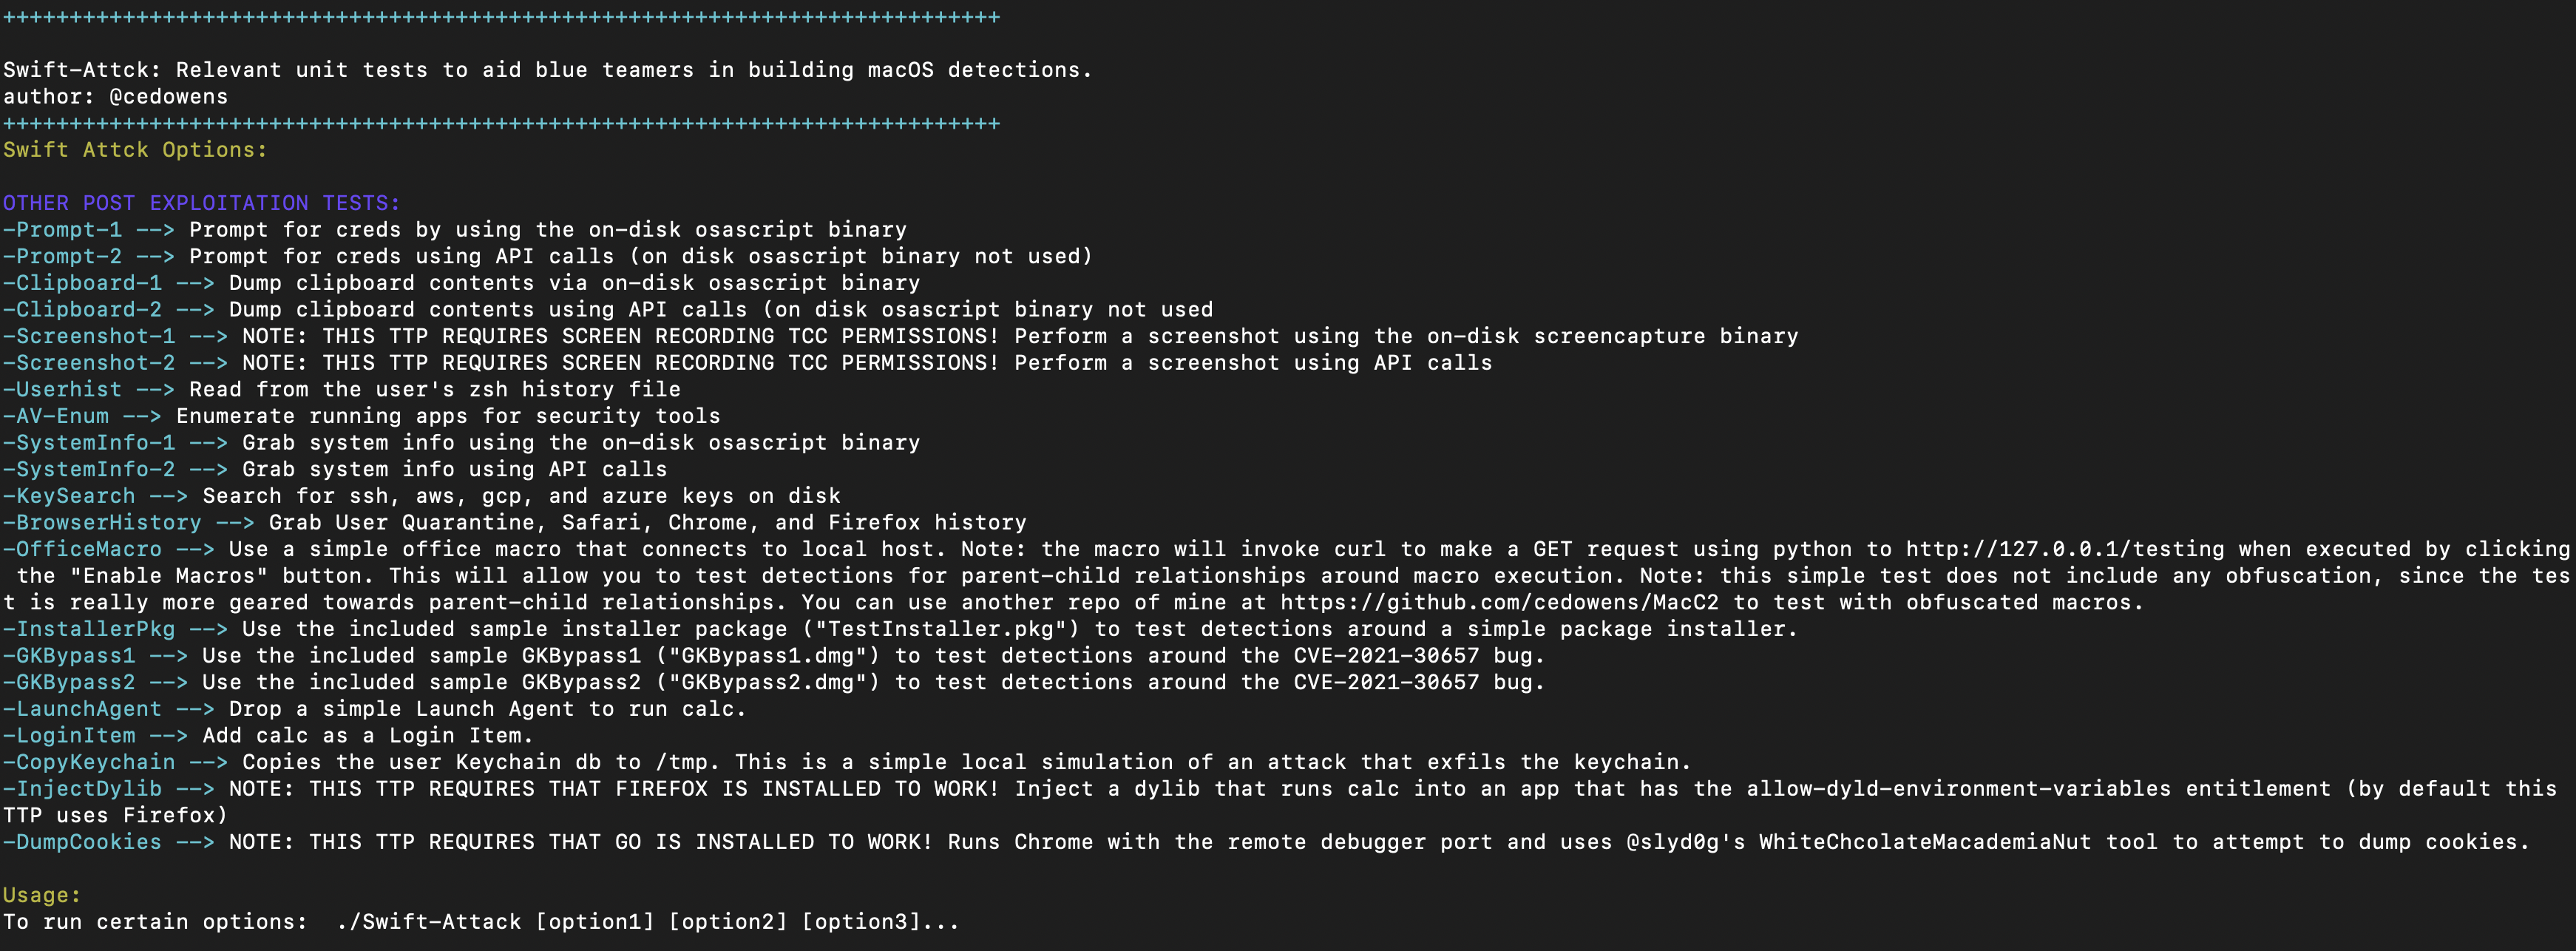 cedowens/swift-attack
Unit tests for blue teams to aid with building detections for some common macOS post exploitation methods.
 34zy/nerv0usr4bbit
Nerv0us r4bbit - Post Exploitation Windows Enumeration Tool
 matheuzsecurity/furtex
Post-exploitation and evasion research toolkit for Linux.