
SniffAir
 tylous/sniffair
A framework for wireless pentesting.
exploitationinformation-gatheringpenetration-testing+3
tylous/sniffairA framework for wireless pentesting.
 sec-consult/aggrokatz
Aggrokatz is an aggressor plugin extension for Cobalt Strike which enables pypykatz to interface with the beacons remotely and allows it to parse…
 w4r10ck423/envvisualizer
Parse and visualize /proc/self/environ on compromised Linux boxes — categorizes env vars by tech stack (AWS, Django, Rails, NodeJS, MySQL, K8s,…
 byt3bl33d3r/pymalleablec2
Python interpreter for Cobalt Strike Malleable C2 Profiles. Allows you to parse, build and modify them programmatically.
 vysecurity/cve-2017-8759
CVE-2017-8759 - A vulnerability in the SOAP WDSL parser.
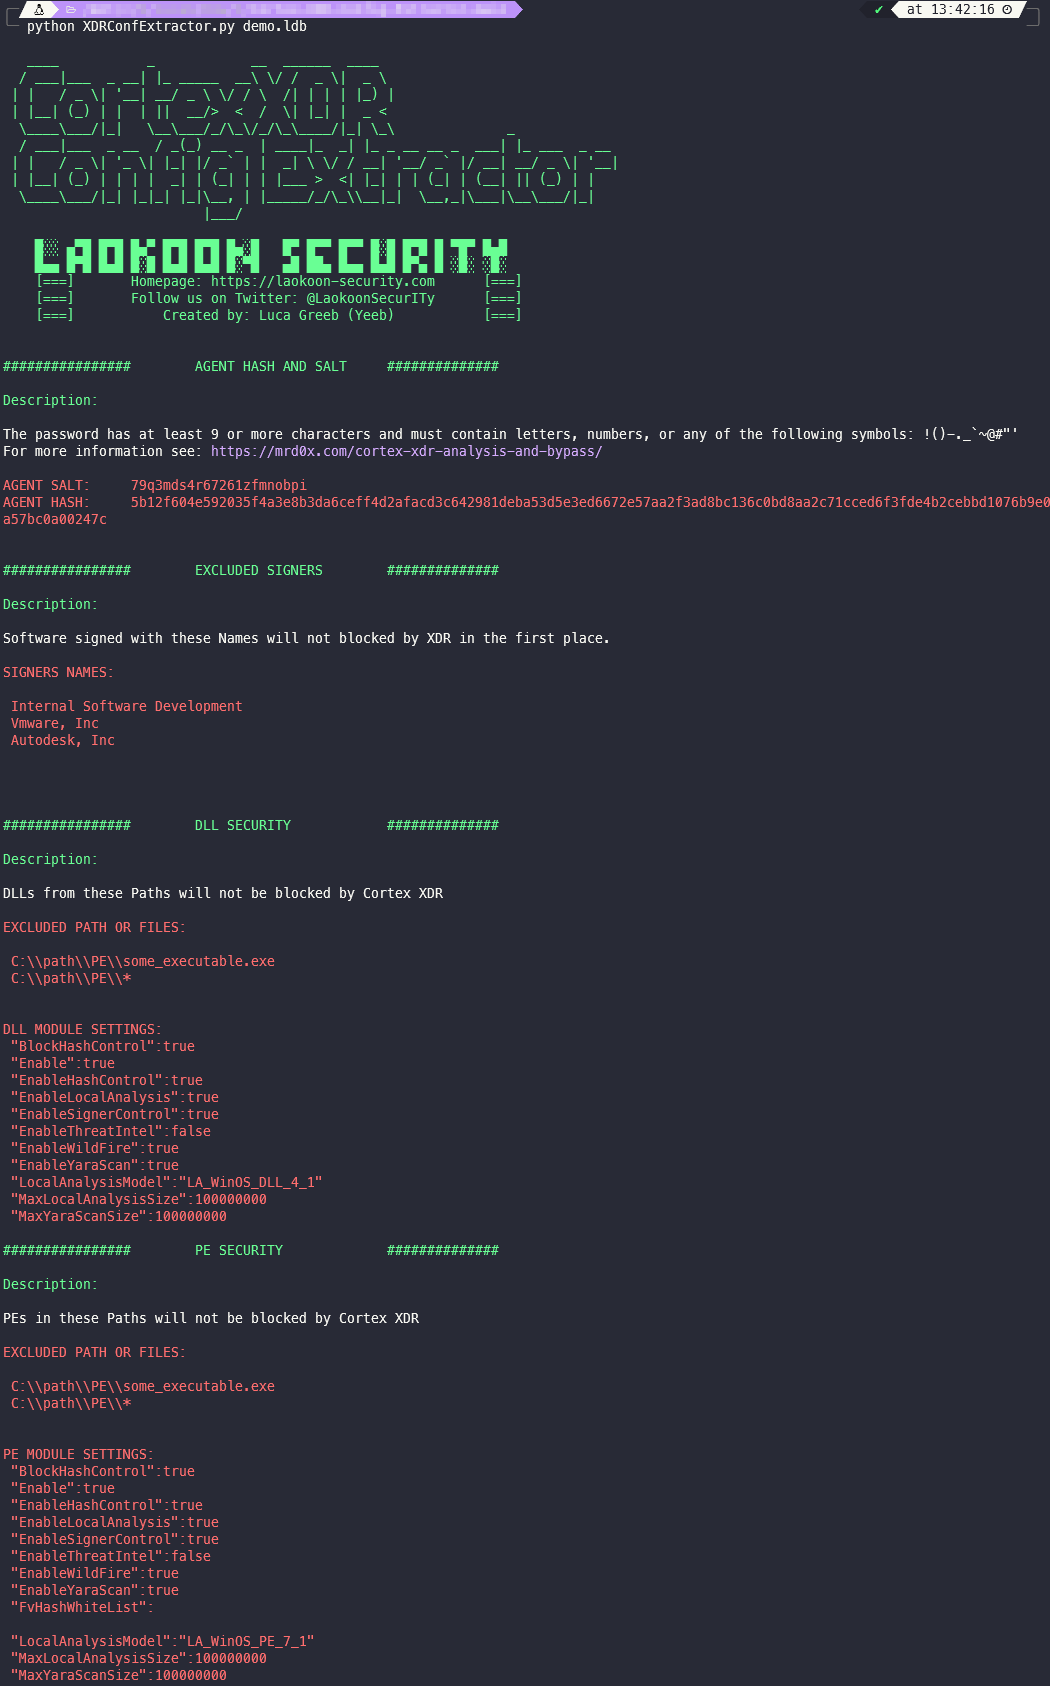 laokoon-security/cortex-xdr-config-extractor
Parses Cortex XDR agent database lock files to extract agent settings, uninstall password hash/salt, and security exclusions for red team assessments…
 kamalx06/xxeripper
Black-box XXE scanner detecting in-band, error-based, and blind out-of-band injection via statistical baselining, parser fingerprinting, and OOB…
 vmtyan/poc-cve-2024-23897
Proof-of-concept exploit for CVE-2024-23897 enabling remote code execution on Jenkins instances via vulnerable args4j command-line parser. Written in…
 24520597-blip/cve-2026-999999
A critical Server-Side Template Injection (SSTI) vulnerability exists in the X-Trading Portal v1.4.2 dashboard metadata rendering engine. The flaw…
 r0xdb/cve-2024-23897
Jenkins 2.441 and earlier, LTS 2.426.2 and earlier does not disable a feature of its CLI command parser that replaces an '@' character followed by a…
 ivancabrera02/srhollow
Extracts LSA secrets and DPAPI keys from Windows registry hives via existing or newly created VSS shadow copies, with an inline regf parser and…
 h4x0r-dz/cve-2024-23897
Python exploit for Jenkins CVE-2024-23897: arbitrary file read via CLI args4j parsing, enabling RCE. Scans hosts and extracts sensitive files from…
 ricardojoserf/whoamialternatives
Different methods to get current username without using whoami
 frkngksl/silentnimvest
Nim implementation for sud0Ru's Credential Dumping from SAM/SECURITY Hives Method (a.k.a. SilentHarvest)
 plantdaddy/fuzzap
A python script for obfuscating wireless networks
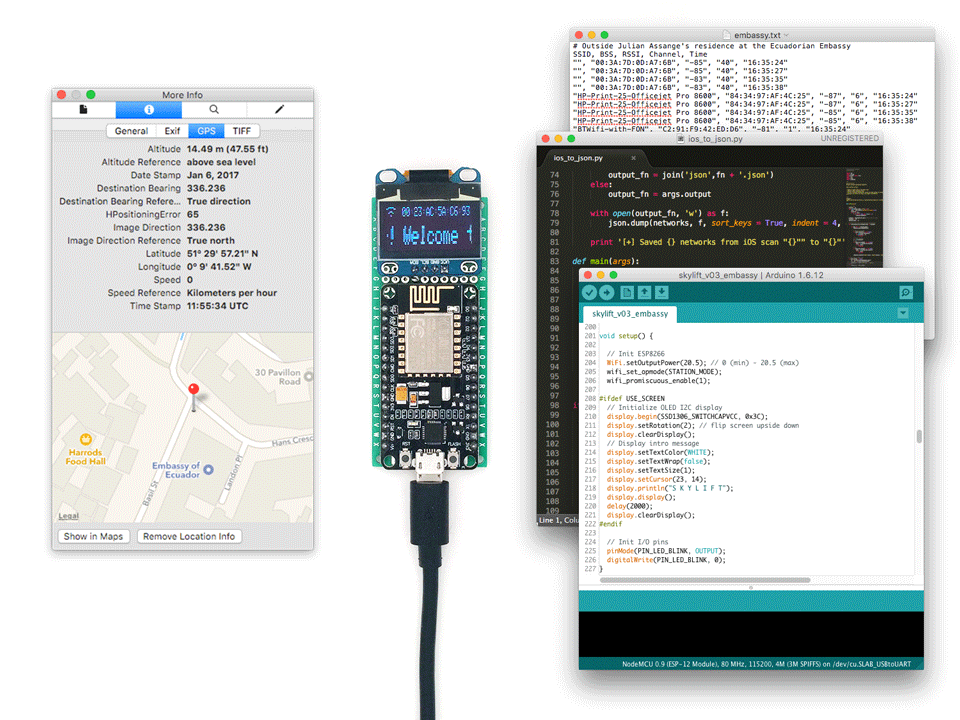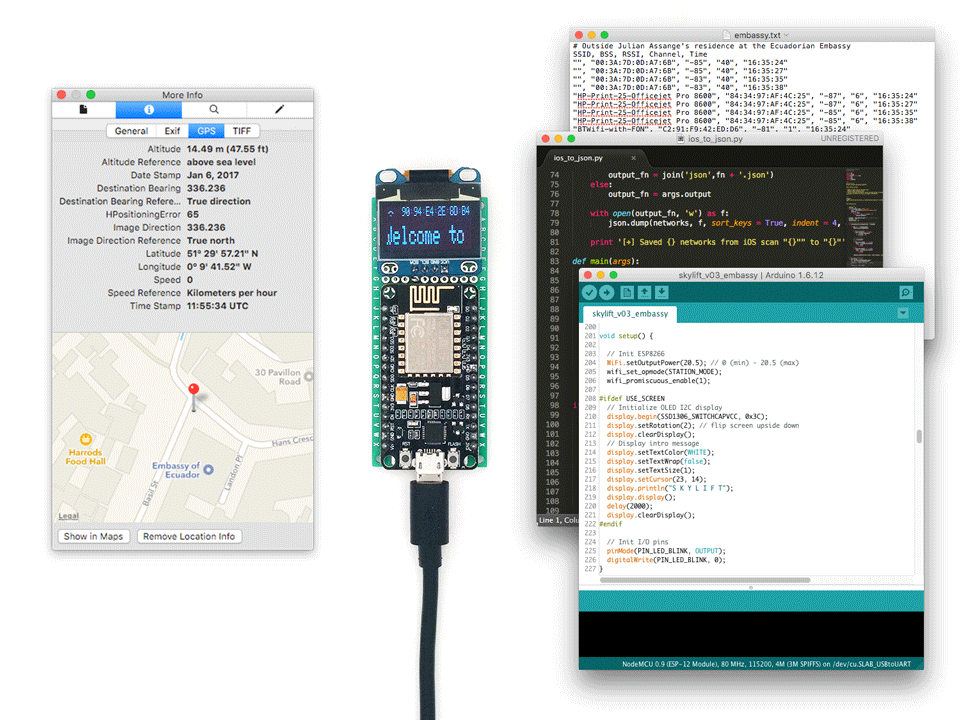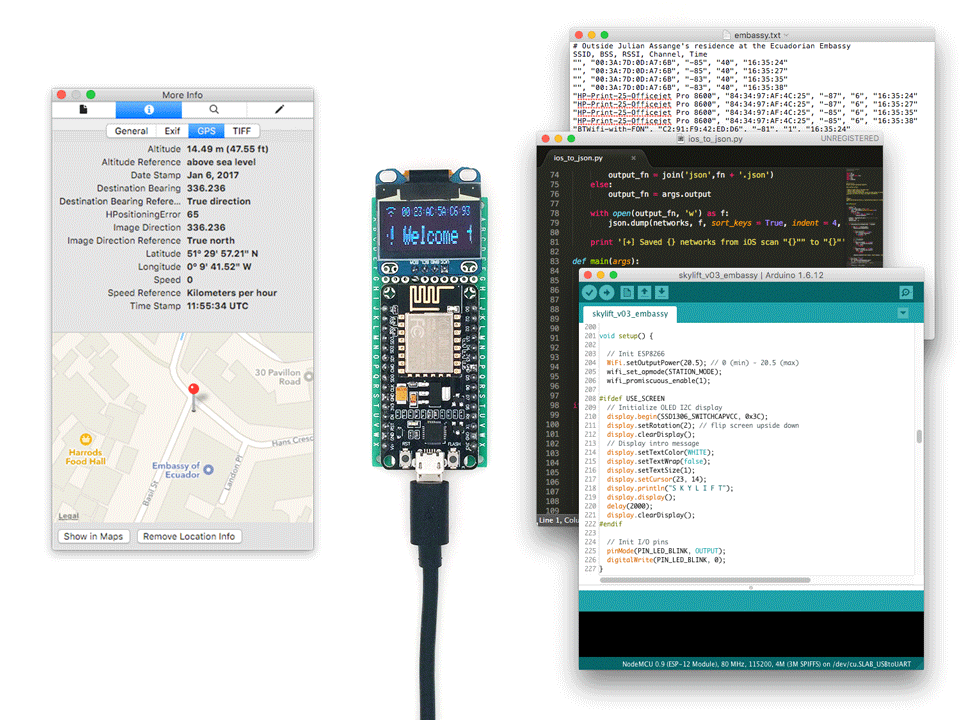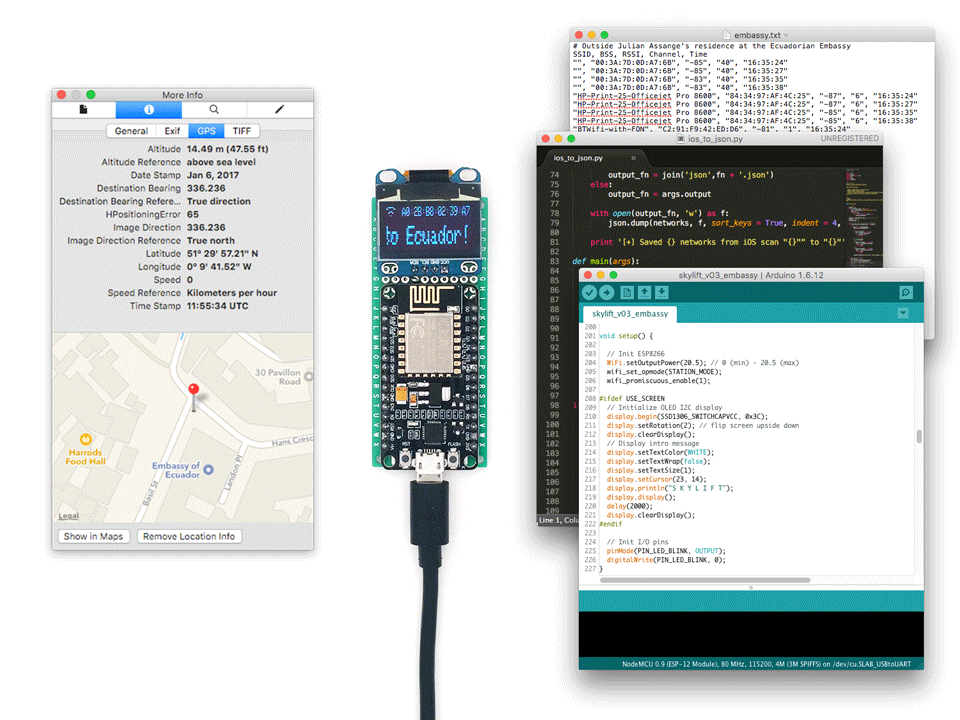 awesome-pentest-gadgets/skylift
WiFi Geolocation Spoofing with the ESP8266
 thoxy67/zig-pe
Reflective PE loader written in Zig. Loads and executes native and .NET PE files directly from memory.
 rnb-team/loghound
Post-Exploitation EVTX Analyzer for BloodHound Mapping