
Owasp-top-10-k8s-2025
 hac01/owasp-top-10-k8s-2025
Hands-on capture-the-flag lab for the OWASP Kubernetes Top 10 (2025). Exploit 11 real-world cluster weaknesses, capture flags, then apply fixes and…
cloud-securitycontainer-securityctf+8
50
hac01/owasp-top-10-k8s-2025Hands-on capture-the-flag lab for the OWASP Kubernetes Top 10 (2025). Exploit 11 real-world cluster weaknesses, capture flags, then apply fixes and…
 lincolino/lab-annie
Automates exploitation of CVE-2020-13160, a critical remote code execution vulnerability in AnyDesk 5.5.2, enabling penetration testers to validate…
 portbuster1337/lpe-toolkit
Multi-architecture Linux privilege escalation toolkit with 29 pre-built and runtime-compilable exploits. Auto-detects kernel version, filters patched…
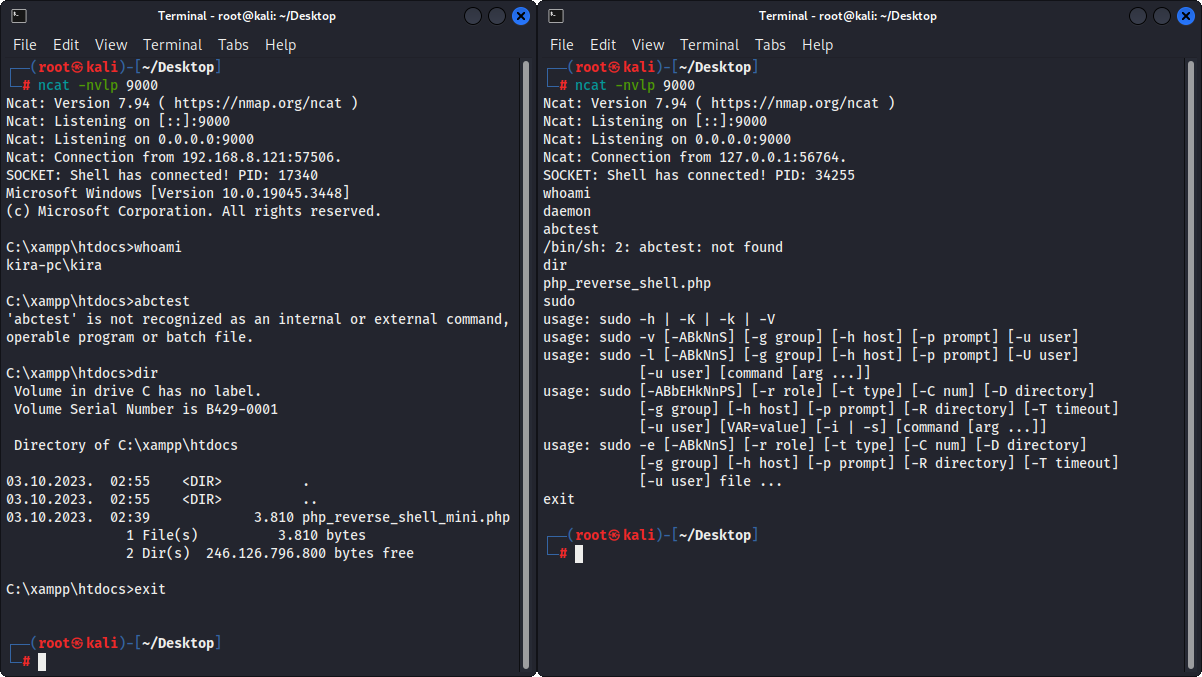 ivan-sincek/php-reverse-shell
PHP shells that work on Linux OS, macOS, and Windows OS.
 redcanaryco/chain-reactor
Generate Linux executables that simulate adversary behaviors and techniques for testing detection and response coverage. Consumes JSON for easy…
 trevohack/dynastypersist
Linux persistence toolkit with 11 modules for SSH key backdoors, cronjobs, systemd services, LKM rootkits, and LD_PRELOAD privilege escalation.…
 buter-chkalova/project-rvbbit
Educational Linux kernel rootkit PoC exploring DKOM, syscall hooking, stealth, observability and defensive detection
 undeadsec/socialfish
Modern dynamic phishing toolkit for authorized red team exercises. Clones login pages, captures credentials, cookies, and 2FA codes with a live…
 yogsec/hacking-tools
A curated list of penetration testing and ethical hacking tools, organized by category. This compilation includes tools from Kali Linux and other…
 ahegazy0/linux-basics-for-hackers-notes
A structured course built from personal study notes of the book Linux Basics for Hackers by OccupyTheWeb.
 outflanknl/evilclippy
A cross-platform assistant for creating malicious MS Office documents. Can hide VBA macros, stomp VBA code (via P-Code) and confuse macro analysis…
 gosecure/pyrdp
RDP monster-in-the-middle (mitm) and library for Python with the ability to watch connections live or after the fact
 specterops/skills
Reusable offensive security skills and plugins for AI agents, covering reconnaissance, exploitation, C2, payload development, and reporting across…
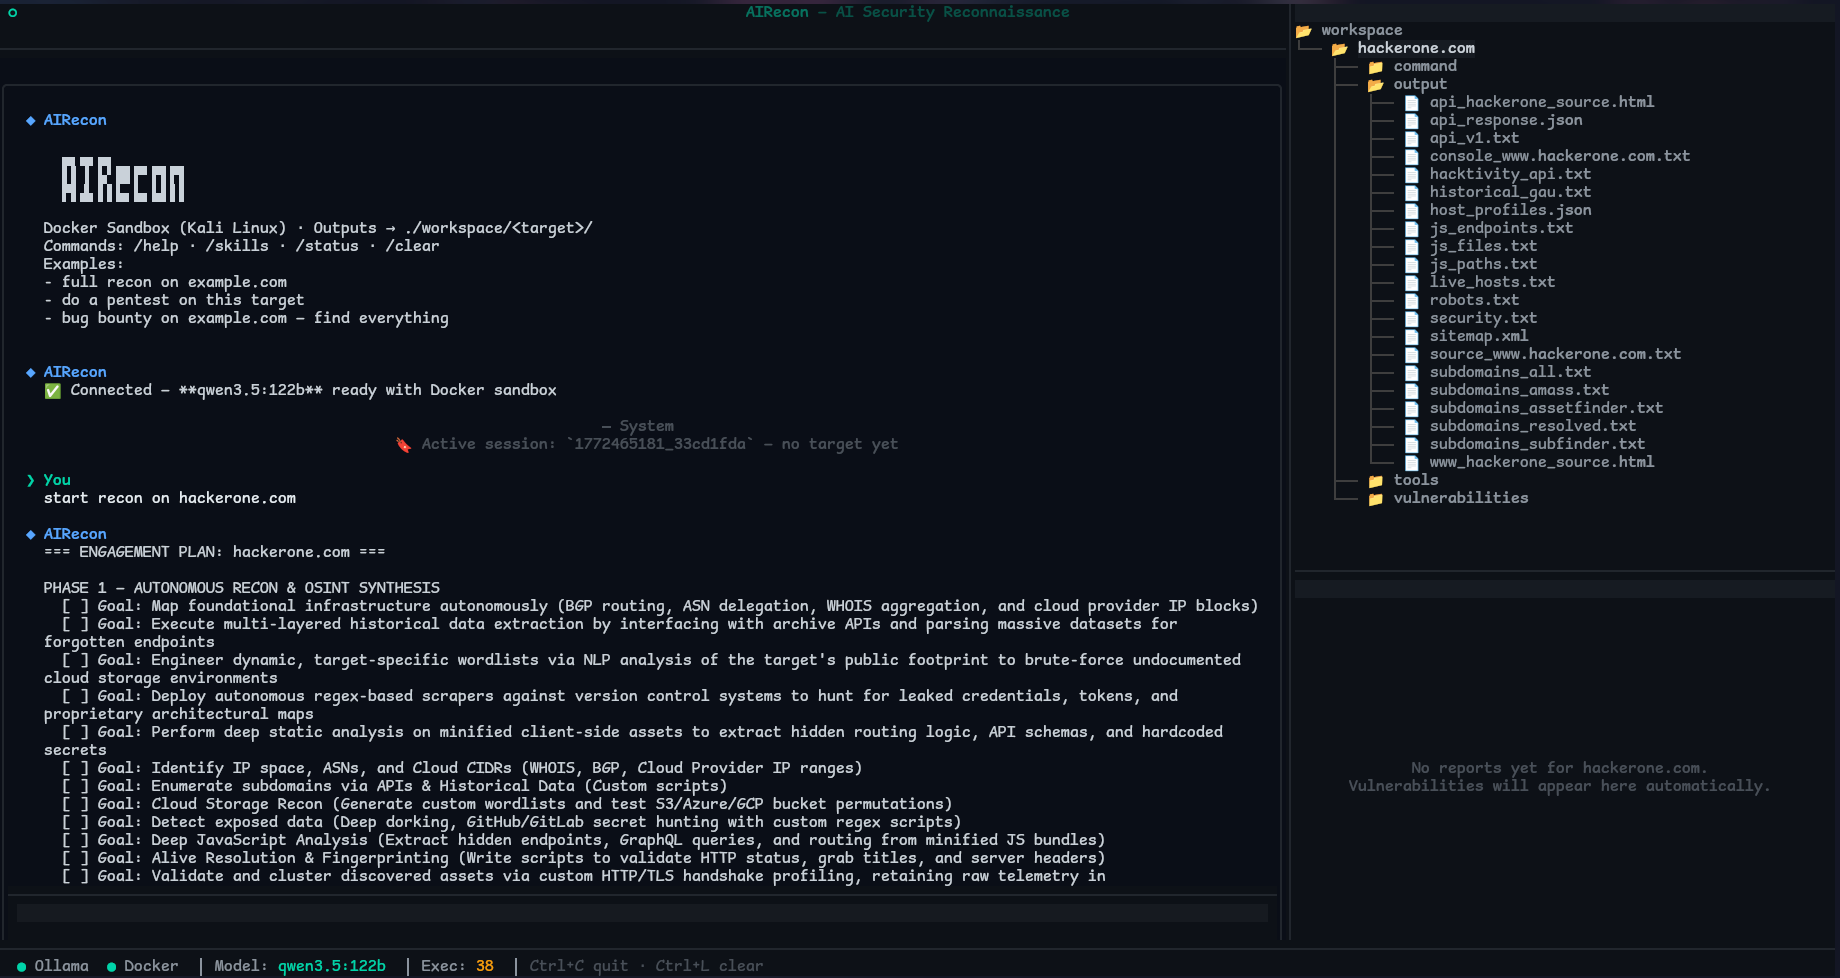 pikpikcu/airecon
AIRecon is an autonomous cybersecurity agent that combines a self-hosted Large Language Model (Ollama) with a Kali Linux Docker sandbox and a Textual…
 goshs-labs/goshs
Feature-rich single-binary file server for red teamers and developers. HTTP/S · WebDAV · FTP/SFTP · SMB · LDAP/S · NTLM hash capture · DNS/SMTP…
 nongiach/sudo_inject
[Linux] Two Privilege Escalation techniques abusing sudo token
 flamingspork/iptable_evil
Kernel-level iptables backdoor that accepts all packets with the RFC 3514 evil bit set, bypassing firewall rules. Includes in-tree and out-of-tree…
 karazajac/dirtyfail
Detector + PoC for Linux page-cache write vulnerabilities: Copy Fail (CVE-2026-31431) and Dirty Frag (CVE-2026-43284/43500). Authorized security…