CVE-2023-33105-Transient-DOS-in-WLAN-Host-and-Firmware

This repository contains the exploit code for CVE-2023-33105, a vulnerability identified in Qualcomm devices. The exploit leverages authentication…

This repository contains the exploit code for CVE-2023-33105, a vulnerability identified in Qualcomm devices. The exploit leverages authentication…

Proof-of-concept backdoor for SCCM Management Point using rogue COM service for persistent remote command execution as SYSTEM.

Rogue access point attack and defense on Kali Linux: deauth with aireplay-ng, an airbase-ng evil twin with a captive portal, plus real-time…

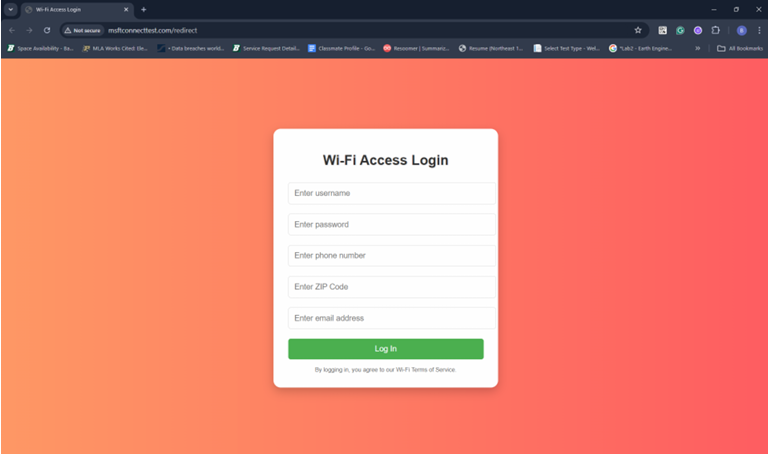
Rogue access point toolkit for WiFi penetration testing, deploying evil portal phishing payloads to capture credentials and perform social…

[NOT MAINTAINED] This script creates a NATed or Bridged WiFi Access Point.

PoC for CVE-2019-6203, works on < iOS 12.2, macOS < 10.14.4

A "Exposed Dangerous Method or Function" or "Use of Hard-coded, Security-relevant Constants" vulnerability in PrintixService.exe, in Kofax Printix's…

Proof-of-concept Denial of Service exploit for CVE-2020-1350 (SIGRed) targeting Windows DNS servers via crafted DNS SIG records. Includes PCAP for…

Mass scanner for CVE-2024-24919

ppsx file generator for cve-2017-8570 (based on bhdresh/cve-2017-8570)