

Hollow
 chaelsoo/hollow
A shellcode loader generator with support for multiple injection techniques, built for red team engagements.
binary-exploitationencryption-decryption-toolsexploitation+7
102
chaelsoo/hollowA shellcode loader generator with support for multiple injection techniques, built for red team engagements.
 voidsecsoftwares/voidsyscall
Cross-platform syscall-powered implant & C2 — direct syscalls (Win), raw syscalls (Linux), HTTPS/DNS/ICMP channels. No winapi layer.
 knight0x07/bumblecrypt
A Bumblebee-inspired Crypter
 lawndoc/mediator
An extensible, end-to-end encrypted reverse shell that works across networks without port forwarding.
 weedhashpeddler/rc4decryption
Abuses the Microsoft-signed tlscsp.dll LOLBin to run RC4 encrypt/decrypt via LsCsp_EncryptHwid, patching the hardcoded key in memory for BYOK…
 28zaaky/pulse-c2
HTTPS C&C Framework with encrypted beacons, web dashboard, and Windows agent.
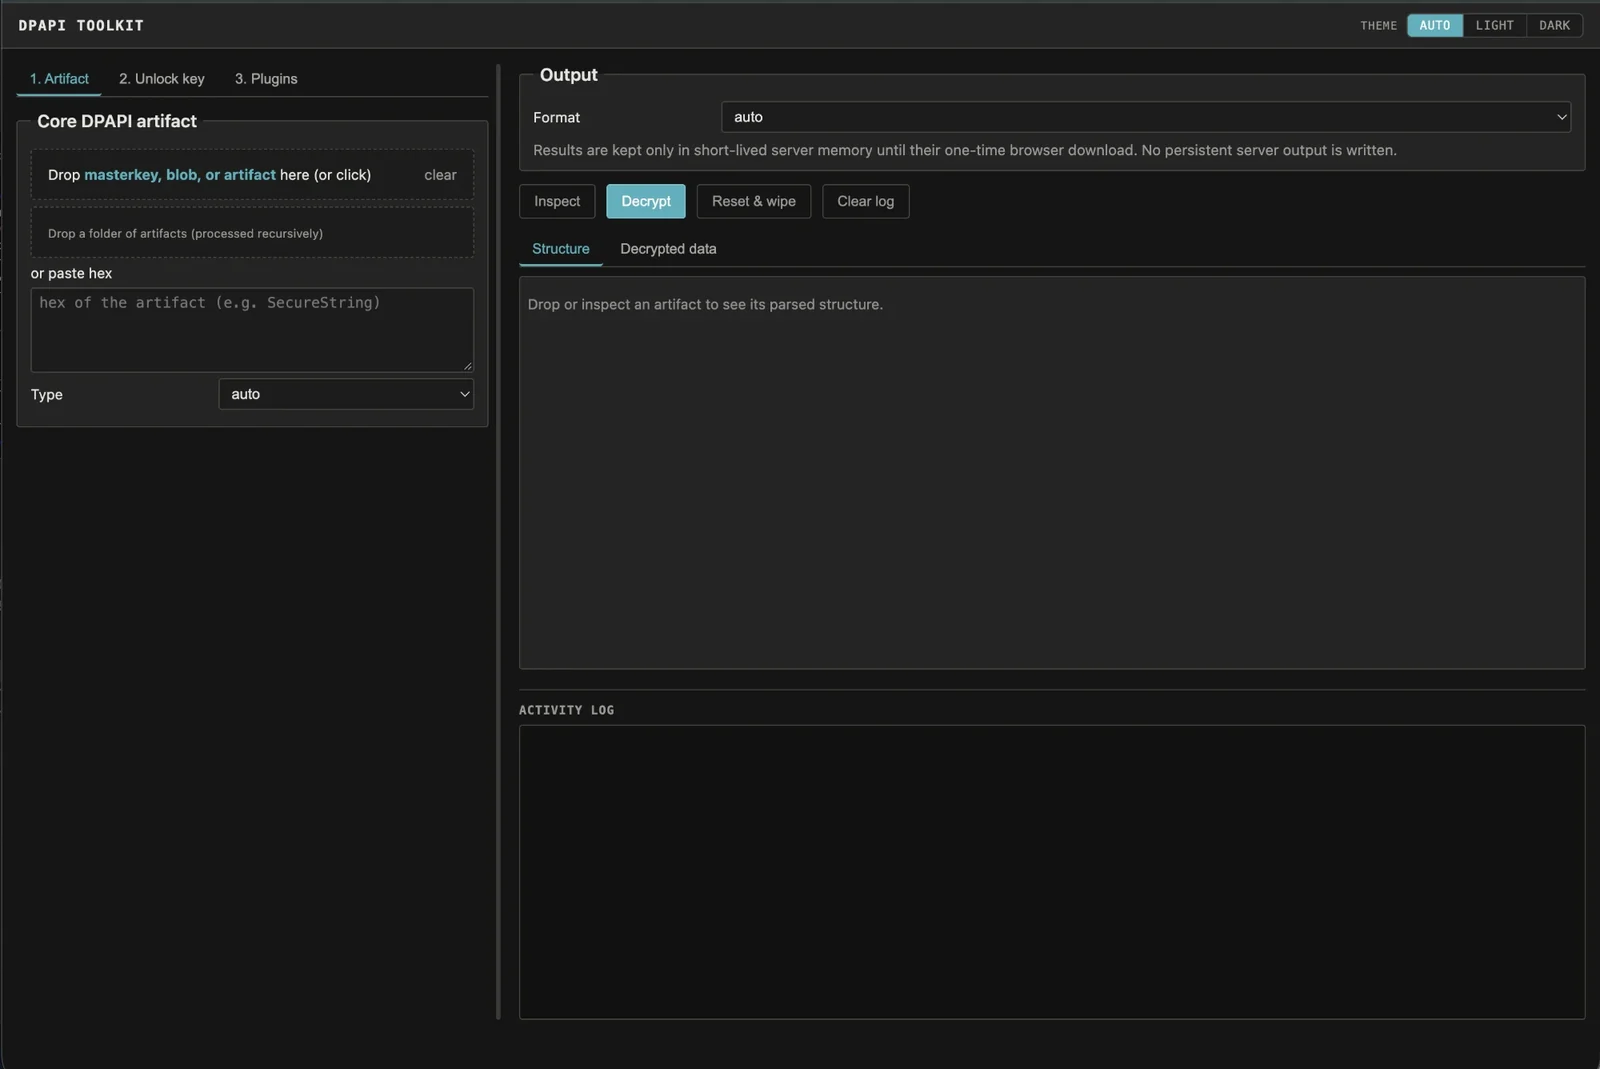 crypt0p3g/dpapi-toolkit
Drop any Windows DPAPI artifact and it identifies the format and the exact master key it needs, then decrypts once you supply the key. Offline, CLI +…
 rek7/ddoor
DDoor - cross platform backdoor using dns txt records
 s1lkys/phantomfs
Serving payloads only to allowed processes using Windows projected file system feature
 synacktiv/laravel_cookie_killer
Decrypt and re-encrypt Laravel session cookies to exploit insecure PHP deserialization for remote code execution.
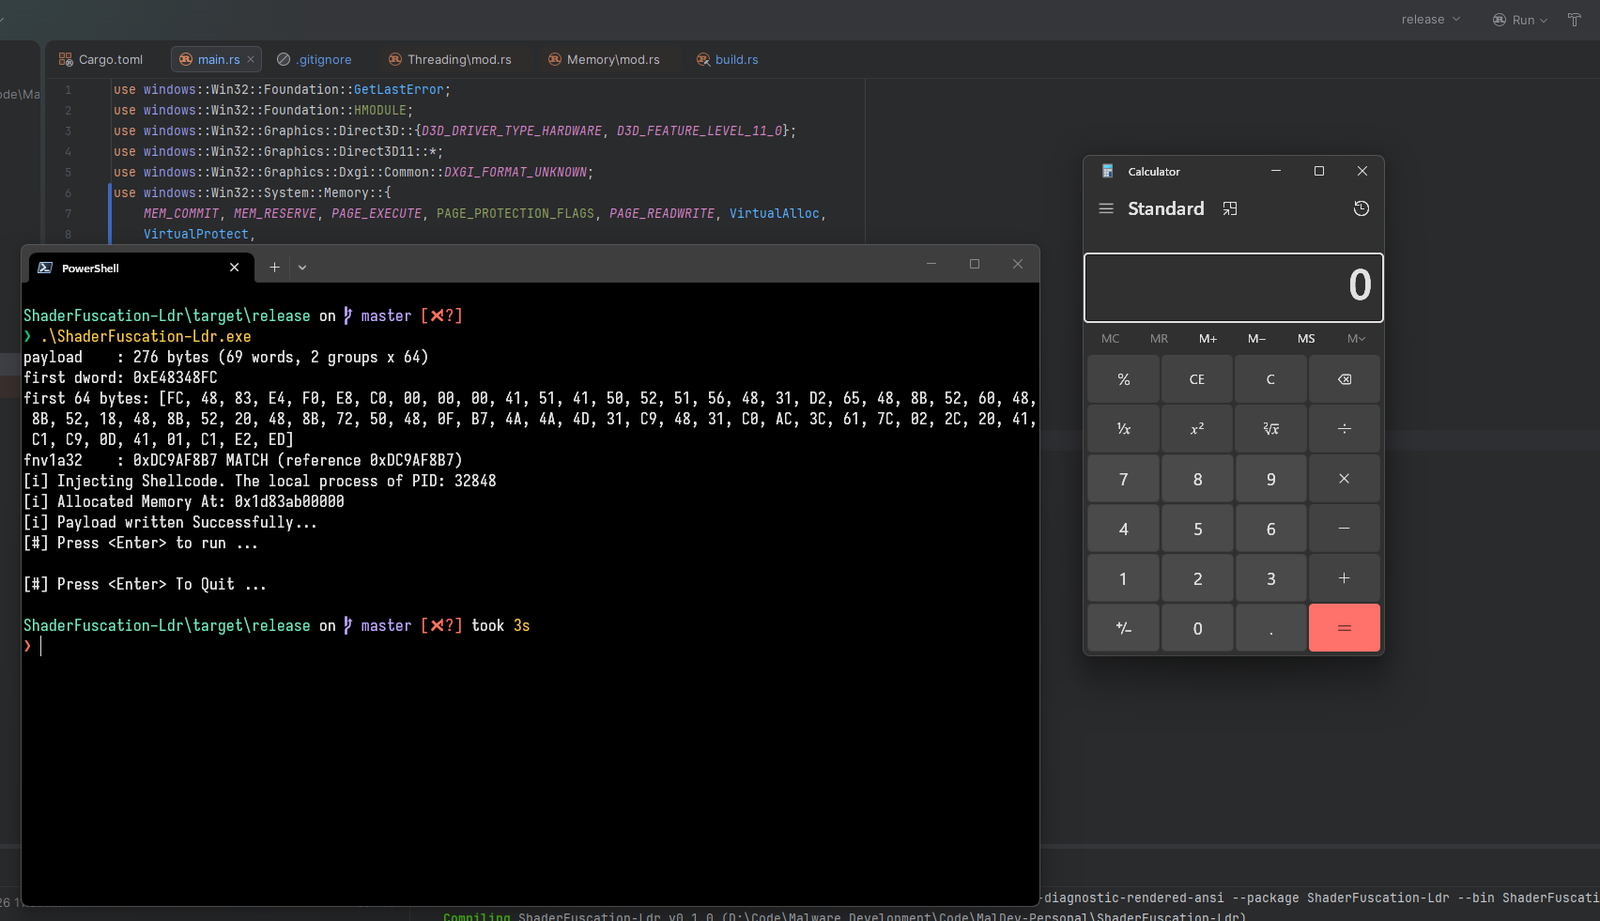 dovelus/polychrome-rs
A PoC on how to use a Compute Shader as Payload
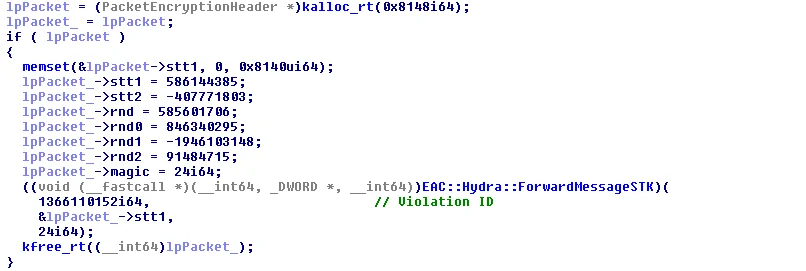 gmh5225/eac-kernel-packet-fucker
Reverse-engineered Easy Anti-Cheat kernel driver bypass that intercepts memory allocation to suppress violation packets, with report decryption…
 regent8sh/panosexploitmultitool
Exploitation and Post-Exploitation Multitool for Palo Alto PAN-OS Systems affected by vulnerabilities CVE-2024-0012 and CVE-2024-9474
 cenobyte-vincit/encrypted-linux-kernel-modules
encrypted-linux-kernel-modules
 davidcarliez/mythic_telegram_profile
Mythic C2 profile that tunnels Athena and Apollo agent traffic through Telegram bot-to-bot messages, bridging encrypted payloads to Mythic via its…
 shehzade/peeping-tom
Remote Windows keylogger with AES-256 encrypted keystroke exfiltration via configurable callback intervals and a companion Python server for log…
 chandermanipandey2022/yellow-key-check
YellowKey | BitLocker Bypass Vulnerability (CVE-2026-45585)
 web-logs2/snapshot-demo
CVE-2022-27499