

CVE-2020-0688
 tvdat20004/cve-2020-0688
CVE-2020-0688: Remote Code Execution on Microsoft Exchange Server Through Fixed Cryptographic Keys
exploitationpayload-generationpenetration-testing+3
tvdat20004/cve-2020-0688CVE-2020-0688: Remote Code Execution on Microsoft Exchange Server Through Fixed Cryptographic Keys
 cediegreyhat/bigfinger
CVE-2023-46747-RCE PoC
 mandatoryprogrammer/sonar.js
A framework for identifying and launching exploits against internal network hosts. Works via WebRTC IP enumeration combined with WebSockets and…
 overgrowncarrot1/cve-2021-22911
Python exploit script for CVE-2021-22911 targeting Rocket.Chat admin password reset via unauthenticated user registration. Automates exploitation…
 ludy-dev/big-ip-f5-tmui-rce-vulnerability
(CVE-2020-5902) BIG IP F5 TMUI RCE Vulnerability RCE PoC/ Test Script
 ariary/notionterm
Embed a reverse shell in Notion pages using the Notion API as a proxy, enabling stealthy remote shell sessions with encrypted and authenticated…
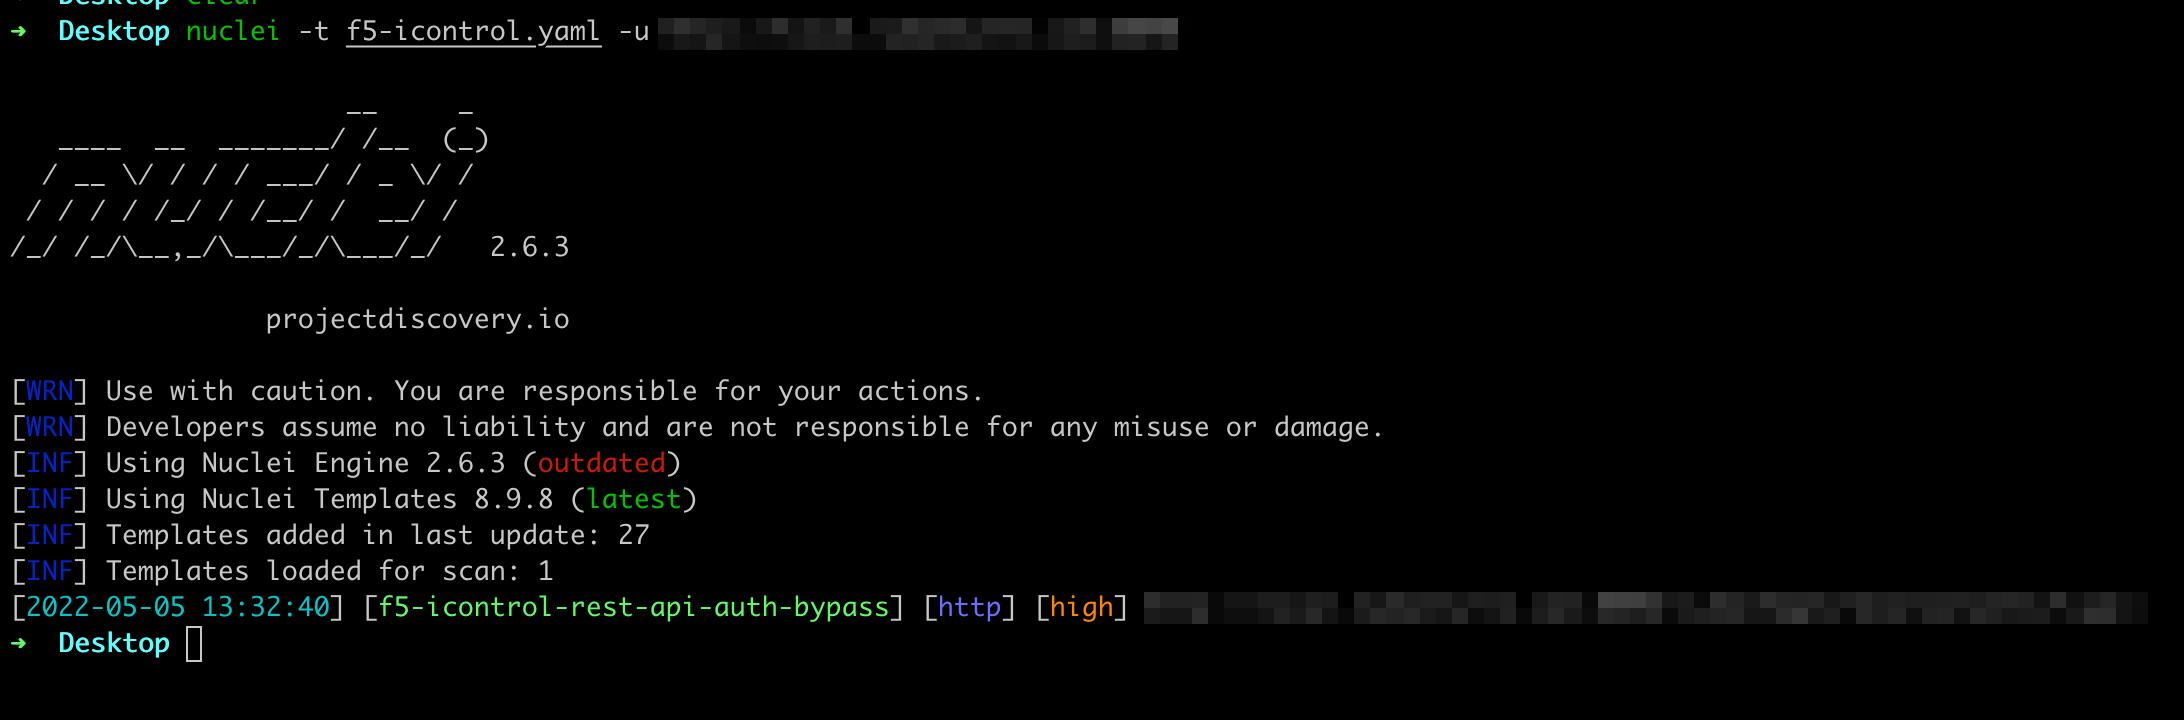 numanturle/cve-2022-1388
K23605346: BIG-IP iControl REST vulnerability CVE-2022-1388
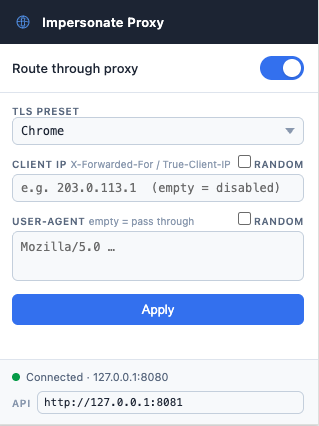 ytkoka/impersonate-proxy
A local MITM proxy that lets you control TLS fingerprints (JA3/JA4), HTTP/2 fingerprints, HTTP header order, and User-Agent — all from a single YAML…
 d4rk007/f5-big-ip-cve-2020-5902-mass-exploiter
Mass exploiter for CVE-2020-5902 targeting F5 Big-IP devices, with multi-threaded scanning and exploitation capabilities for unauthenticated remote…
 stonzyy/exploit-f5-cve-2022-1388
PoC For F5 BIG-IP - bash script Exploit one Liner
 jiahong-guan/log4j-shell-poc
A Proof-Of-Concept for the CVE-2021-44228 vulnerability.
 litndat/camera-dahua-research-l-h-ng-cve-2021-33044
DAHUA_AUTH-BYPASS-CVE-2021-33044
 kondordevsecuritycorp/cve-2026-34197
Exploit for Apache ActiveMQ RCE via Jolokia API (CVE-2026-34197) with command output capture, mass scanning, and auto-exploitation.
 aancw/cve-2022-1388-rs
CVE-2022-1388 F5 BIG-IP iControl REST Auth Bypass RCE written in Rust
 labdookhtegan/cve-2020-0796-exp
CVE-2020-0796-EXP
 feng-huang-0520/dataease_postgresql_jdbc_bypass-cve-2025-49002
Proof-of-concept exploit for CVE-2025-49002, a remote code execution vulnerability in DataEase via PostgreSQL JDBC bypass, including a crafted HTTP…
 bysinks/cve-2022-22947
Exploit for CVE-2022-22947 in Spring Cloud Gateway, allowing remote code execution via SpEL expressions. Affects versions < 3.1.1 and < 3.0.7.
 cuerv0x/cve-2015-6967
Python exploit for CVE-2015-6967 targeting Nibbleblog with a reverse shell payload. Executes authenticated remote code execution via file upload…