
AutoSploit
 nullarray/autosploit
Automated Mass Exploiter
command-and-controlexploit-frameworksinformation-gathering+5
nullarray/autosploitAutomated Mass Exploiter
 itsecurityco/cve-2021-41773
Proof-of-concept exploit for Apache HTTP Server path traversal vulnerability CVE-2021-41773, with Docker setup and detailed vulnerability analysis.
 milesrichardson/docker-onion-nmap
Scan .onion hidden services with nmap using Tor, proxychains and dnsmasq in a minimal alpine Docker container.
 cr0nx/awesome-linux-attack-forensics-purplelabs
This page is a result of the ongoing hands-on research around advanced Linux attacks, detection and forensics techniques and tools.
 hakaioffsec/ingressnightmare-poc
This is a PoC code to exploit the IngressNightmare vulnerabilities (CVE-2025-1097, CVE-2025-1098, CVE-2025-24514, and CVE-2025-1974).
 hac01/owasp-top-10-k8s-2025
Hands-on capture-the-flag lab for the OWASP Kubernetes Top 10 (2025). Exploit 11 real-world cluster weaknesses, capture flags, then apply fixes and…
 corvralabs/evilneko
Automated container orchestration tool for Browser-in-the-Browser (BITB) phishing attacks, enabling red teams to scale multi-target infrastructure…
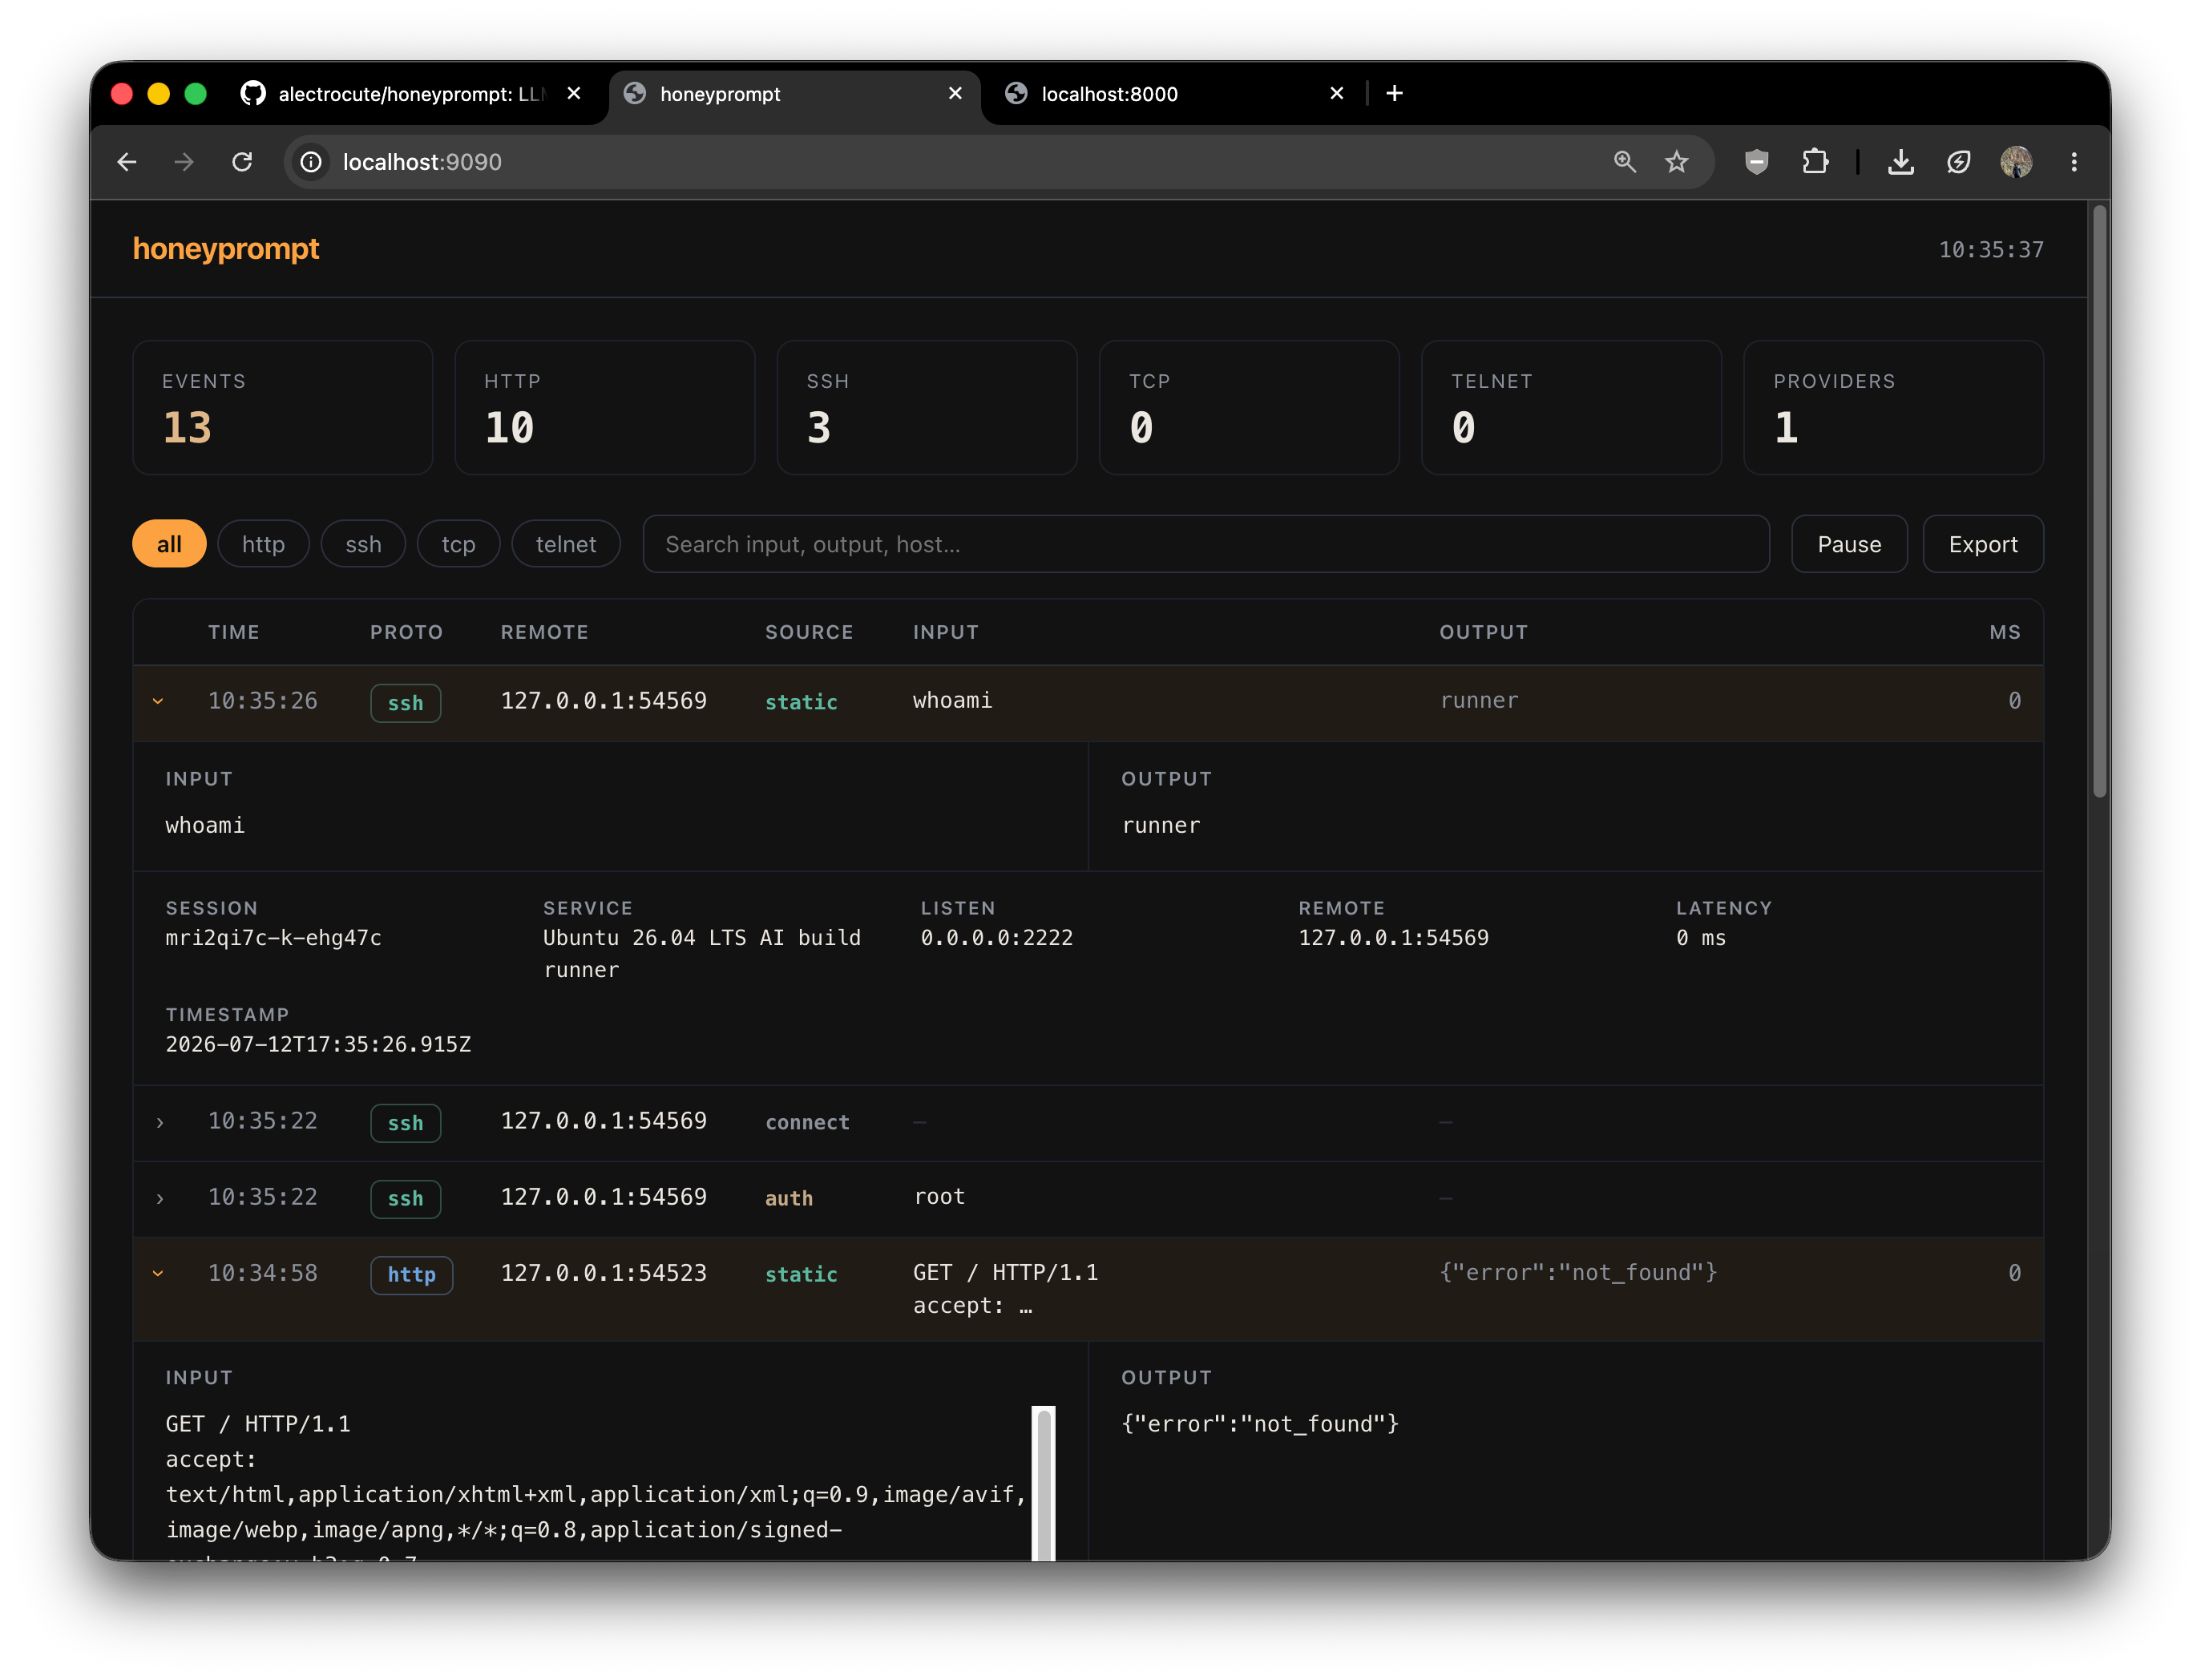 alectrocute/honeyprompt
LLM-first deception framework: "The honeypot that talks back!™"
 strikoder-premium/cve-2024-21626-runc-1.1.11-escape
PoC for CVE-2024-21626: runc leaks an internal fd referencing the host CWD before pivot_root, enabling container escape by setting process.cwd to…
 eyodav/cve-2025-34159
A critical Remote Code Execution (RCE) vulnerability exists in Coolify's application deployment workflow. This flaw allows a low-privileged member to…
 abdurahmon3236/cve-2024-36539
PoC exploit for insecure permissions in Contour v1.28.3 that retrieves a Kubernetes service account token and accesses the cluster API, demonstrating…
 atlasvector/kestra-cve-2026-53576
End-to-end reproduction and cross-layer detection of CVE-2026-53576, the unauthenticated RCE in Kestra — taken past the base PoC to show how a common…
 initstring/lxd_root
Linux privilege escalation via LXD
 eeriedusk/nysm
eBPF-based stealth container that hides processes, sockets, eBPF objects, and audit logs from system monitoring tools, enabling covert…
 twistlock/runc-cve-2019-5736
CVE-2019-5736 POCs
 tabbysable/poc-2020-8558
Information about Kubernetes CVE-2020-8558, including proof of concept exploit.
 boianeduard/cve-2025-1974
ingress-nginx admission controller RCE escalation PoC