
Archived
gato
 praetorian-inc/gato
GitHub Actions Pipeline Enumeration and Attack Tool
devsecopsexploitationinformation-gathering+7
9
 wddadk/offensive-osint-tools
Curated list of OSINT tools for offensive security, covering email harvesting, subdomain enumeration, threat intelligence, and social engineering for…
 ly4k/certipy
Tool for Active Directory Certificate Services enumeration and abuse
 uphiago/recon-skills
Field-validated offensive security skill pack with 169 techniques for reconnaissance and penetration testing. Covers CORS, SSRF, subdomain takeover,…
 capture0x/adstrike
AI-powered modular Active Directory red-team framework for authorized penetration testing, AD enumeration, attack-path analysis, Kerberos/ADCS…
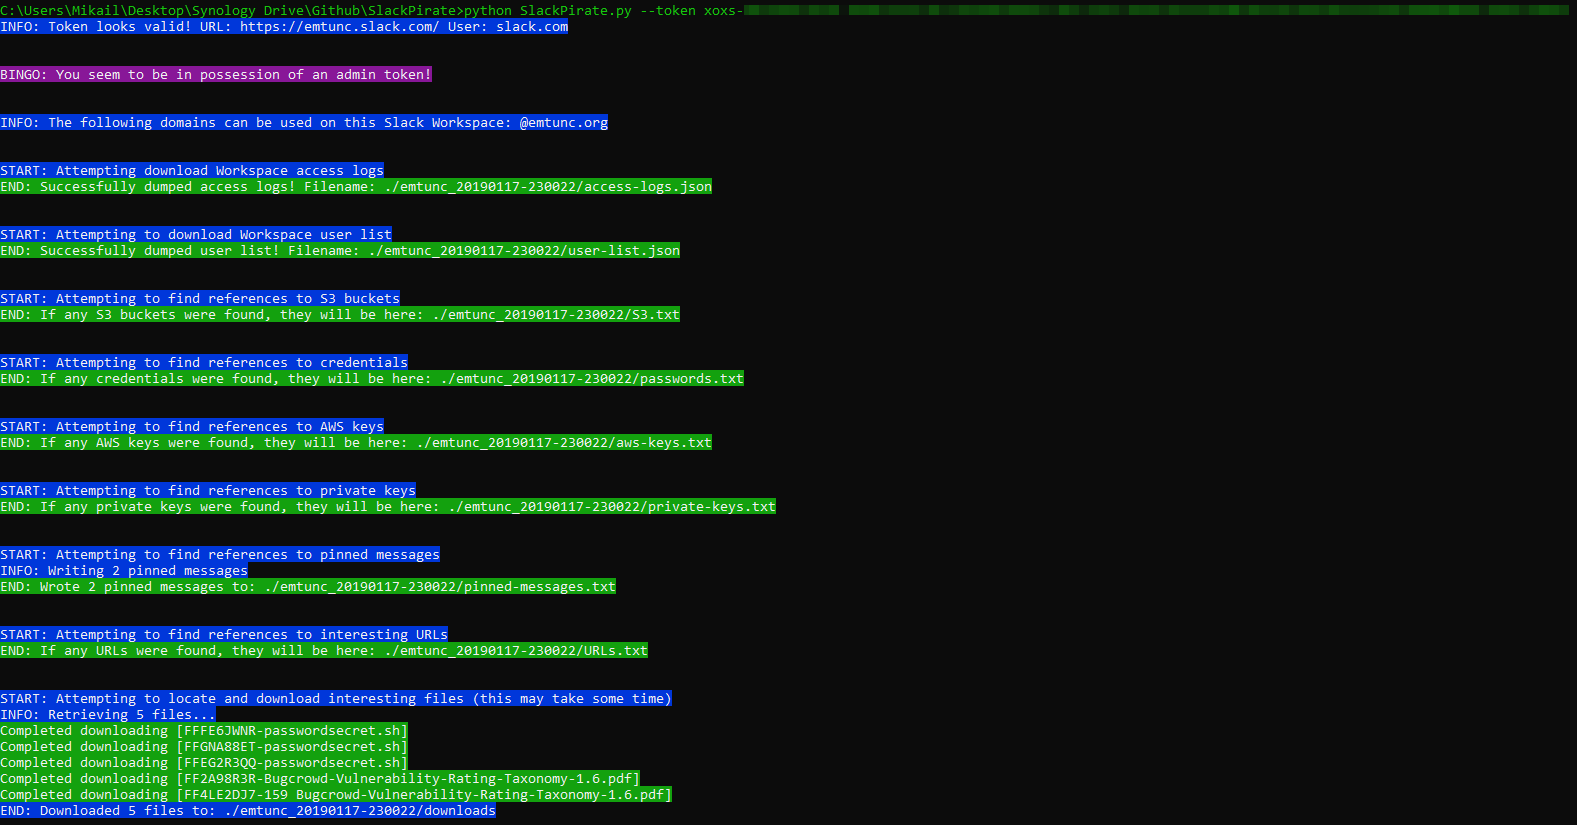 emtunc/slackpirate
Slack Enumeration and Extraction Tool - extract sensitive information from a Slack Workspace
 thundergunexpress/badministration
Offensive tool for exploiting management applications (SolarWinds Orion, McAfee ePO) via non-technical vulnerabilities. Enables client enumeration,…
 kozmer/aad-bofs
Cobalt Strike BOF collection for attacking Azure AD during red team operations, covering authentication, enumeration, and post-exploitation vectors.
 lloydlabs/process-enumeration-stealth
Stealth Windows process enumeration PoC that lists PIDs using NTFS via NtQueryInformationFile, bypassing standard monitoring APIs and enabling EDR…
 daddycocoaman/azbelt
AAD related enumeration in Nim
 karmanya03/overthrone
All-Rust Active Directory exploitation framework: LDAP/SMB/Kerberos enumeration, attack-graph pathfinding, Kerberoasting, NTLM relay, ticket forging,…
 blue0x1/nimux
Pure-Nim network enumeration and remote execution toolkit for authorized security assessments. Supports SMB, LDAP, Kerberos, WinRM, database clients,…
 zales2004/sunset-noontide-pentesting
Description Professional penetration testing assessment of the Sunset: Noontide VulnHub machine, covering reconnaissance, service enumeration,…
 gmh5225/github-gato
GitHub Self-Hosted Runner Enumeration and Attack Tool
 galisko/cve-2025-24799
Unauthenticated SQL injection exploit for GLPI versions before 10.0.18, enabling database enumeration, credential extraction, and API token…
 proxydom/supahunter
Automated reconnaissance and exploitation framework for misconfigured Supabase instances. Features schema enumeration, Selenium-based key extraction,…
 3jee/copy-fail-go
Go port of the CVE-2026-31431 (copy-fail) Linux kernel privilege escalation PoC, with automatic SUID binary enumeration and interactive target…
 plur1bu5/gitread
CVE-2026-85706 · GitLab CE/EE unauthenticated file read · research PoC with oracle mode, fd enumeration, and tiered loot targeting