
CVE-2021-41773
 skentagon/cve-2021-41773
Exploit scripts for Apache HTTP Server 2.4.49 directory traversal vulnerability (CVE-2021-41773), enabling path traversal and potential RCE via…
exploitationpenetration-testingred-teaming+2
skentagon/cve-2021-41773Exploit scripts for Apache HTTP Server 2.4.49 directory traversal vulnerability (CVE-2021-41773), enabling path traversal and potential RCE via…
 sumitpathania03/drupal-cve-2019-6340
Python exploit for Drupal 8 core RESTful API RCE (CVE-2019-6340) that sends crafted requests to execute arbitrary commands on vulnerable sites.
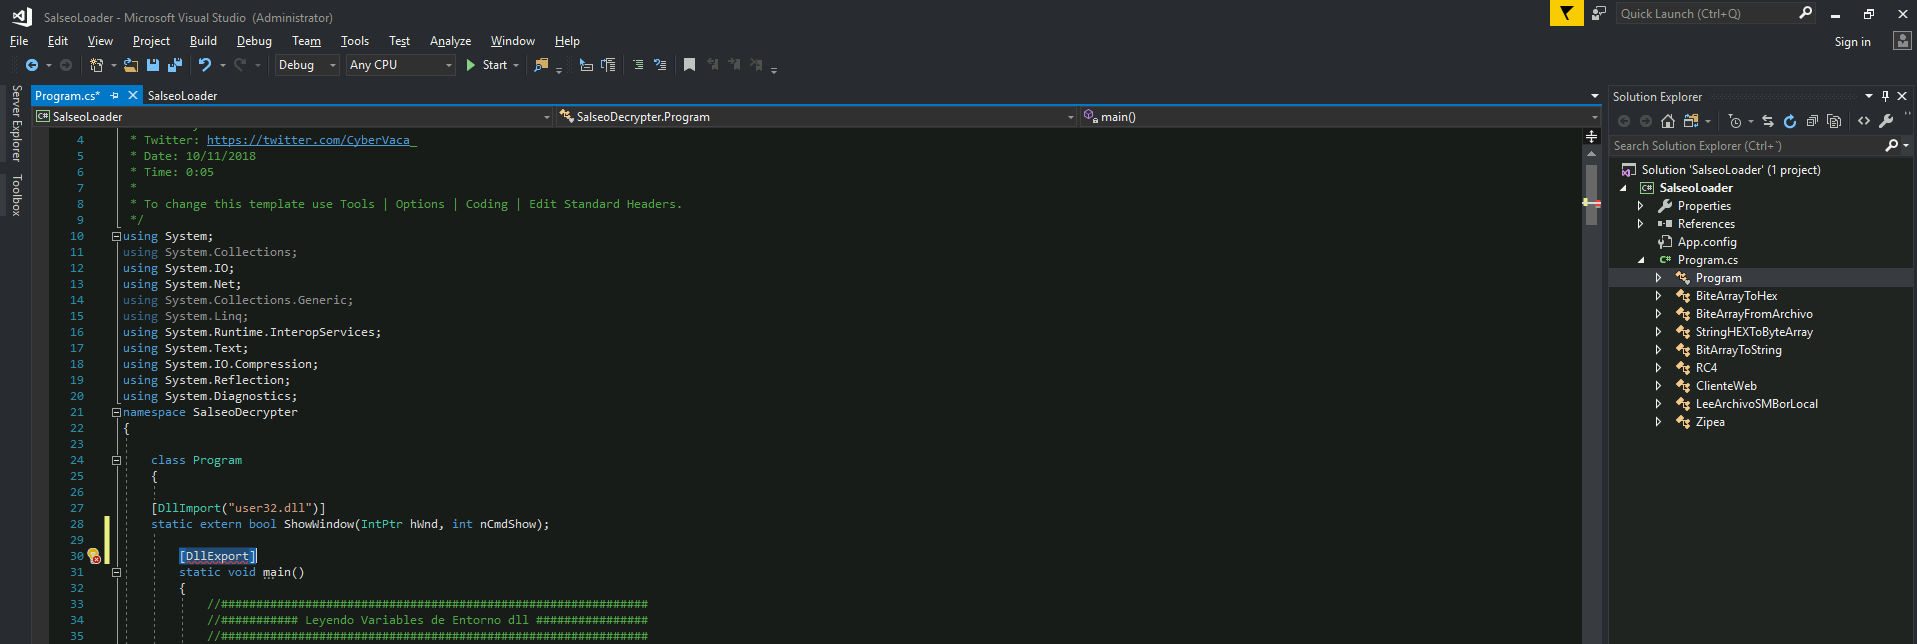 hackplayers/salsa-tools
Salsa Tools - ShellReverse TCP/UDP/ICMP/DNS/SSL/BINDTCP/Shellcode/SILENTTRINITY and AV bypass, AMSI patched
 arcanum-sec/wraith
Browser-hooking framework for authorized red teams and educators. Hooks browsers via XSS, provides interactive post-exploitation control, blind-XSS…
 s4dp4nd4/frida-c2-mcp
Agentic C2-style MCP server for Frida instrumentation on rooted Android and jailbroken iOS.
 koadt/poc-cve-2026-32255
This repository contains a proof of concept (POC) for CVE-2026-32255, a high-severity Server-Side Request Forgery (SSRF) vulnerability in Kan, an…
 10cks/cve-2014-6287
Rejetto http File Server 2.3.x (Reverse shell)
 aydinnyunus/keylogger
Get Keyboard,Mouse,ScreenShot,Microphone Inputs from Target Computer and Send to your Mail.
 zhuowei/macdirtycowdemo
Get root on macOS 13.0.1 with CVE-2022-46689 (macOS equivalent of the Dirty Cow bug), using the testcase extracted from Apple's XNU source.
 ricardojoserf/whoamialternatives
Different methods to get current username without using whoami
 wh04m1001/diagtrackeop
Windows privilege-escalation exploit abusing SeImpersonate via DiagTrack RPC, using Secondary Logon to get an INTERACTIVE token and gain SYSTEM.
 peewpw/prettytrusts
A browser based visualization of domain trusts. Give it a csv, get a pretty diagram to play with!
 ahmed-fa7im/cve-2023-38831-winrar-expoit-simple-poc
CVE-2023-38831 winrar exploit generator and get reverse shell
 electronicbots/cve-2021-31761
Exploiting a Reflected Cross-Site Scripting (XSS) attack to get a Remote Command Execution (RCE) through the Webmin's running process feature
 randomrobbiebf/kong-pwn
Use Exposed KongAPI to act like a proxy and get metadata urls or internal urls
 mesh3l911/cve-2021-31760
Exploiting a Cross-site request forgery (CSRF) attack to get a Remote Command Execution (RCE) through the Webmin's running process feature
 electronicbots/cve-2021-31760
Exploiting a Cross-site request forgery (CSRF) attack to get a Remote Command Execution (RCE) through the Webmin's running process feature
 freakazoidile/ms15-011-files
Repo that the MS15-011 exploit clones to get required files. Avoids having to download all files from exploit_dev.