
evilwaf
 matrixleons/evilwaf
evilwaf is a penetration testing tool designed to detect and bypass common Web Application Firewalls (WAFs).
fingerprint-spoofinginformation-gatheringosint+6
898
matrixleons/evilwafevilwaf is a penetration testing tool designed to detect and bypass common Web Application Firewalls (WAFs).
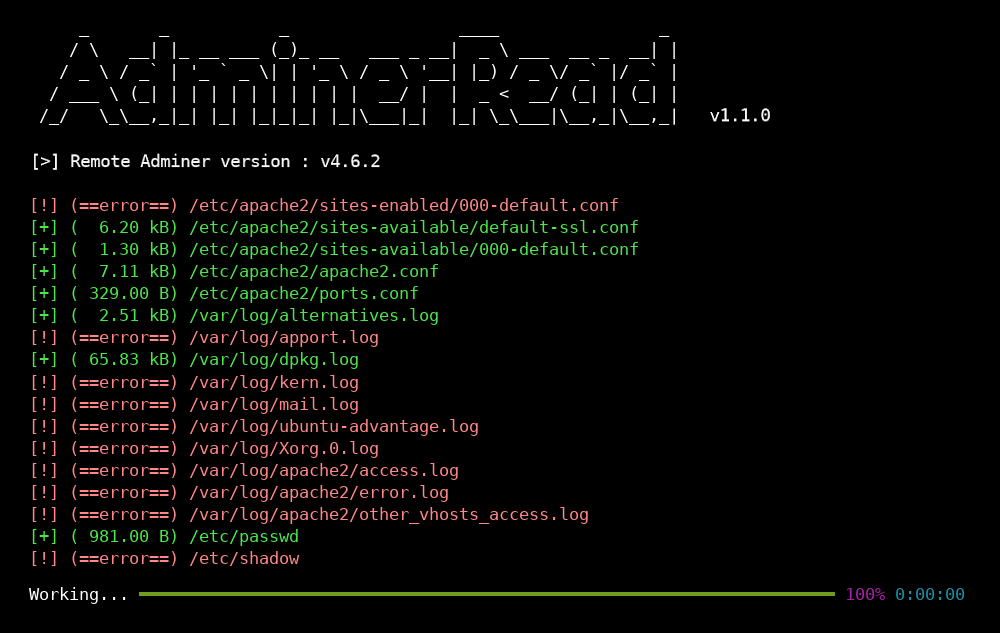 p0dalirius/cve-2021-43008-adminerread
Exploit tool for CVE-2021-43008 Adminer 1.0 up to 4.6.2 Arbitrary File Read vulnerability
 toxy4ny/artaxerxes
Advanced Multi-Technology Stress Testing Framework Educational Cybersecurity Tool for High-Performance Network Testing
 zan8in/afrog
A Security Tool for Bug Bounty, Pentest and Red Teaming.
 ghostpack/certify
C# tool for enumerating and exploiting misconfigurations in Active Directory Certificate Services (AD CS), enabling certificate template abuse,…
 ly4k/certipy
Tool for Active Directory Certificate Services enumeration and abuse
 i-am-shodan/usbarmyknife
USB Army Knife – the ultimate close access tool for penetration testers and red teamers.
 mr-un1k0d3r/edrs
Red team tool for EDR evasion: dynamically resolves syscall IDs, patches ntdll stubs, unhooks IAT hooks, and lists hooked APIs from major EDR vendors.
 ph4ntonn/stowaway
Multi-hop proxy tool for pentesters enabling traffic routing through multiple nodes, SOCKS5/SSH tunneling, port forwarding, remote shell, and…
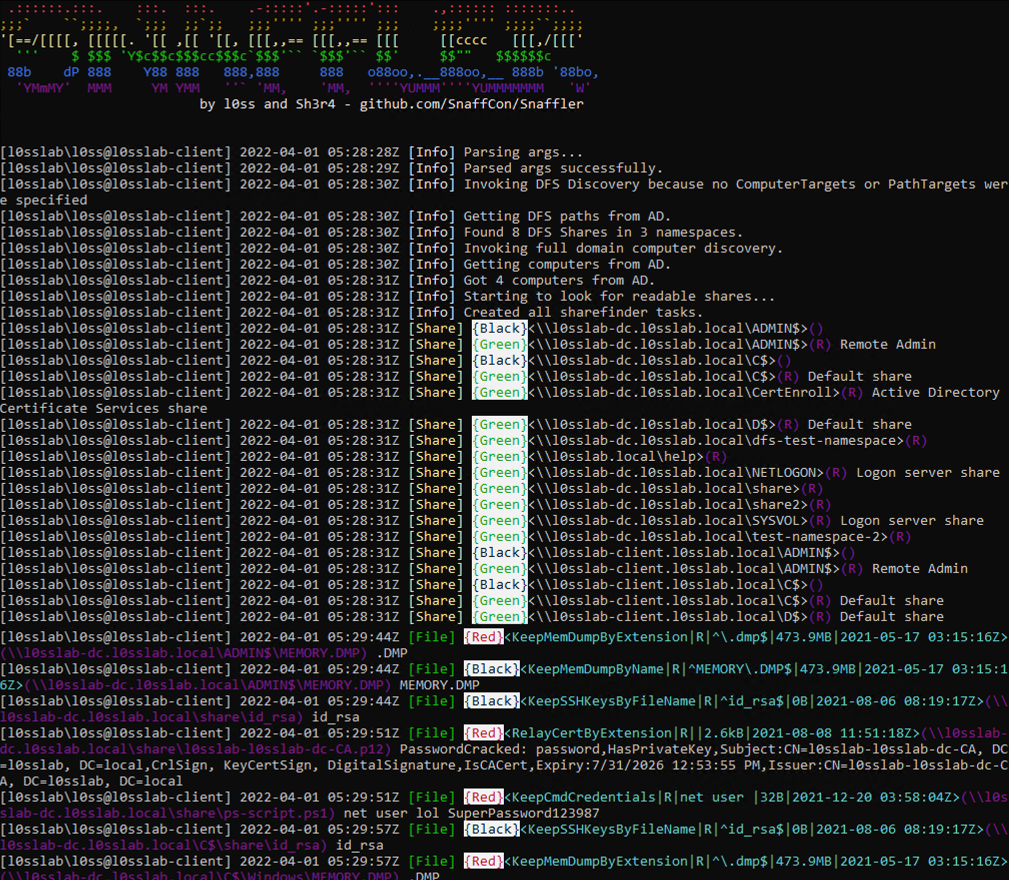 snaffcon/snaffler
a tool for pentesters to help find delicious candy, by @l0ss and @Sh3r4 ( Twitter: @/mikeloss and @/sh3r4_hax )
 nccgroup/demiguise
HTA encryption tool for RedTeams
 nccgroup/redsnarf
RedSnarf is a pen-testing / red-teaming tool for Windows environments
 parrotsec/mimikatz
Tool for extracting Windows credentials (passwords, hashes, Kerberos tickets) from memory and performing pass-the-hash, pass-the-ticket, and golden…
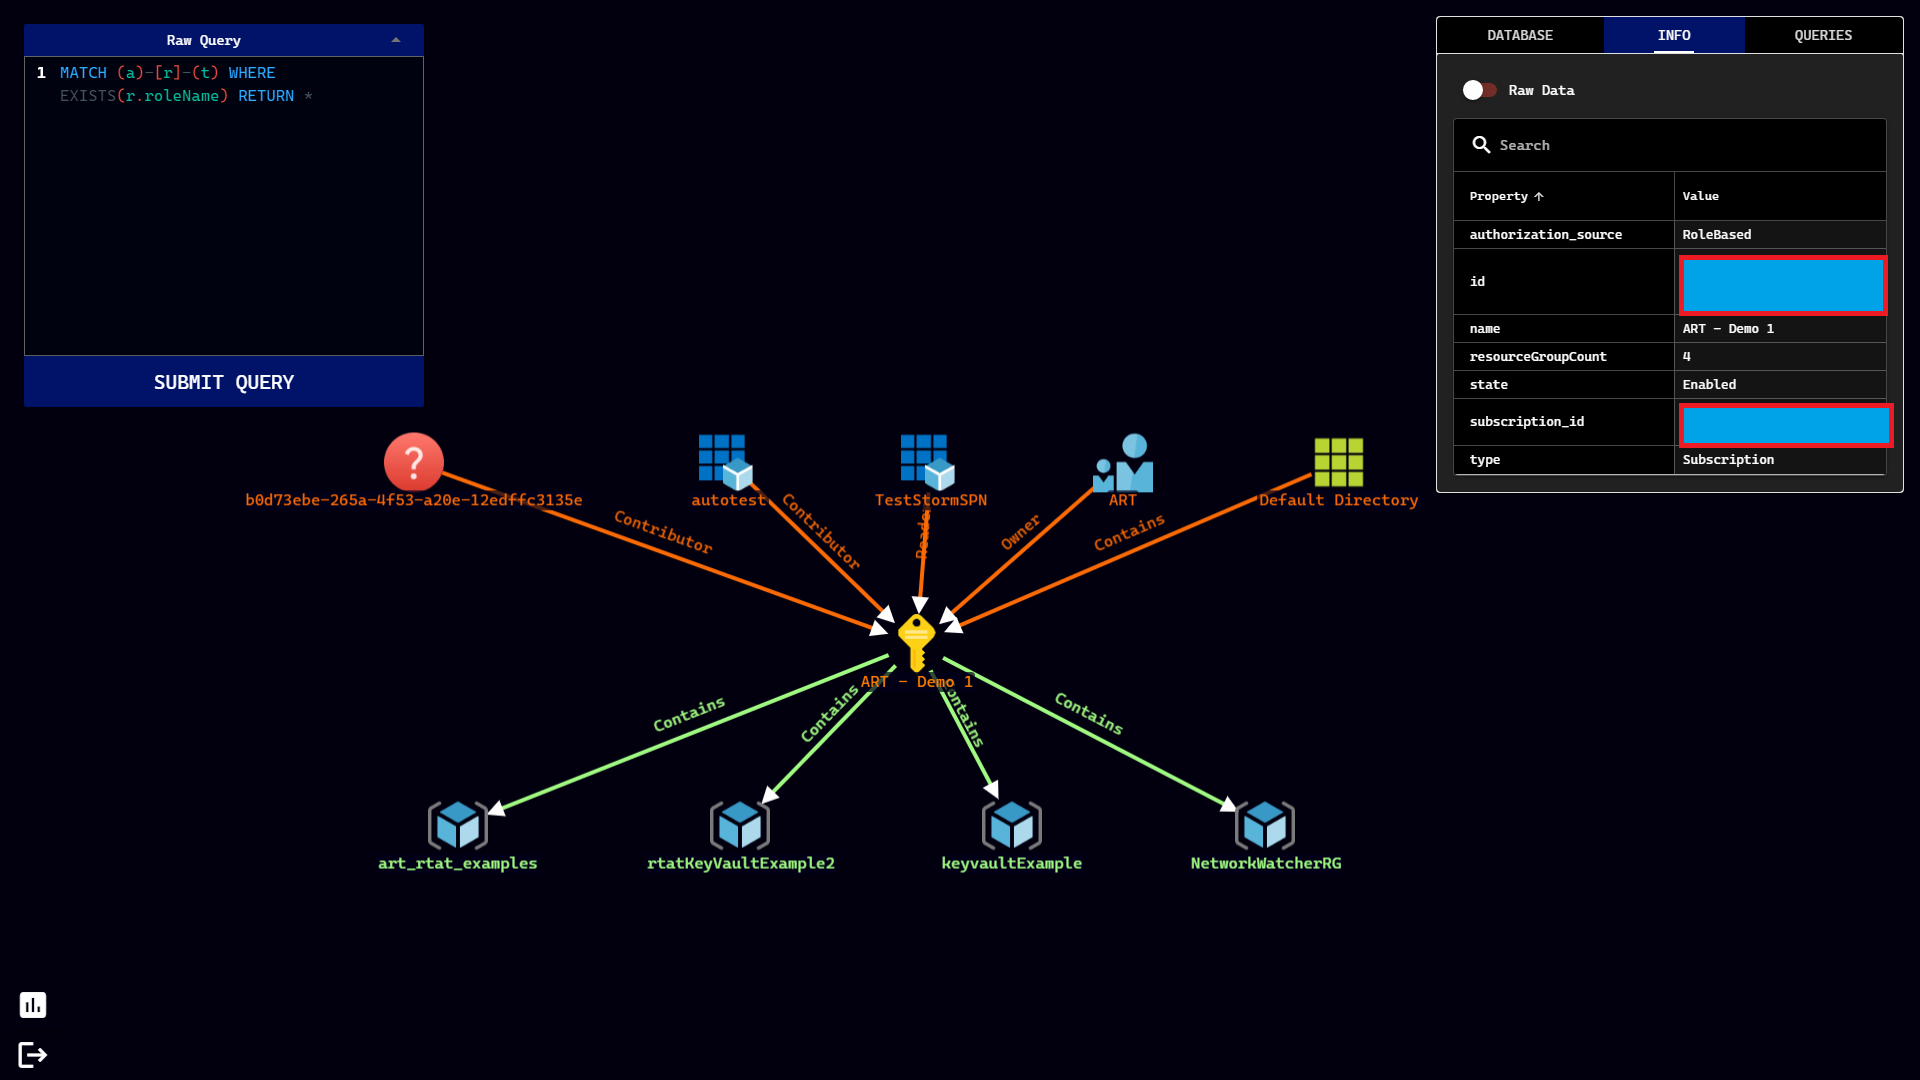 azure/stormspotter
Azure Red Team tool for graphing Azure and Azure Active Directory objects
 m00nrise/processhider
Post-exploitation tool for hiding processes from monitoring applications
 aircrack-ng/mdk4
IEEE 802.11 Wi-Fi testing tool for protocol weakness exploitation, including beacon flooding, deauthentication, packet fuzzing, and IDS evasion.…
 samratashok/kautilya
Kautilya - Tool for easy use of Human Interface Devices for offensive security and penetration testing.
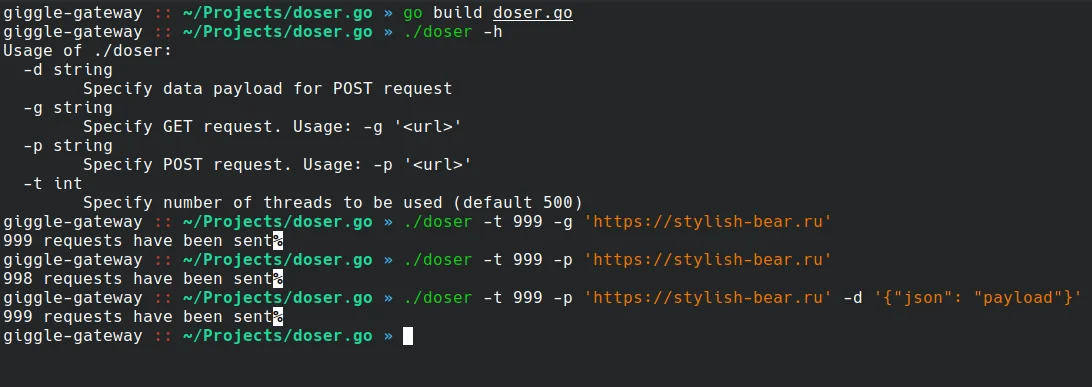 quitten/doser.go
DoS tool for HTTP requests (inspired by hulk but has more functionalities)