
CVE-2025-57819-exploit
 jeanback1/cve-2025-57819-exploit
FreePBX Pre-Auth SQLi to RCE (CVE-2025-57819) — All-in-One Exploit
educationexploitationpayload-generation+4
2
jeanback1/cve-2025-57819-exploitFreePBX Pre-Auth SQLi to RCE (CVE-2025-57819) — All-in-One Exploit
 rippsec/cve-2026-31431-copy-fail
Comprehensive analysis of CVE-2026-31431, a Linux kernel LPE, including exploit methodology, detection scripts, YARA rules, auditd and Falco…
 estebanzarate/cve-2025-4517-python-tarfile-filter-data-bypass-poc
Proof-of-concept exploit for CVE-2025-4517, a path traversal vulnerability in Python's tarfile filter='data' sandbox, enabling arbitrary file writes…
 mafifrizi/ares
Autonomous red-team engagement platform with MITRE ATT&CK module orchestration, DAG attack-path solving, OPSEC controls, encrypted credential vault,…
 javelinnetworks/honeypotbuster
PowerShell module for red teams to detect honeypots, honeytokens, and deception techniques in Active Directory environments, including fake accounts,…
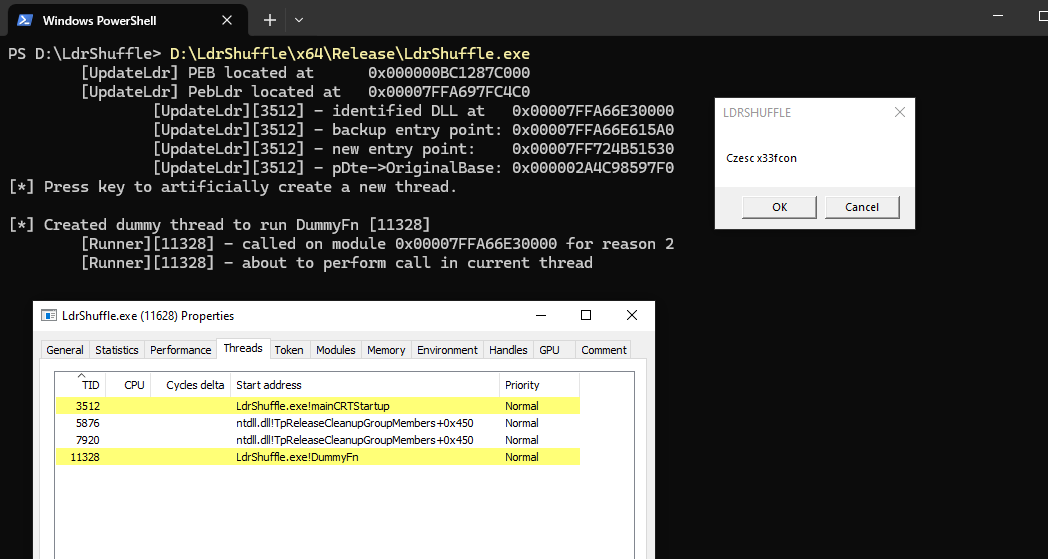 rwxstoned/ldrshuffle
Code execution/injection technique using DLL PEB module structure manipulation
 mgeeky/azurert
AzureRT - A Powershell module implementing various Azure Red Team tactics
 wietze/invoke-argfuscator
Invoke-ArgFuscator is an open-source, cross-platform PowerShell module that helps generate obfuscated command-lines for common system-native…
 idov31/silverseal
Linux post-exploitation framework with a UEFI bootkit that persistently and stealthily loads a Rust-based kernel module rootkit on modern Linux…
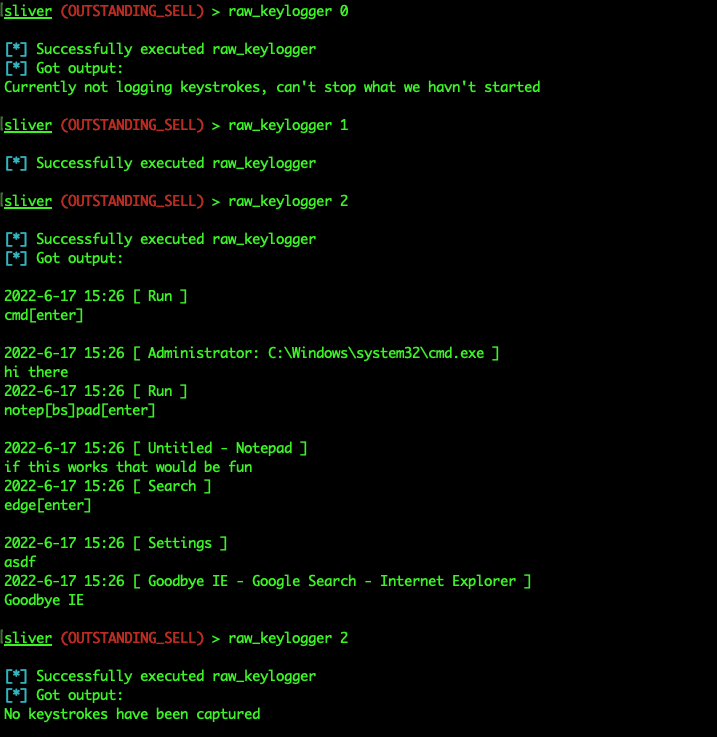 trustedsec/sliverkeylogger
Windows keylogging module for the Sliver C2 implant framework, using Raw Input to capture keystrokes and expose start, stop, and retrieval commands…
 withsecurelabs/modulestomping
Research and proof-of-concept for module stomping, a technique to hide malicious code in legitimate Windows modules, with documentation and…
 blacksnufkin/maverick
Adaptix C2 agent using Crystal Palace PIC linker and PICO module system
 hyd3sec/azur3alph4
PowerShell module for post-breach Azure red teaming, automating token extraction, resource enumeration, and lateral movement within managed identity…
 zerodayevil/cve-2026-54121-certighost
Proof-of-concept module for CVE-2026-54121 (Certighost), exploiting AD CS enrollment validation via rogue LDAP/SMB listeners to impersonate a Domain…
 kuwaitist/astral_projection
Cobalt Strike UDRL that performs advanced module stomping using VEH to intercept calls, unmap modules during sleep, and remap fresh modules to evade…
 theshinigami/mafrida
A Magisk module that simplifies running the Frida server on Android, with easy management commands to download specific versions, enable or disable…
 strozfriedberg/badsamba
This module is used to exploit startup script execution through Windows Group Policy settings when configured to run off of a remote SMB share.
 ymsniper/umbra
External read-only game overlay for Linux. Derived offsets, composed skeletons, optional kernel module for ptrace-independent memory reads and…