
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
19 results
CVE-2022-22077 preview

CVE-2022-22077

GitHubgrisuno/cve-2022-22077

BYOVD exploitation framework for CVE-2022-22077 targeting RTCore64.sys. Demonstrates kernel token theft, privilege escalation to SYSTEM, and C2…
binary-exploitationcommand-and-controleducation+5
7
15 days ago
LocalStranger preview

LocalStranger

GitHubnbs32k/localstranger

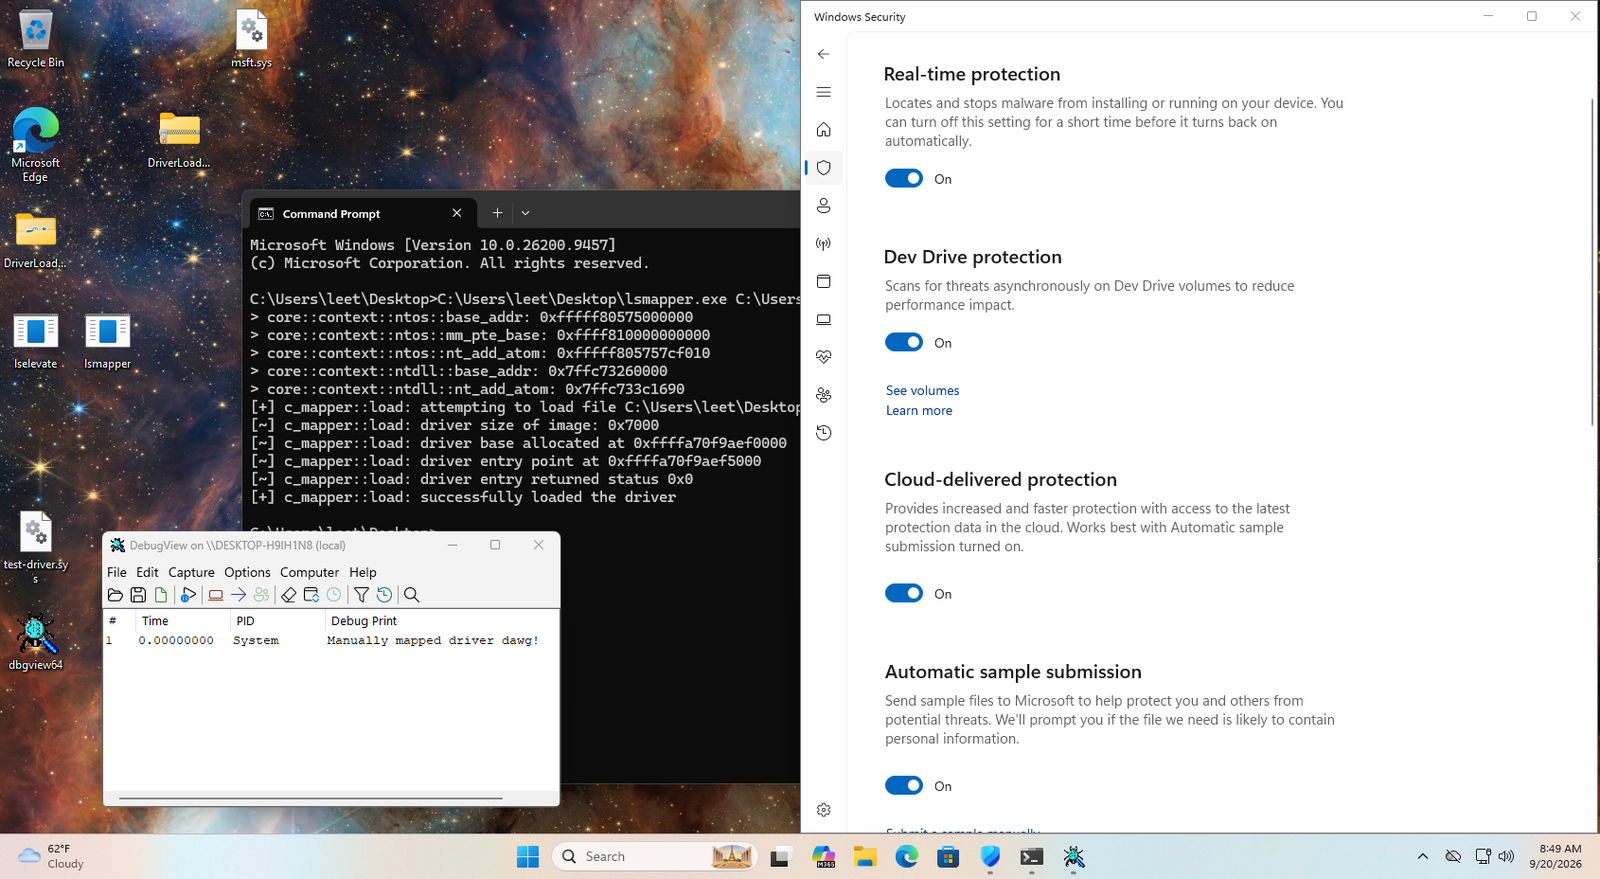
PoC for WinNotify, demonstrated through a driver mapper, and local privilege escalation.
binary-exploitationexploit-frameworkspayload-development+3
411 month ago
Tokenizer preview
Archived

Tokenizer

GitHubzeromemoryex/tokenizer

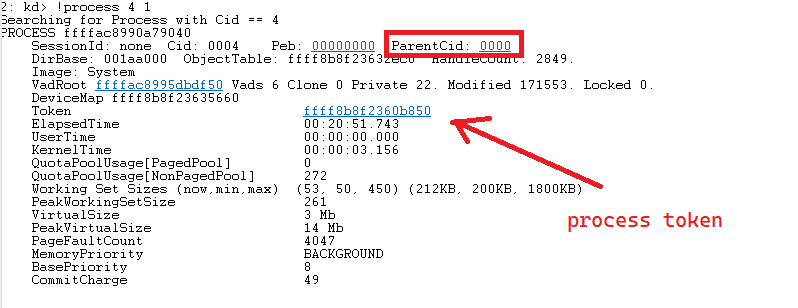
Simple Kernel Mode Driver for Swapping Process Token
exploitationpost-exploitationprivilege-escalation+1
1301 month ago
Nidhogg preview

Nidhogg

GitHubidov31/nidhogg

Windows rootkit for Intel x64 with 25+ features, demonstrating rootkit techniques compatible with all Windows 10 and Windows 11 versions.
command-and-controlpayload-developmentprivilege-escalation+1
2.5k4 months ago
POSTDump preview

POSTDump

GitHubyolop0wn/postdump

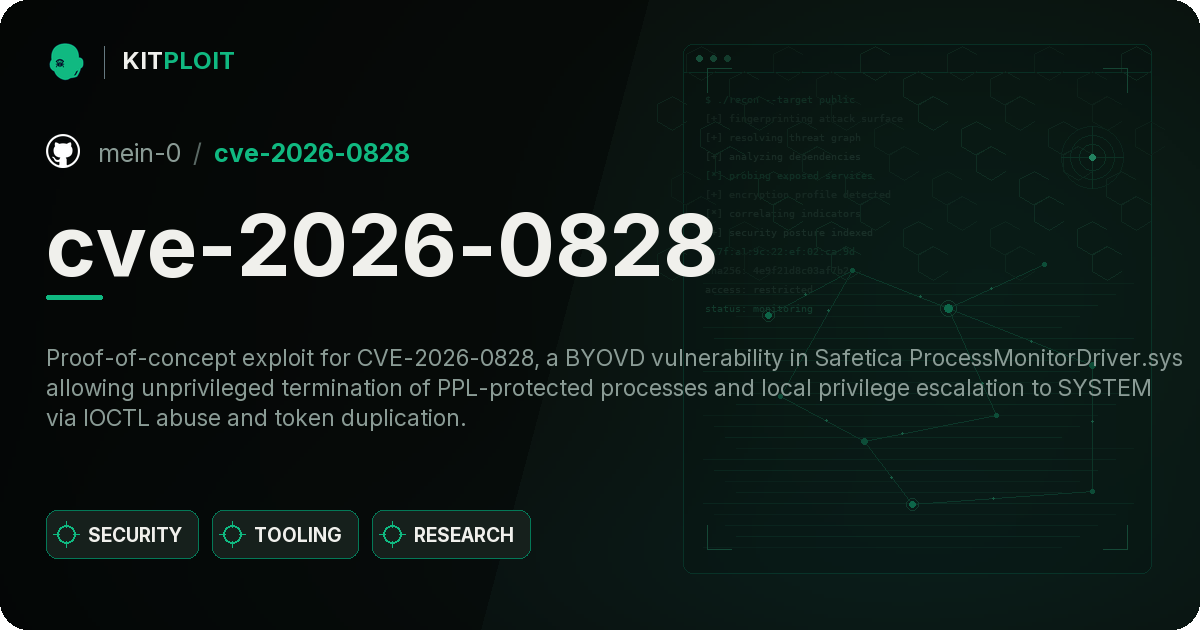
C# tool for LSASS minidump with multiple evasion techniques including indirect syscalls, ETW patching, and PPL bypass via driver or WER fault.…
post-exploitationprivilege-escalationred-teaming
3474 months ago
cve-2026-0828 preview

cve-2026-0828

GitHubmein-0/cve-2026-0828

Proof-of-concept exploit for CVE-2026-0828, a BYOVD vulnerability in Safetica ProcessMonitorDriver.sys allowing unprivileged termination of…
binary-exploitationexploitationids-ips-evasion+6
14 months ago
KillChain preview

KillChain

GitHuboxfemale/killchain

Kernel Process Termination Tool ( CVE-2026-0828 exploit)
binary-exploitationexploitationmalware-analysis+3
386 months ago
CVE-2024-30804 preview

CVE-2024-30804

GitHubgeozstevenzz/cve-2024-30804

Windows LPE PoC exploiting the AsInsHelp64.sys driver via arbitrary physical memory read/write to overwrite kernel tokens and gain SYSTEM privileges.
binary-exploitationexploitationpayload-development+3
10 months ago
Reaper preview

Reaper

GitHubbrosck/reaper

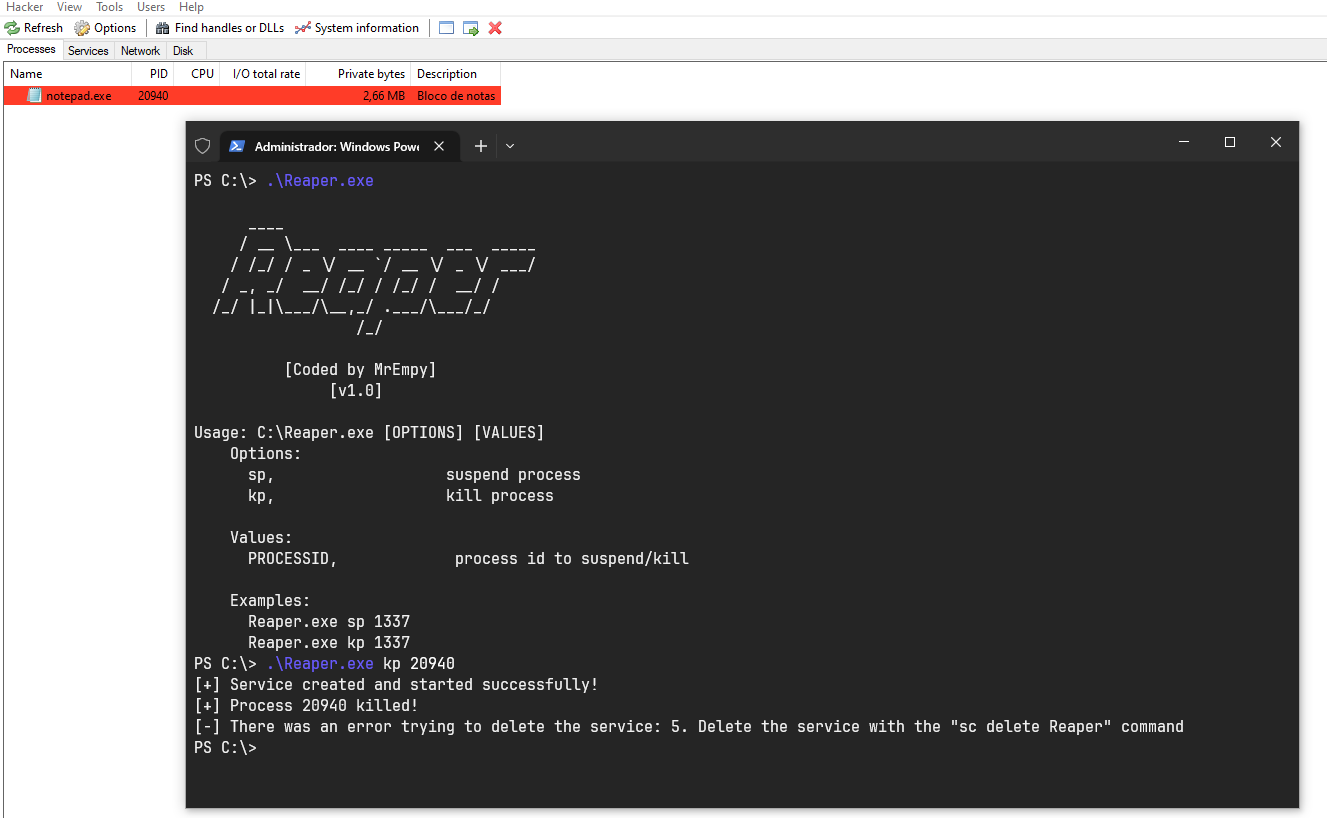
Proof-of-concept BYOVD exploit targeting kprocesshacker.sys driver to kill or suspend processes with kernel-level privileges on Windows systems.
exploitationprivilege-escalationred-teaming
1641 year ago
CVE-2024-26229 preview

CVE-2024-26229

GitHubmqxmm/cve-2024-26229

Proof-of-concept exploit for CVE-2024-26229, a Windows kernel privilege escalation vulnerability targeting specific system components for local…
binary-exploitationexploitationpenetration-testing+3
2 years ago
EDRSandblast preview

EDRSandblast

GitHubwavestone-cdt/edrsandblast

Weaponizes vulnerable signed drivers to bypass EDR kernel callbacks, object callbacks, ETW TI provider, and userland hooks for LSASS memory dumping…
defensive-toolsexploitationpenetration-testing+2
1.9k2 years ago
Kernel-Arbitrary-Read-Vulnerability-Superfetch-EOP preview

Kernel-Arbitrary-Read-Vulnerability-Superfetch-EOP

GitHubspiralbl0ck/kernel-arbitrary-read-vulnerability-superfetch-eop

Kernel Arbitrary Read Vulnerability + Superfetch EOP based on reacher from https://starlabs.sg/blog/2022/06-trying-to-exploit-a-windows-kernel-arbitra…
binary-exploitationexploitationpenetration-testing+3
12 years ago
criPPLe preview

criPPLe

GitHubgmh5225/cripple

Windows kernel driver that removes Process Protection (PP) and Process Protection Light (PPL).
exploitationmalware-analysisprivilege-escalation+1
2 years ago
CVE-2020-17086 preview

CVE-2020-17086

GitHubt81oub/cve-2020-17086

Exploit code for CVE-2020-17086, a Windows kernel privilege escalation vulnerability.
binary-exploitationexploitationpenetration-testing+2
2 years ago
Kernelhub preview

Kernelhub

GitHubascotbe/kernelhub

:palm_tree:Linux、macOS、Windows Kernel privilege escalation vulnerability collection, with compilation environment, demo GIF map, vulnerability…
curated-resourceseducationexploitation+4
3.2k3 years ago
DuplicateDump preview

DuplicateDump

GitHubhagrid29/duplicatedump

Dumping LSASS with a duplicated handle from custom LSA plugin
post-exploitationprivilege-escalationred-teaming
2074 years ago
BypassUAC preview

BypassUAC

GitHubmemoryo3o/bypassuac

Windows UAC bypass tool using whitelist-based technique to elevate privileges silently, compatible with Cobalt Strike payloads for post-exploitation…
exploitationprivilege-escalationred-teaming
1685 years ago
evil-mhyprot-cli preview

evil-mhyprot-cli

GitHubkkent030315/evil-mhyprot-cli

A PoC for Mhyprot2.sys vulnerable driver that allowing read/write memory in kernel/user via unprivileged user process.

binary-exploitationexploitationprivilege-escalation+2
3565 years ago
Previous12Next