

Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
20 results
XXERipper preview

XXERipper

GitHubkamalx06/xxeripper

Black-box XXE scanner detecting in-band, error-based, and blind out-of-band injection via statistical baselining, parser fingerprinting, and OOB…
api-security-testingdata-exfiltrationexploitation+9
10
13 days ago
SrHollow preview

SrHollow

GitHubivancabrera02/srhollow

Extracts LSA secrets and DPAPI keys from Windows registry hives via existing or newly created VSS shadow copies, with an inline regf parser and…

cryptographydata-exfiltrationdefensive-tools+5
5817 days ago
USB Spy preview

USB Spy

GitLabchristophe.duvernois/usb-spy

Intercepts and analyzes USB Mass Storage traffic at the block and file level, emulates USB devices, and supports custom Python stubs for security…
digital-forensicsexploitationfirmware-analysis+6
32 months ago
pyMalleableC2 preview

pyMalleableC2

GitHubbyt3bl33d3r/pymalleablec2

Python interpreter for Cobalt Strike Malleable C2 Profiles. Allows you to parse, build and modify them programmatically.

command-and-controlpayload-developmentred-teaming+1
2904 months ago
CVE-2026-999999 preview

CVE-2026-999999

GitHub24520597-blip/cve-2026-999999

A critical Server-Side Template Injection (SSTI) vulnerability exists in the X-Trading Portal v1.4.2 dashboard metadata rendering engine. The flaw…
educationexploitationpenetration-testing+3
4 months ago
EnvVisualizer preview

EnvVisualizer

GitHubw4r10ck423/envvisualizer

Parse and visualize /proc/self/environ on compromised Linux boxes — categorizes env vars by tech stack (AWS, Django, Rails, NodeJS, MySQL, K8s,…
cloud-securityconfiguration-auditingctf+7
14 months ago
LogHound preview

LogHound

GitHubrnb-team/loghound

Post-Exploitation EVTX Analyzer for BloodHound Mapping
authenticationdigital-forensicsforensics+6
125 months ago
SilentNimvest preview

SilentNimvest

GitHubfrkngksl/silentnimvest

Nim implementation for sud0Ru's Credential Dumping from SAM/SECURITY Hives Method (a.k.a. SilentHarvest)
data-exfiltrationlateral-movementpassword-cracking+3
1076 months ago
zig-pe preview

zig-pe

GitHubthoxy67/zig-pe

Reflective PE loader written in Zig. Loads and executes native and .NET PE files directly from memory.
binary-exploitationexploitationpayload-development+3
657 months ago
Roundcube-CVE-2025-49113 preview

Roundcube-CVE-2025-49113

GitHubbiitts/roundcube-cve-2025-49113

Proof-of-concept to CVE-2025-49113

exploitationpayload-developmentpenetration-testing+3
61 year ago
WhoamiAlternatives preview

WhoamiAlternatives

GitHubricardojoserf/whoamialternatives

Different methods to get current username without using whoami
information-gatheringmalware-analysispost-exploitation+2
1862 years ago
CVE-2024-23897 preview

CVE-2024-23897

GitHubr0xdb/cve-2024-23897

Jenkins 2.441 and earlier, LTS 2.426.2 and earlier does not disable a feature of its CLI command parser that replaces an '@' character followed by a…
exploitationinformation-gatheringpenetration-testing+3
2 years ago
CVE-2024-23897 preview

CVE-2024-23897

GitHubh4x0r-dz/cve-2024-23897

Python exploit for Jenkins CVE-2024-23897: arbitrary file read via CLI args4j parsing, enabling RCE. Scans hosts and extracts sensitive files from…

exploitationinformation-gatheringpenetration-testing+3
2092 years ago
poc-cve-2024-23897 preview

poc-cve-2024-23897

GitHubvmtyan/poc-cve-2024-23897

Proof-of-concept exploit for CVE-2024-23897 enabling remote code execution on Jenkins instances via vulnerable args4j command-line parser. Written in…
exploitationpenetration-testingred-teaming+3
22 years ago
Cortex-XDR-Config-Extractor preview

Cortex-XDR-Config-Extractor

GitHublaokoon-security/cortex-xdr-config-extractor

Parses Cortex XDR agent database lock files to extract agent settings, uninstall password hash/salt, and security exclusions for red team assessments…
configuration-auditingpassword-crackingpenetration-testing+1
1433 years ago
aggrokatz preview

aggrokatz

GitHubsec-consult/aggrokatz

Aggrokatz is an aggressor plugin extension for Cobalt Strike which enables pypykatz to interface with the beacons remotely and allows it to parse…
exploit-frameworkspayload-developmentpenetration-testing+2
1545 years ago
SniffAir preview

SniffAir

GitHubtylous/sniffair

A framework for wireless pentesting.
exploitationinformation-gatheringpenetration-testing+3
1.2k5 years ago
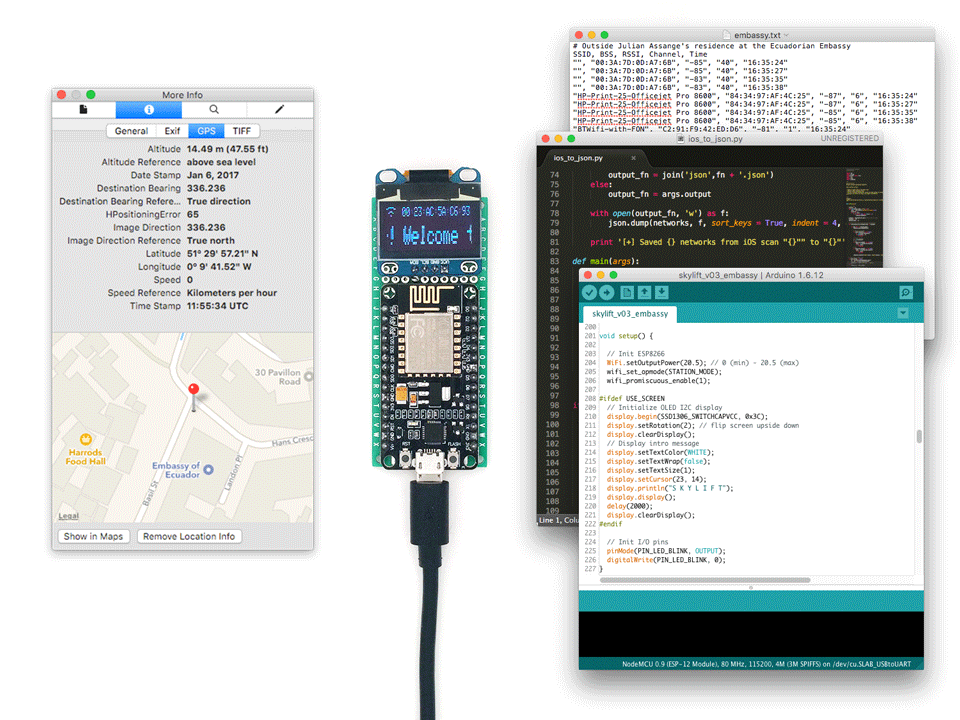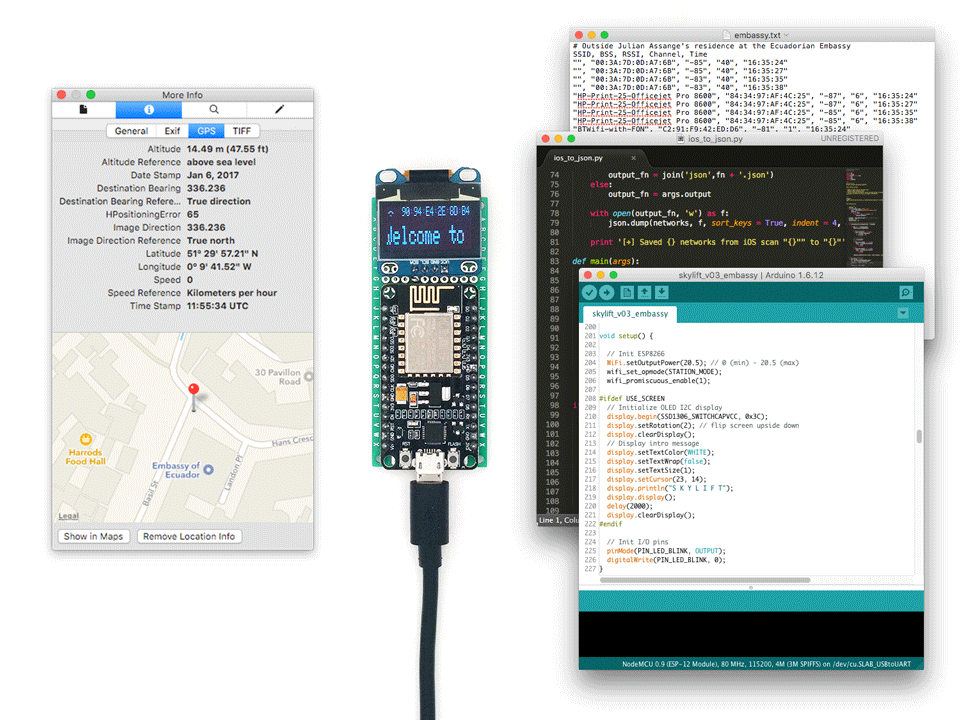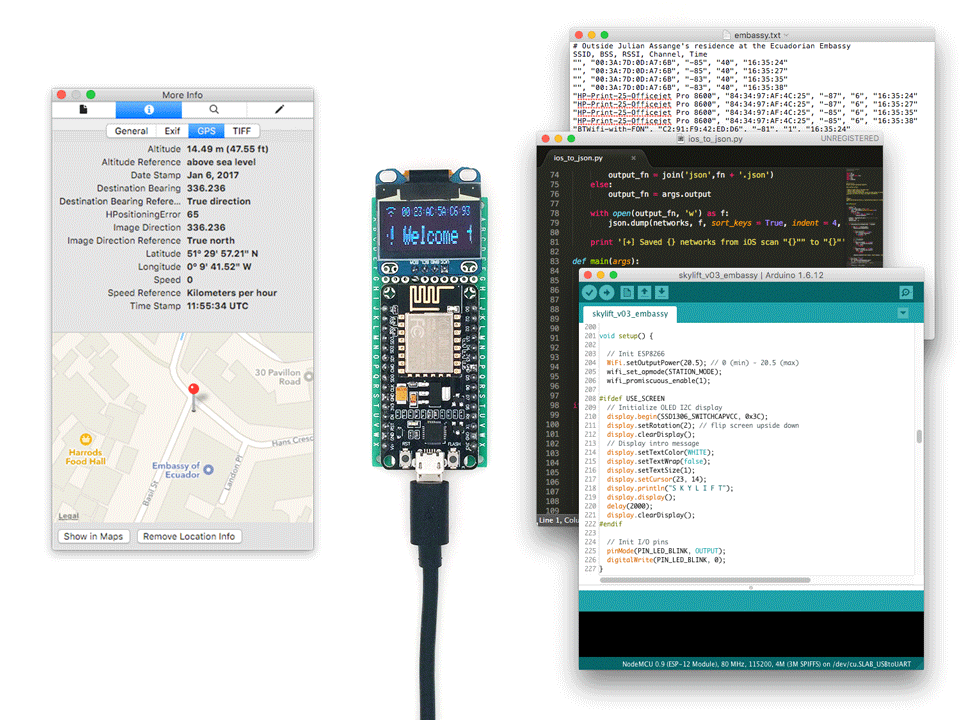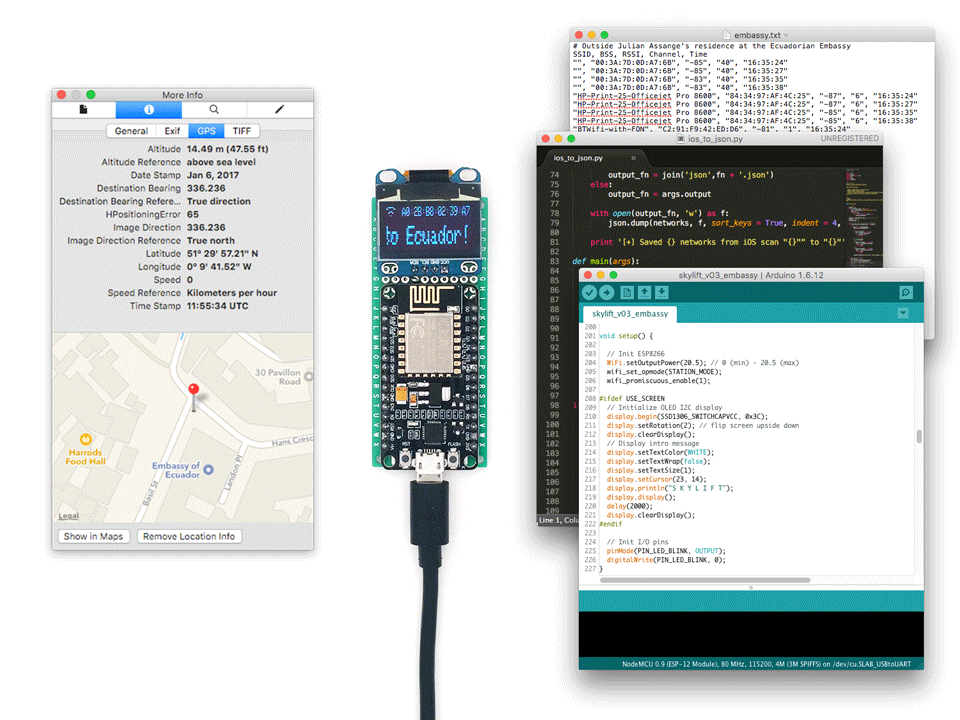
skylift preview

skylift

GitHubawesome-pentest-gadgets/skylift

WiFi Geolocation Spoofing with the ESP8266

embedded-systems-securityexploitationhardware-iot-security+3
838 years ago
Previous12Next