

rules
 ibnaleem/rules
Curated collection of Hashcat password-cracking rules with benchmark data, designed to help red teams and penetration testers crack complex passwords…
curated-resourcespassword-attackspassword-cracking+2
73
ibnaleem/rulesCurated collection of Hashcat password-cracking rules with benchmark data, designed to help red teams and penetration testers crack complex passwords…
 antid00t/cve-2026-15989
Python PoC scanner for CVE-2026-15989, exploiting unauthenticated role injection in WordPress Super Forms to create admin accounts and verify access.
 fl0ydsec/cve-2026-63030
Python mass exploit and detector for the WordPress Core pre-auth RCE chain CVE-2026-63030 and CVE-2026-60137, chaining SQL injection into remote code…
 polosss/by-poloss..-..cve-2026-19125
Verified proof-of-concept exploiting the EthPress <= 2.3.5 unauthenticated authentication bypass, granting a WordPress administrator session via a…
 faceless0x7/cve-2026-93453
Python PoC for CVE-2026-93453, a SOGo password reset link poisoning flaw via attacker-controlled Origin header that enables reset token interception…
 mwr-cybersec/veeamdumper-bof
A credential extraction BOF for Veeam Backup and Replication and Veeam One
 amibhai/credential-attacks-toolkit
Complete credential attack suite for authorized security testing — SSH, FTP, Web Login, Bruteforce, Dictionary attacks
 0xwhoknows/wp2shell
Automated exploit chain for CVE-2026-63030 / CVE-2026-60137 — unauthenticated blind SQLi via WordPress REST batch route-confusion. Dumps user hashes,…
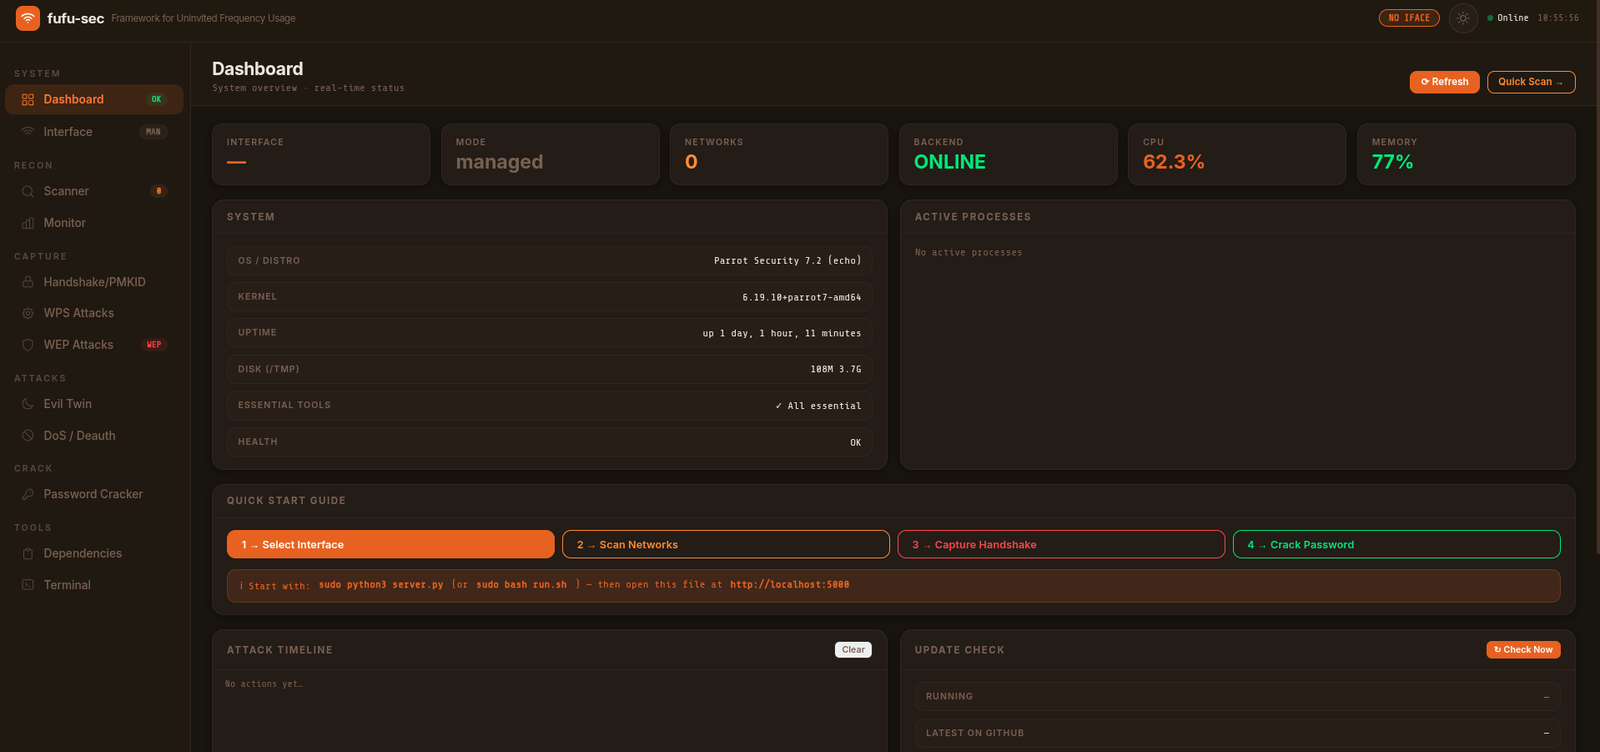 kyllr-qwen/fufu-sec
Framework for Uninvited Frequency Usage
 nxploited/cve-2025-15030
User Profile Builder < 3.15.2 - Unauthenticated Arbitrary Password Reset
 agent-skywalker/cve-2025-60787
Proof-of-concept exploit for CVE-2025-60787, an OS command injection in motionEye v0.43.1b4, enabling remote code execution via crafted…
 tenebrae93/rocketchat-nosqli-chain-cve-2021-22911
Automated exploit for Rocket.Chat NoSQL injection (CVE-2021-22911) that leaks password reset tokens and performs unauthenticated account takeover.
 hyunchiya/cve-2025-14736
Unauthenticated Privilege Escalation to Administrator via Role Form Field
 d3vn0mi/cve-2016-16113-poc
cve-2016-16113
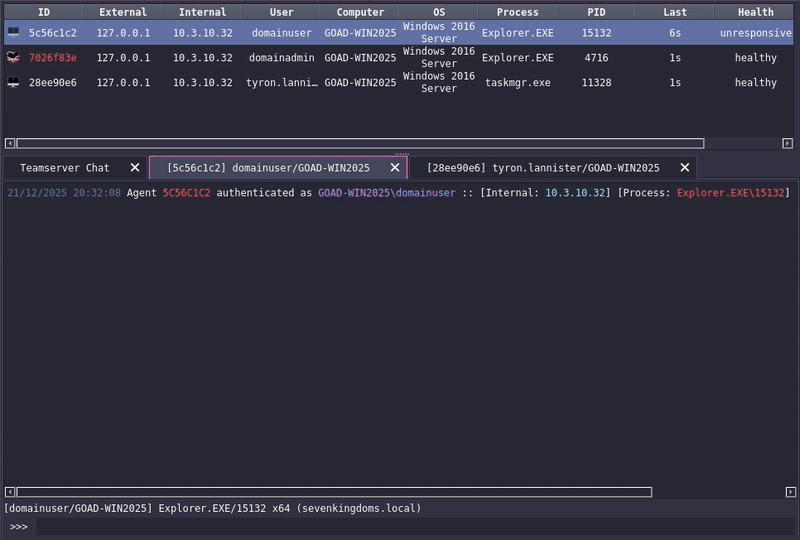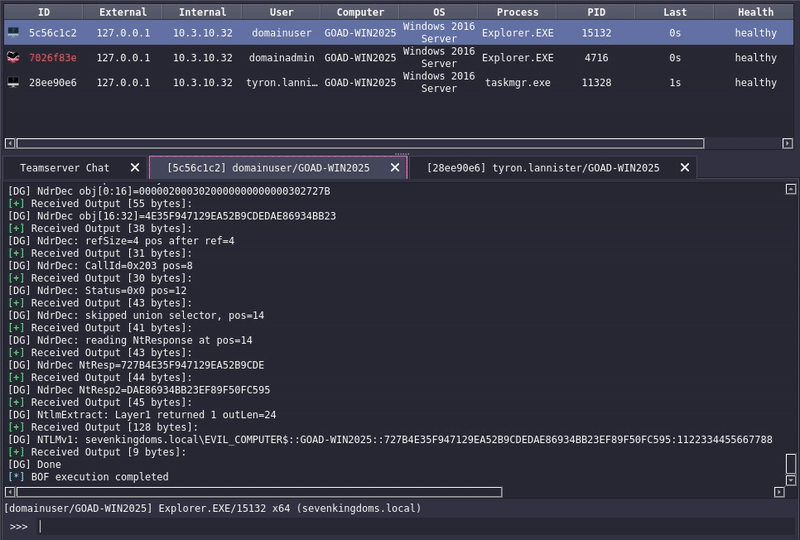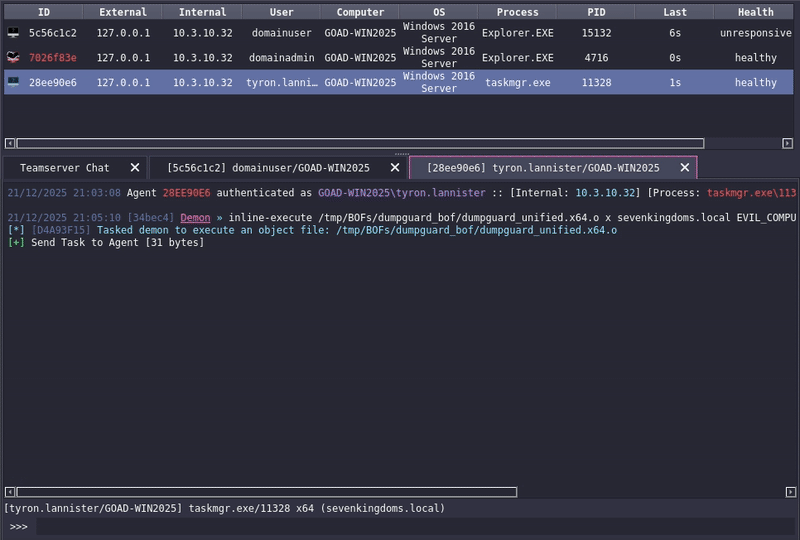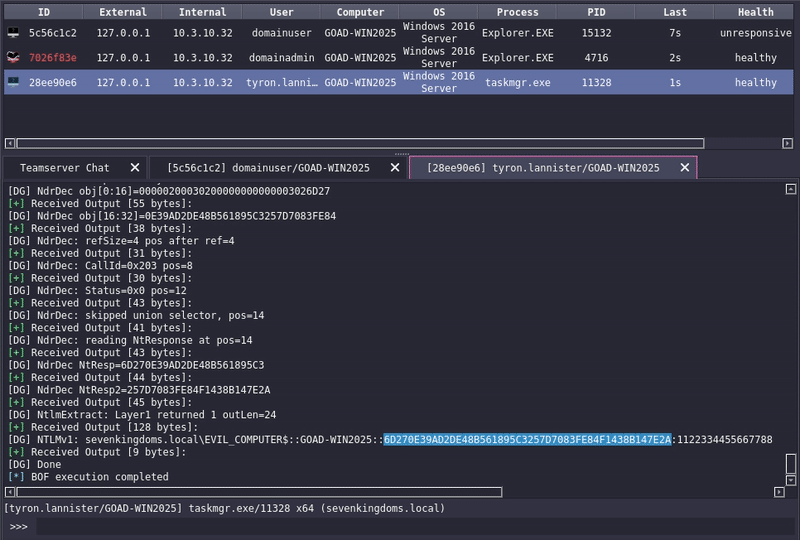 0xedh/dumpguard_bof
Beacon Object File (BOF) port of DumpGuard for extracting NTLMv1 hashes from sessions on modern Windows systems.
 synacktiv/captaincredz
CaptainCredz is a modular and discreet password-spraying tool.
 mdriaz009/cve-2025-21574-exploit
Black-box exploit for CVE-2025-21574 targeting MySQL servers. Automates credential brute-forcing, anonymous access attempts, and triggers server…