CVE-2023-42793-TeamCity-Unauthenticated-RCE

A PoC and automated version detection/exploit tool for JetBrains TeamCity Authentication Bypass & RCE (CVE-2023-42793).

A PoC and automated version detection/exploit tool for JetBrains TeamCity Authentication Bypass & RCE (CVE-2023-42793).

Group Policy Objects manipulation and exploitation framework

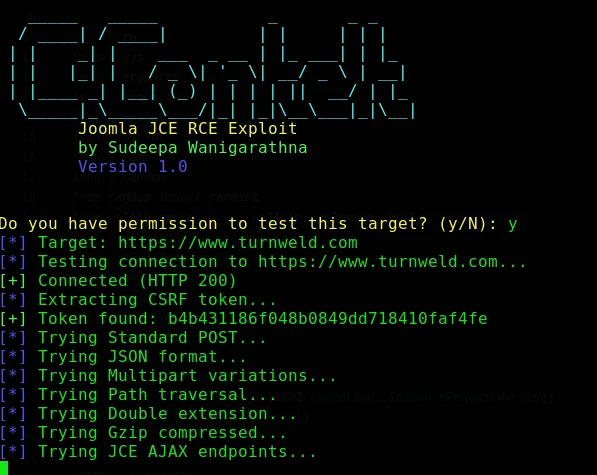
Automated RCE exploit for Joomla JCE (CVE-2026-48907) with interactive shell, batch command execution, file download, and proxy support for…

Curated collection of validated Joomla exploit artifacts with Docker lab environments. Includes RCE, SQLi, XSS, and privilege escalation scripts…

About 2026 Guide: Bypass User Account Control Prompts on Windows 11


TCP Port Forwarding Utility on C

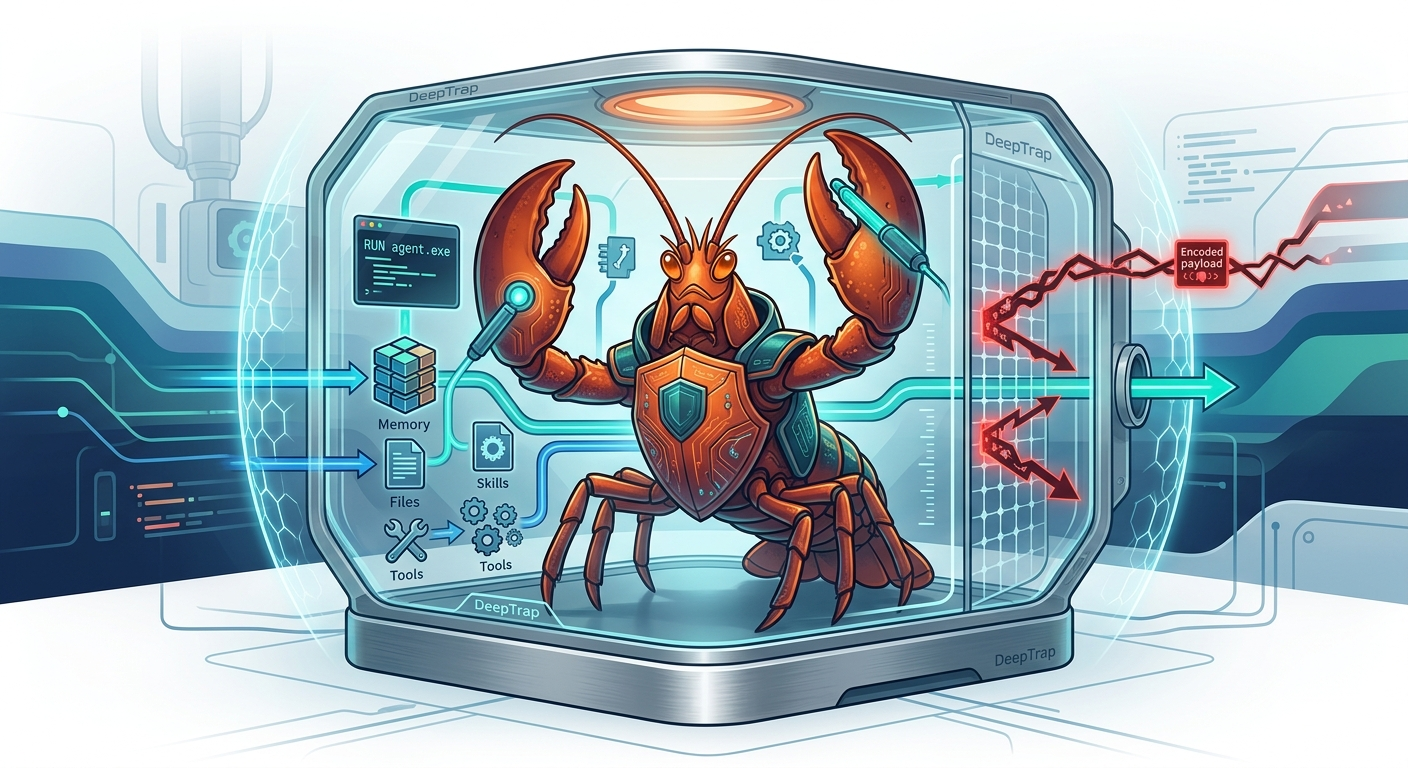
Security benchmark for evaluating OpenClaw agents against adversarial execution contexts including poisoned files, injected skills, misleading tool…

Red Team exploitation of CVE-2021-3156 (Baron Samedit) – Heap Buffer Overflow in Sudo leading to Local Privilege Escalation on Ubuntu 20.04

CVE-2020-5902

needrestart < 3.8 Local Privilege Escalation via PYTHONPATH injection

VeilTransfer is a data exfiltration utility designed to test and enhance the detection capabilities. This tool simulates real-world data exfiltration…

HikvisionExploiter is a Python-based utility designed to automate exploitation and directory accessibility checks on Hikvision network cameras…

A C# utility for interacting with SCOM

PoC for CVE-2024-48990

PowerShell toolkit that extracts locked Windows files (SAM, SYSTEM, NTDS, ...) using MFT parsing and raw disk reads

This is an alternative poc for the CVE-2024-32019 written in python

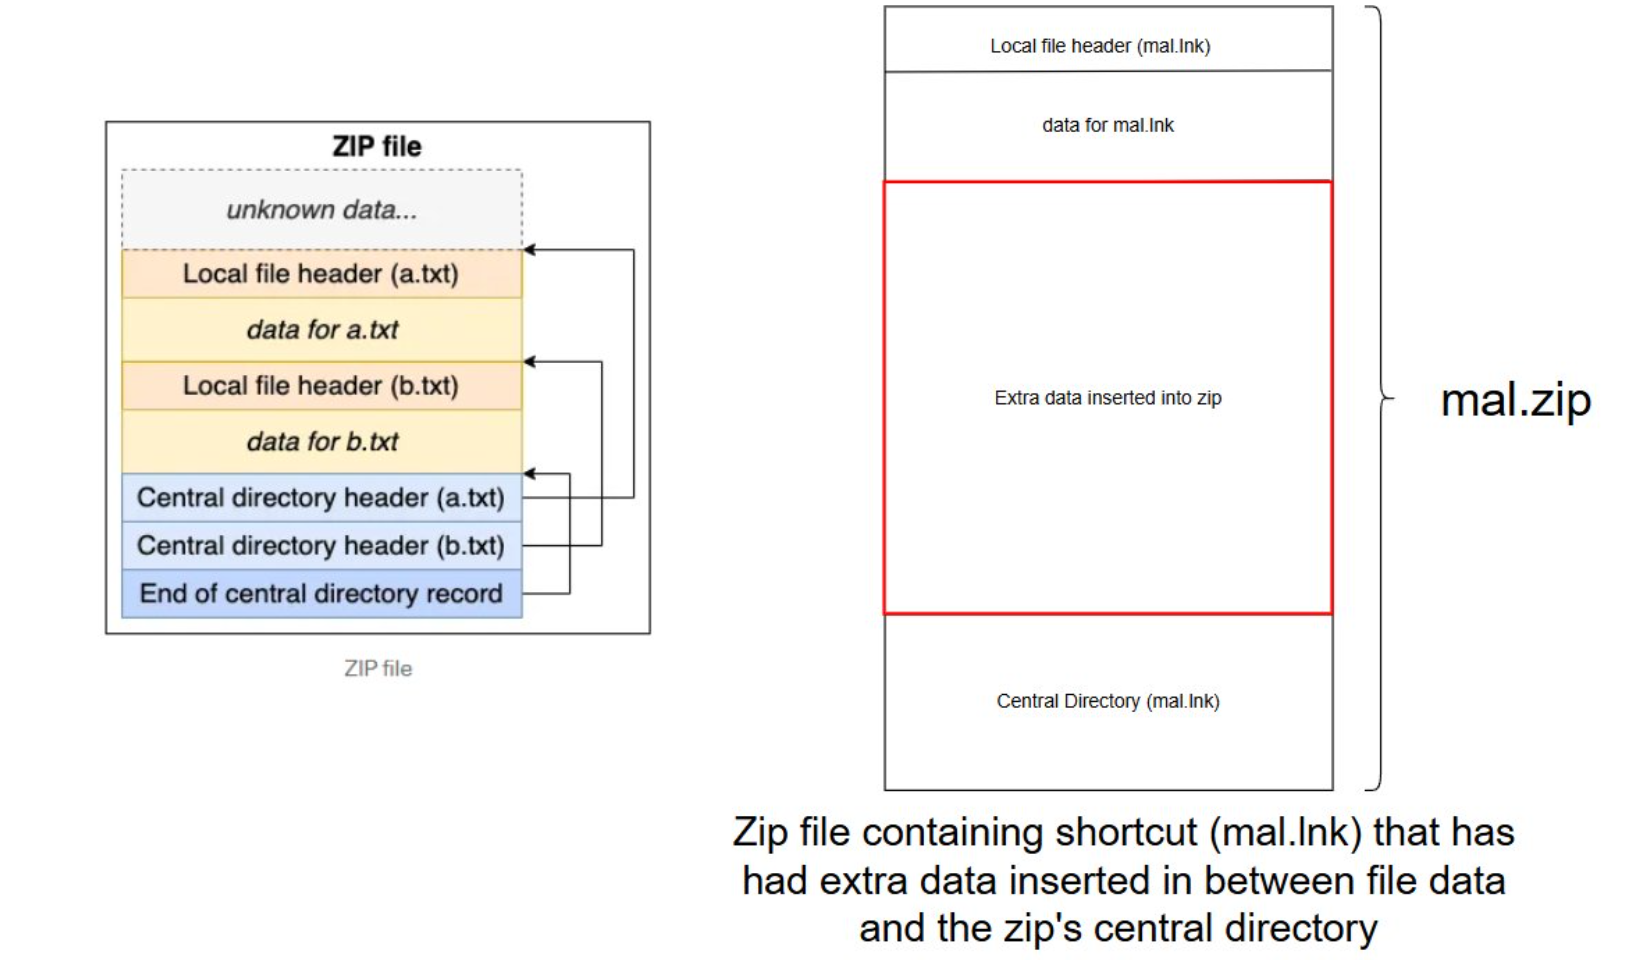
Python3 utility for creating zip files that smuggle additional data for later extraction