
CVE-2026-44402
 0xcyp1337/cve-2026-44402
Exploit for CVE-2026-44402 targeting Voltronic Power SNMP Web Pro 1.1, enabling unauthenticated remote code execution via malicious firmware upload.…
exploitationpenetration-testingred-teaming+3
0xcyp1337/cve-2026-44402Exploit for CVE-2026-44402 targeting Voltronic Power SNMP Web Pro 1.1, enabling unauthenticated remote code execution via malicious firmware upload.…
 poxsky/cve-2026-38577
Proof-of-concept demonstrating hardcoded root credentials (admin/system) in Tenda HG21 XPON modem firmware, enabling unauthorized root access via…
 amiraliuks/ip-camera-research
Security research on a consumer IP camera built on the Fullhan FH8626V100 SoC (model AJL30PG0803).
 darkflippers/unleashed-firmware
Custom firmware for Flipper Zero enabling Sub-GHz radio, NFC/RFID emulation, infrared, and BadUSB attack features for hardware security testing.
 judgedbykira/cve-2026-25938-fuxa-unauthenticated-rce
An explanation and PoC to exploit CVE-2026-25938 Unauthenticated RCE Vulnerability on FUXA
 ghostesp-revival/ghostesp
The open-source wireless research platform for ESP32.
 marginresearch/foisted
MikroTik remote jailbreak for v6.x.x
 jimilinuxguy/lrs-pager-systems-bruteforce
Long Range Pager Systems pagers and coasters URH and YS1 (yardstick one / cc11xx) information and brute force tool
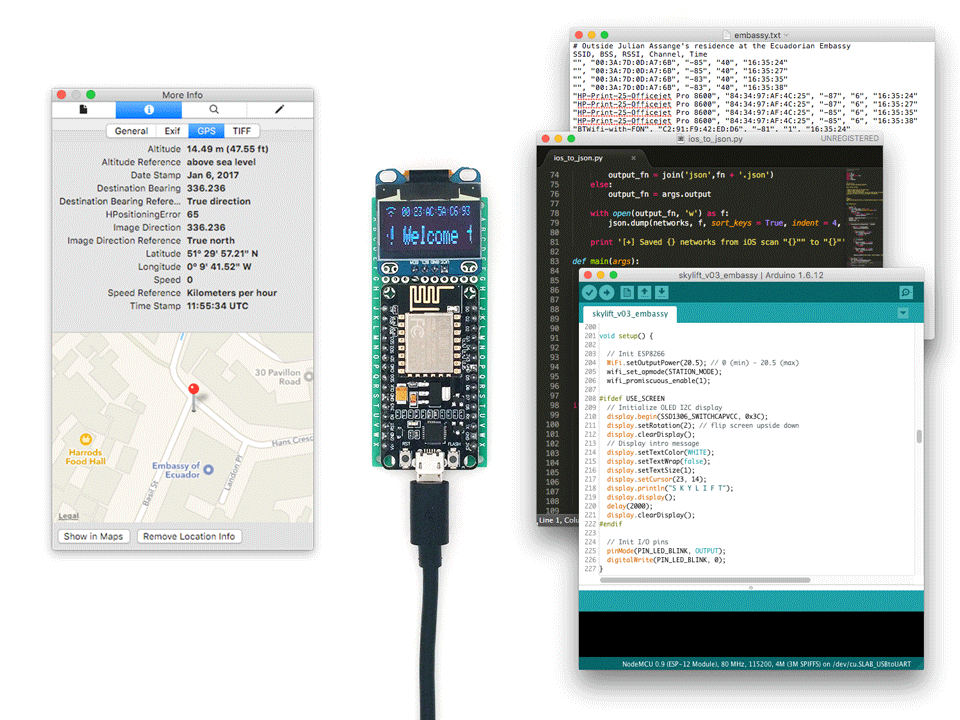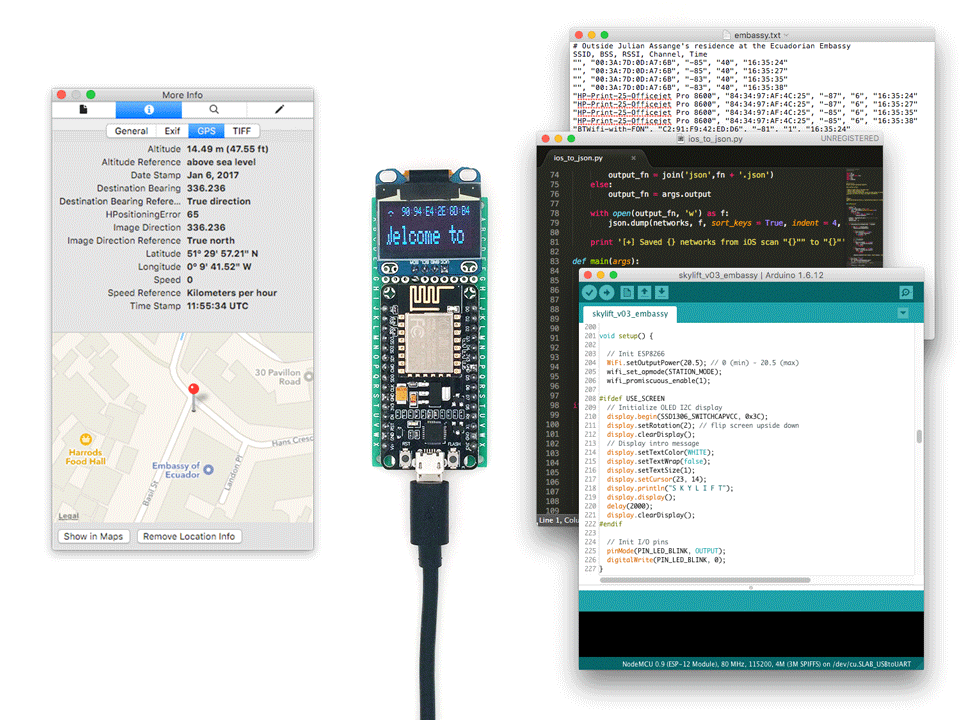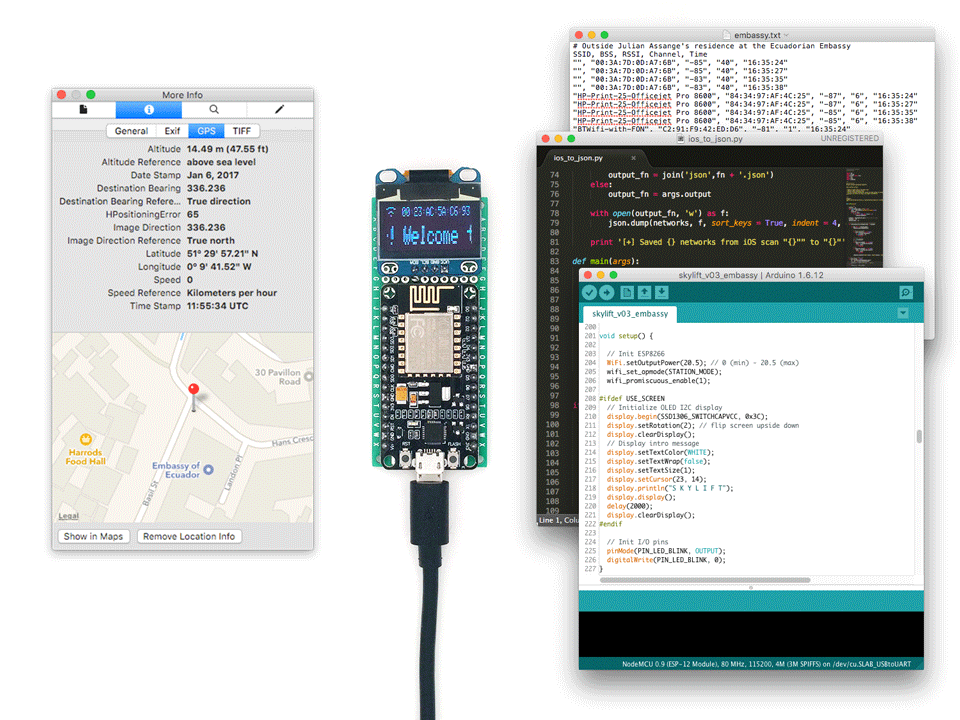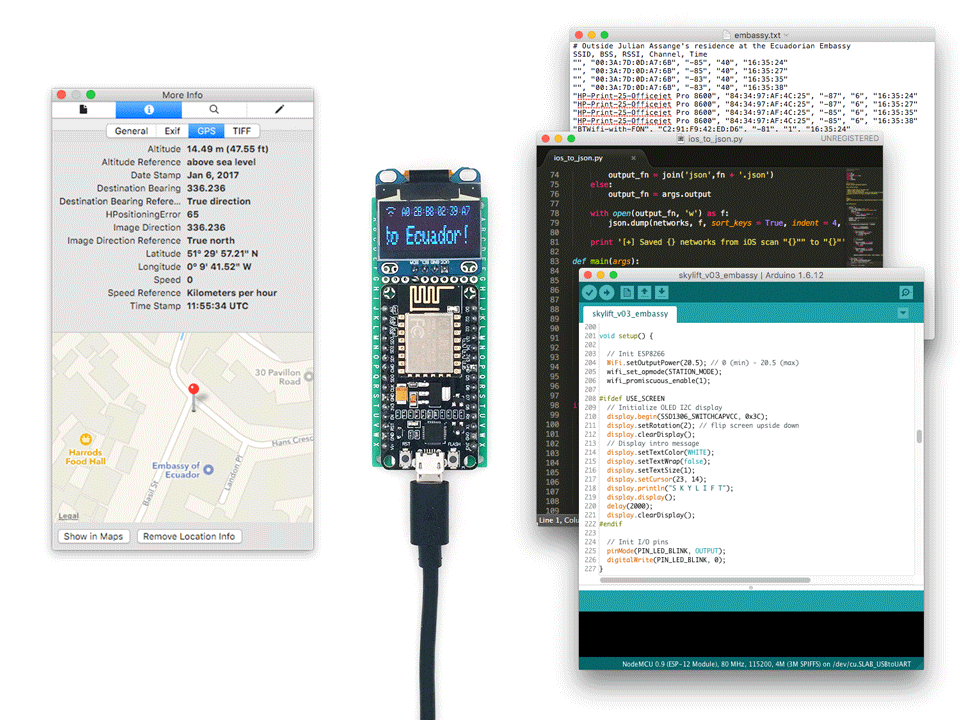 awesome-pentest-gadgets/skylift
WiFi Geolocation Spoofing with the ESP8266
 adamhrv/skylift
Wi-Fi Geolocation Spoofing with ESP8266 / ESP32
 xairy/lights-out
Tools for controlling webcam LED on ThinkPad X230
 lixmk/concierge
Concierge Toolkit: Physical Access Control Identification and Exploitation
 samyk/keysweeper
KeySweeper is a stealthy Arduino-based device, camouflaged as a functioning USB wall charger, that wirelessly and passively sniffs, decrypts, logs…
 elvanderb/tcp-32764
some codes and notes about the backdoor listening on TCP-32764 in linksys WAG200G.
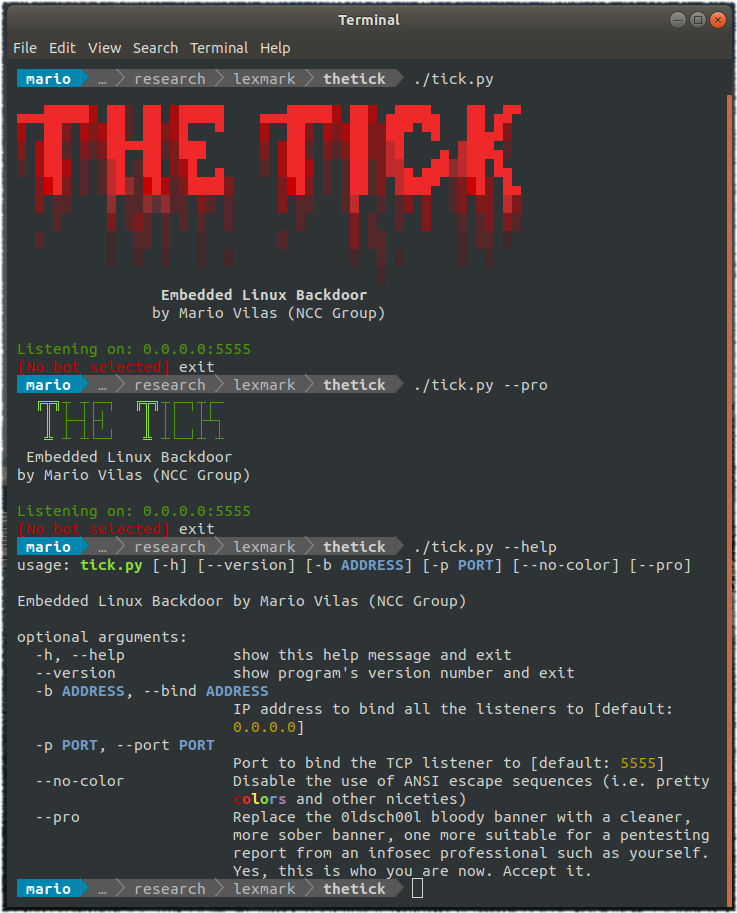 nccgroup/thetick
A simple embedded Linux backdoor.
 spiralbl0ck/bios-stuff-related-programming
Final OBJECTIVE:BIOS ROOTKIT AND RSHELL USING BIOS NETWORKING STACK
 spiralbl0ck/sigint_through_brother_printers
Exploit vulnerable Brother printers via CVE-2017-7588, collect data, and develop custom firmware implants for attack simulation.
 watchtowrlabs/watchtowr-vs-sonicwall-preauth-rce-chain
PoC exploit chain for pre-authentication remote code execution on SonicWall SMA 100 appliances exploiting CVE-2023-44221 and CVE-2024-38475.